

sRDI
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
monoxgas/srdiShellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 gsoffmarket/malvinci
This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
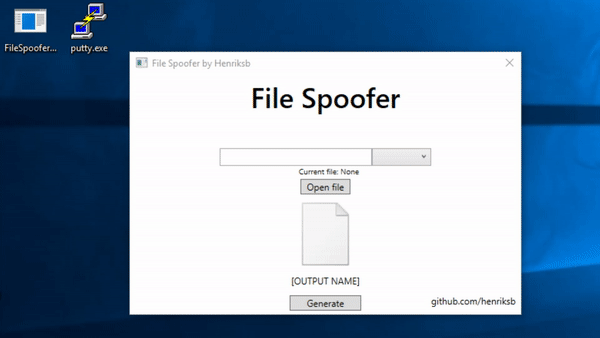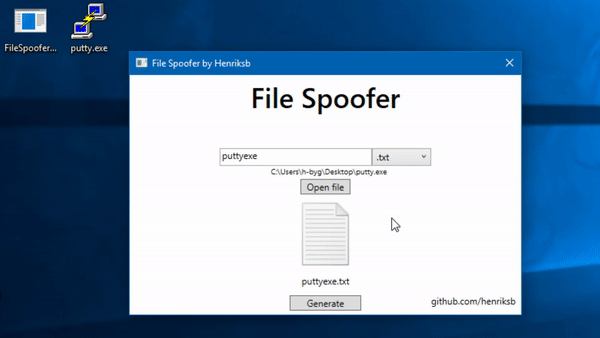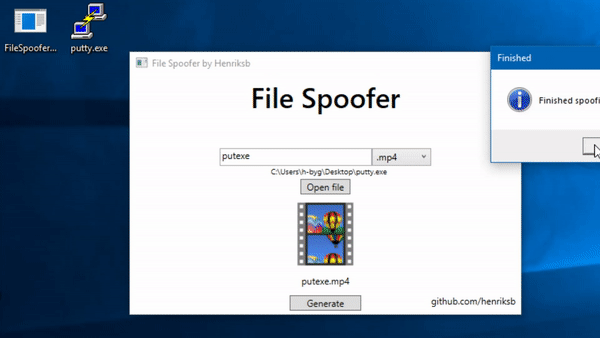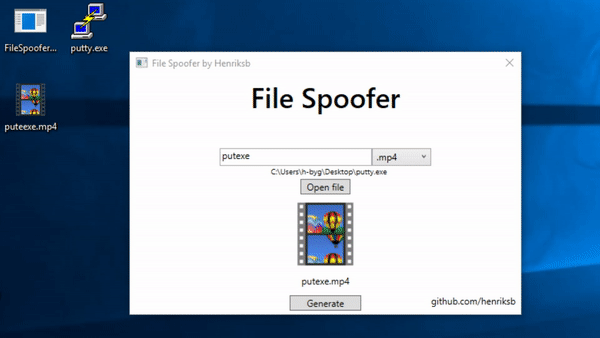 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 s3cur3th1ssh1t/amsi-bypass-powershell
This repo contains some Amsi Bypass methods i found on different Blog Posts.
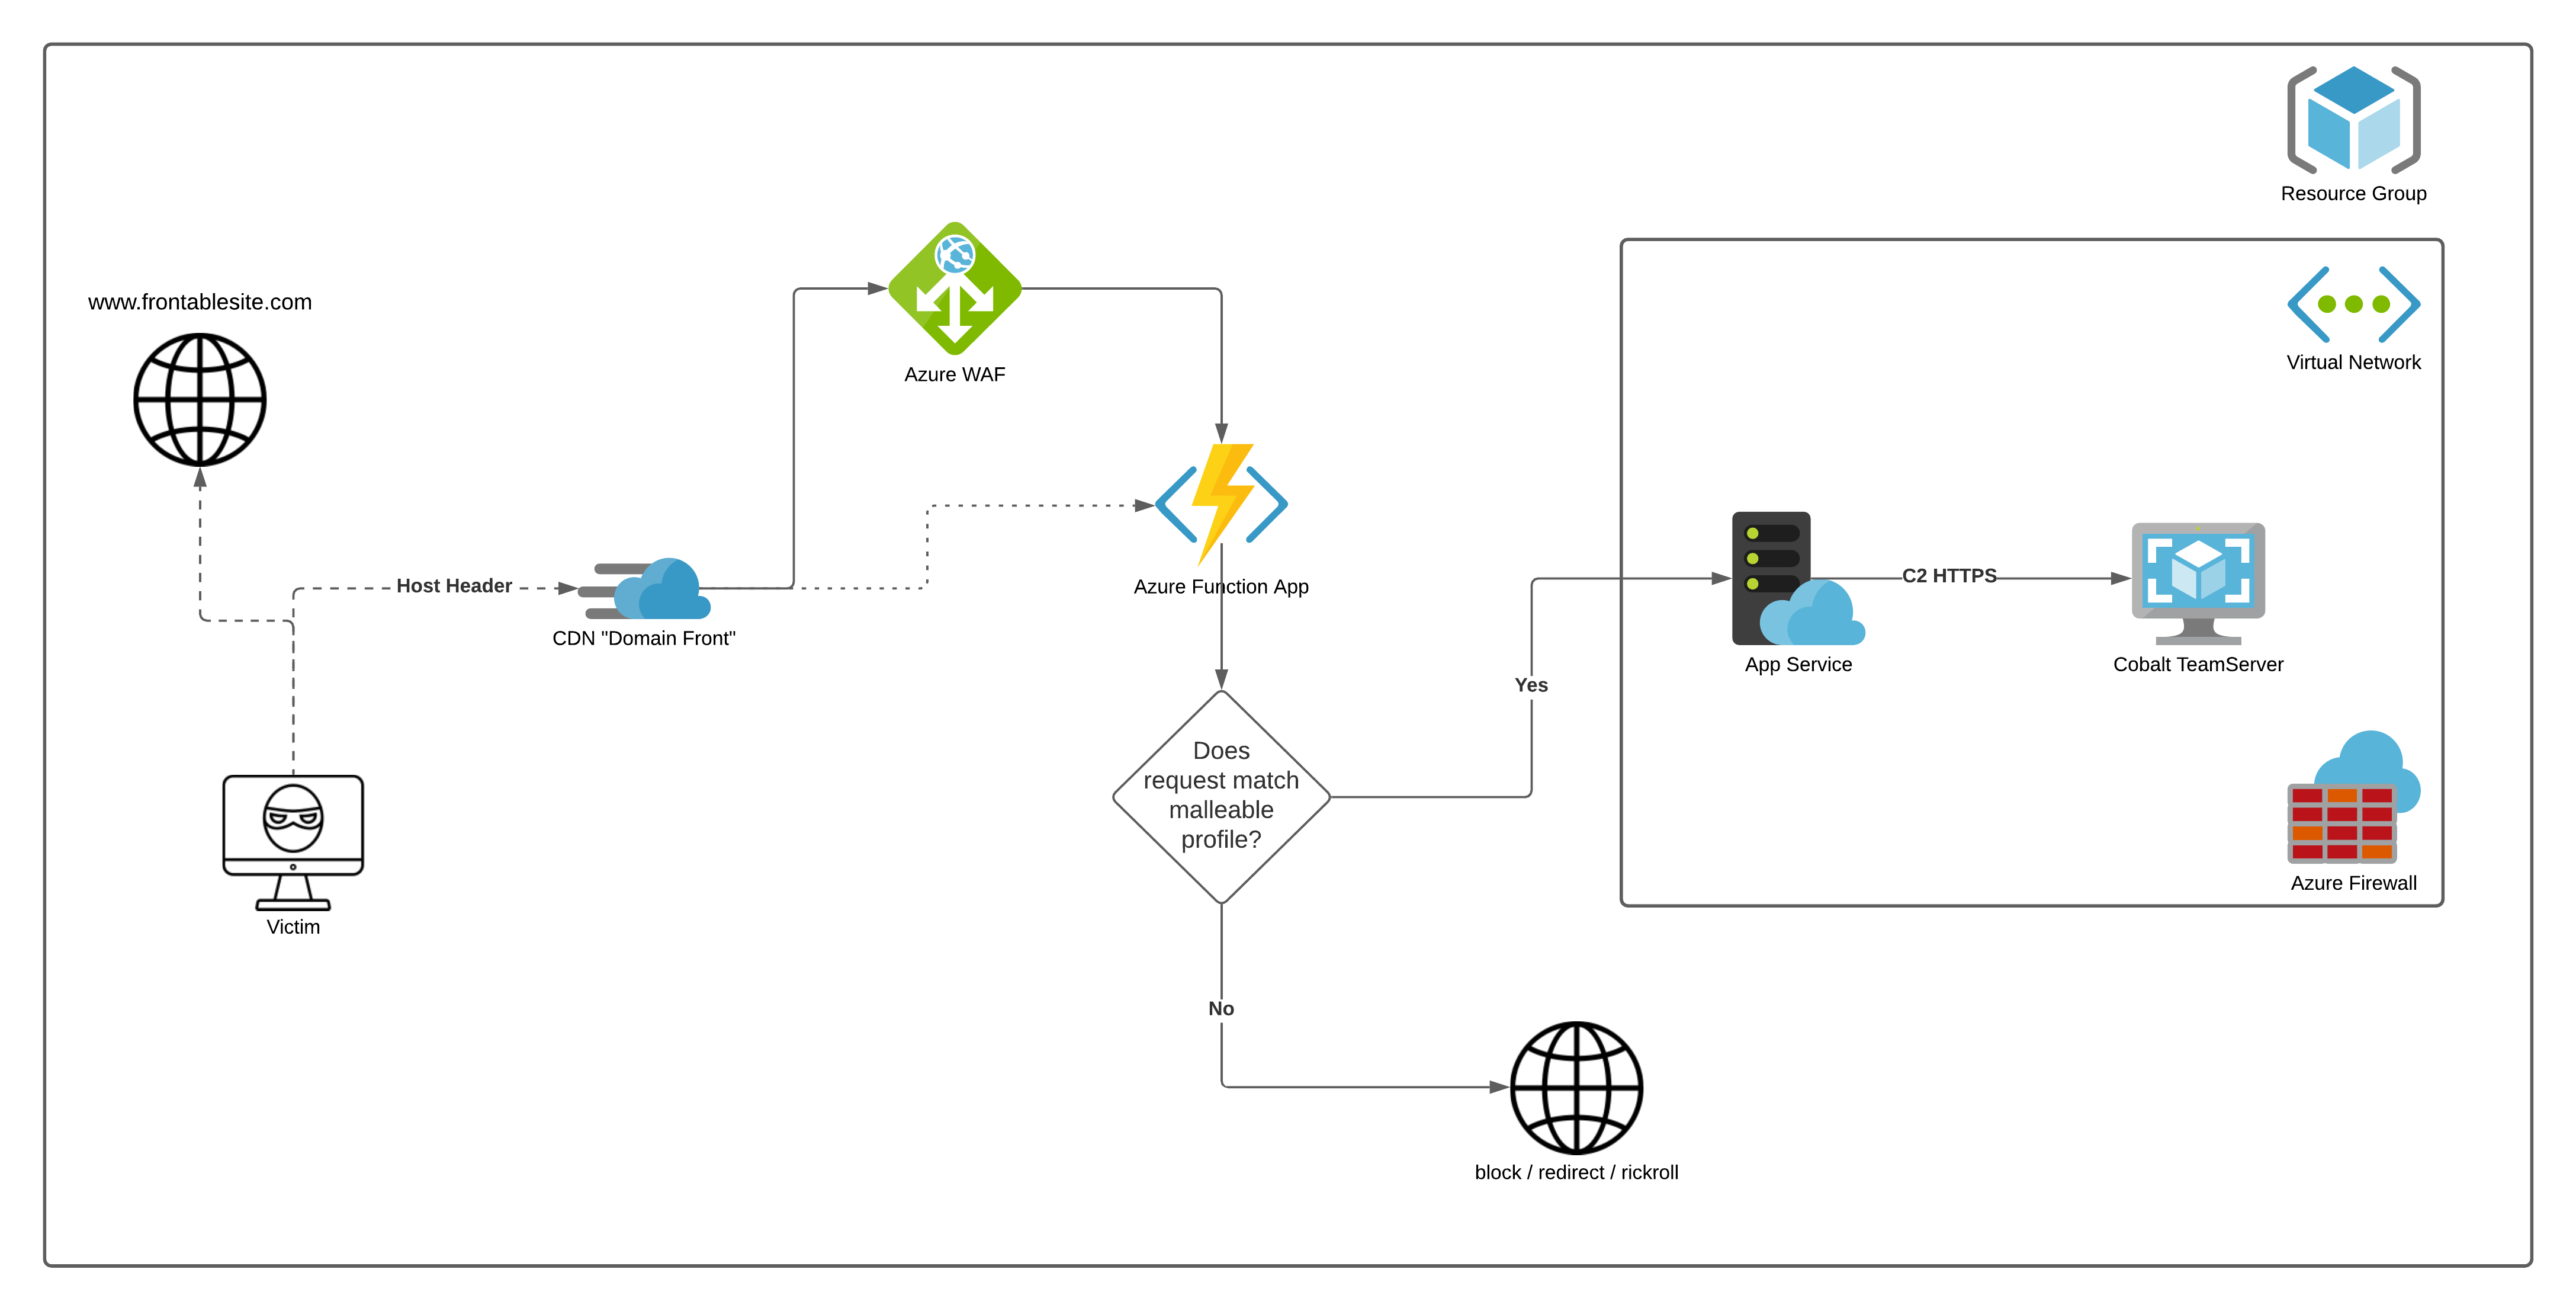 flangvik/azurec2relay
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 rsmudge/malleable-c2-profiles
Malleable C2 is a domain specific language to redefine indicators in Beacon's communication. This repository is a collection of Malleable C2 profiles…
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 synacktiv/twoface
"Two-Face" Rust binary on Linux
 jas502n/cs_sleepmask
CS_SleepMask
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 cenobyte-vincit/dyen
In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver