

CredMaster
 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
api-security-testingauthenticationcloud-security+9
1.3k
knavesec/credmasterRefactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 d0n601/pentest-cheat-sheet
There are many cheat sheets out there, but this is mine.
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 teymurnovruzov/cve-2019-9053-python3-remastered
The script has been remastered by Teymur Novruzov to ensure compatibility with Python 3. This tool is intended for educational purposes only.…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 ekultek/pybelt
The hackers tool belt
 yucaerin/cve-2024-55555
Laravel Crypto Killer Mass Scanner (CVE-2024-55555)
 x3rx3ssec/cve-2025-2011
Exploit for CVE-2025-2011
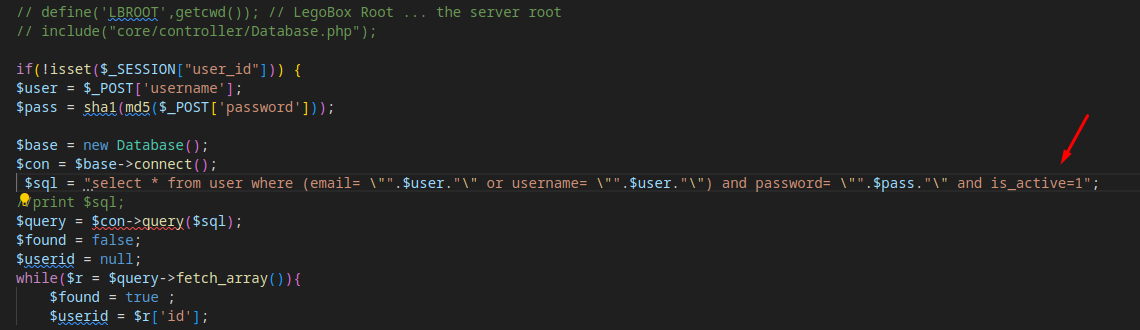 pointedsec/cve-2024-44541
This repository details a SQL Injection vulnerability in Inventio Lite v4's, including exploitation steps and a Python script to automate the attack.…
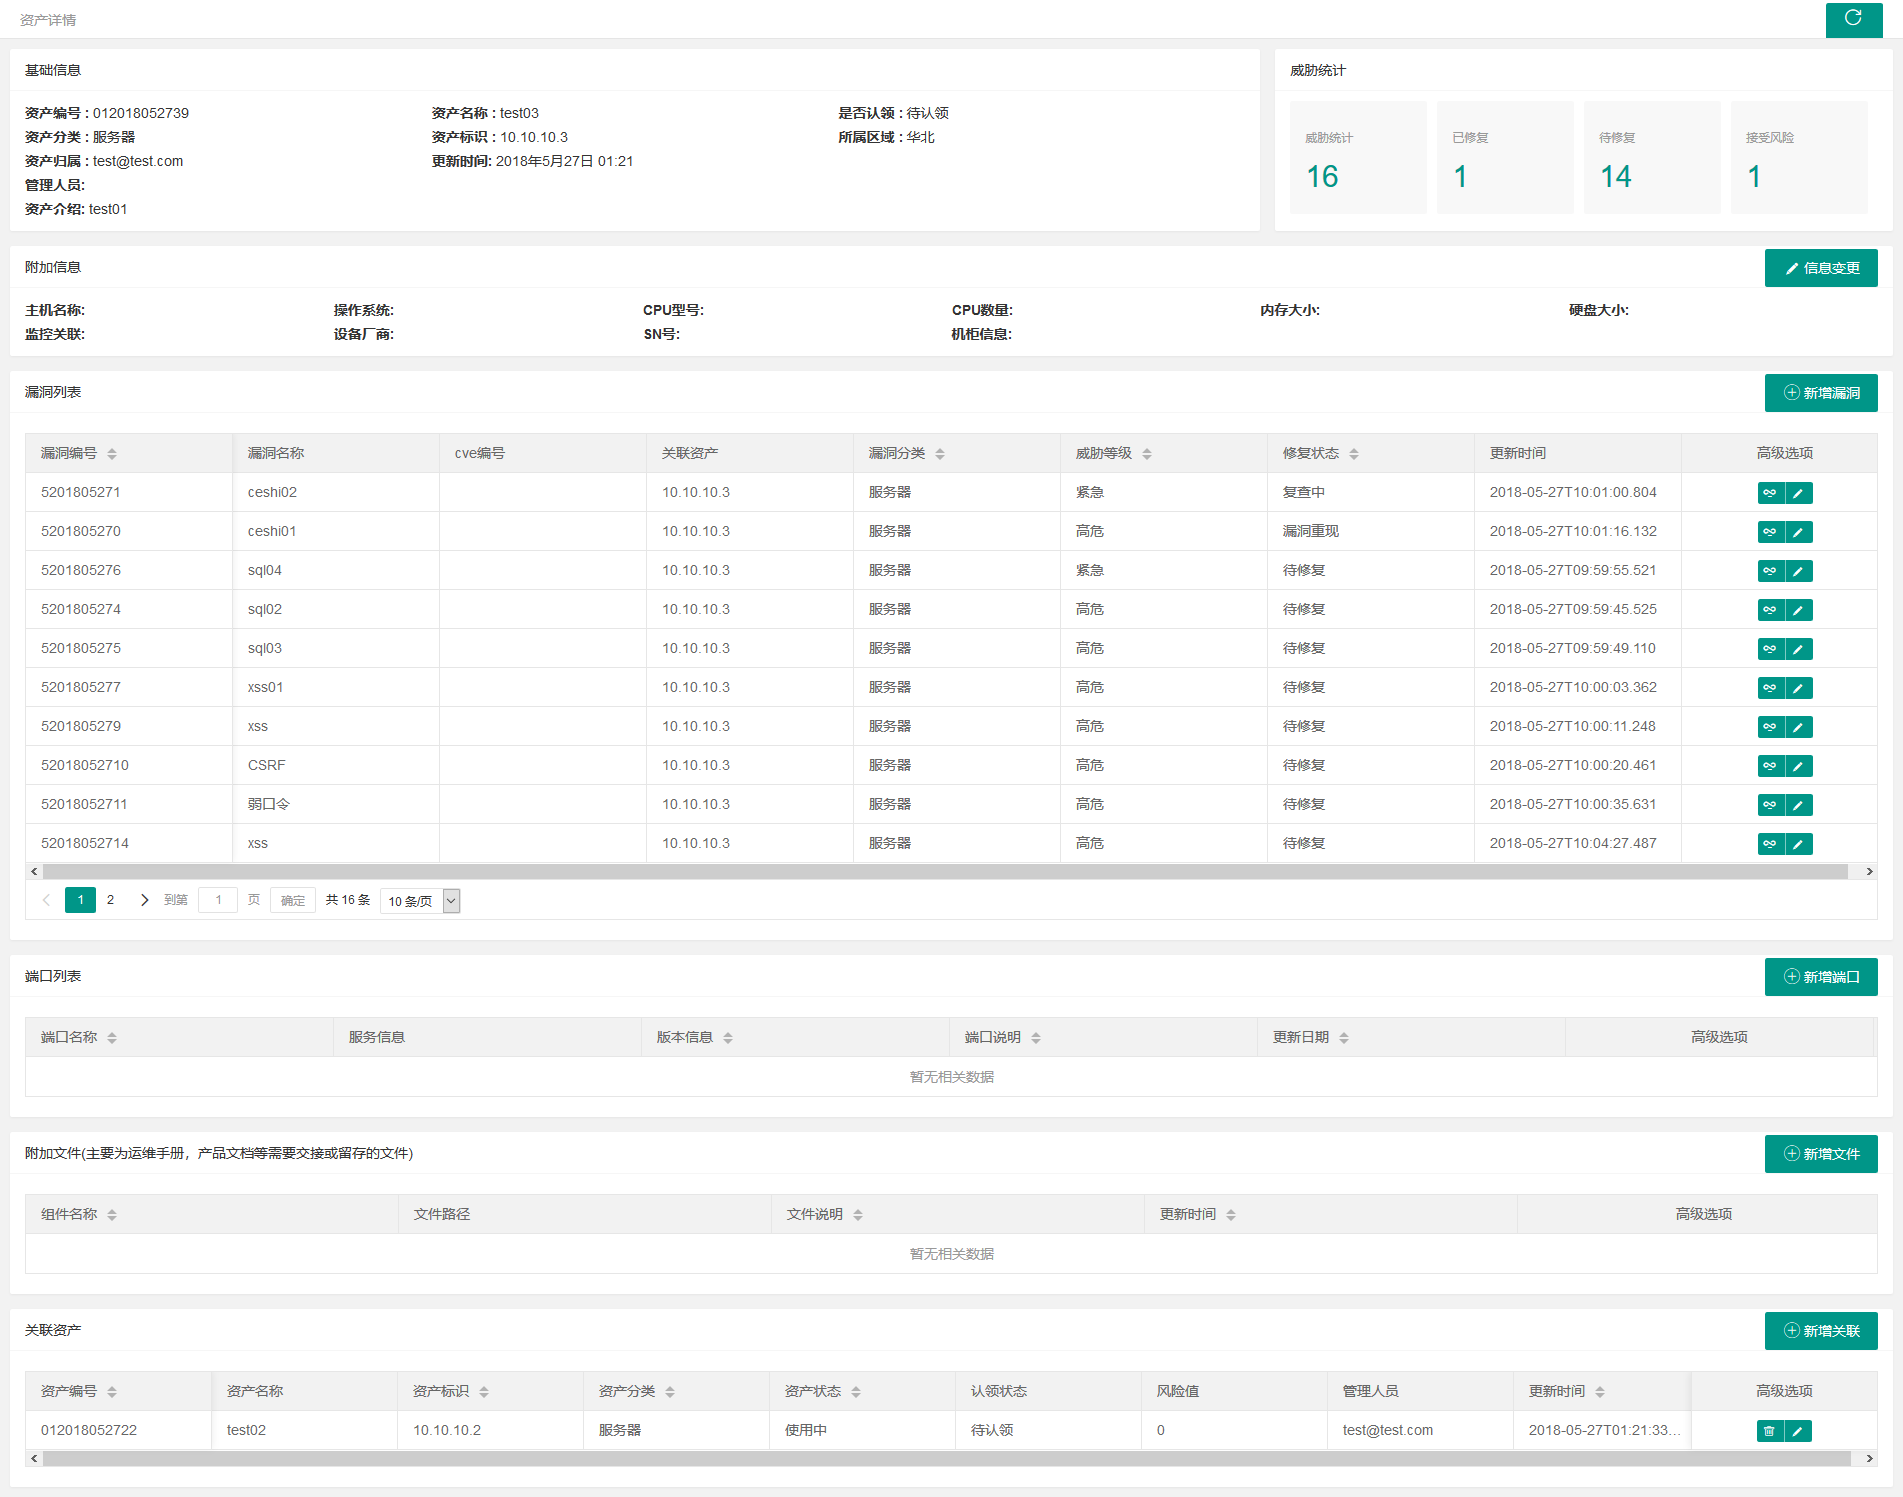 we1h0/securitymanageframwork
Security Manage Framwork is a security management platform for enterprise intranet, which includes asset management, vulnerability management,…
 verylazytech/cve-2024-4956
POC - CVE-2024–4956 - Nexus Repository Manager 3 Unauthenticated Path Traversal
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 rayferrufino/make-and-break
Built a custom Virtual Machine, running Ubuntu 18.04.1 and Webmin 1.810. Using CVE-2019-15107 to exploit a backdoor in the Linux machine