
SecLists
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
ctfcurated-resourcesdns-fuzzing+11
74.0k
danielmiessler/seclistsCurated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
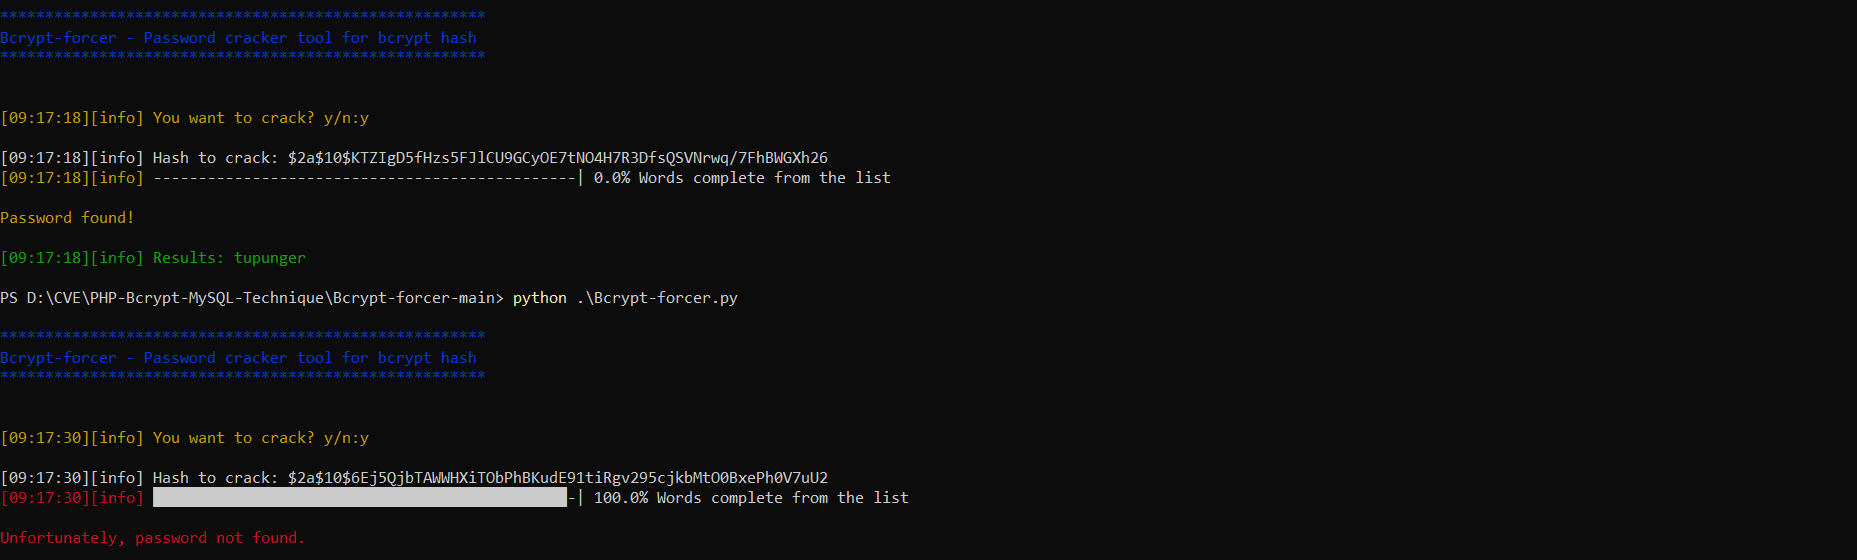 nu11secur1ty/bcrypt-forcer
Bcrypt hash cracker for penetration testing and password recovery. Decrypts Bcrypt hashes using dictionary or brute-force methods.
 mebus/cupp
Interactive password profiler that generates targeted wordlists by gathering personal details about a user, used for penetration testing and forensic…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 klynezyro/metasploitable2-vapt-report
Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 androguide/dsploit
dSploit - The most complete and advanced IT security professional toolkit on Android.
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 sup3rdav3/cve-2025-4396
CVE-2025-4396 - WordPress Relevanssi Time-Based Blind SQL Injection
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
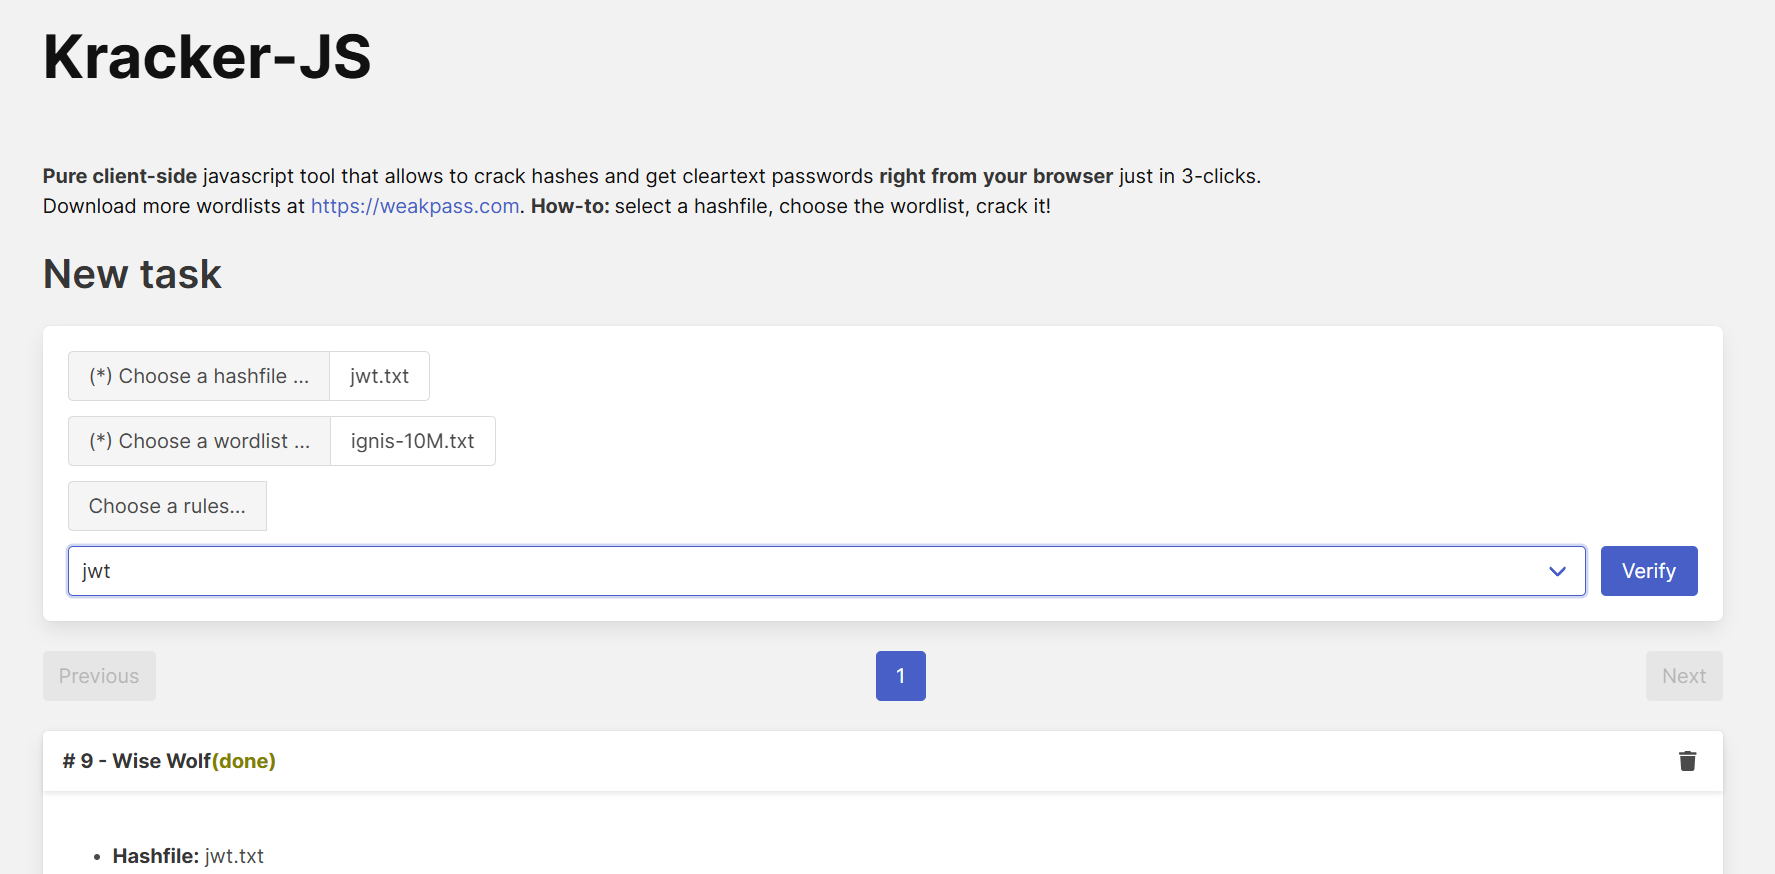 zzzteph/weakpass
Browser-based password cracking toolkit with hash lookup, wordlist generation, rule-based attack simulation, and client-side hash cracking for…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…