

mimikatz
 gentilkiwi/mimikatz
A little tool to play with Windows security
authenticationexploitationexploit-frameworks+10
gentilkiwi/mimikatzA little tool to play with Windows security
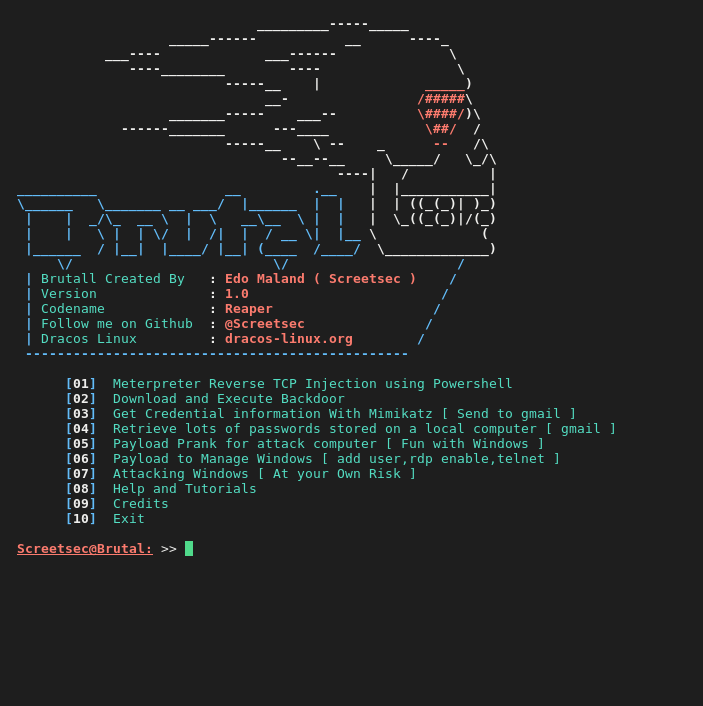 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
 jpg0mez/adcsync
Use ESC1 to perform a makeshift DCSync and dump hashes
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 icryo/rfcpwn
An enumeration and exploitation toolkit using RFC calls to SAP
 fin3ss3g0d/cosmicrakp
Go-based tool to exploit CVE-2013-4786 for dumping IPMI password hashes via RAKP authentication, supporting concurrent scanning of IP ranges or…
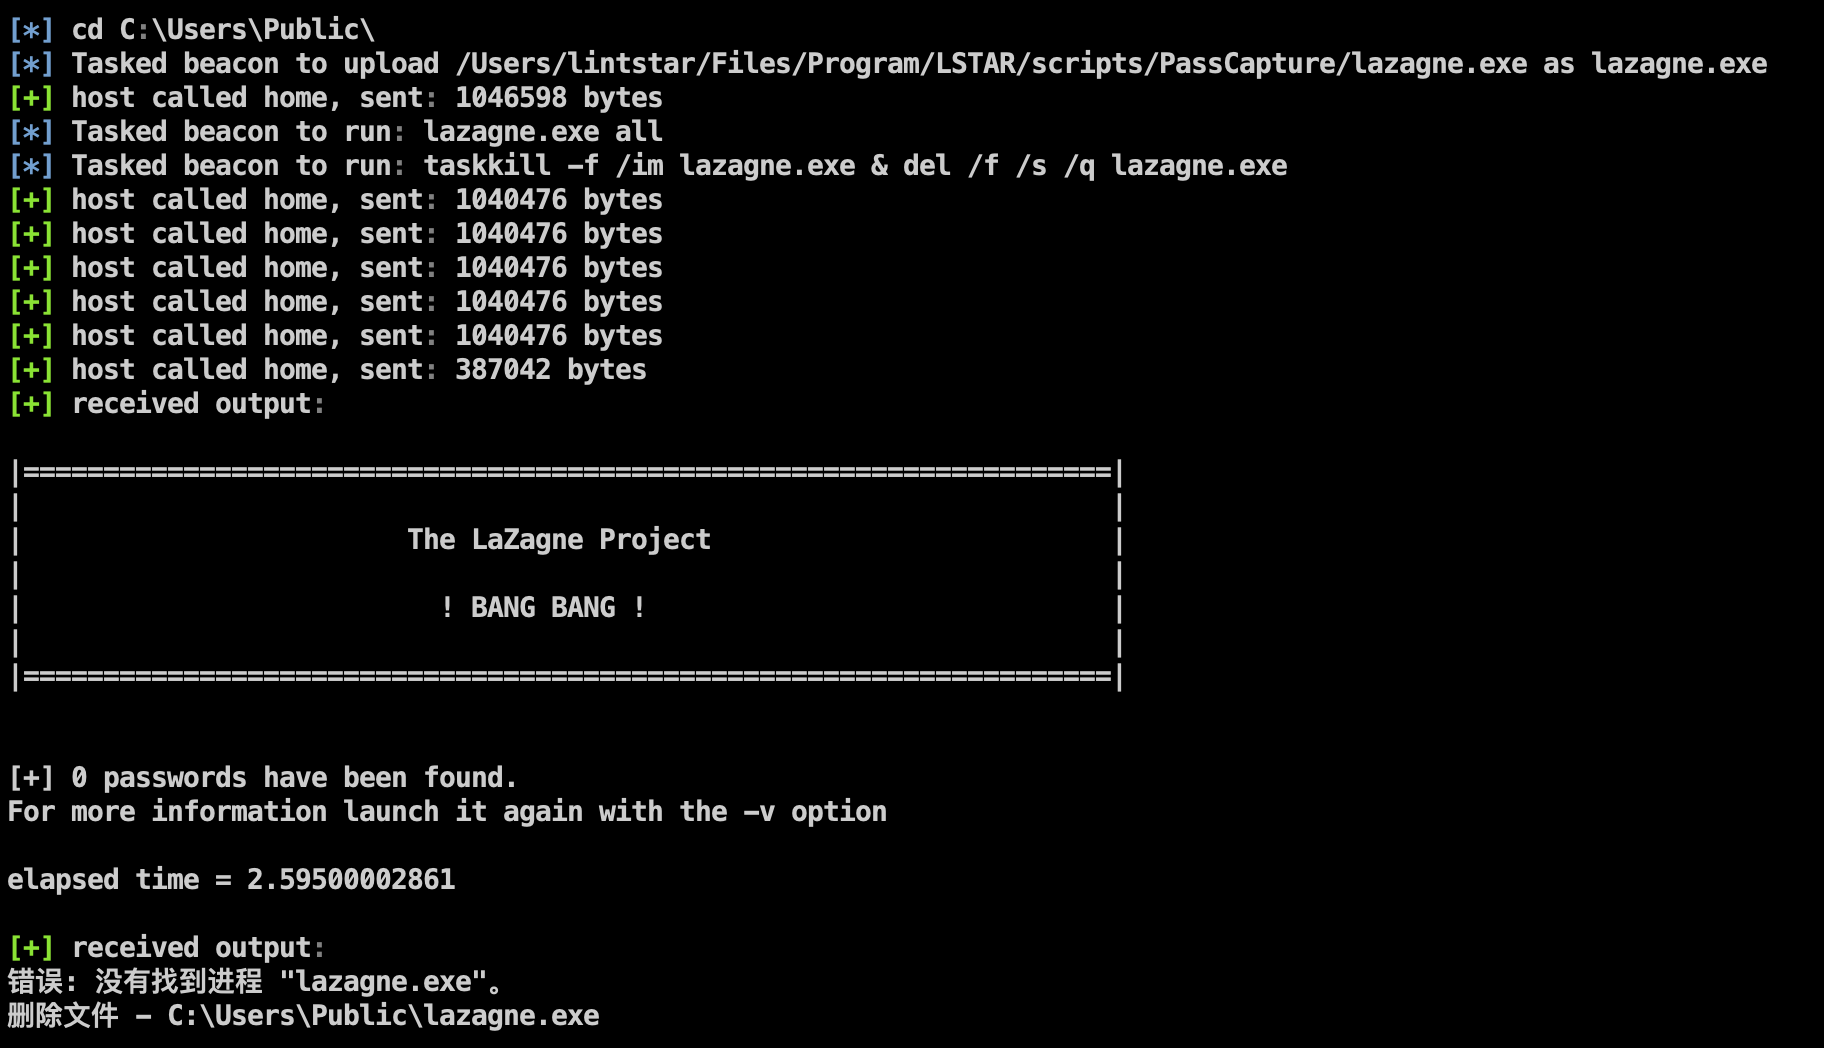 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 abdelrahman0sayed/cve-2025-24071
This is a python PoC scripts for CVE-2025-24071 which is a vulnerability in Windows File Explorer that allows unauthorized access to sensitive…
 iveresk/cve-2022-31749
PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.
 c4cnm/exploit_cve-2021-24762
This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.