
jwt-cracker
 lmammino/jwt-cracker
Simple HS256, HS384 & HS512 JWT token brute force cracker.
authenticationpassword-crackingweb-security
lmammino/jwt-crackerSimple HS256, HS384 & HS512 JWT token brute force cracker.
 4n4nk3/wordlister
A simple wordlists generator and mangler written in Python 3.10.1.
 frizb/wordlistgen
Super Simple Python Word List Generator for Fuzzing and Brute Forcing in Python
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 synacktiv/cachedata_decrypt
A simple Toolkit to BF and decrypt Windows EntraId CacheData
 ajuremesh/pdfpasswordunlocker
This project offers a straightforward solution for retrieving forgotten PDF passwords using Google Colab. With just five simple steps, it efficiently…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
 randomuser1983/ikeabuser
A simple tool wrapper to automate the enumeration, fingerprinting, and PSK extraction of an IPSec VPN gateway.
 azrenom/cms-made-simple-2.2.9-cve-2019-9053
Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…
 jagdeepsinghceh/cms-made-simple-python3
Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 itzr1g/cve-2019-9053
Python exploit for CVE-2019-9053 targeting CMS Made Simple with SQL injection detection and password hash cracking via wordlist, featuring argparse…
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
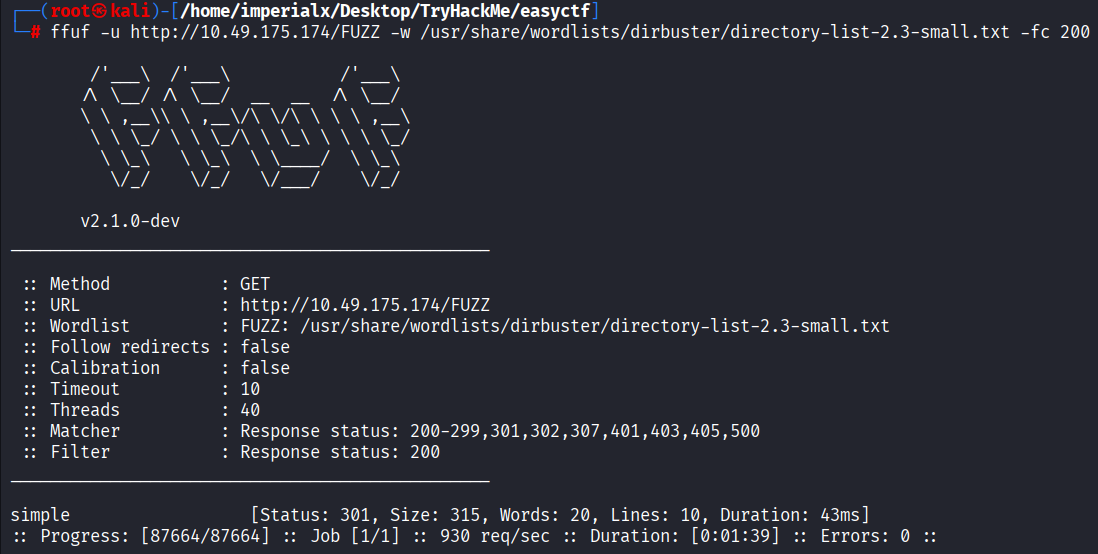 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…