
AD-PathFinder
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
exploitationinformation-gatheringlateral-movement+7
247
netspi/ad-pathfinderAttack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 puckblush/tofu
Windows offline filesystem hacking tool for Linux
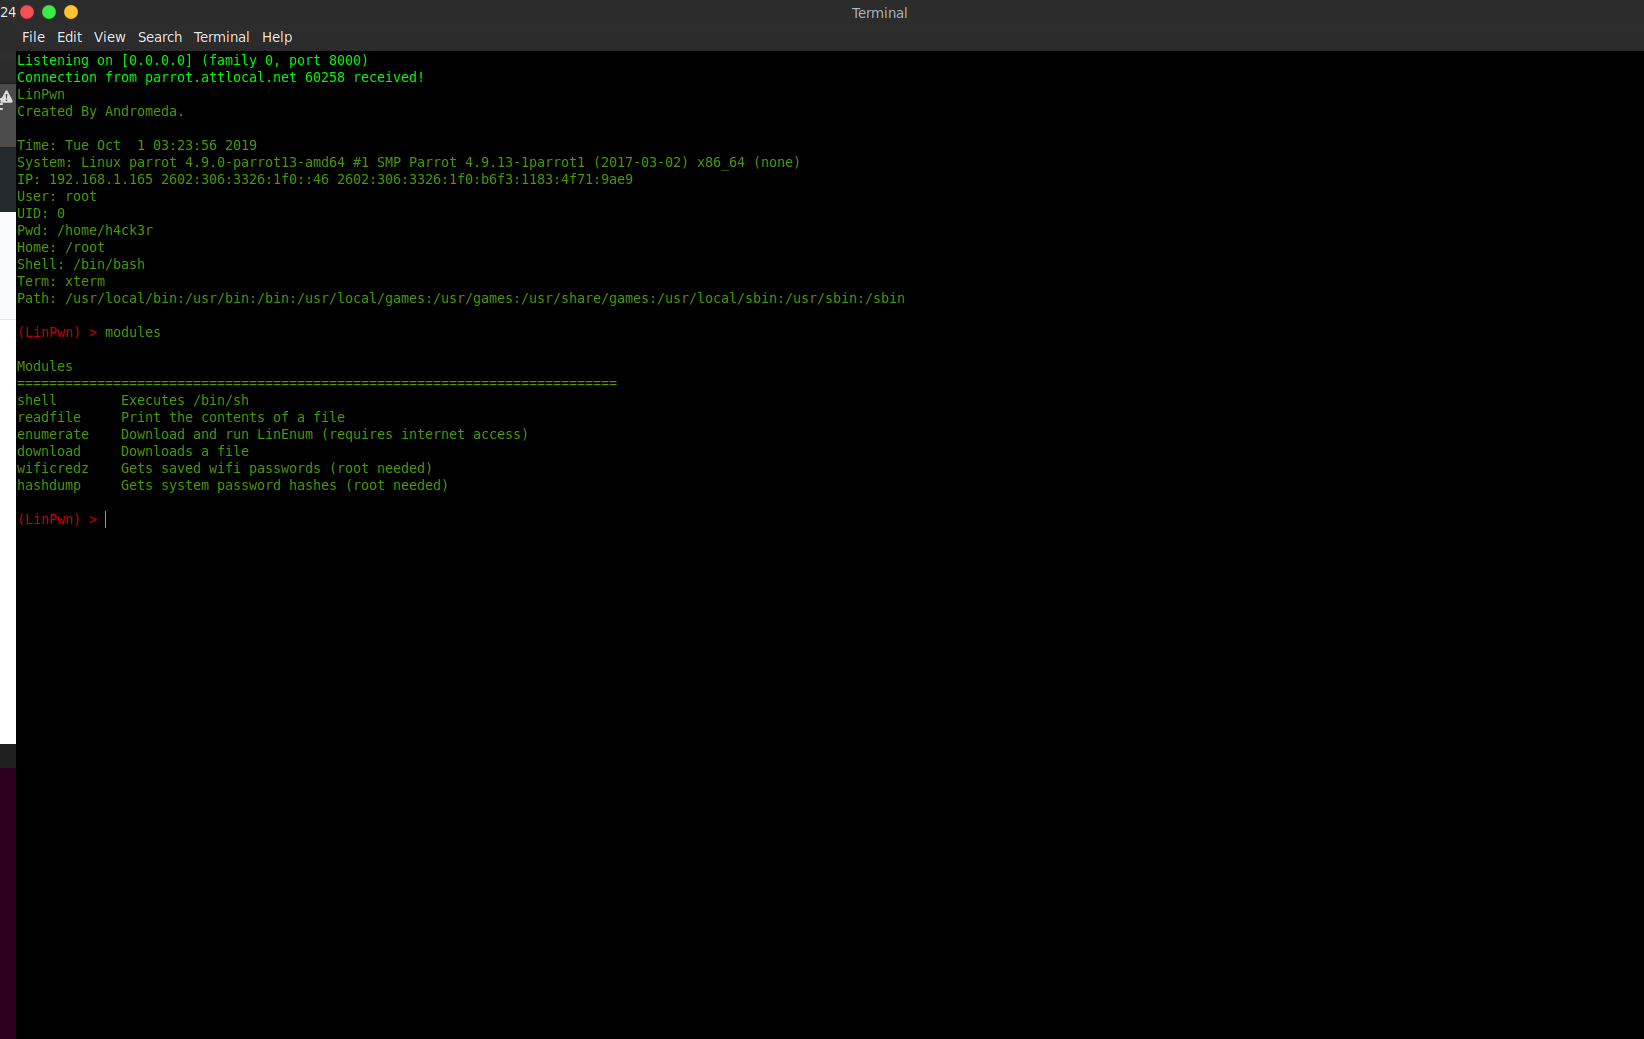 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
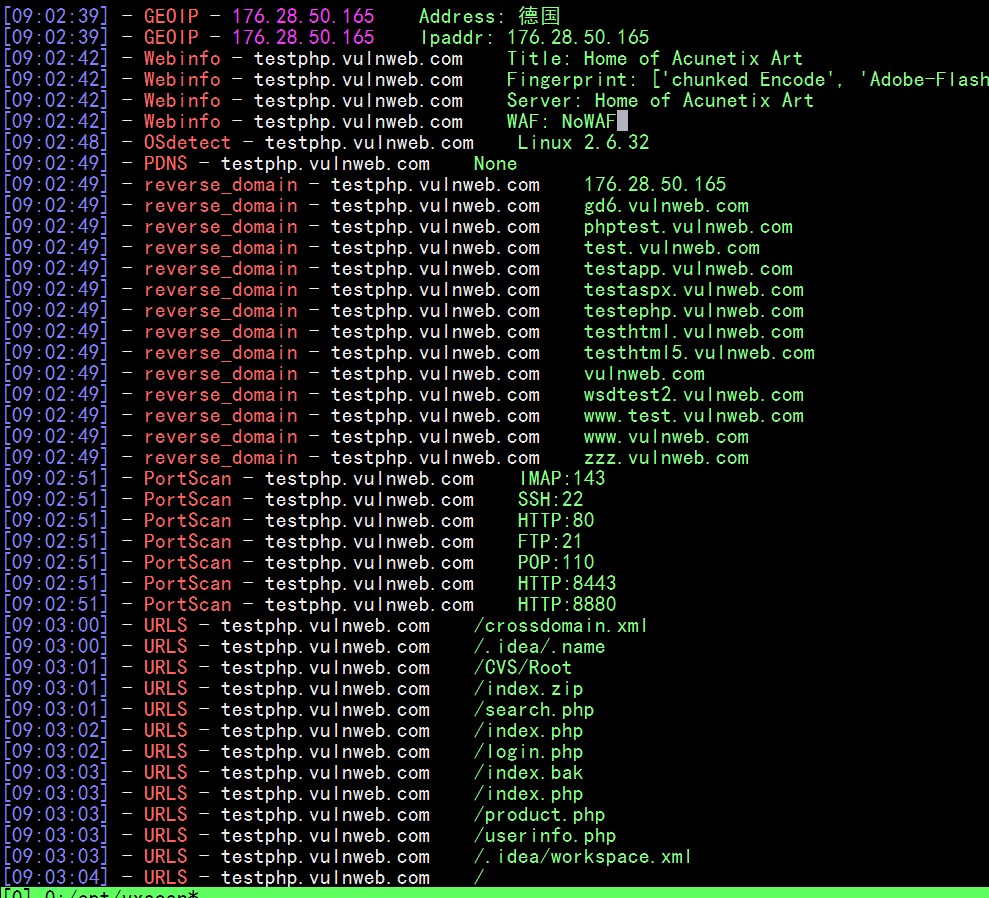 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
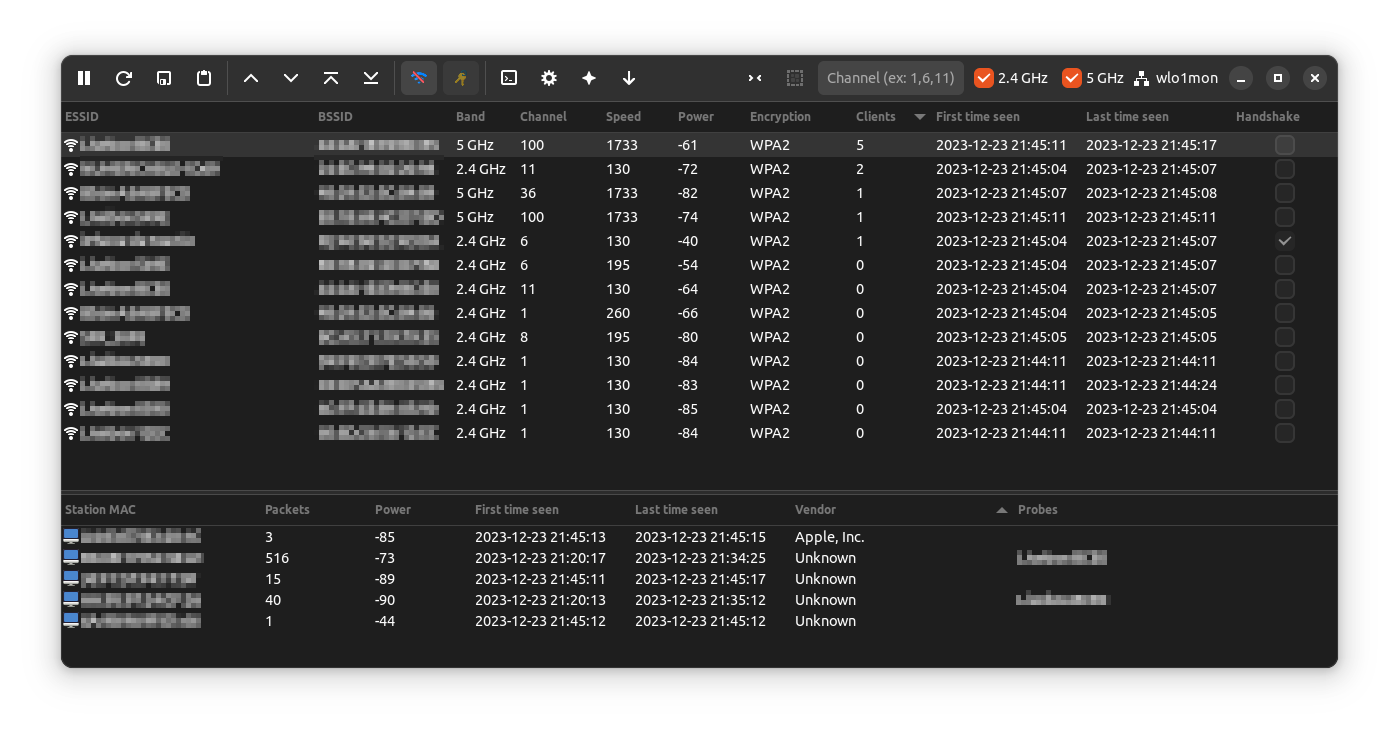 martin-olivier/airgorah
Rust-based GUI tool for WiFi security auditing: captures traffic, discovers clients, performs deauthentication attacks, captures handshakes, and…
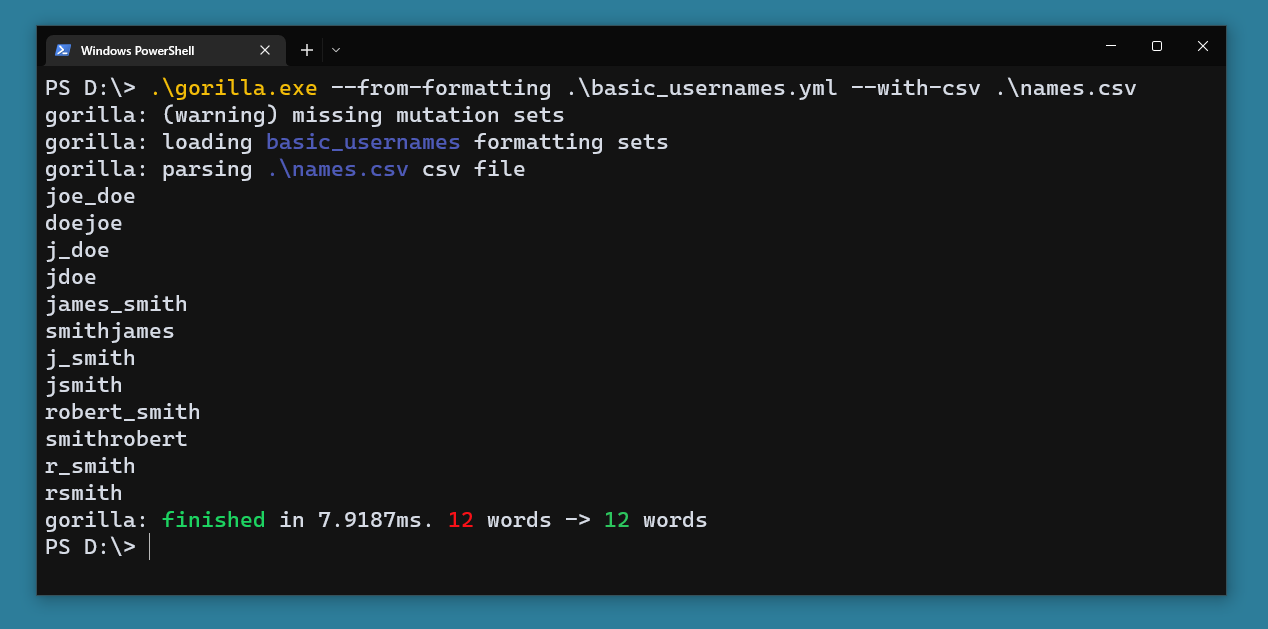 andreiverse/gorilla
tool for generating wordlists or extending an existing one using mutations.
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 occasionpuffbird12/airstrike
Audit Wi-Fi security on Linux with monitor mode, handshake capture, and offline WPA/WPA2 password testing in one guided GUI
 meliht/mr.sip
SIP Security Assessment Framework for VoIP Pentesters. Presented at DEFCON, BlackHat & Offzone.
 stiffies/airscout
A nice tool that automates network hash capturing and has a nice GUI. Read README.md for more information and NEVER use this without explicit…
 fin3ss3g0d/cosmicrakp
Go-based tool to exploit CVE-2013-4786 for dumping IPMI password hashes via RAKP authentication, supporting concurrent scanning of IP ranges or…
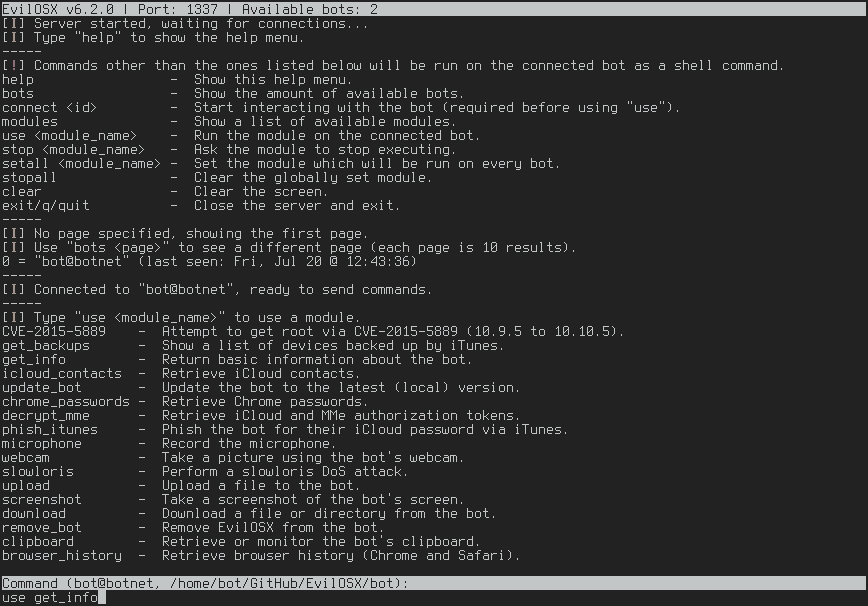 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 khast3x/h8mail
Email OSINT & Password breach hunting tool, locally or using premium services. Supports chasing down related email
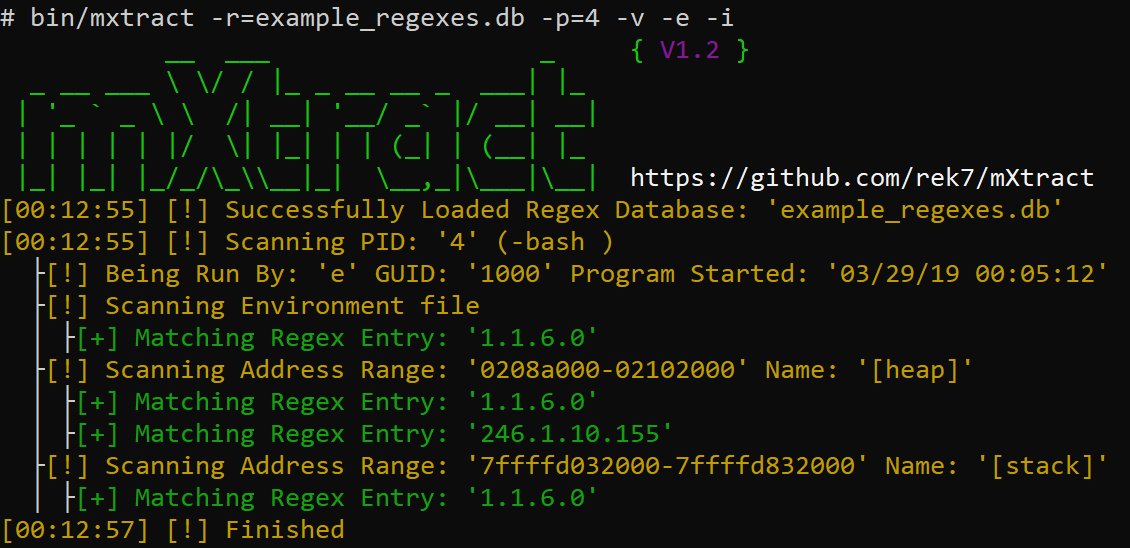 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
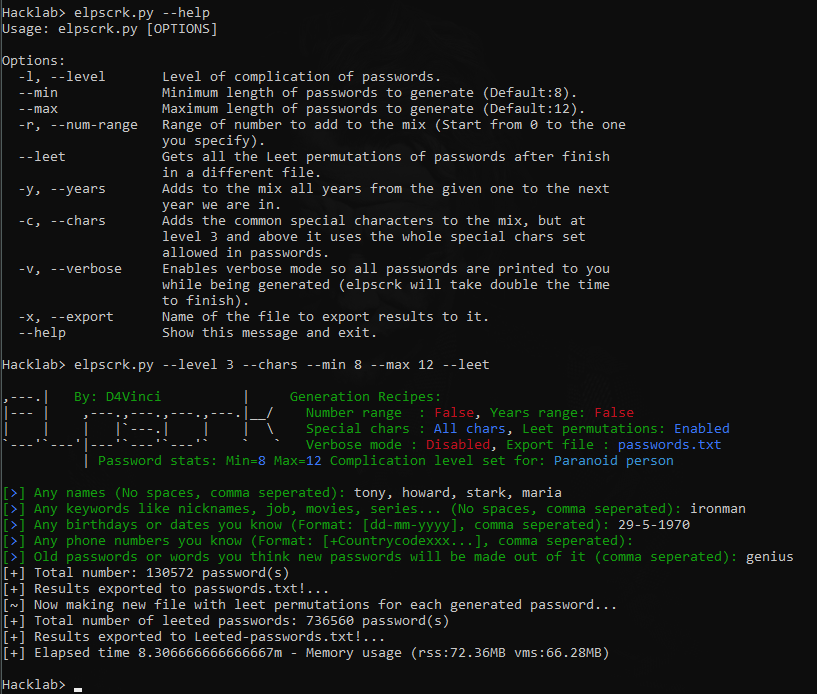 d4vinci/elpscrk
An Intelligent wordlist generator based on user profiling, permutations, and statistics. (Named after the same tool in Mr.Robot series S01E01)
 viralmaniar/smwyg-show-me-what-you-got
This tool allows you to perform OSINT and reconnaissance on an organisation or an individual. It allows one to search 1.4 Billion clear text…