


 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
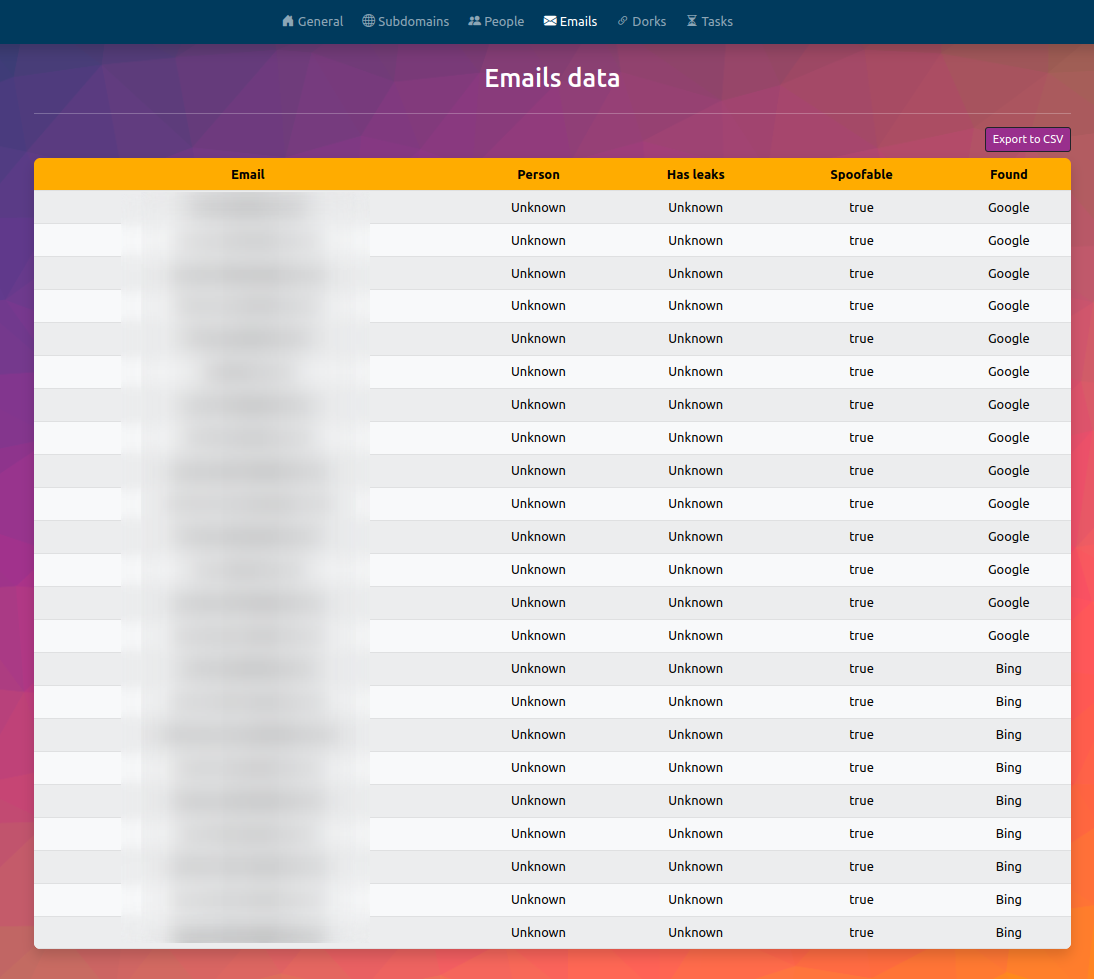 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 ledksv/monitorsfour
HackTheBox MonitorsFour walkthrough covering credential leak, CVE-2025-24367 Cacti RCE, and CVE-2025-9074 Docker Desktop API container escape to root.
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 skelsec/pypykatz
Mimikatz implementation in pure Python
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
 danmcinerney/icebreaker
Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 viralmaniar/smwyg-show-me-what-you-got
This tool allows you to perform OSINT and reconnaissance on an organisation or an individual. It allows one to search 1.4 Billion clear text…
 joelgmsec/leaksearch
Searches and parses plaintext passwords from public breach databases (ProxyNova COMB) by keyword (user/domain/password), with proxy support and…
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 secuproject/adenum
AD Enum is a pentesting tool that allows to find misconfiguration through the the protocol LDAP and exploit some of those weaknesses with kerberos.
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.