
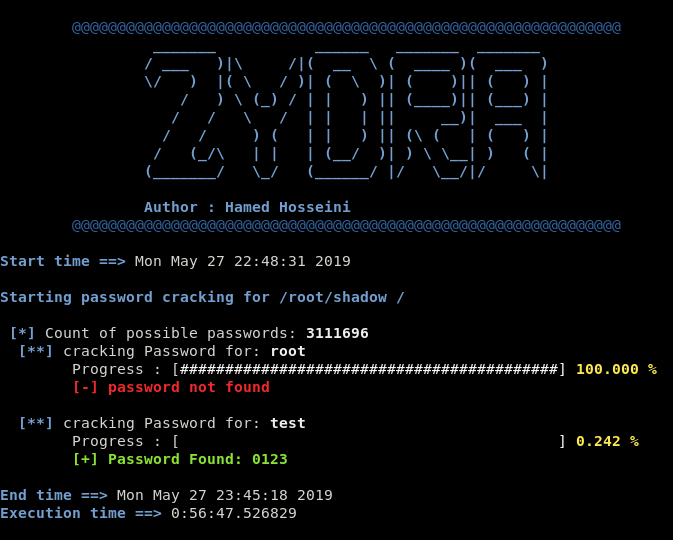
Zydra
 hameda2/zydra
Multi-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
data-recoverypassword-attackspassword-cracking
hameda2/zydraMulti-threaded password recovery tool for RAR, ZIP, PDF, and Linux shadow files using dictionary and brute-force methods with configurable character…
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 glv2/bruteforce-wallet
Try to find the password of an encrypted Peercoin (or Bitcoin, Litecoin, etc...) wallet file.
 0x6rss/cve-2025-24071_poc
CVE-2025-24071: NTLM Hash Leak via RAR/ZIP Extraction and .library-ms File
 floyd-fuh/jks-private-key-cracker-hashcat
Nail in the JKS coffin - Cracking passwords of private key entries in a JKS file
 funoverip/mcafee-sitelist-pwd-decryption
Password decryption tool for the McAfee SiteList.xml file
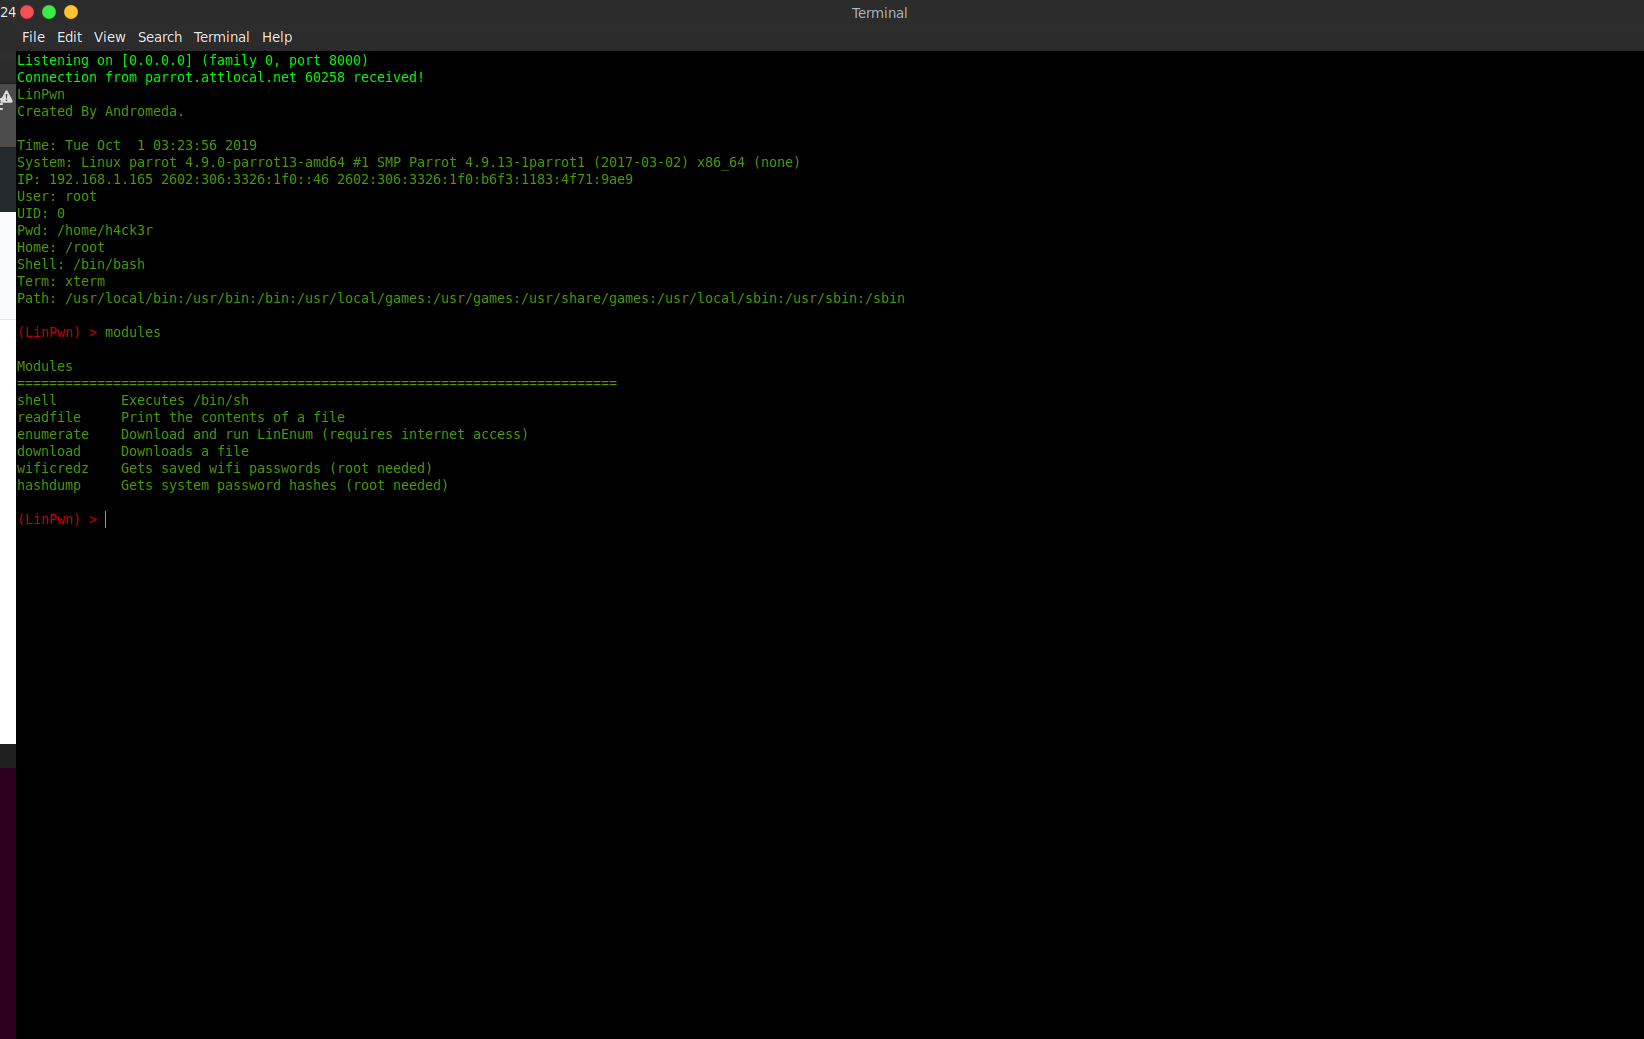 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 entry33/aes256_passwd_store
AES-256 encrypted password manager with scrypt/SHA256 key derivation, supporting create, edit, query, and master password change operations with…
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 hellgatecorp/docxnginxfx
Deep File Forensic. Create or manipulate Wordlists out of Text Documents (ex: for BruteForcing). Save it Line by Line as a Binary .BIN File or as a…
 0xsazzad/grafana-cve-2021-43798
Python implementation of a tool for decrypting and encrypting sensitive data in Grafana, specifically addressing the vulnerabilities associated with…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 okymi-x/cve-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…