

CVE-2019-9053-port-py3
 del0x3/cve-2019-9053-port-py3
CVE-2019-9053.
educationexploitationpassword-cracking+3
del0x3/cve-2019-9053-port-py3CVE-2019-9053.
 davcwikla/cve-2019-9053-exploit
Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 mbadanoiu/cve-2020-13941
CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr
 ret2desync/cve-2024-38793-poc
Proof of Concept code for exploitation of CVE-2024-38793 (Best Restaurant Menu by PriceListo <= 1.4.1 - Authenticated (Contributor+) SQL Injection)
 pointedsec/cve-2024-44541
This repository details a SQL Injection vulnerability in Inventio Lite v4's, including exploitation steps and a Python script to automate the attack.…
 hackheart-tech/-exploit-lab
Exploits Python cve-2019-9053– by HackHeart
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…
 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
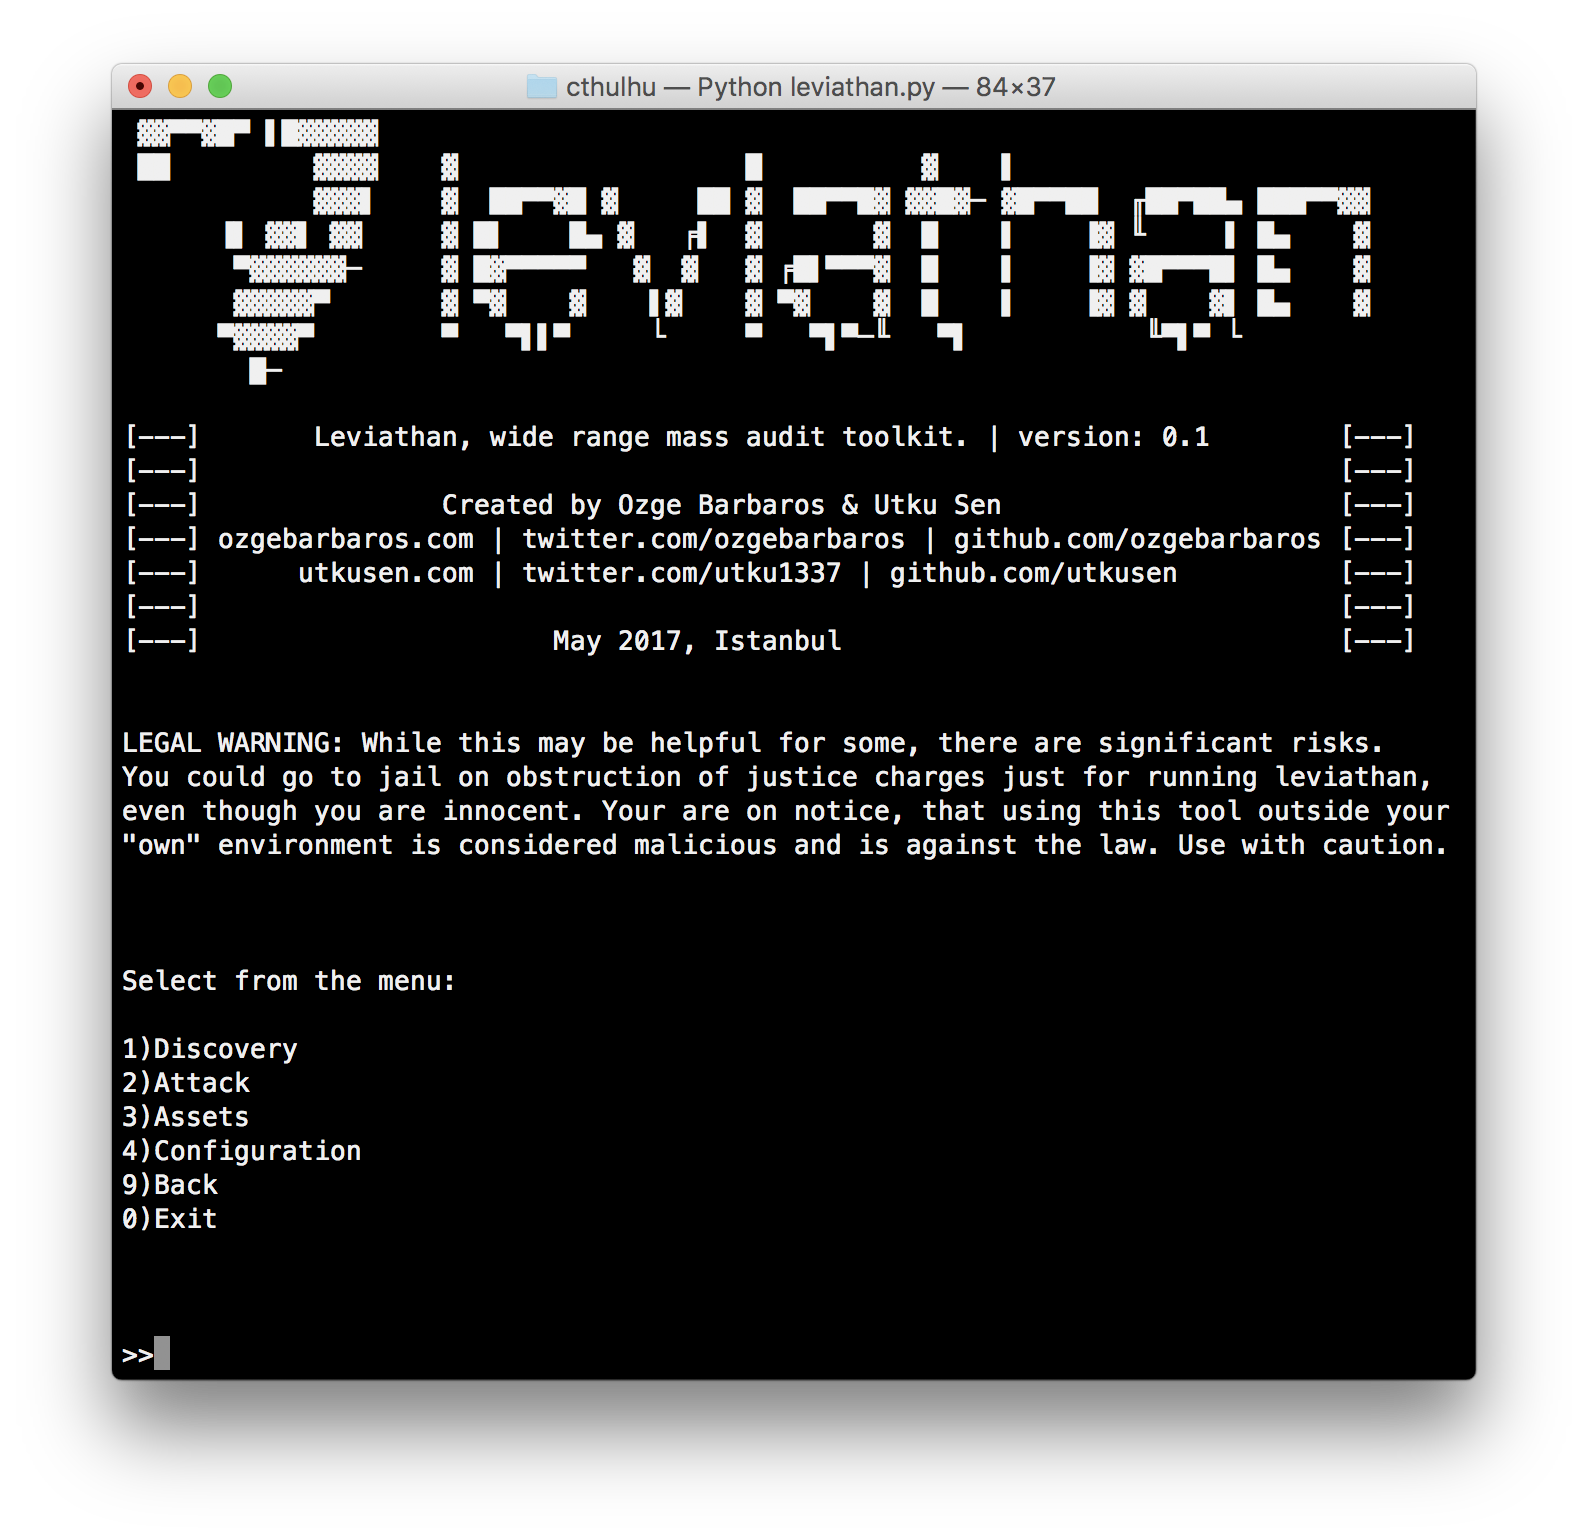 utkusen/leviathan
wide range mass audit toolkit
 mehulj94/radium
Python logger with multiple features.
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation