

CVE-2019-9053
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
exploitationpassword-crackingpenetration-testing+2
byrek/cve-2019-9053Improved code of Daniele Scanu SQL Injection exploit
 hackheart-tech/-exploit-lab
Exploits Python cve-2019-9053– by HackHeart
 hf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-
Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…
 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
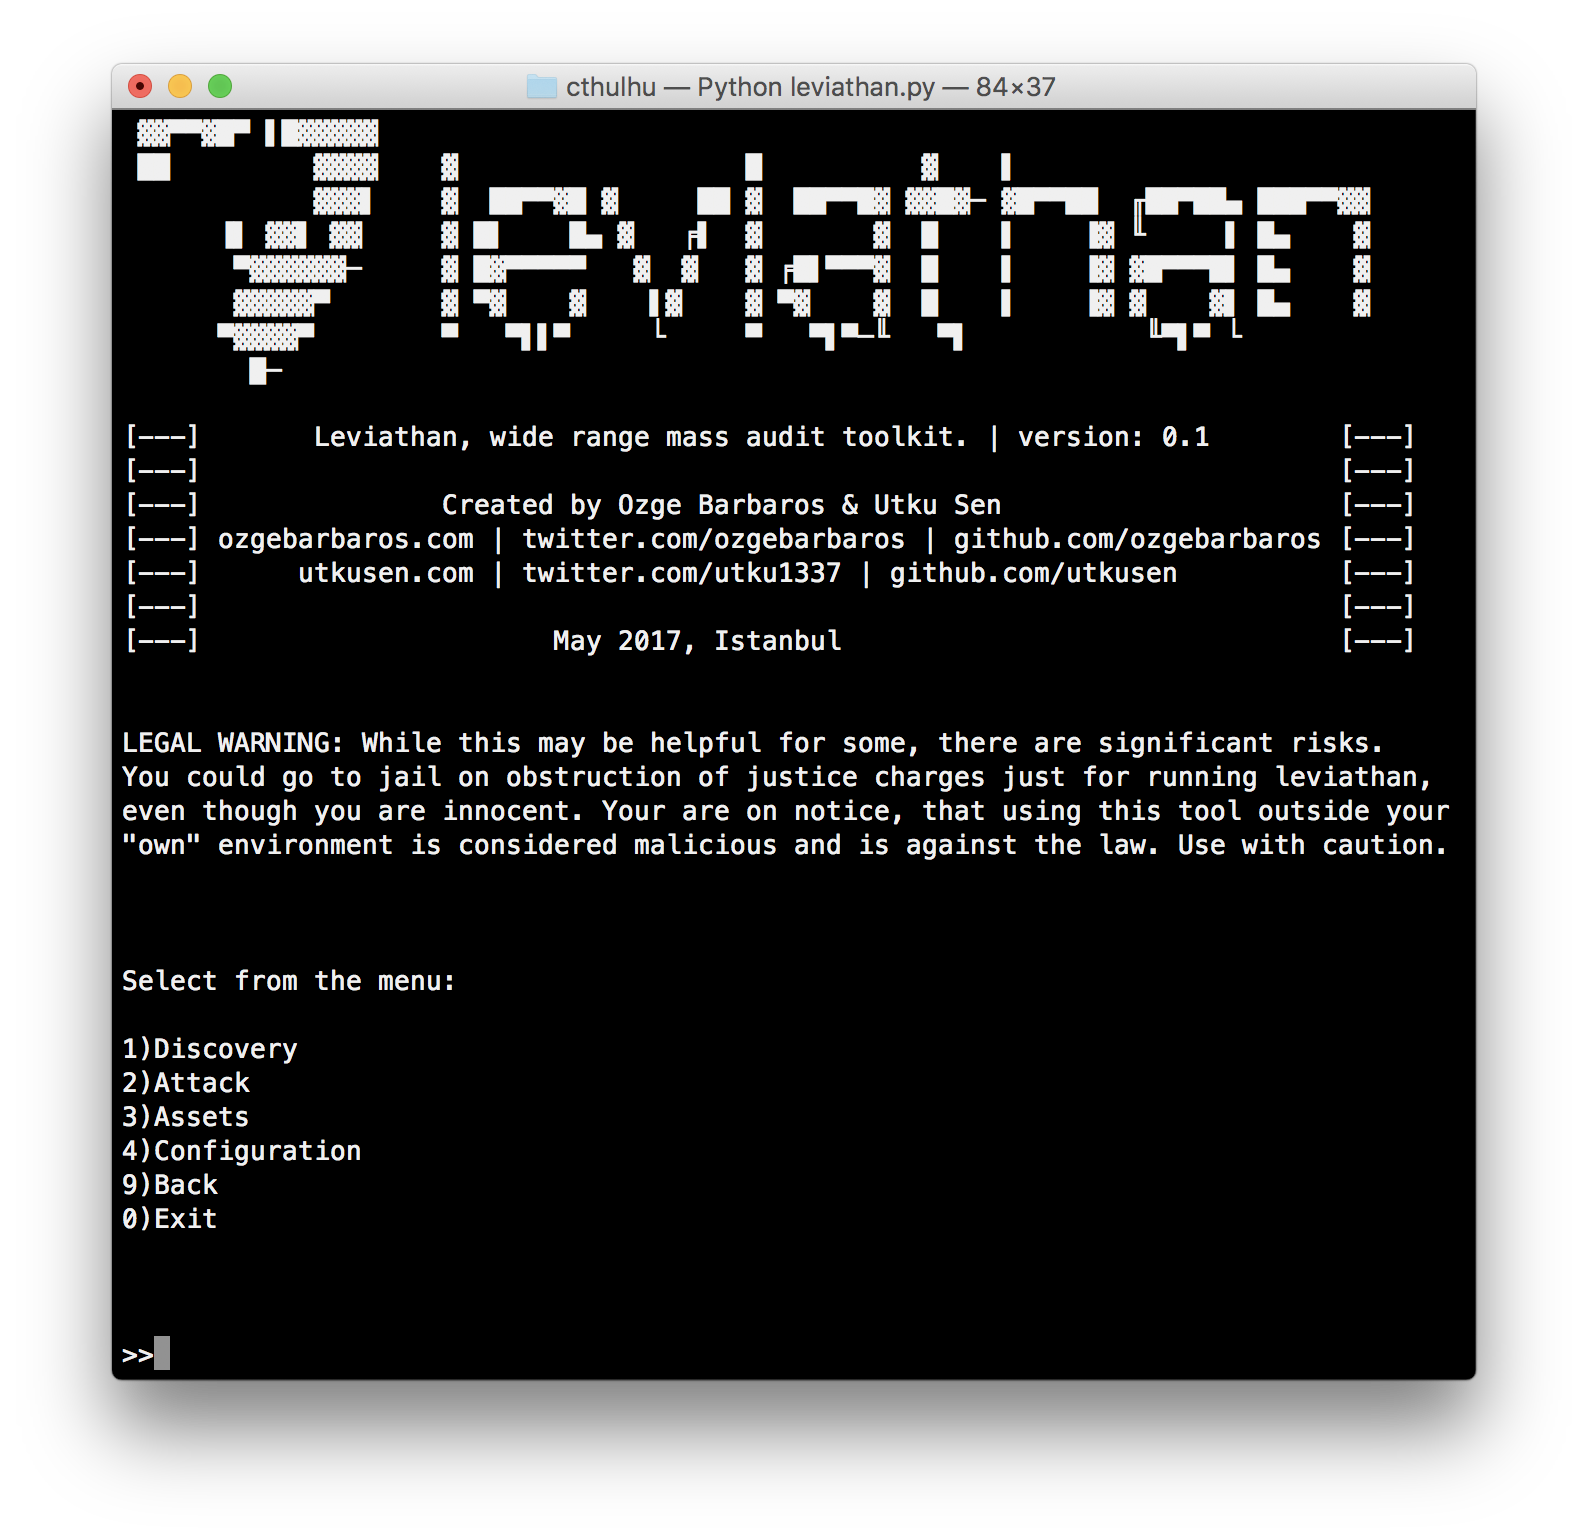 utkusen/leviathan
wide range mass audit toolkit
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
