

Hacking-Cheatsheets
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
curated-resourcesdigital-forensicseducation+9
567
ilias1988/hacking-cheatsheetsA comprehensive collection of penetration testing cheatsheets, guides, and tools.
 samdenty/injectify
Perform advanced MiTM attacks on websites with ease 💉
 bwithe/cve-2024-9796
CVE-2024-9796 WP-Advanced-Search < 3.3.9.2 - Unauthenticated SQL Injection. Poc.
 asbawy/graftraverse-cve-2021-43798
CVE-2021-43798 MiNi Exploitation Framework
 sup3rdav3/cve-2025-4396
CVE-2025-4396 - WordPress Relevanssi Time-Based Blind SQL Injection
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 0xsha/wp2shell
CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
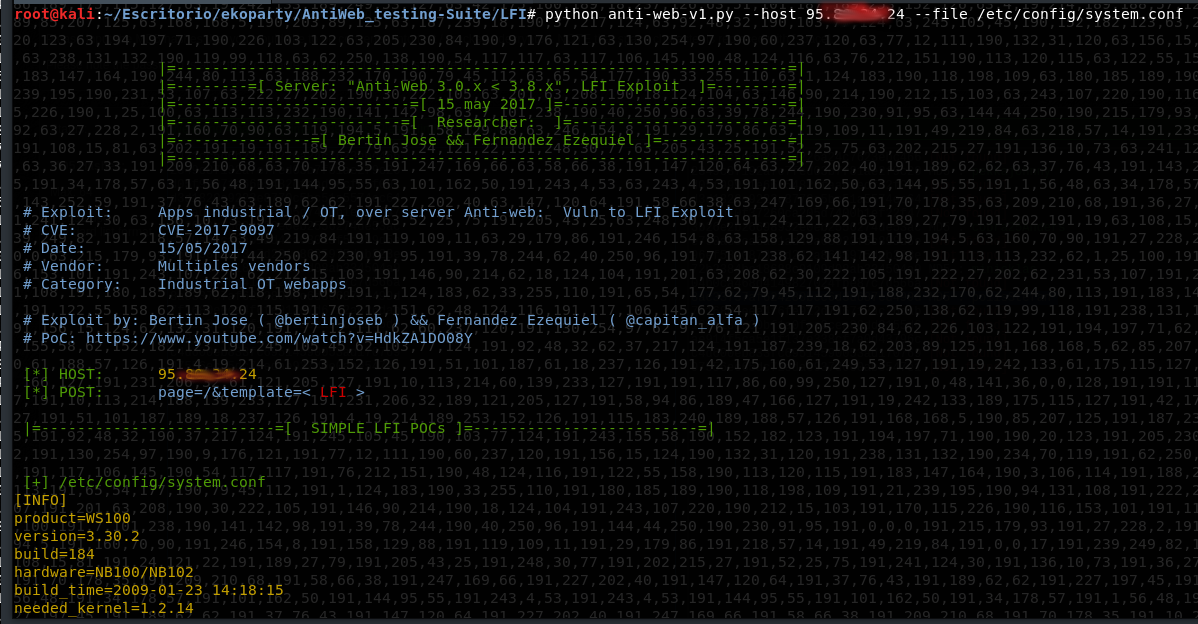 mdudek-ics/antiweb_testing-suite
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)
 incommatose/cve-2023-6063-poc
A Proof on Concept for CVE-2023-6063, a time-based blind SQL injection vulnerability in WP Fastest Cache ≤1.2.2.
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 folks-iwd/cve-2025-68999-poc
PoC exploit for CVE-2025-68999 - Second-Order SQL Injection in Happy Addons for Elementor <= 3.20.4
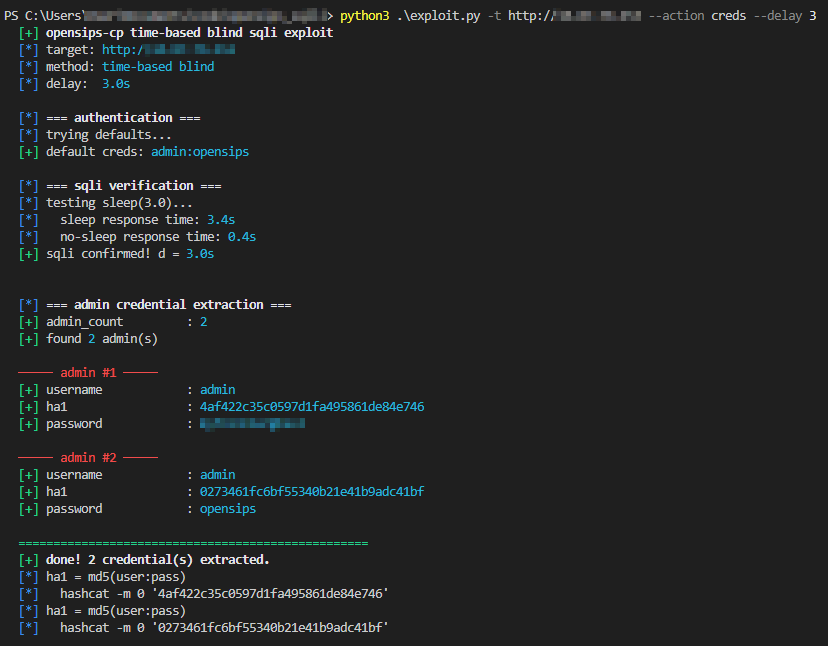 gabriel-lacorte/cve-2026-36670
Pre-auth SQL Injection Exploit for the OpenSIPs Control Panel