
EIPP
 synacktiv/eipp
Entra ID Password Protection Banned Password Lists
authenticationcloud-securityconfiguration-auditing+4
synacktiv/eippEntra ID Password Protection Banned Password Lists
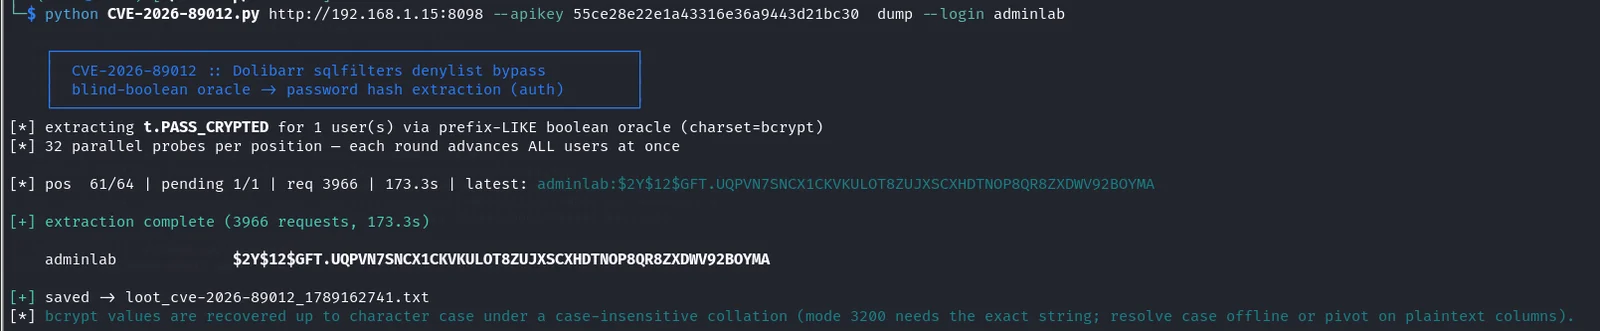 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 jas502n/nfc-ic-keys-dict
keys for ic
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 x3rx3ssec/cve-2022-0169
CVE-2022-0169 - WordPress Photo Gallery SQLi PoC
 brodsbytes/cyberpup
A free, open-source cybersecurity app for non techy people.
 dopaminauta/onetwoseven-writeup
HTB OneTwoSeven full walkthrough: deterministic creds, chroot symlink escape, rewrite-rule bypass RCE, CVE-2024-1086 to root
 gquere/cve-2018-16987
Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…
 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
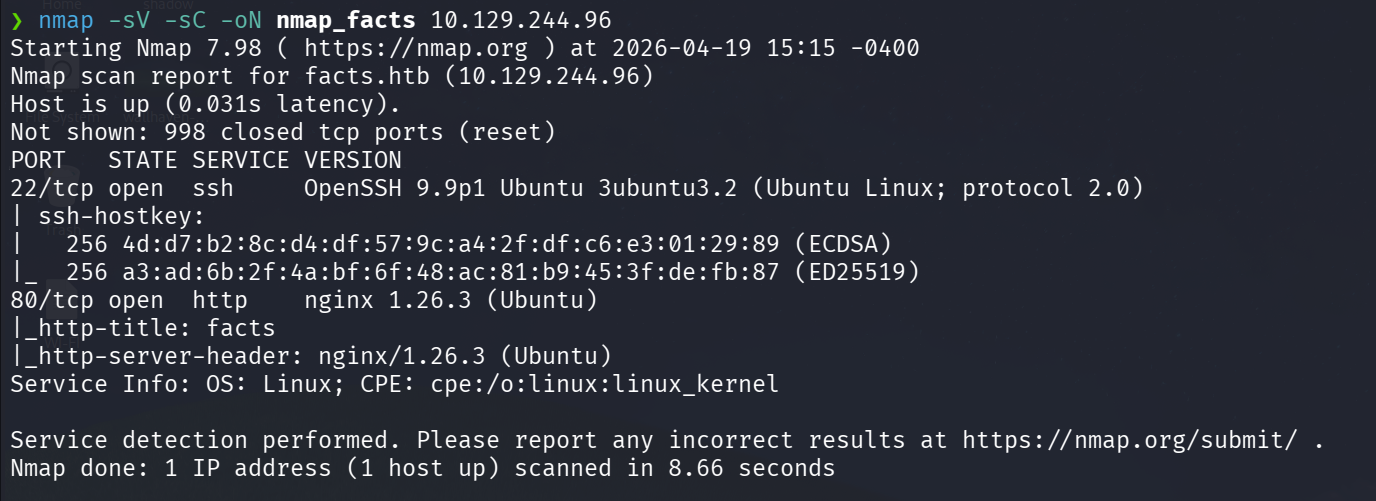 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 karimelsheikh1/htb-pterodactyl-writeup
HTB Season 10 - Pterodactyl machine writeup. Medium Linux box covering CVE-2025-49132 (Pterodactyl Panel RCE) and CVE-2025-6018/6019 (udisks2…
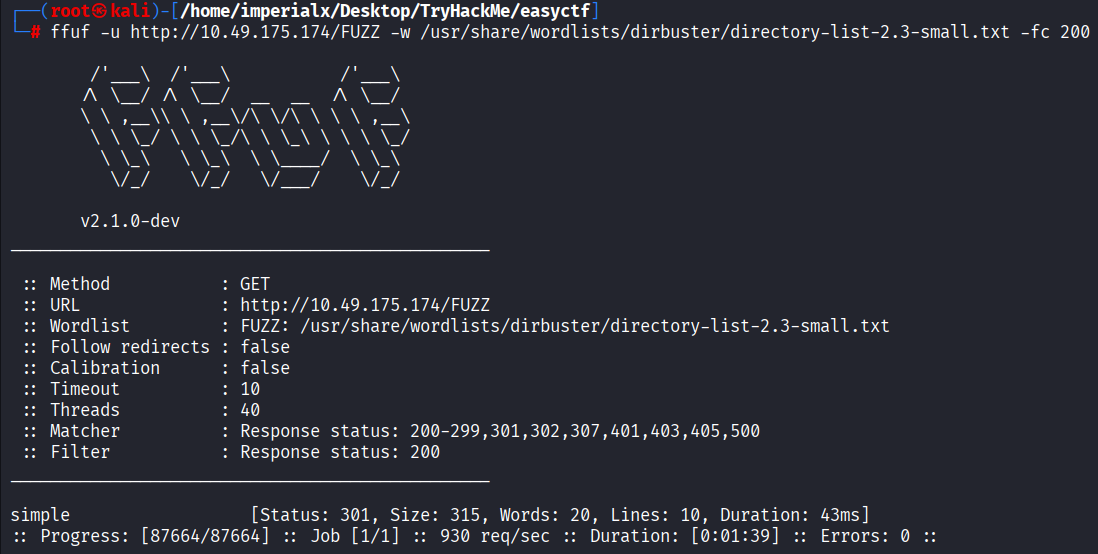 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 teymurnovruzov/cve-2019-9053-python3-remastered
The script has been remastered by Teymur Novruzov to ensure compatibility with Python 3. This tool is intended for educational purposes only.…
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…