PyLadon
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
command-and-controlexploitationlateral-movement+6
535 years ago
k8gege/pyladonLadon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 hotpotcookie/cve-2022-44877-white-box
Red Team utilities for setting up CWP CentOS 7 payload & reverse shell (Red Team 9 - CW2023)
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 saqib-butt2/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 si-ni/cve-2025-29927-proof-of-concept
Capture the Flag challenge: CVE-2025-29927 in combination with a command injection vulnerability
 fbm31/audit-blackbox-web-to-root
Audit de sécurité Black Box d'un serveur Drupal 7. Démonstration d'une Kill Chain complète : Injection SQL (CVE-2014-3704) ➔ RCE ➔ Reverse Shell ➔…
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)
 yen223/hotpot
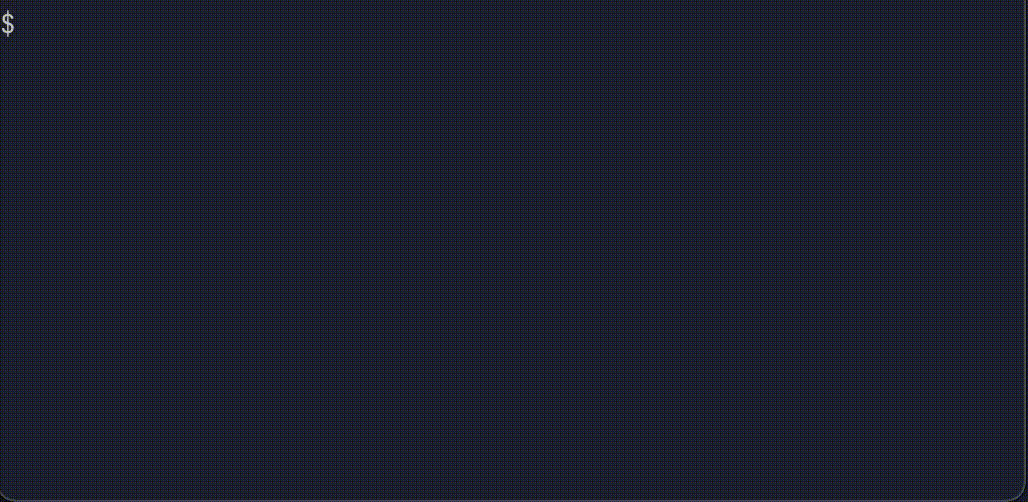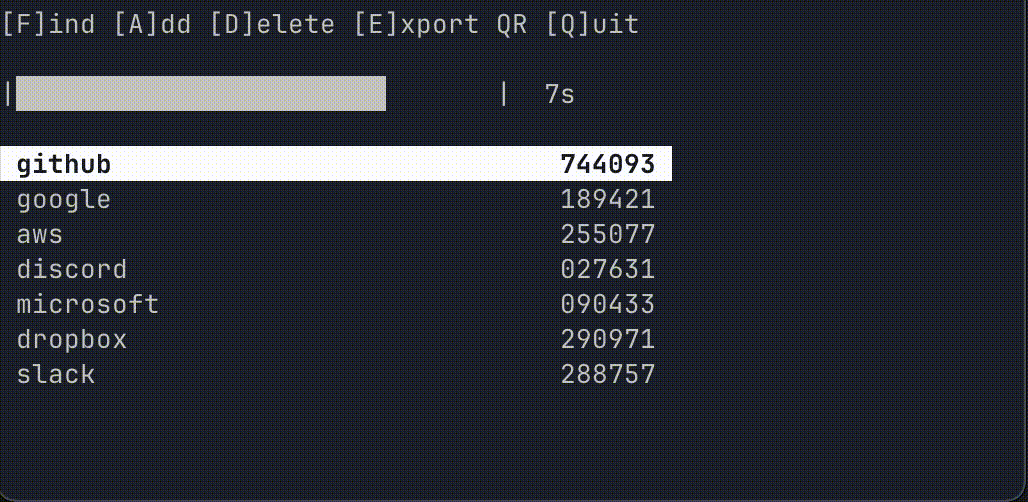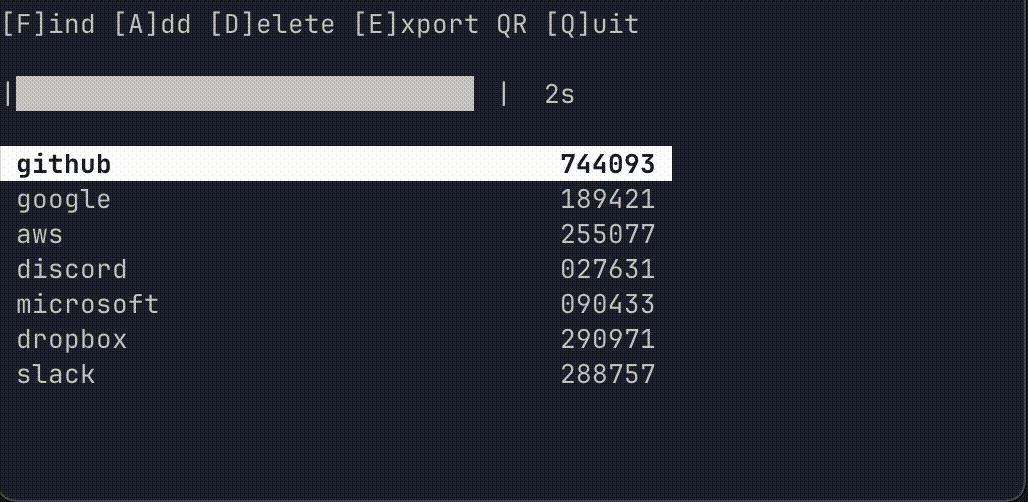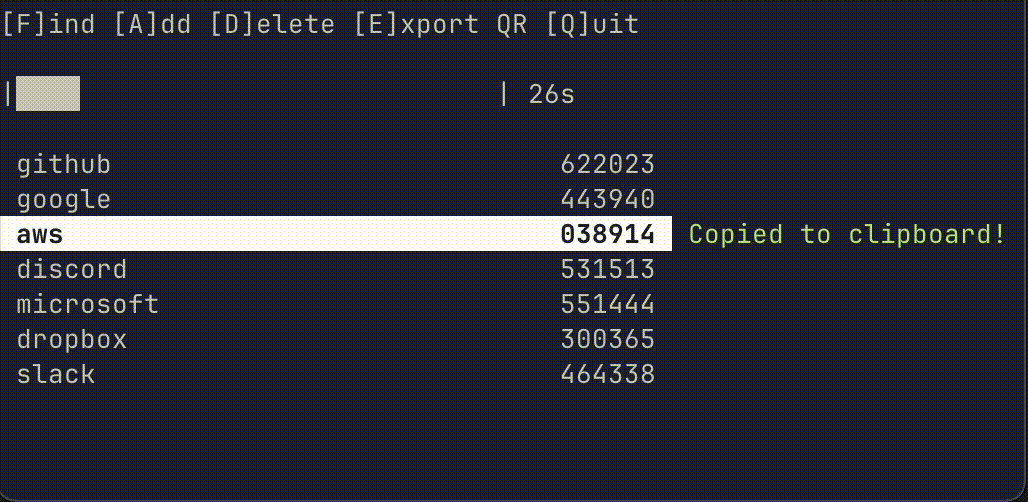
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.
 mbadanoiu/cve-2020-13941
CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram