
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
cve-2019-9053-py3 preview

cve-2019-9053-py3

GitHubvedantrana73/cve-2019-9053-py3

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
educationexploitationpassword-cracking+3
3 months ago
poc-CVE-2019-9053 preview

poc-CVE-2019-9053

GitHubrideckszz/poc-cve-2019-9053

PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
ctfeducationlabs-practice+3
13 months ago
CVE-2019-9053-exploit preview

CVE-2019-9053-exploit

GitHubjeanback1/cve-2019-9053-exploit

Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
exploitationinformation-gatheringpassword-cracking+3
4 months ago
Simple-CTF-Writeup preview

Simple-CTF-Writeup

GitHubimperialx1104/simple-ctf-writeup

Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…

ctfeducationexploitation+6
4 months ago
SimpleCTF-THM-Walkthrough preview

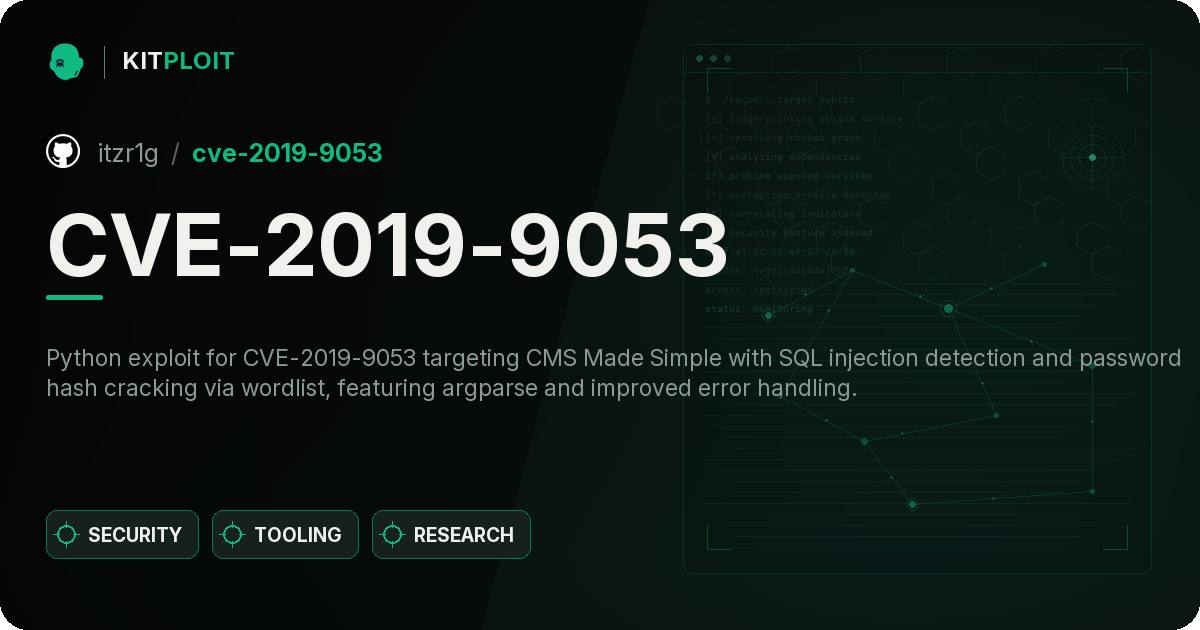
SimpleCTF-THM-Walkthrough

GitHubpaulameg/simplectf-thm-walkthrough

First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
ctfeducationpassword-cracking+5
14 months ago
CVE-2019-9053 preview

CVE-2019-9053

GitHubitzr1g/cve-2019-9053

Python exploit for CVE-2019-9053 targeting CMS Made Simple with SQL injection detection and password hash cracking via wordlist, featuring argparse…

educationexploitationpassword-cracking+3
5 months ago
CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit preview

CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

GitHubelizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

exploitationpassword-crackingpenetration-testing+2
55 months ago
cmsms-sqli preview

cmsms-sqli

GitHubtim-karov/cmsms-sqli

Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.

ctfexploitationpassword-cracking+3
8 months ago
CVE-2019-9053-working- preview

CVE-2019-9053-working-

GitHubperseus99999/cve-2019-9053-working-

CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
ctfpassword-crackingpenetration-testing+2
110 months ago
cms-made-simple-python3 preview

cms-made-simple-python3

GitHubjagdeepsinghceh/cms-made-simple-python3

Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…

educationexploitationpassword-cracking+3
210 months ago
CVE-2019-9053-POC preview

CVE-2019-9053-POC

GitHubcaelumisme/cve-2019-9053-poc

Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
educationexploitationpassword-cracking+3
11 months ago
CMS-Made-Simple-2.2.9-CVE-2019-9053 preview

CMS-Made-Simple-2.2.9-CVE-2019-9053

GitHubboon-rekcah/cms-made-simple-2.2.9-cve-2019-9053

Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…

exploitationpassword-crackingpenetration-testing+2
1 year ago
CVE-2019-9053 preview

CVE-2019-9053

GitHubkalidas-7/cve-2019-9053

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…

exploitationinformation-gatheringpassword-cracking+3
1 year ago
CVE-2022-0169 preview

CVE-2022-0169

GitHubx3rx3ssec/cve-2022-0169

CVE-2022-0169 - WordPress Photo Gallery SQLi PoC

educationexploitationinformation-gathering+3
31 year ago
CVE-2019-9053-port-py3 preview

CVE-2019-9053-port-py3

GitHubdel0x3/cve-2019-9053-port-py3

CVE-2019-9053.
educationexploitationpassword-cracking+3
1 year ago
CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053- preview

CMS-Made-Simple-2.2.9-Unauthenticated-SQL-Injection-Exploit-CVE-2019-9053-

GitHubhf3cyber/cms-made-simple-2.2.9-unauthenticated-sql-injection-exploit-cve-2019-9053-

Time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9 (CVE-2019-9053) that extracts username, email, password hash, and salt, with…
exploitationinformation-gatheringpassword-cracking+3
1 year ago
CVE-2019-9053-Exploit-Python-3 preview

CVE-2019-9053-Exploit-Python-3

GitHubmahamedm/cve-2019-9053-exploit-python-3

The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.

exploitationpassword-crackingpenetration-testing+2
81 year ago
shirocrack preview

shirocrack

GitHuban00brektn/shirocrack

Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.

exploitationhash-analysispassword-cracking+2
21 year ago
Previous12Next