
SecLists
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
ctfcurated-resourcesdns-fuzzing+11
73.8k
danielmiessler/seclistsCurated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 beemdevelopment/aegis
A free, secure and open source app for Android to manage your 2-step verification tokens.
 zzzteph/weakpass
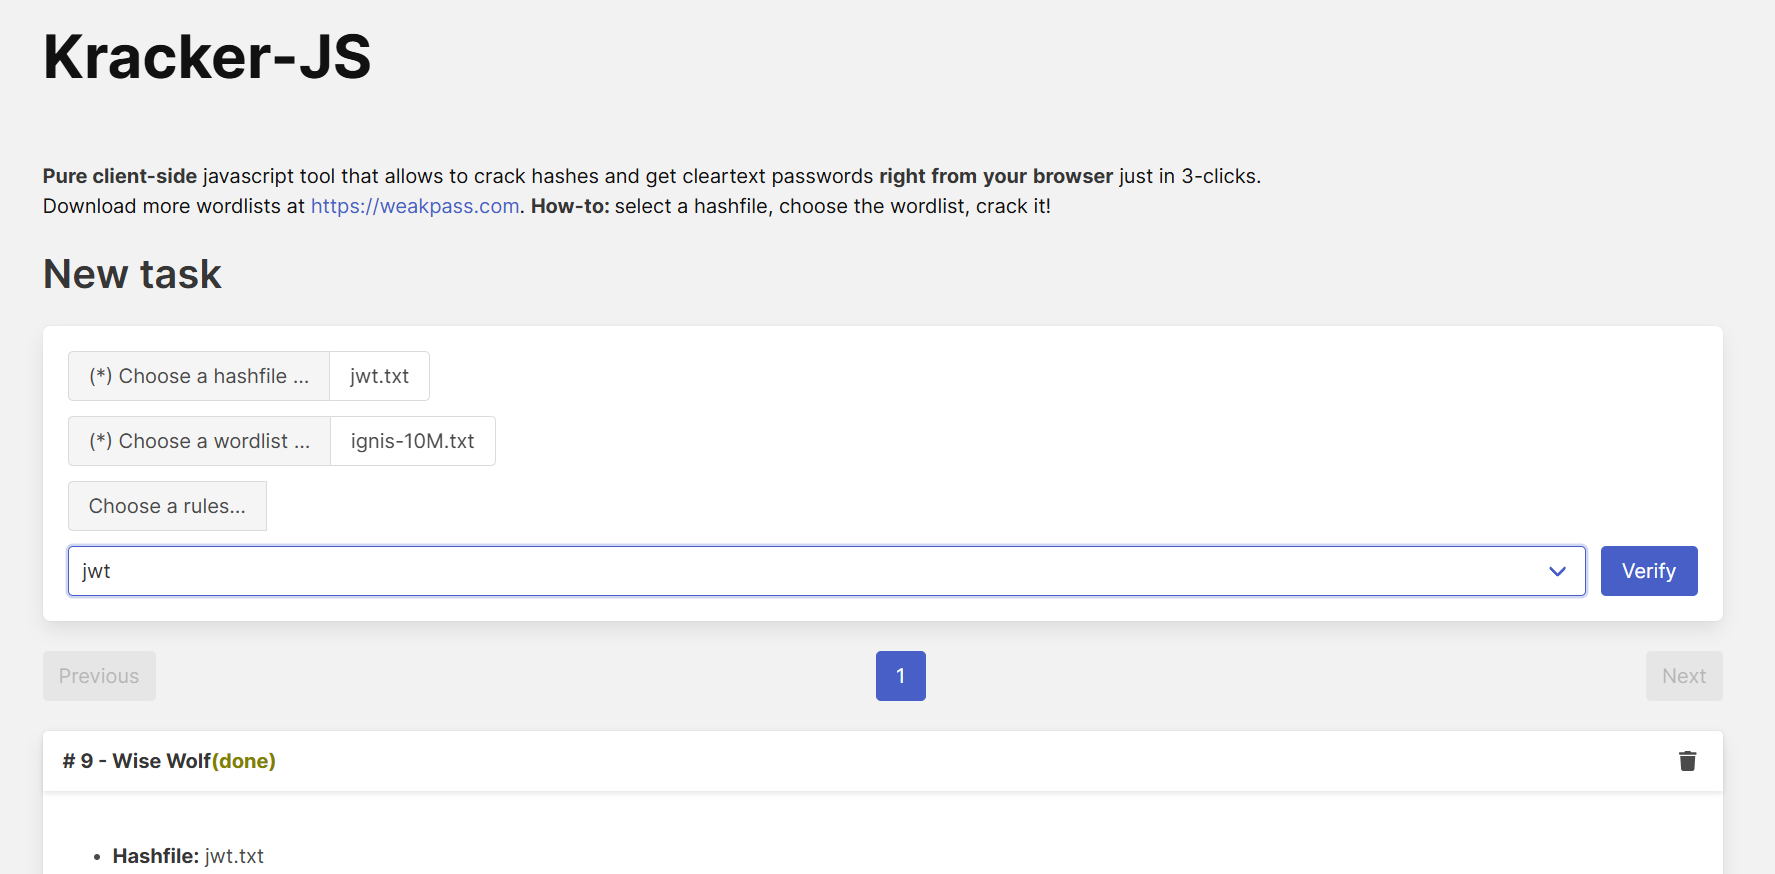
Browser-based password cracking toolkit with hash lookup, wordlist generation, rule-based attack simulation, and client-side hash cracking for…
 garagehq/nightcrawler
Local AI powered red teamer on a phone
 mebus/cupp
Interactive password profiler that generates targeted wordlists by gathering personal details about a user, used for penetration testing and forensic…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 helviojunior/knowsmore
Correlates NTLM hashes, BloodHound data, and cracked passwords for Active Directory penetration testing. Imports NTDS.dit, syncs to Neo4j, analyzes…
 vedantrana73/cve-2019-9053-py3
Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.
 ibnaleem/rules
Curated collection of Hashcat password-cracking rules with benchmark data, designed to help red teams and penetration testers crack complex passwords…
 sup3rdav3/cve-2025-4396
CVE-2025-4396 - WordPress Relevanssi Time-Based Blind SQL Injection
 s_r_e_e_r_a_j/ziprarhunter
ZipRarHunter is a powerful command-line ethical hacking tool designed to crack passwords of ZIP and RAR archive files using a wordlist.
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 klynezyro/metasploitable2-vapt-report
Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…