

pwned
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
information-gatheringosintpassword-cracking+1
246
wkovacs64/pwnedCLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction
 ledksv/monitorsfour
HackTheBox MonitorsFour walkthrough covering credential leak, CVE-2025-24367 Cacti RCE, and CVE-2025-9074 Docker Desktop API container escape to root.
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 skelsec/pypykatz
Mimikatz implementation in pure Python
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
 yucaerin/cve-2024-55555
Laravel Crypto Killer Mass Scanner (CVE-2024-55555)

 joelgmsec/leaksearch
Searches and parses plaintext passwords from public breach databases (ProxyNova COMB) by keyword (user/domain/password), with proxy support and…
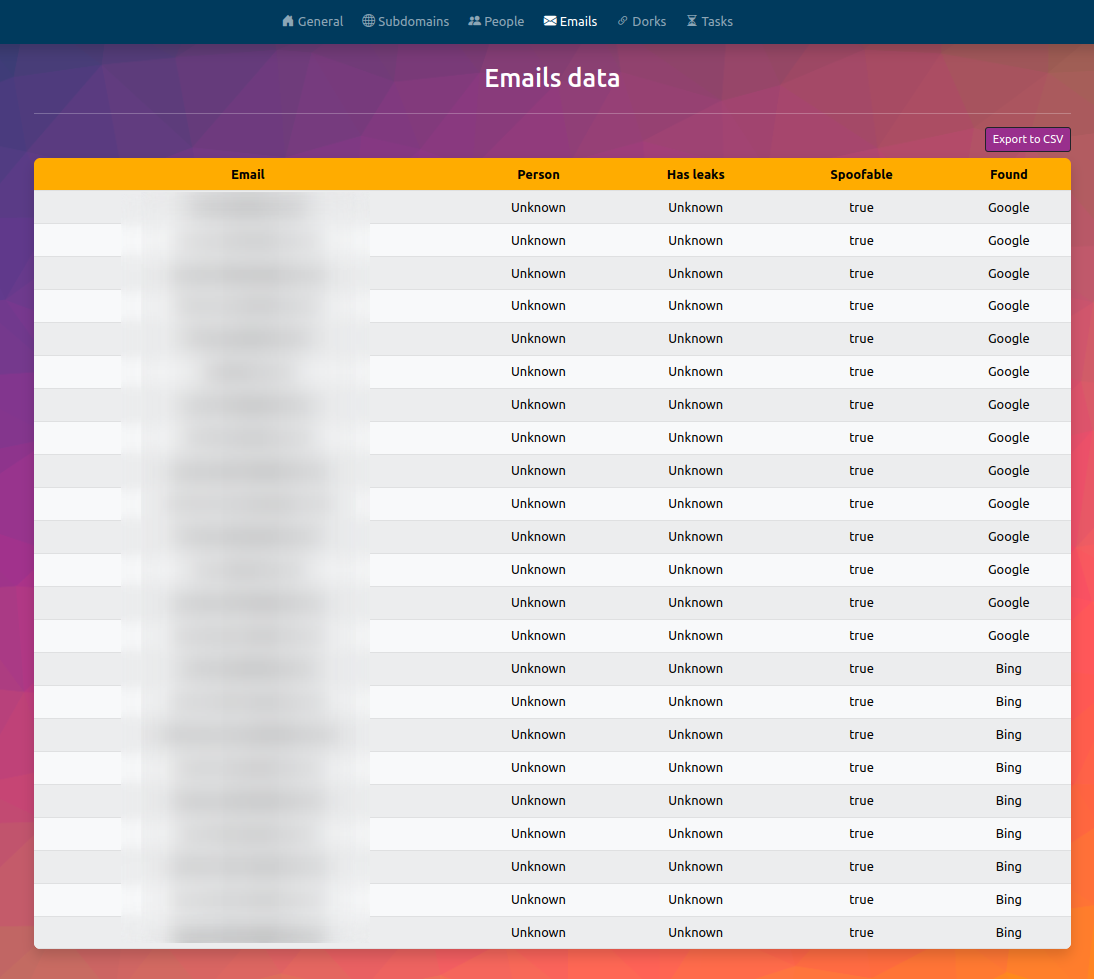 fundacio-i2cat/infohound
InfoHound is an OSINT to extract a large amount of data given a web domain name.
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 r00tb1t/cve-2024-21413-poc
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - CVE-2024-21413 POC