
even-you-brutus
 j-baines/even-you-brutus
Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
authenticationembedded-systems-securityexploitation+5
9
j-baines/even-you-brutusDictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 0xsyr0/vx-underground-wordlist
Wordlist to crack .zip-file password
 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 ignis-sec/pwdb-public
A collection of all the data i could extract from 1 billion leaked credentials from internet.
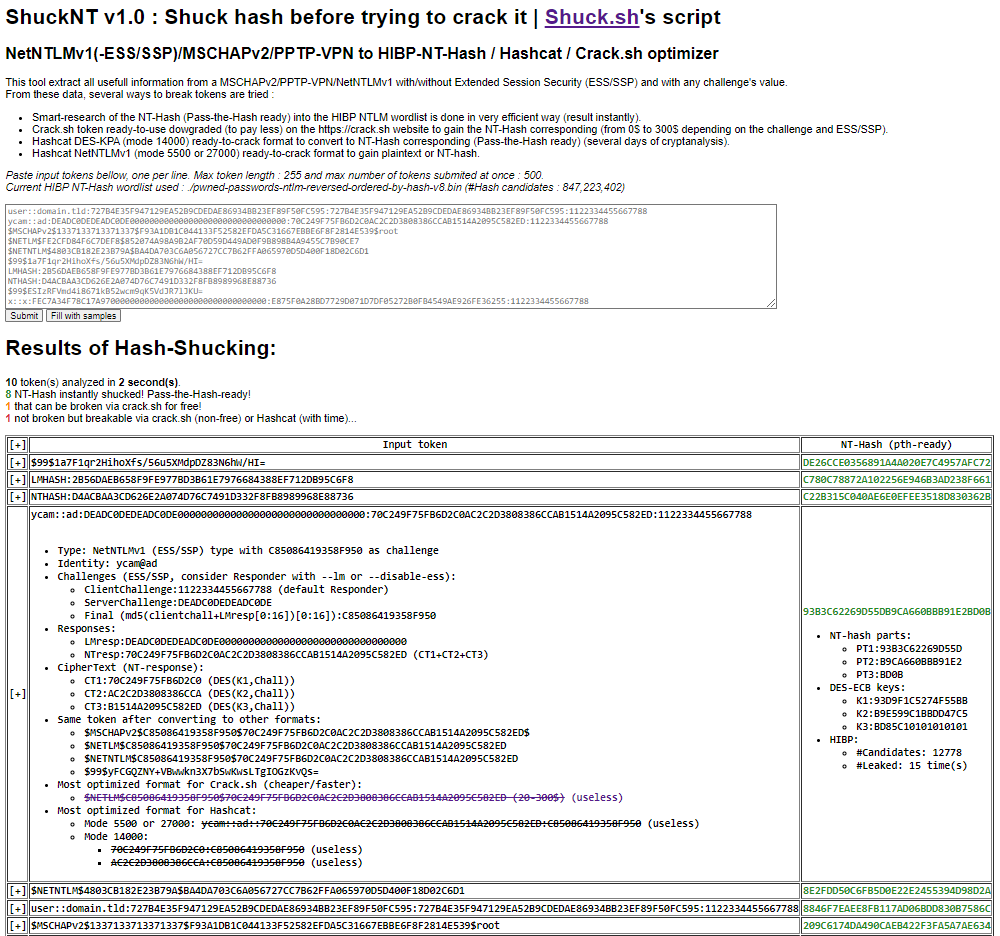 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…