
voidsec-proxy
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
data-exfiltrationdigital-forensicsdns-subdomain-enumeration+8
4
voidsecsoftwares/voidsec-proxyMulti-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 joelgmsec/cloudtopolis
Zero Infrastructure Password Cracking
 michaeldim02/narthex
Modular personalized dictionary generator.
 amitr12/cybersec
Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
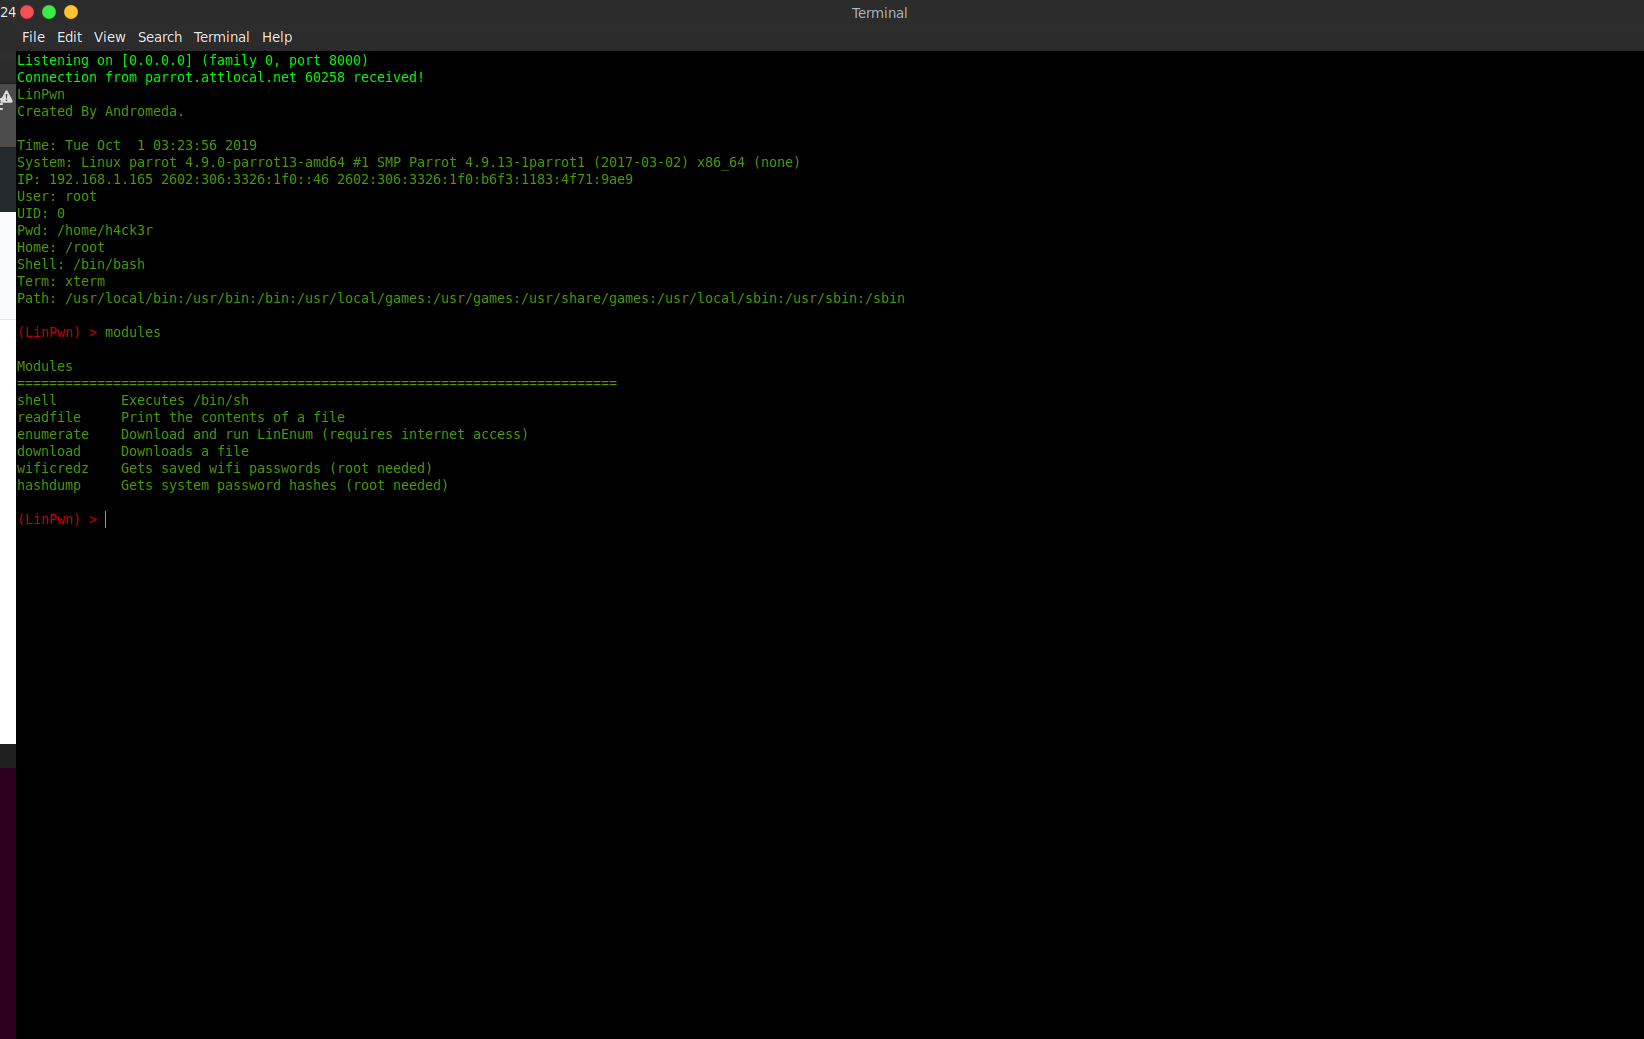 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
 fbm31/audit-blackbox-web-to-root
Audit de sécurité Black Box d'un serveur Drupal 7. Démonstration d'une Kill Chain complète : Injection SQL (CVE-2014-3704) ➔ RCE ➔ Reverse Shell ➔…
 hotpotcookie/cve-2022-44877-white-box
Red Team utilities for setting up CWP CentOS 7 payload & reverse shell (Red Team 9 - CW2023)
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…