
Corporate_Masks
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
hash-analysispassword-attackspassword-cracking+3
205
golem445/corporate_masks8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 papermtn/lil-pwny
Fast offline auditing of Active Directory passwords using Python.
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
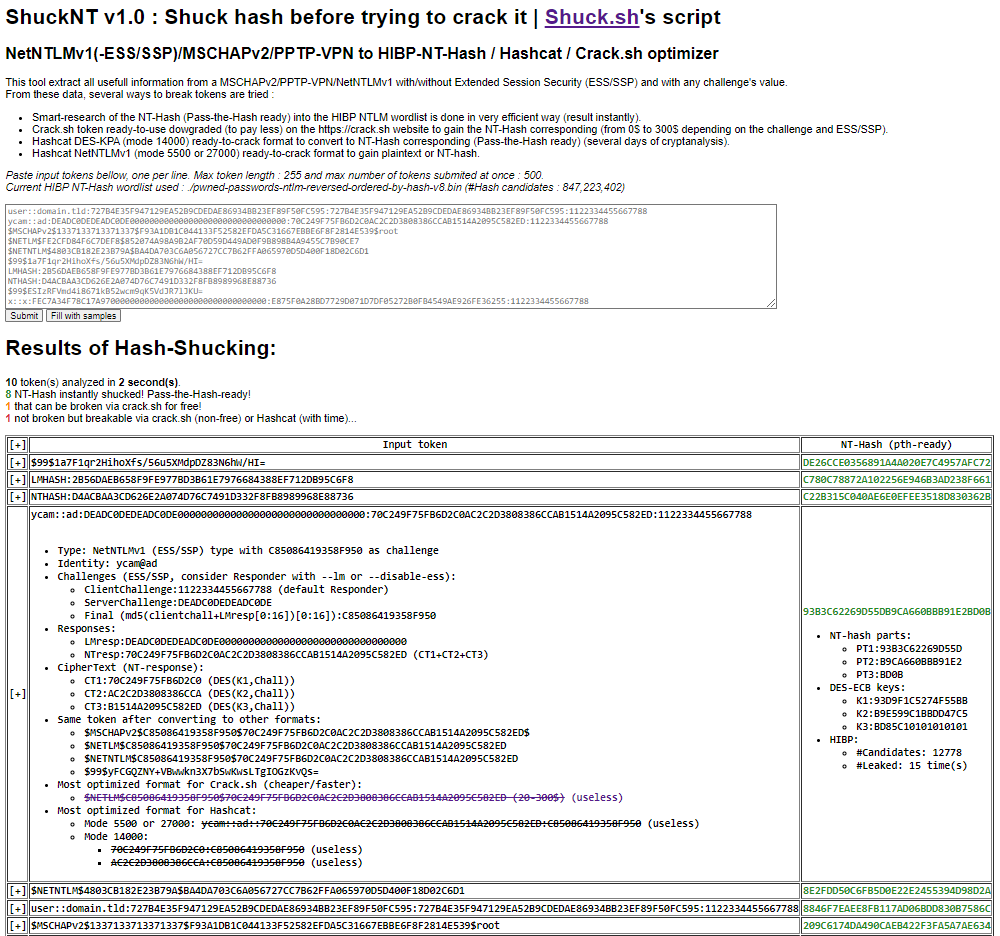 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
 joshuamart/pwnedpasswordschecker
Search (offline) if your password (NTLM or SHA1 format) has been leaked (HIBP passwords list v8)
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 evilmog/ntlmv1-multi
NTLMv1 Multitool
 helviojunior/knowsmore
Correlates NTLM hashes, BloodHound data, and cracked passwords for Active Directory penetration testing. Imports NTDS.dit, syncs to Neo4j, analyzes…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 f4dee-backup/cve-2025-24071
Exploit script for CVE-2025-24071 that leaks NTLM hashes from Windows by extracting a crafted ZIP/RAR file, exploiting .library-ms file handling.…
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…