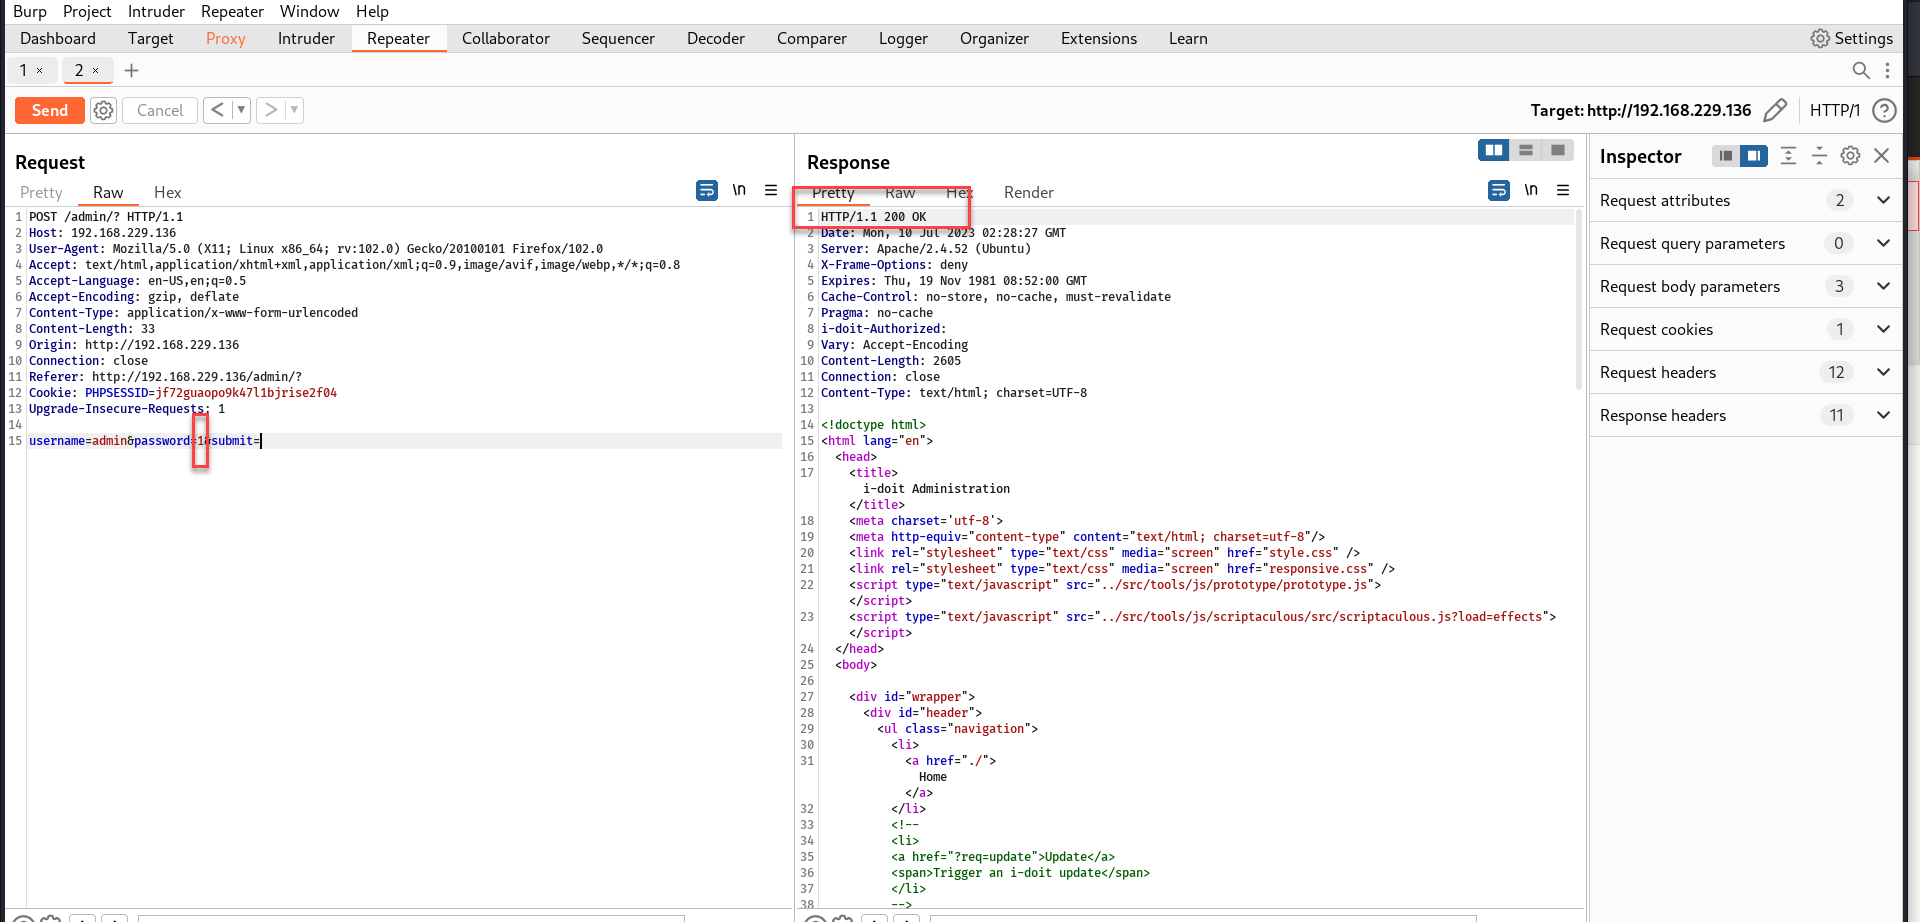
CVE-2023-37756-CWE-521-lead-to-malicious-plugin-upload-in-the-i-doit-Pro-25-and-below

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…

Proof-of-concept exploit for CVE-2020-7378 chaining predictable password reset token generation with blind XXE to gain admin access and exfiltrate…

lib/G/functions.php in Chevereto 1.0.0 through 1.1.4 Free, and through 3.13.5 Core, allows an attacker to perform bruteforce attacks without…

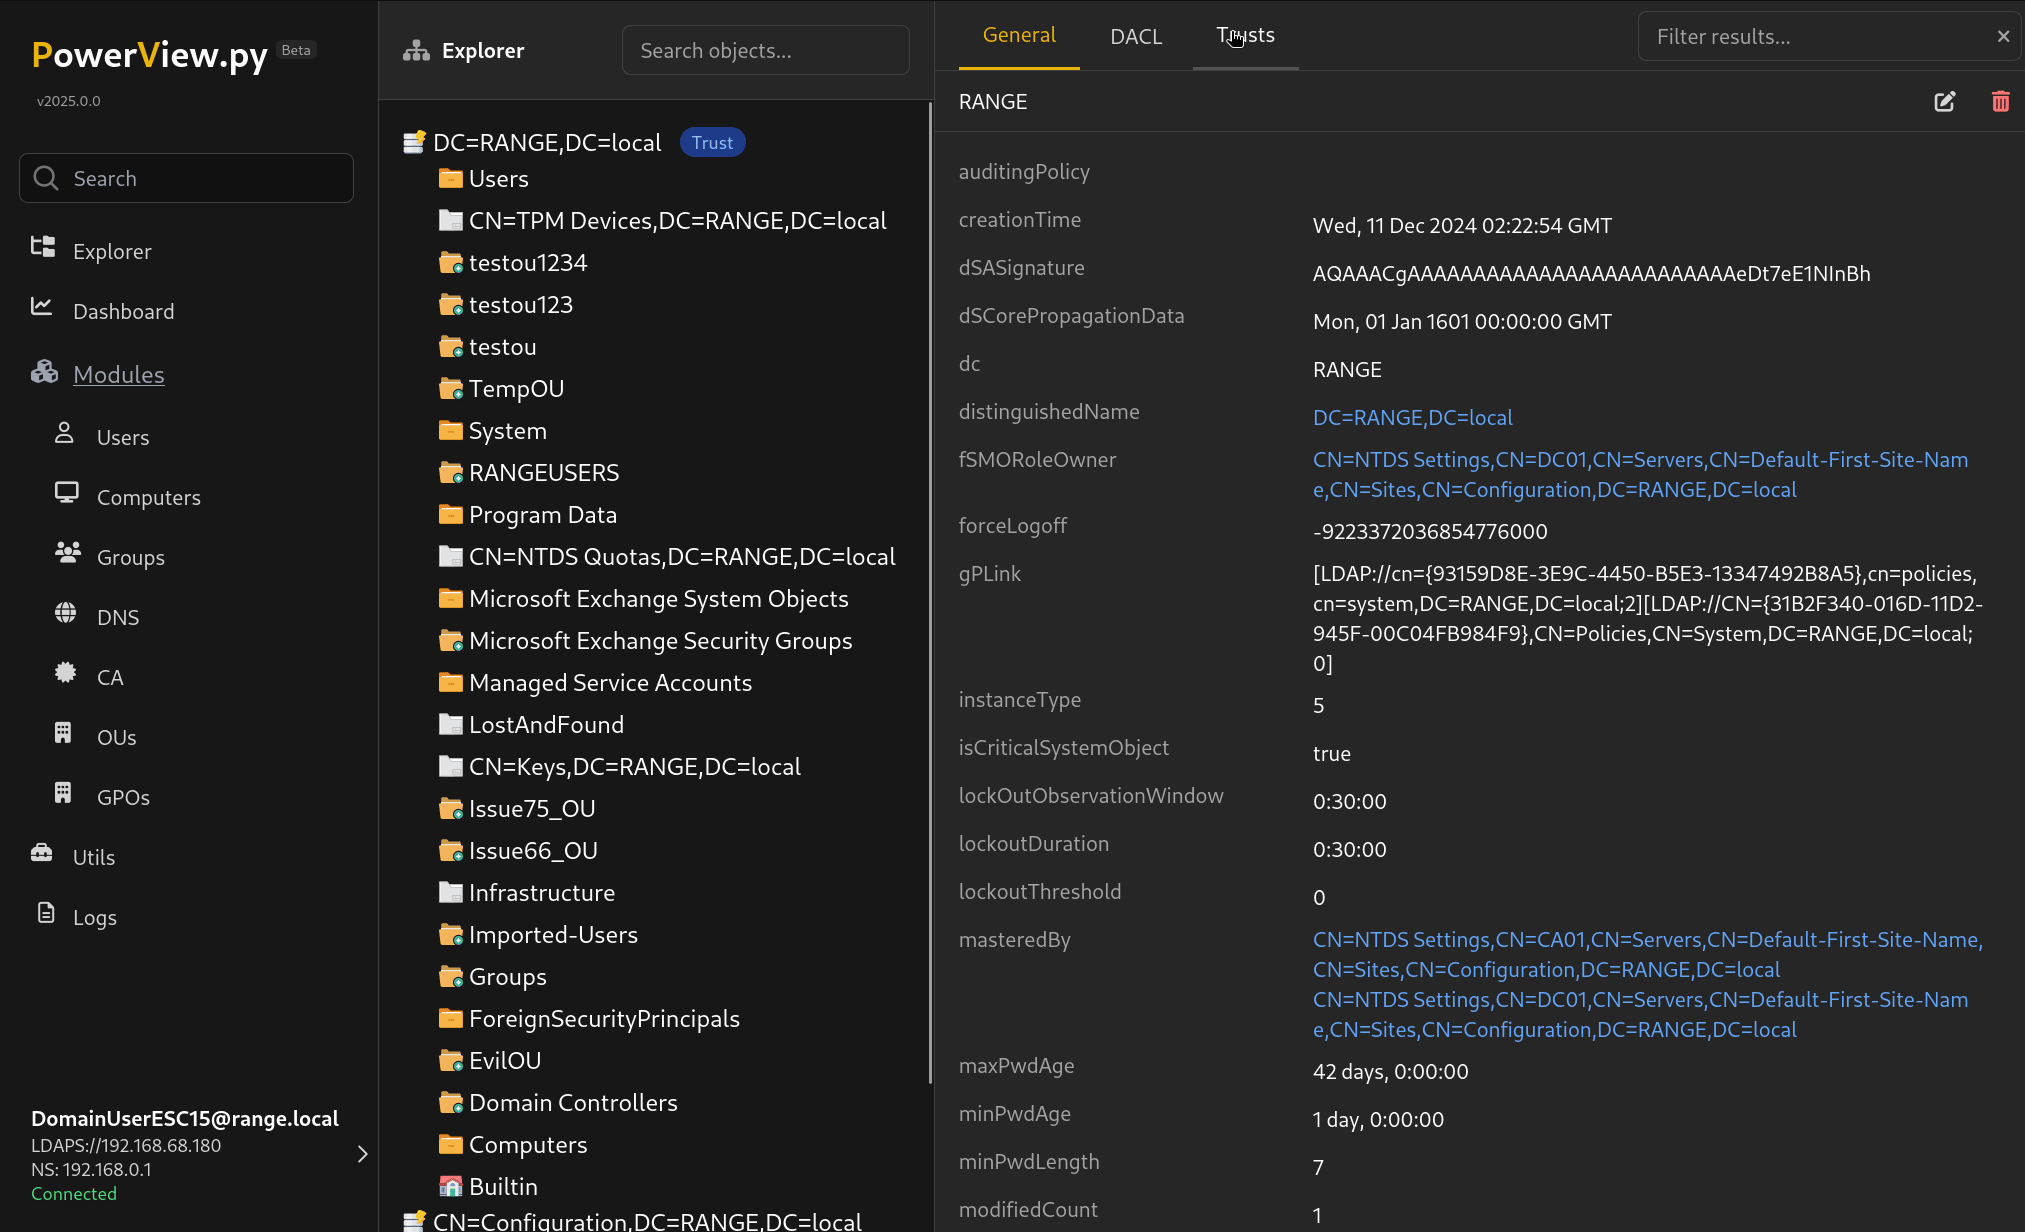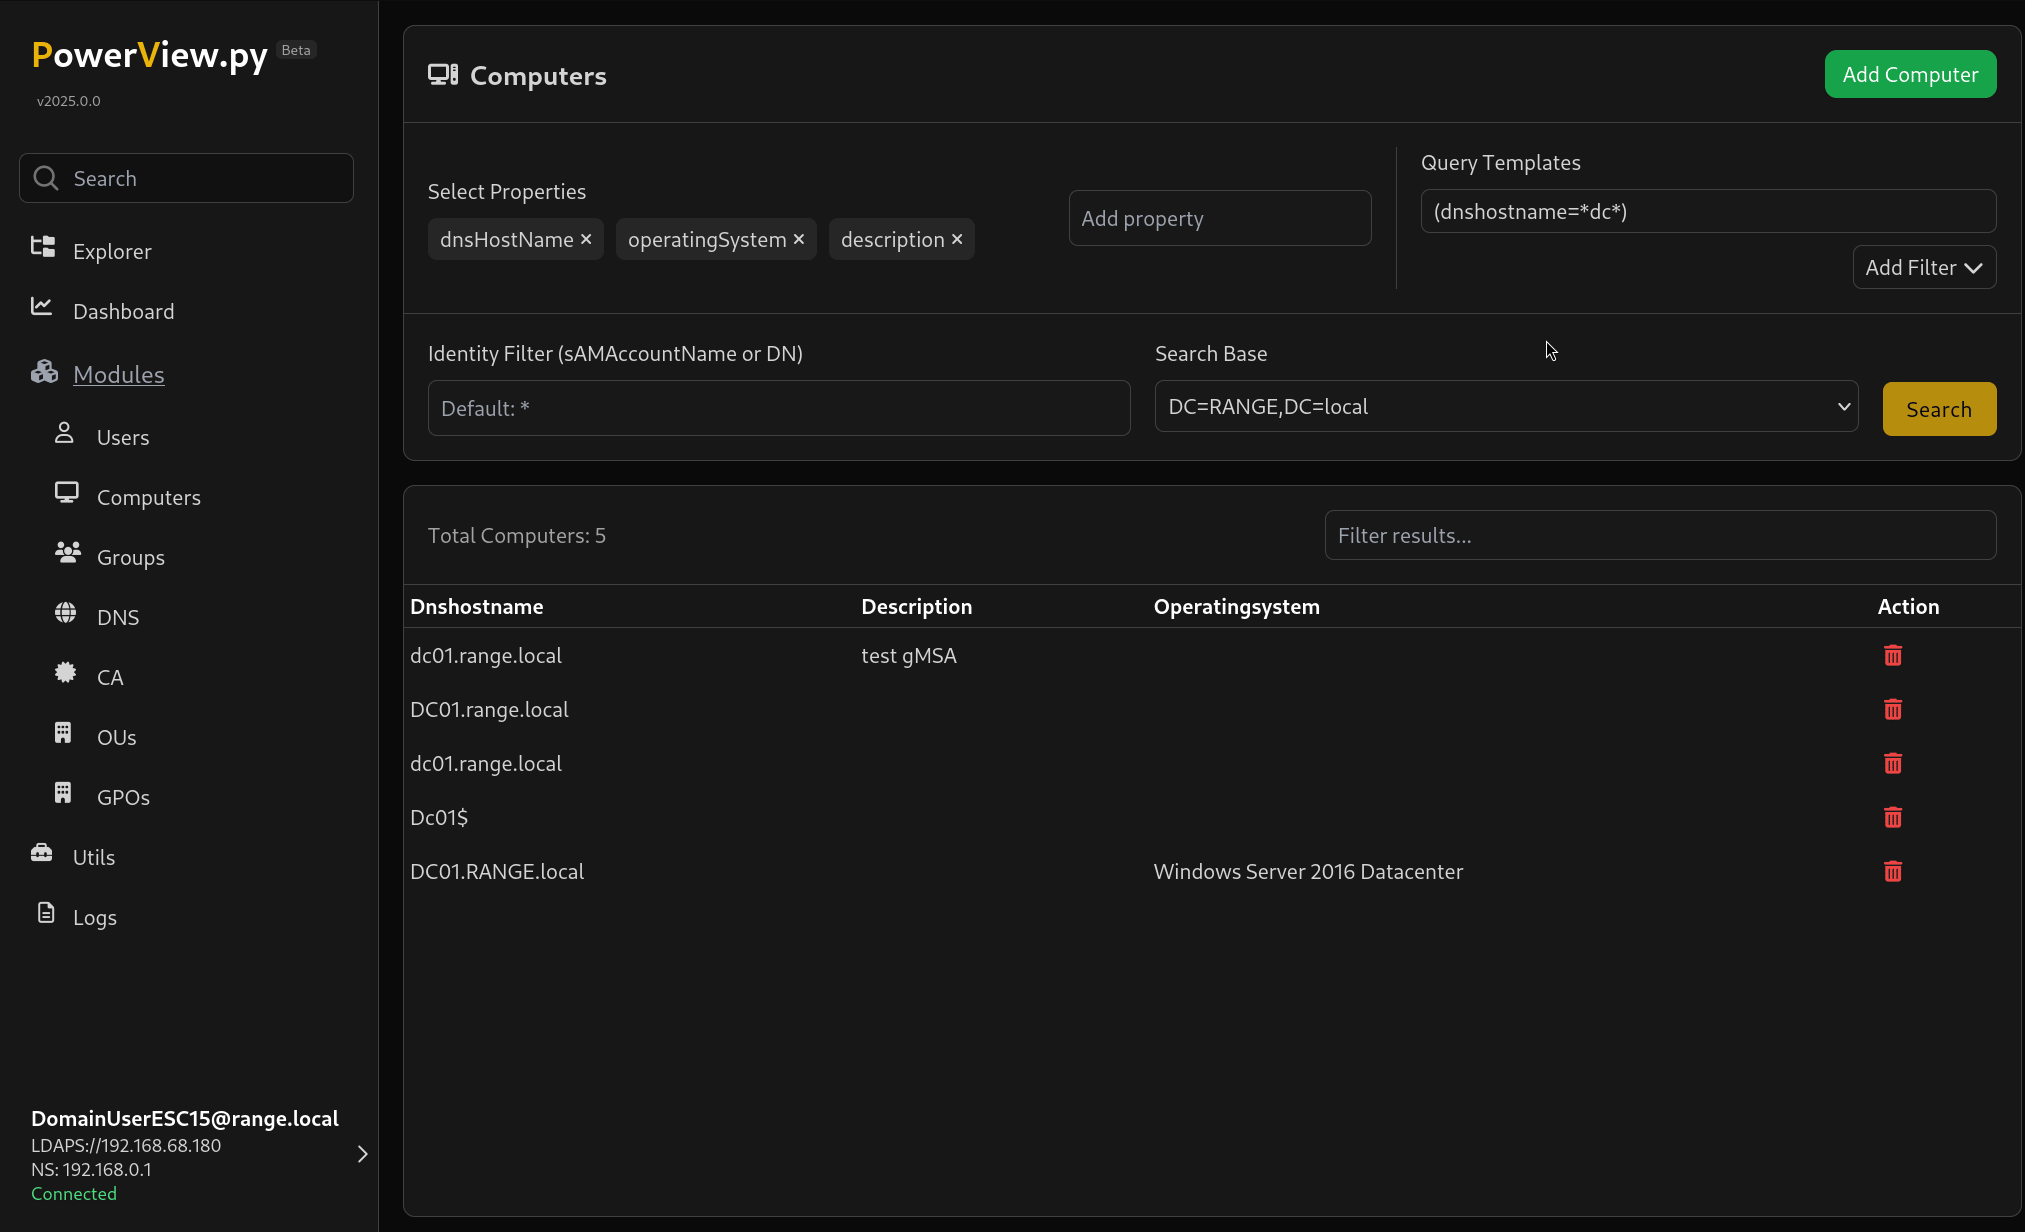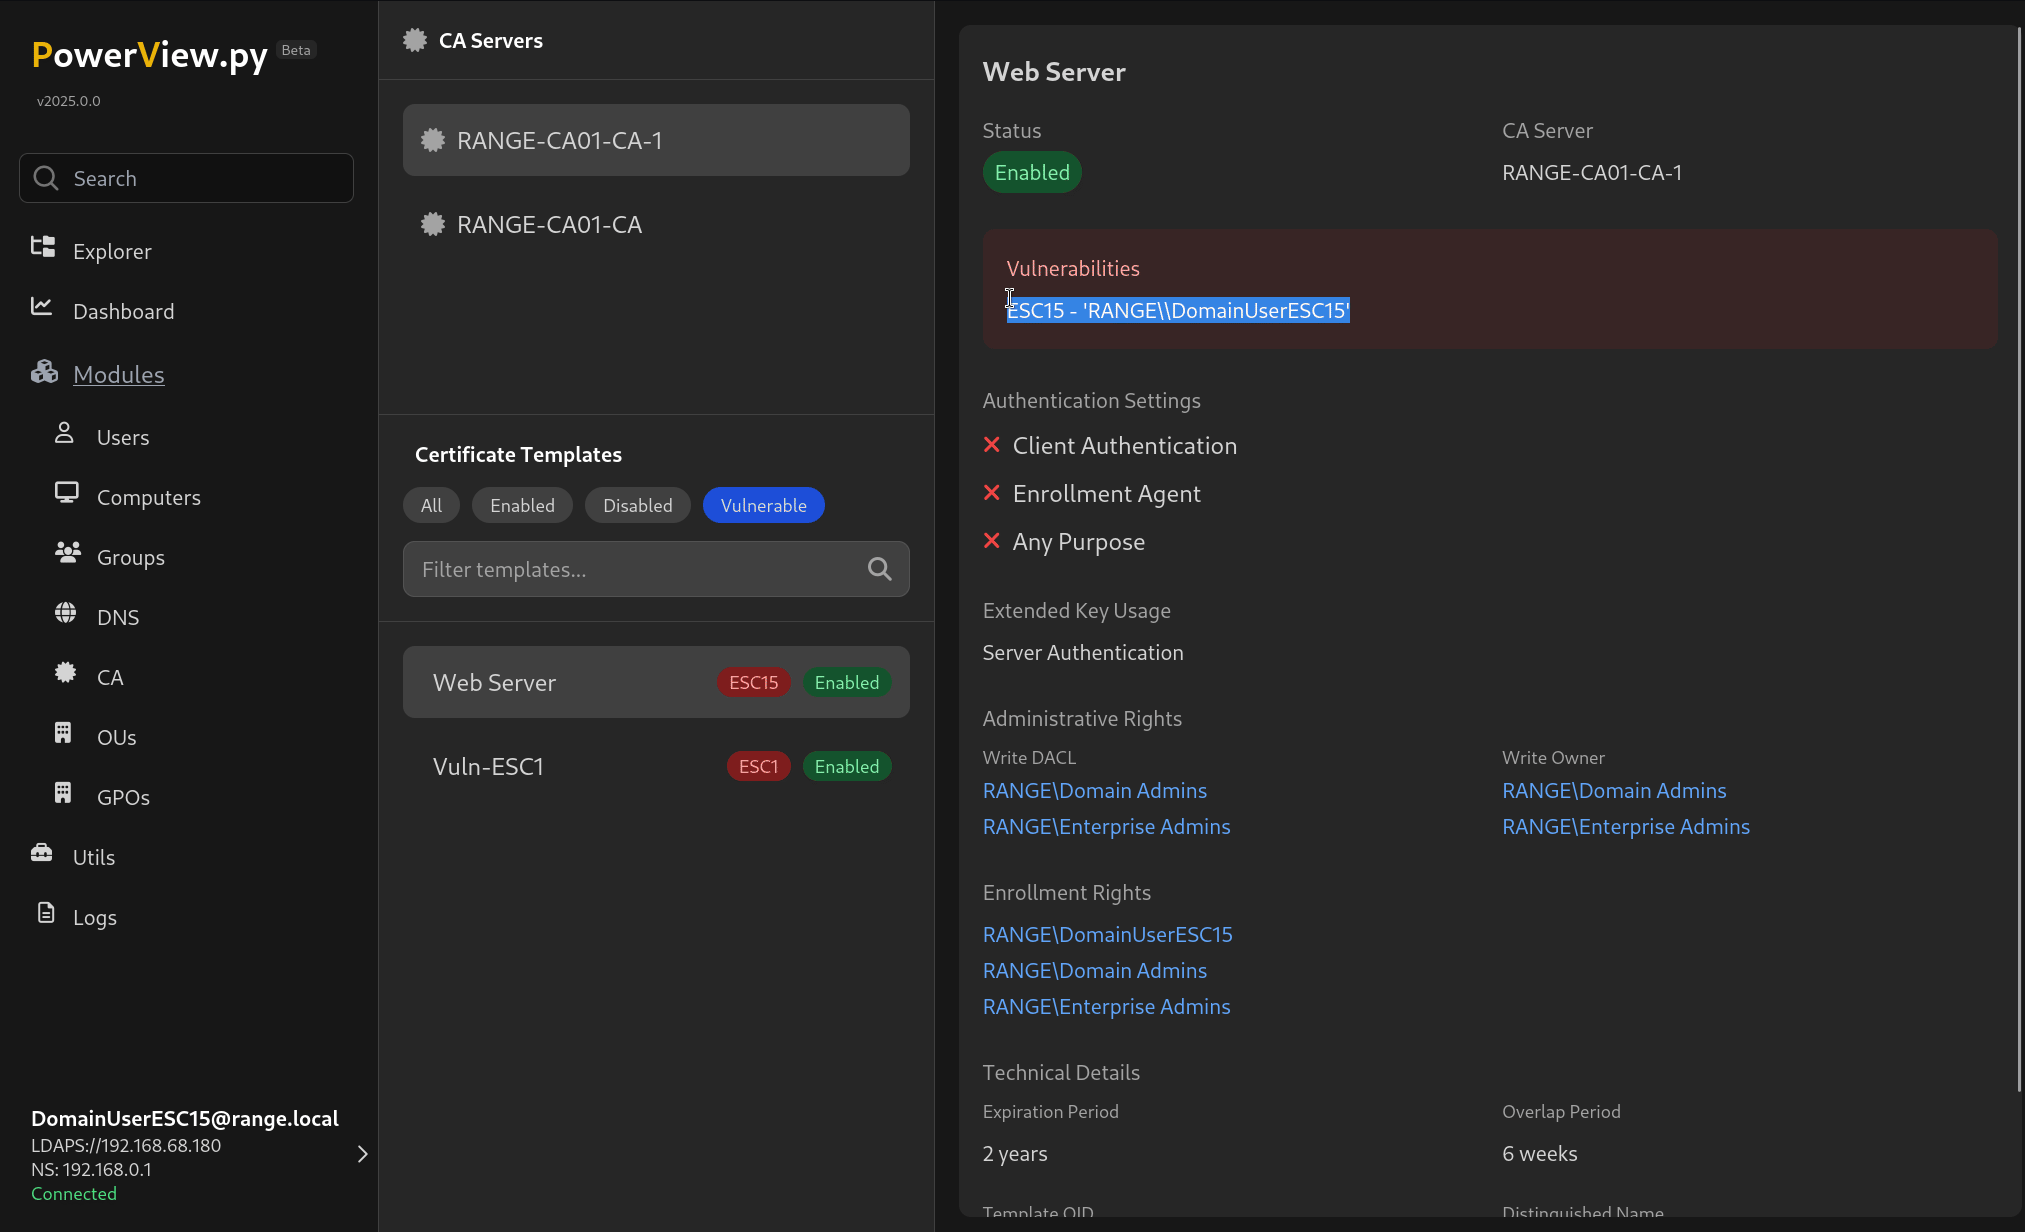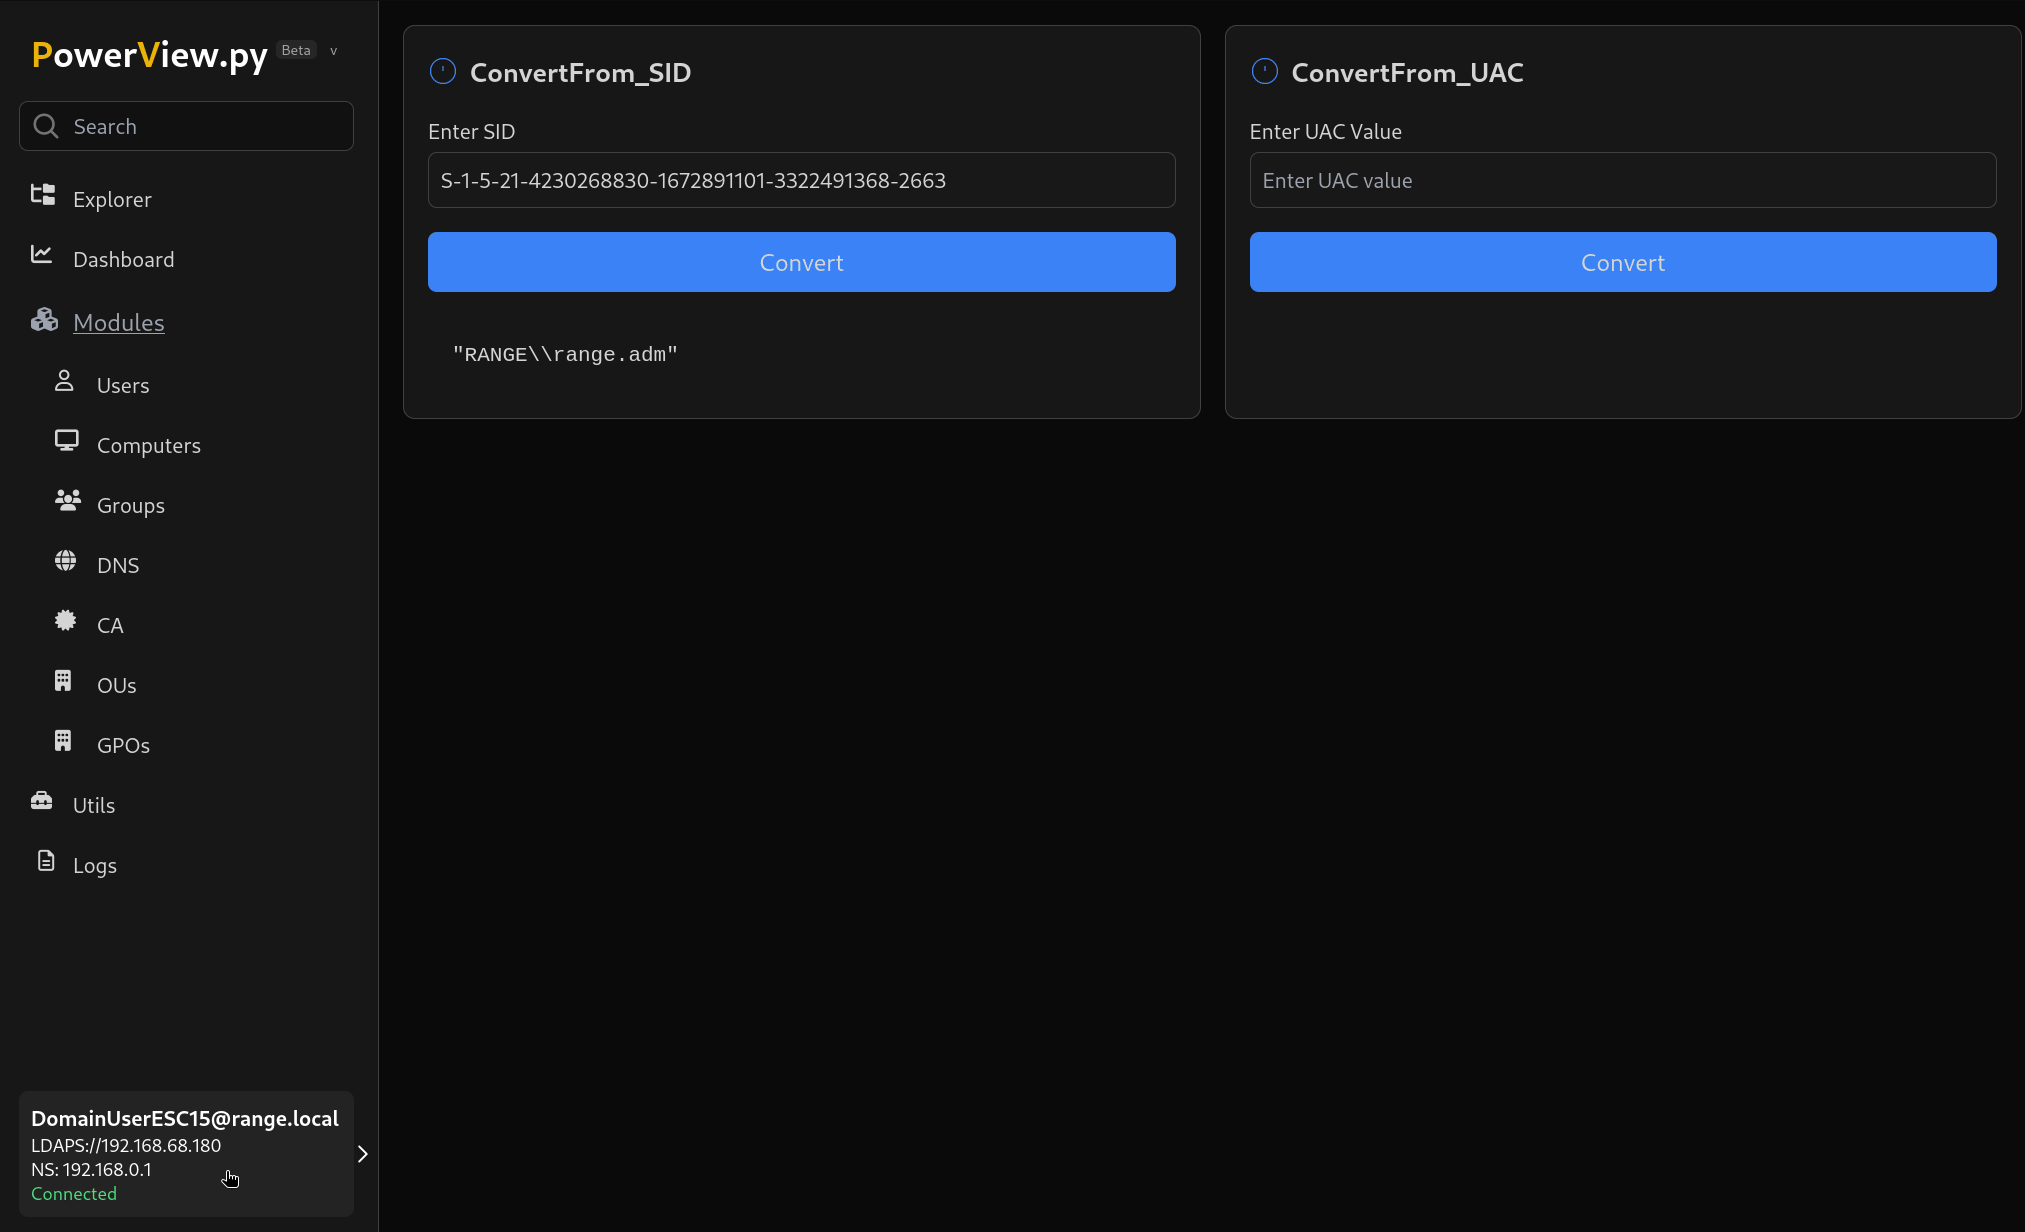
Powerview on steroids

Automated Linux evil maid attack

Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…

Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…

Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…