
CVE-2020-28874
 varandinawer/cve-2020-28874
CVE-2020-28874
exploitationpassword-attackspenetration-testing+3
varandinawer/cve-2020-28874CVE-2020-28874
 loganpkinfosec/cve-2020-7378
Proof-of-concept exploit for CVE-2020-7378 chaining predictable password reset token generation with blind XXE to gain admin access and exfiltrate…
 inflixim4be/cve-2020-15392
Proof-of-concept exploit for user enumeration vulnerability in Supravizio BPM 10.1.2 via password recovery response differences, enabling brute force…
 mods20hh/zerologon-poc-dc-pwn
Zerologon (CVE-2020-1472) Proof-of-Concept application - Critical Active Directory vulnerability exploitation tool.
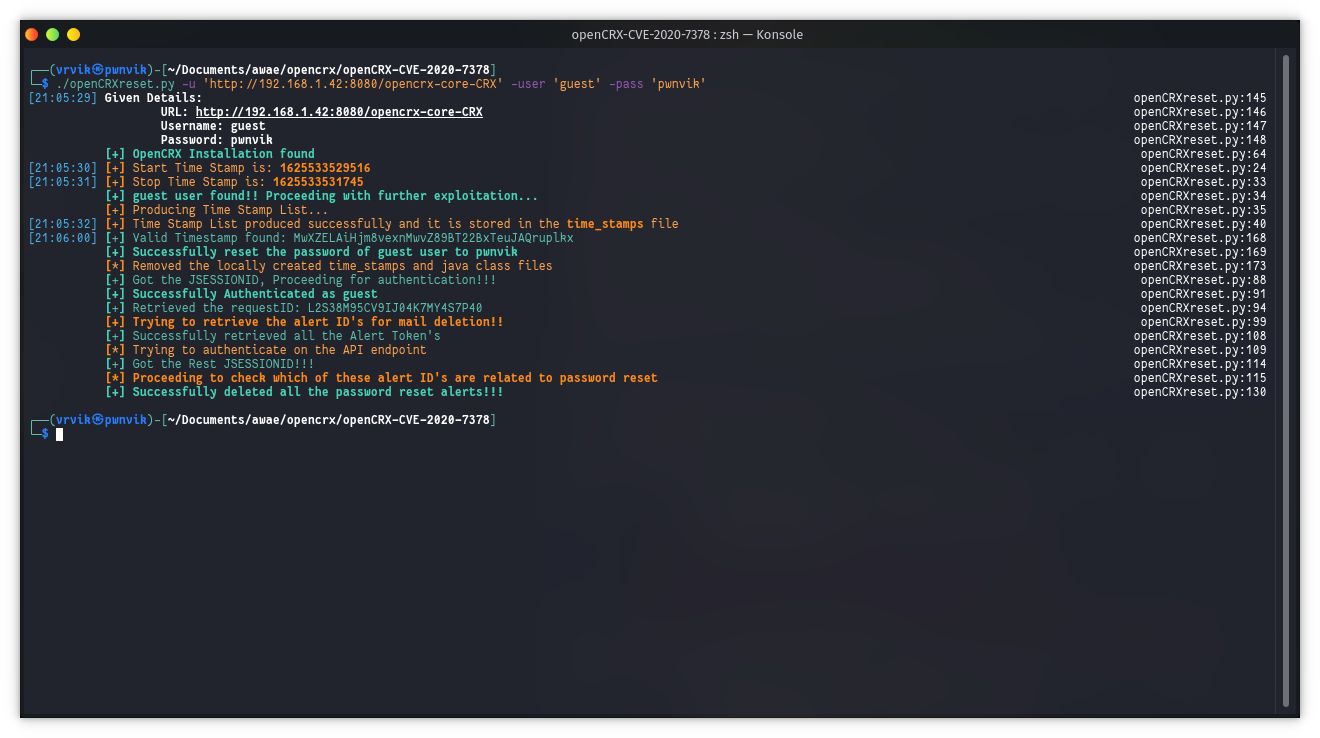 ruthvikvegunta/opencrx-cve-2020-7378
Exploits Password Reset Vulnerability in OpenCRX, CVE-2020-7378. Also maintains Stealth by deleting all the password reset mails created by the script
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 tuancui22/zerologonwithimpacket-cve2020-1472
A practical proof-of-concept for CVE-2020-1472 (Zerologon) using the Impacket library to exploit Netlogon vulnerability and perform unauthorized…
 code-byter/cve-2020-29669
Macally WIFISD2
 s1lkys/cve-2020-29669
Macally WIFISD2
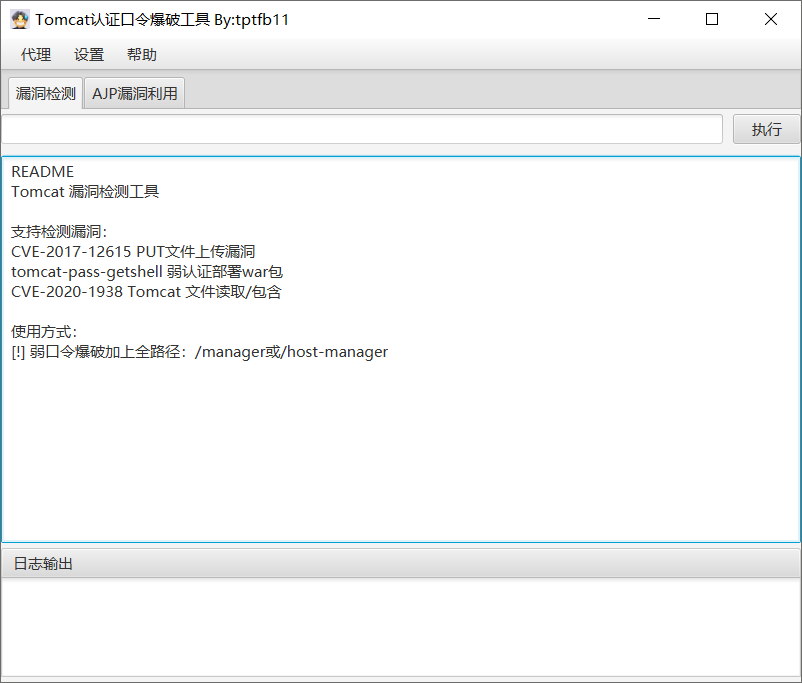 tpt11fb/attacktomcat
Tomcat常见漏洞GUI利用工具。CVE-2017-12615 PUT文件上传漏洞、tomcat-pass-getshell 弱认证部署war包、弱口令爆破、CVE-2020-1938 Tomcat AJP文件读取/包含
 n4nj0/cve-2020-35590
Brute-force tool for WordPress Plugin Limit Login Attempts Reloaded >=2.13.0 - Login Limit Bypass (CVE-2020-35590)
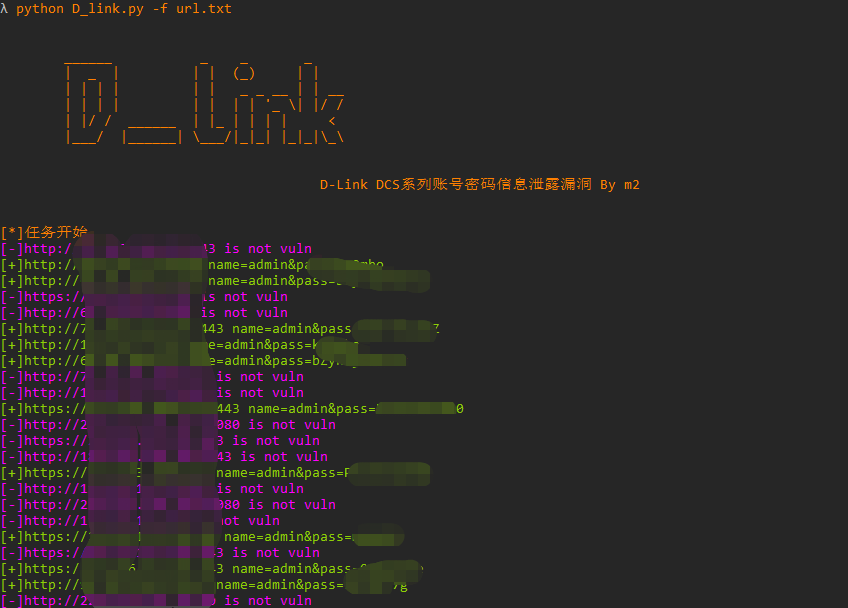 mzzdtot/cve-2020-25078
D-Link DCS系列账号密码信息泄露漏洞,通过脚本获取账号密码,可批量。
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 voidsec/cve-2020-1472
Exploit Code for CVE-2020-1472 aka Zerologon
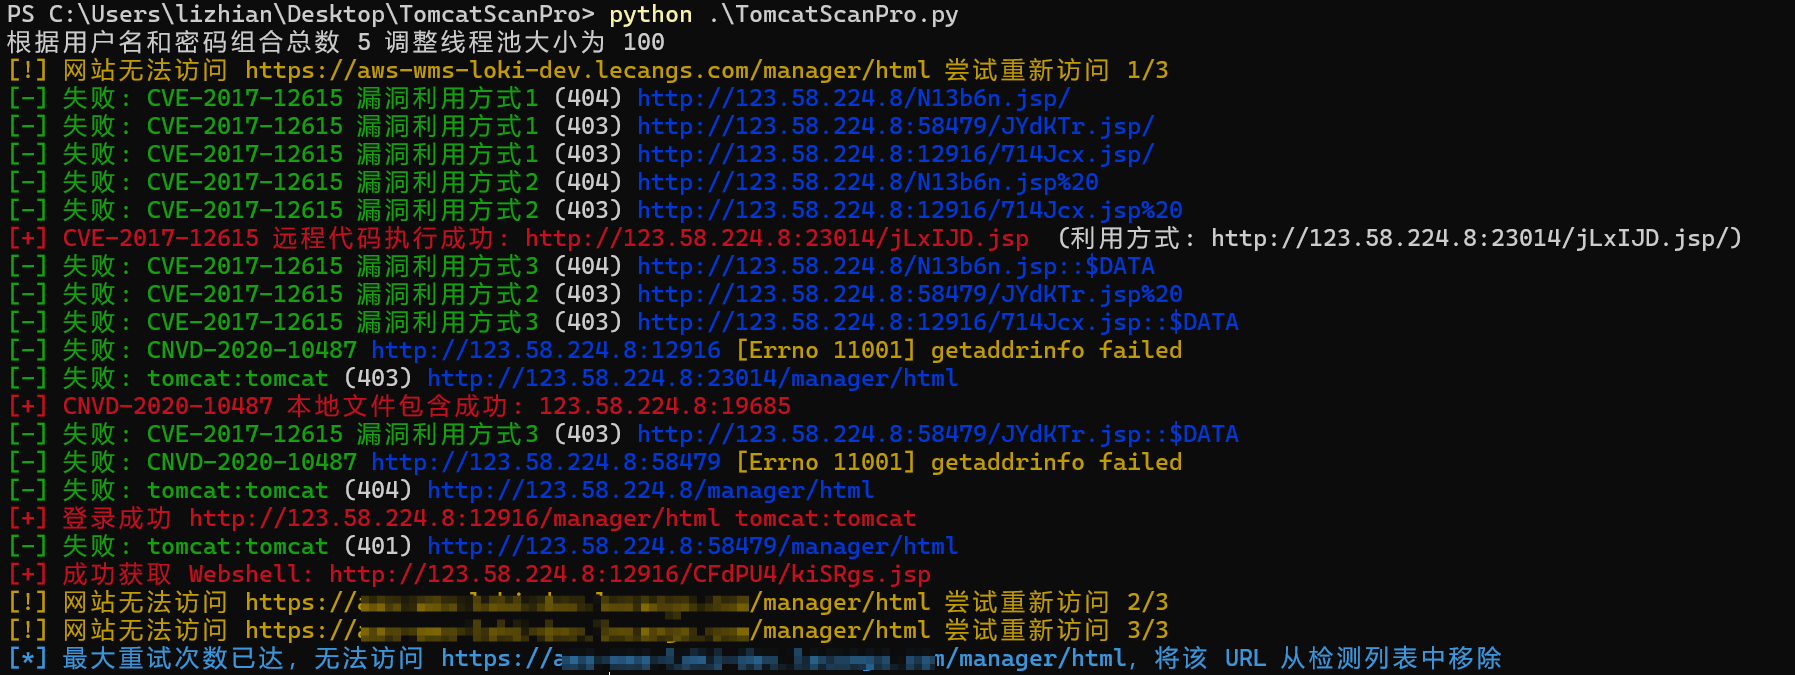 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 risksense/zerologon
Exploit for zerologon cve-2020-1472
 hell-moon/zerologon-exploit
Modified the test PoC from Secura, CVE-2020-1472, to change the machine password to null
 100hnomeunome/zerologon-cve-2020-1472-lab
Explicação e demonstração da vulnerabilidade ZeroLogon (CVE-2020-1472)