

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
AttackTomcat — Tomcat常见漏洞GUI利用工具。CVE-2017-12615 PUT文件上传漏洞、tomcat-pass-getshell 弱认证部署war包、弱口令爆破、CVE-2020-1938 Tomcat AJP文件读取/包含 | Kitploit
Tools/GitHubGitHub/tpt11fb/attacktomcat
Vulnerability ScannersPassword AttacksExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubtpt11fb/attacktomcat

AttackTomcat

Tomcat常见漏洞GUI利用工具。CVE-2017-12615 PUT文件上传漏洞、tomcat-pass-getshell 弱认证部署war包、弱口令爆破、CVE-2020-1938 Tomcat AJP文件读取/包含

View Repository
25719454 years agoReviewed by Kitploit
Share

AttackTomcat

Vulnerability Detection List

CVE-2017-12615 PUT file upload vulnerability tomcat-pass-getshell weak authentication deployment war package Weak password brute force CVE-2020-1938 Tomcat file read/inclusion

Usage

Before first use, please reset the configuration file in settings. For other issues, please read carefully!!! Run with java -jar \*.jar to view the running log information!!

Download the source code and compile with Maven, or directly download from Releases.

Double-click the jar file to run, or execute java -jar AttackTomcat
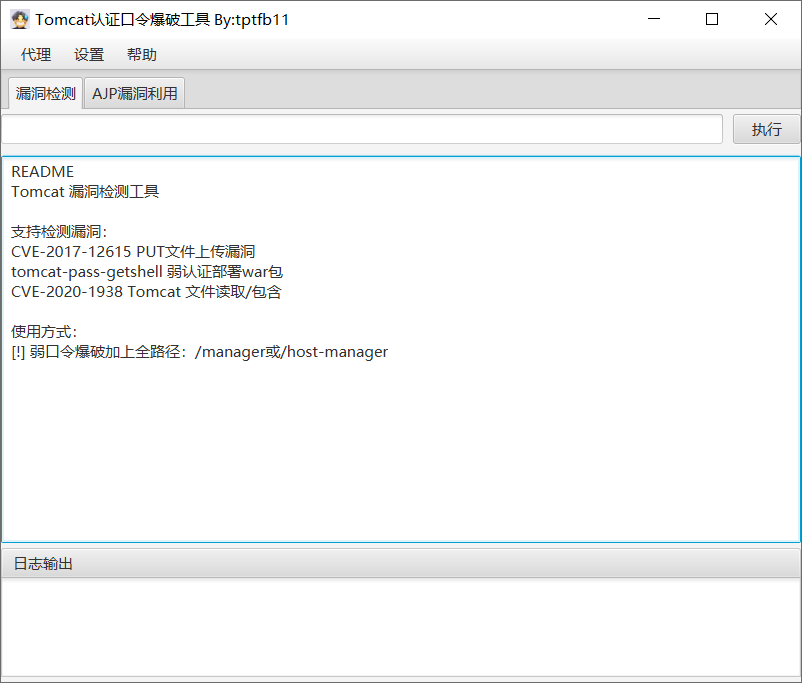
image-20221113190826427

image-20221113190913584

Proxy

Use http and socket proxy.

image-20221113191041737

Configuration

Start the jar file to generate the configuration file config.

AJP vulnerability uses a Python script for verification, requires Python3 environment. Command format: python -V.

Note: If the following prompt appears, it is recommended to directly download AttackTomcat.zip from Releases.

image-20221113191218888

Description

This tool is only for learning exchange, self-testing, prohibits illegal scanning,

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    717
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    504
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    402
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →





