
CVE-2026-45332-PoC
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
authenticationexploitationinformation-gathering+6
lorenzocamilli/cve-2026-45332-pocProof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 groppoxx/cve-2025-25198-poc
PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 pescada-dev/cve-2025-22381
Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project
 super-oof/keepass2-password-finder
PoC for CVE-2023-32784 written in python
 boonjune/poc-cve-2022-30600
A proof of concept for CVE-2022-30600
 ninajafli/dotcms-cve-2022-45782
Proof-of-concept for CVE-2022-45782: predictable dotCMS password-reset tokens, with a token cracker and full exploit chain.
 devisions/cve-2024-29868
Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
 tiemio/ssh-key-and-rce-poc-for-cve-2021-41773
This repository contains a Proof-of-Concept for the CVE-2021-41773. This CVE contains a LFI and RCE vulnerablity.
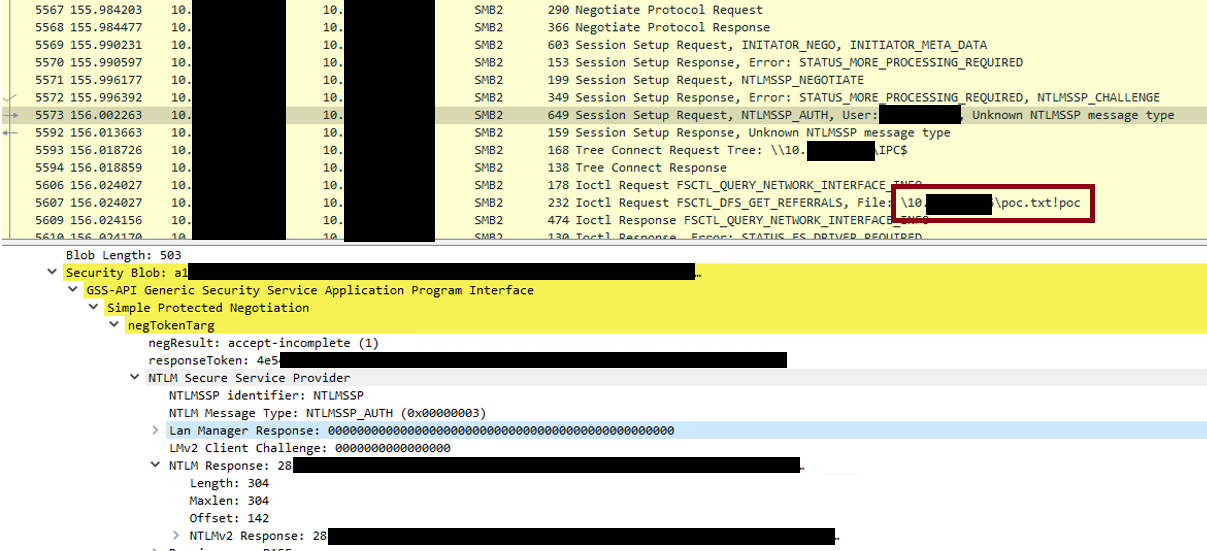 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 c0gnit00/cve-2024-51482
CVE-2025-51482 POC, Dump Credentials From zm.Users
 0xgh057r3c0n/cve-2026-10580
PoC exploit for CVE-2026-10580 - Authentication Bypass in Hippoo Mobile App for WooCommerce <= 1.9.4 leading to Admin Account Takeover
 itzvenom/cve-2023-6329
Python PoC exploit for CVE-2023-6329 authentication bypass in Control iD iDSecure. Reconstructs admin credentials via predictable password derivation…
 sinichi449/python-mikrotikloginexploit
PoC of CVE-2018-14847 Mikrotik Vulnerability using simple script
 loganpkinfosec/cve-2020-7378
Proof-of-concept exploit for CVE-2020-7378 chaining predictable password reset token generation with blind XXE to gain admin access and exfiltrate…
 vincent-vbg/cve-2025-58434-poc
This repository contains a Proof of Concept (PoC) Python script for CVE-2025-58434, which enables attackers to change passwords of other users…
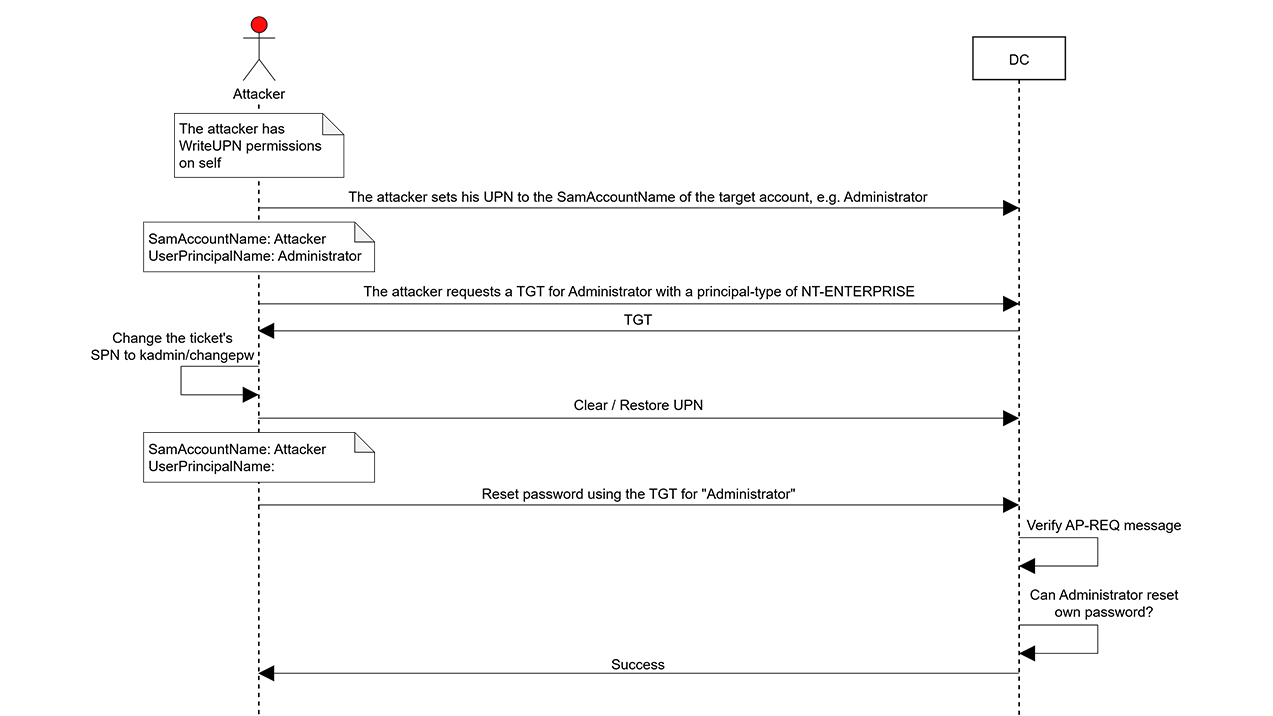 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
 tr33-he11/winboxpoc
Proof of Concept of Winbox Critical Vulnerability (CVE-2018-14847)