

CVE-2025-4094-POC
 pocpioneer/cve-2025-4094-poc
WordPress Plugin Digits < 8.4.6.1 - OTP Auth Bypass via Bruteforce (CVE-2025-4094)
authentication-authorizationexploitationpassword-attacks+3
2
pocpioneer/cve-2025-4094-pocWordPress Plugin Digits < 8.4.6.1 - OTP Auth Bypass via Bruteforce (CVE-2025-4094)
 m1kb0k/cve-2022-25012-dvr4-weak-password-encryption
Decrypts weak encrypted passwords from Argus Surveillance DVR systems via CVE-2022-25012, reconstructing plaintext credentials from DVRParams.ini…
 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
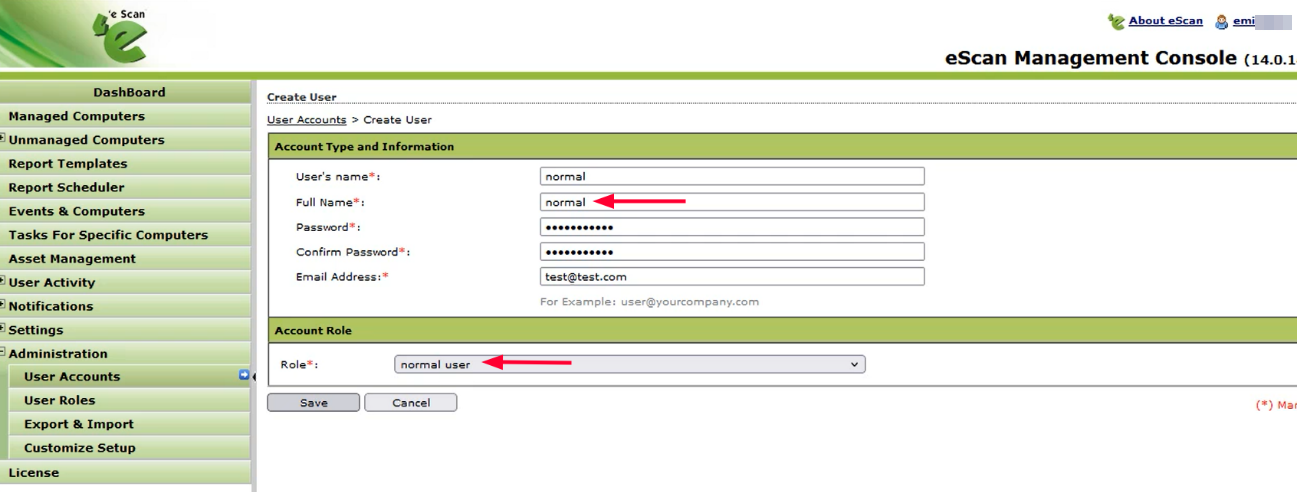 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 nxploited/cve-2025-3604
Flynax Bridge <= 2.2.0 - Unauthenticated Privilege Escalation via Account Takeover
 trqt/cve-2024-48322
Exploit for CVE-2024-48322 targeting RunCodes instances. Retrieves user passwords via email inbox after authentication bypass, requiring only any…
 jenderal92/owa-valid-login-checker
Owa Valid Login Checker
 cappricio-securities/socialengineering
SEt framework
 anmolksachan/cve-2020-2733
Exploit for CVE-2020-2733 in JD Edwards EnterpriseOne Tools, demonstrating unauthenticated admin password decryption and authentication bypass to…
 lastvocher/hikvision-cve-2017-7921-decryptor
Decrypts Hikvision IP camera configuration files extracted via CVE-2017-7921 authentication bypass, recovering user credentials from weakly encrypted…
 jenderal92/prepos-login-checker
Prepostseo Login Checker
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 mauricelambert/gpp-encrypt
This little script encrypts password to gpp cpassword. It useful to create vulnerable lab AD (CVE-2014-1812).
 ubaydev/cve-2024-10508
Proof-of-concept exploit for CVE-2024-10508: unauthenticated privilege escalation via password recovery bypass in RegistrationMagic WordPress plugin…