

SecLists
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
ctfcurated-resourcesdns-fuzzing+11
73.8k
danielmiessler/seclistsCurated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 0ord/magnohost-vulnerabilities-pentest
Manual black-box penetration test of MagnoHost and MeteorCloud infrastructure, documenting exposed MariaDB, default credentials, CVE-2024-27102, and…
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 postmodern/wordlist.rb
A Ruby library and CLI for generating and working with wordlists.
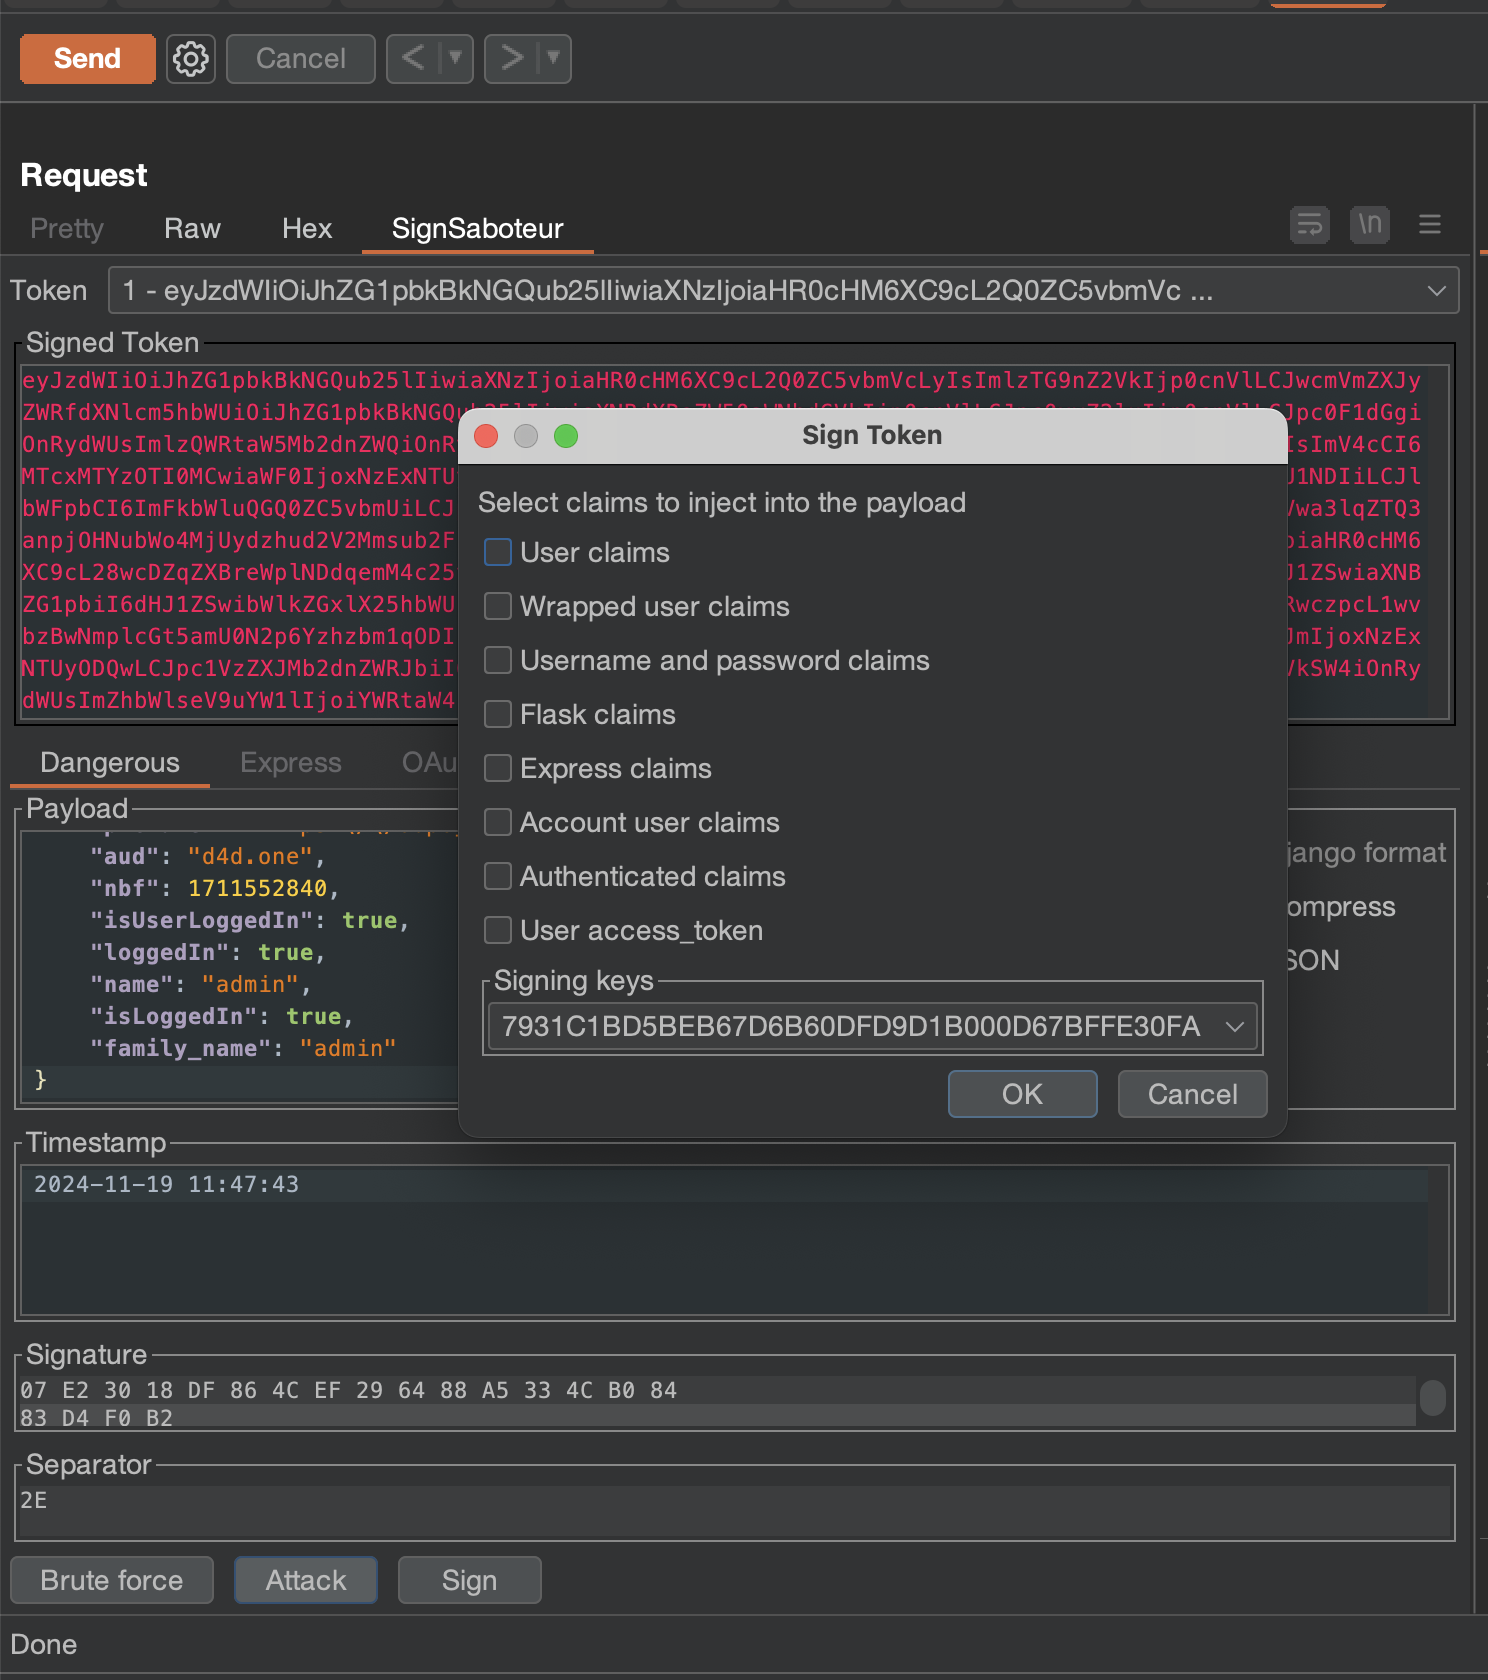 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
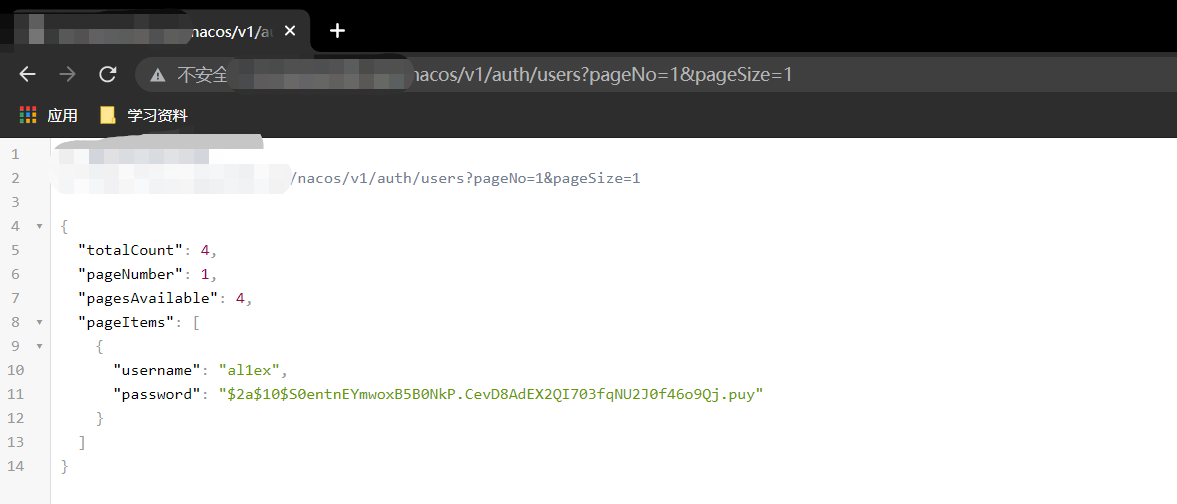 al1ex/alibab-nacos-unauthorized-reset-pwd
Alibab-Nacos-Unauthorized-Reset PWD
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
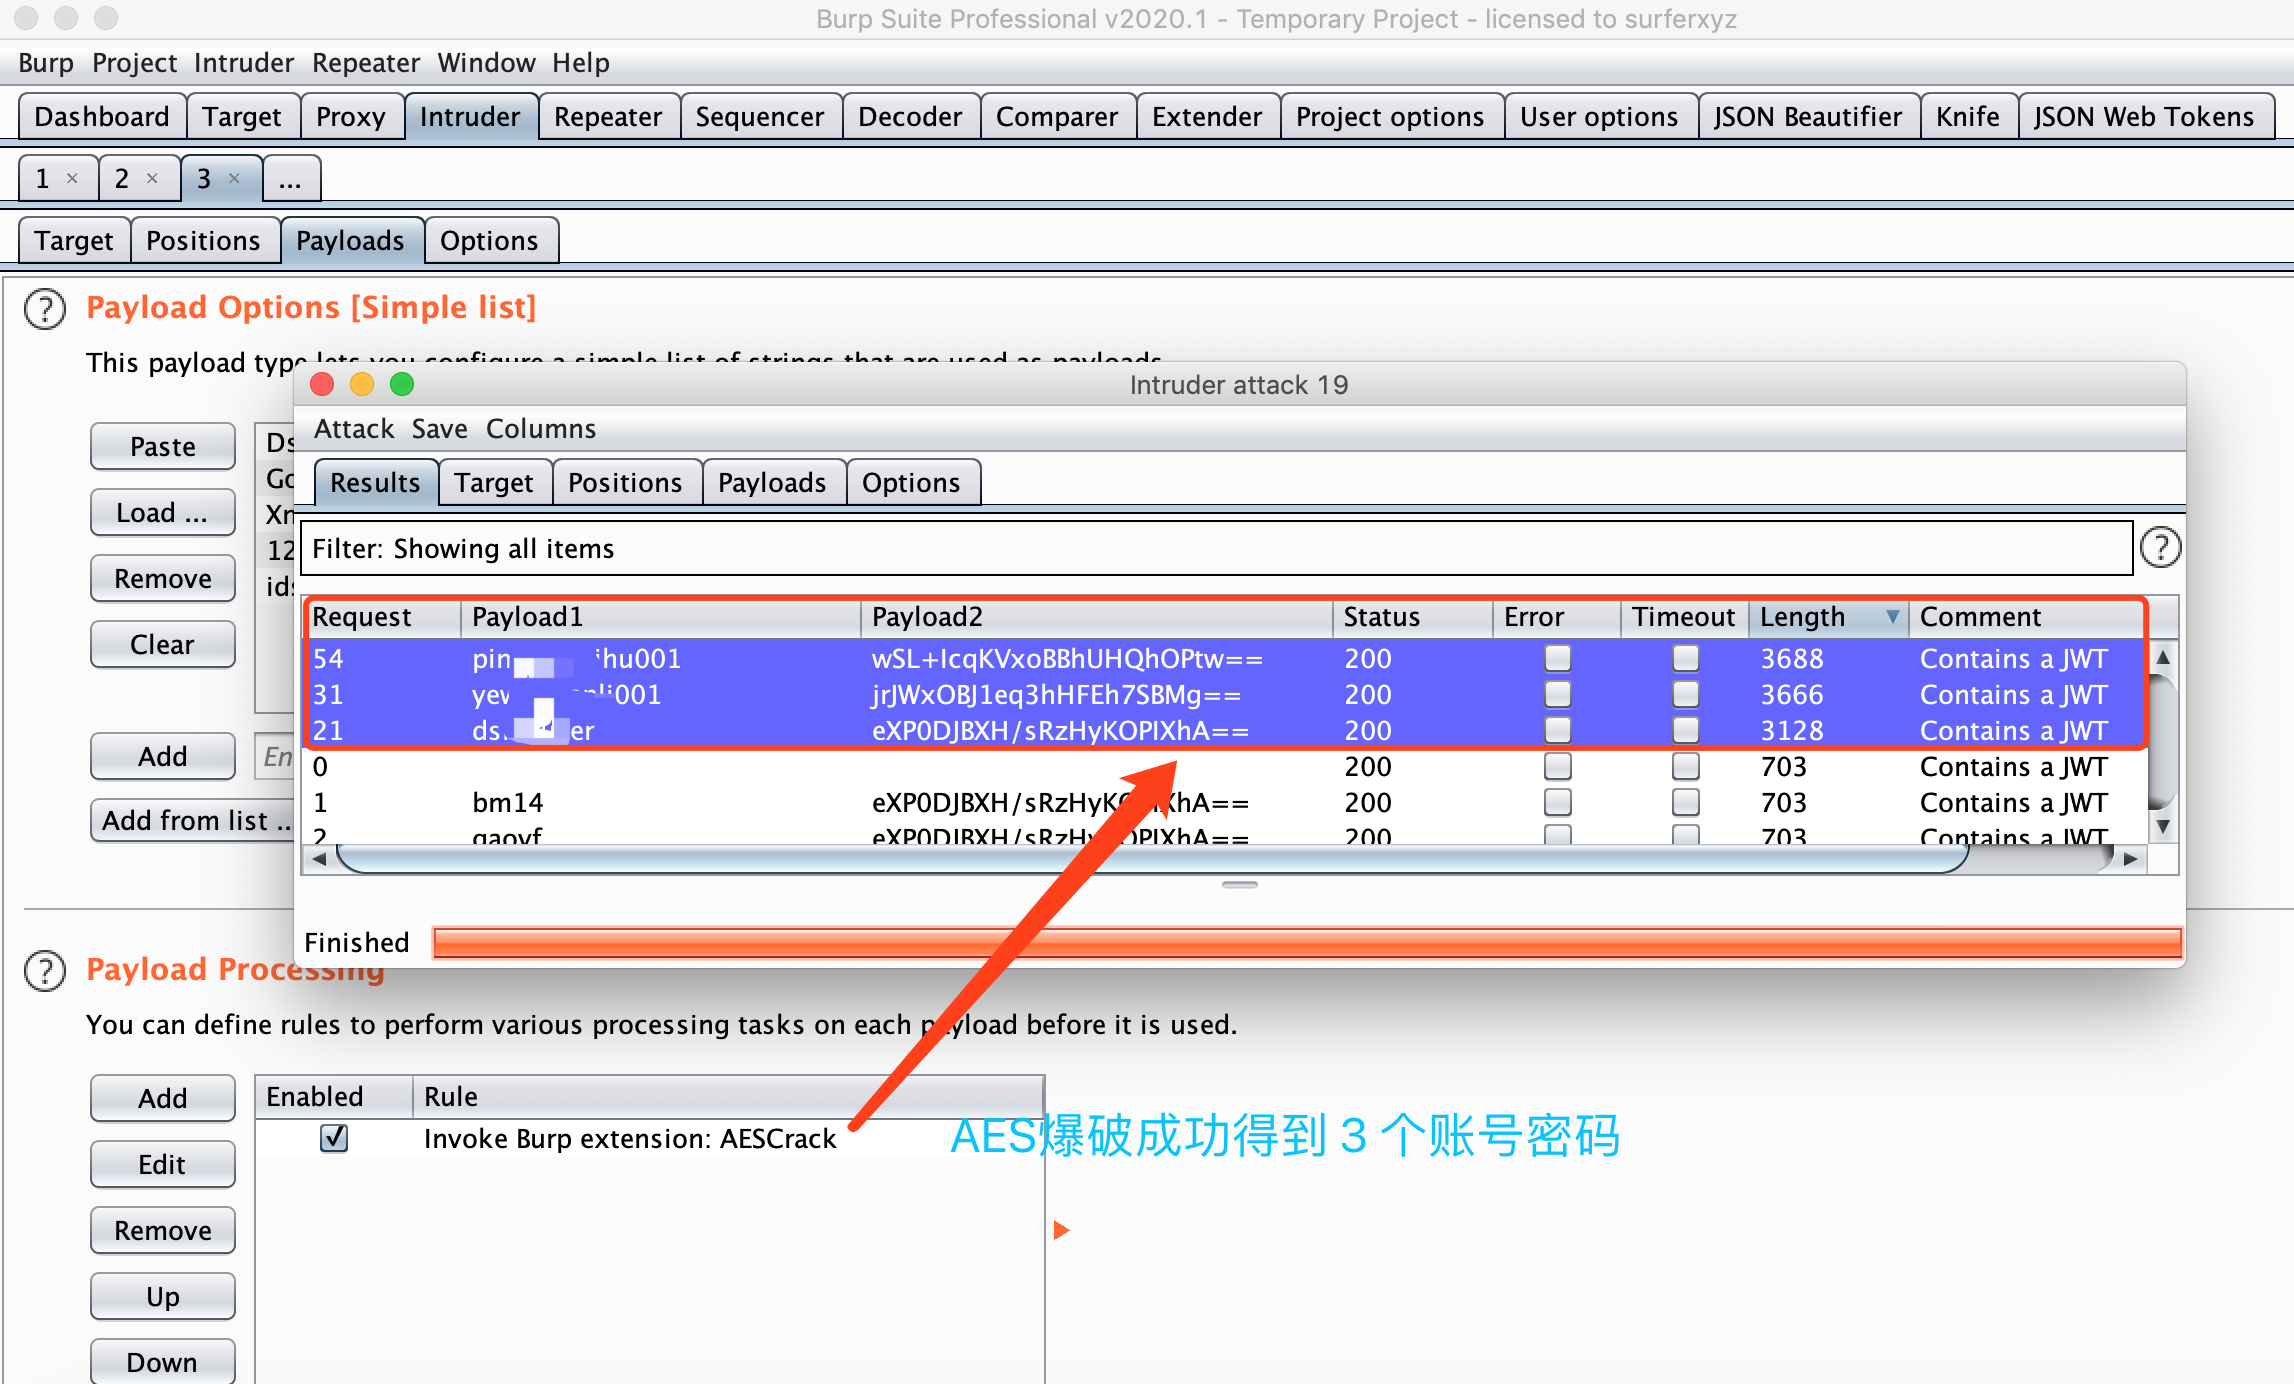 jas502n/burp_aes_plugin
Burpsuite Plugin For AES Crack
 nuid/nebulousad
NebulousAD automated credential auditing tool.
