VeeamDumper-BOF
 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
password-attackspayload-developmentpenetration-testing+2
80
mwr-cybersec/veeamdumper-bofA credential extraction BOF for Veeam Backup and Replication and Veeam One
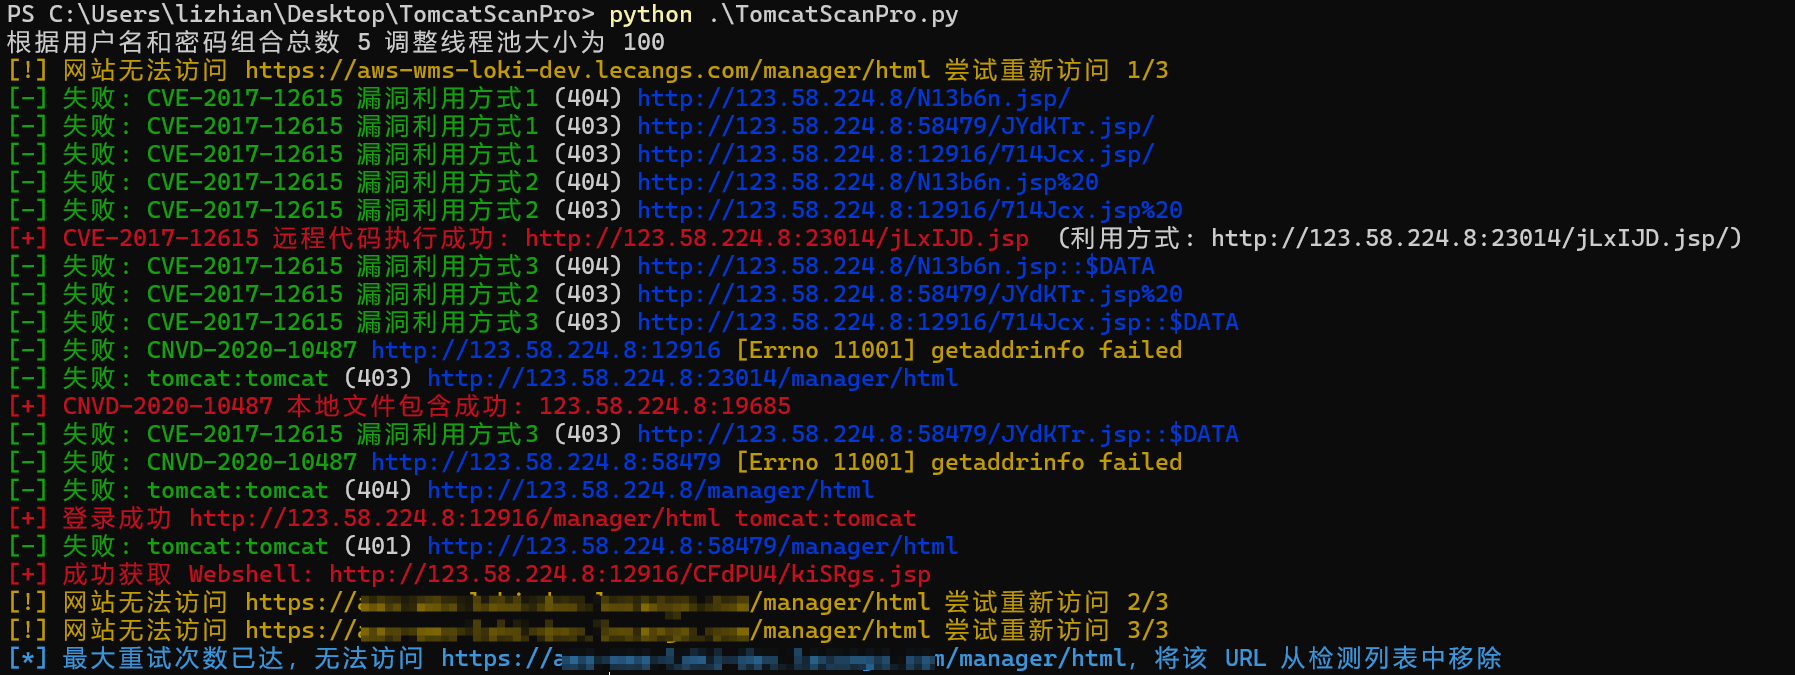 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
 loganpkinfosec/cve-2020-7378
Proof-of-concept exploit for CVE-2020-7378 chaining predictable password reset token generation with blind XXE to gain admin access and exfiltrate…
 ex-cal1bur/smb_cve-2025-24071
Exploited CVE-2025-24071 via SMB by hosting a .library-ms file inside a .tar archive. Using tar x from smbclient, the payload is extracted…
 gl1tch0x1/ghost-cms-exploit
Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…
 entysec/rombuster
RomBuster is a router exploitation tool that allows to disclosure network router admin password.
 hatlesswizard/cve-2023-6875
CVE-2023-6875 exploit written for Xakep.Ru
 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 n000xy/cve-2019-19609-poc-python
Strapi Framework, 3.0.0-beta.17.4
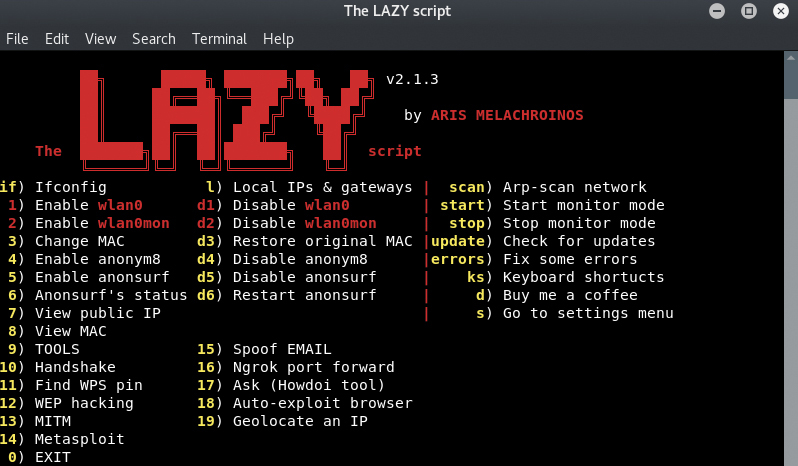 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.