

wapiti
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
api-security-testingconfiguration-auditingcrawler+11
wapiti-scanner/wapitiWeb vulnerability scanner written in Python3
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 7megaumka7/foskiller
FOSSBilling CVE-2026-53647 & CVE-2026-53646 PoC — Unauthenticated API key disclosure & password reset token reuse
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 karma-syndicate/xcrack-python-tools-for-hackers
Python Hacking Tool for Hackers And Spammers
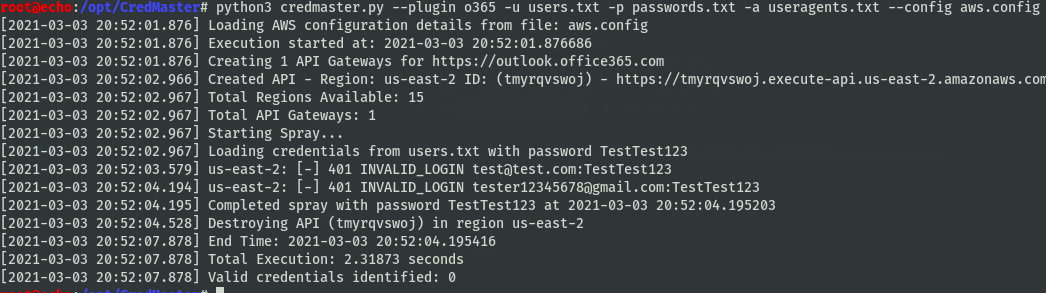 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
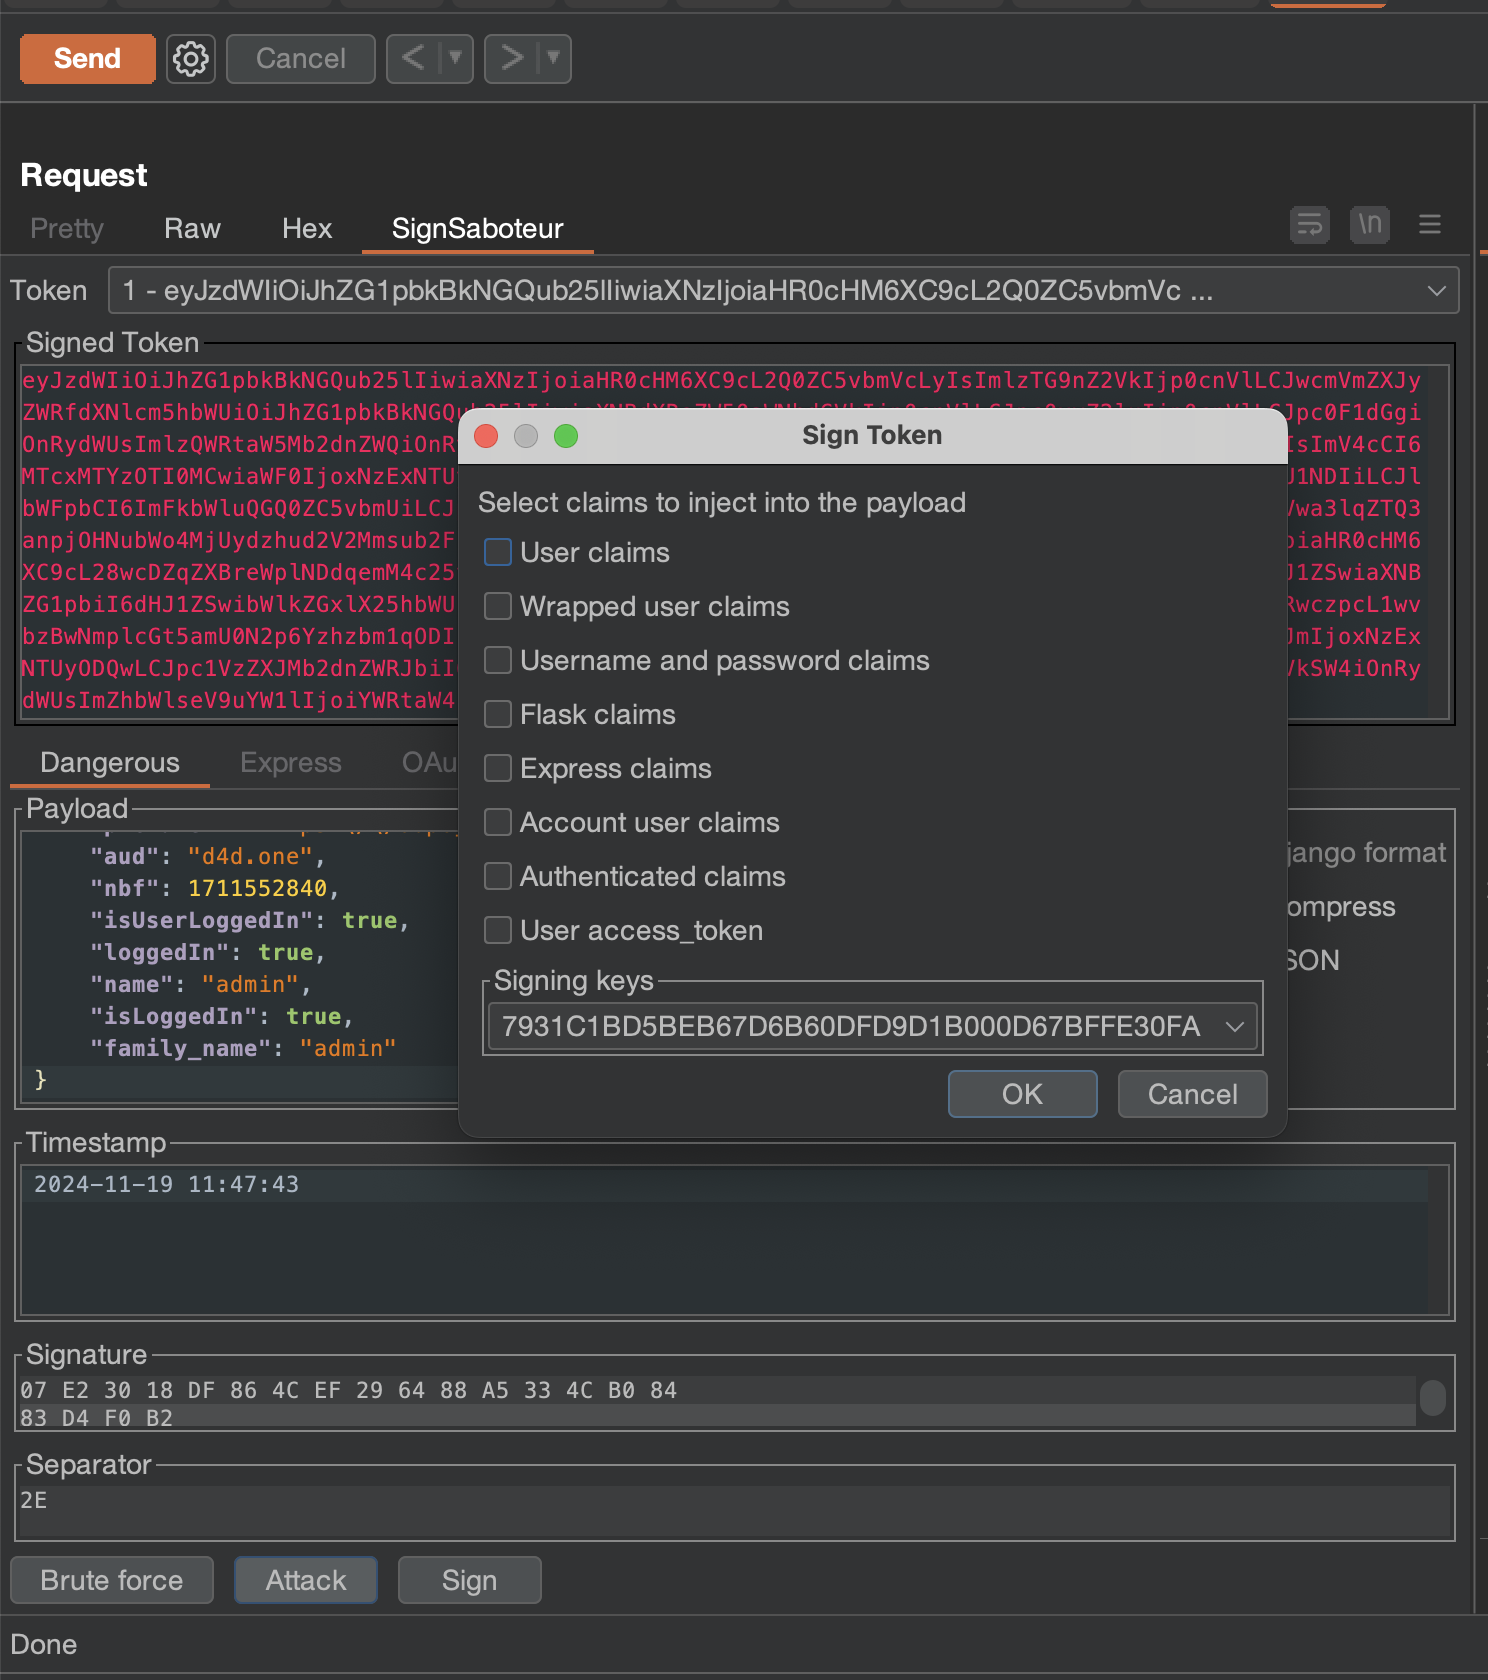 d0ge/sign-saboteur
SignSaboteur is a Burp Suite extension for editing, signing, verifying various signed web tokens
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
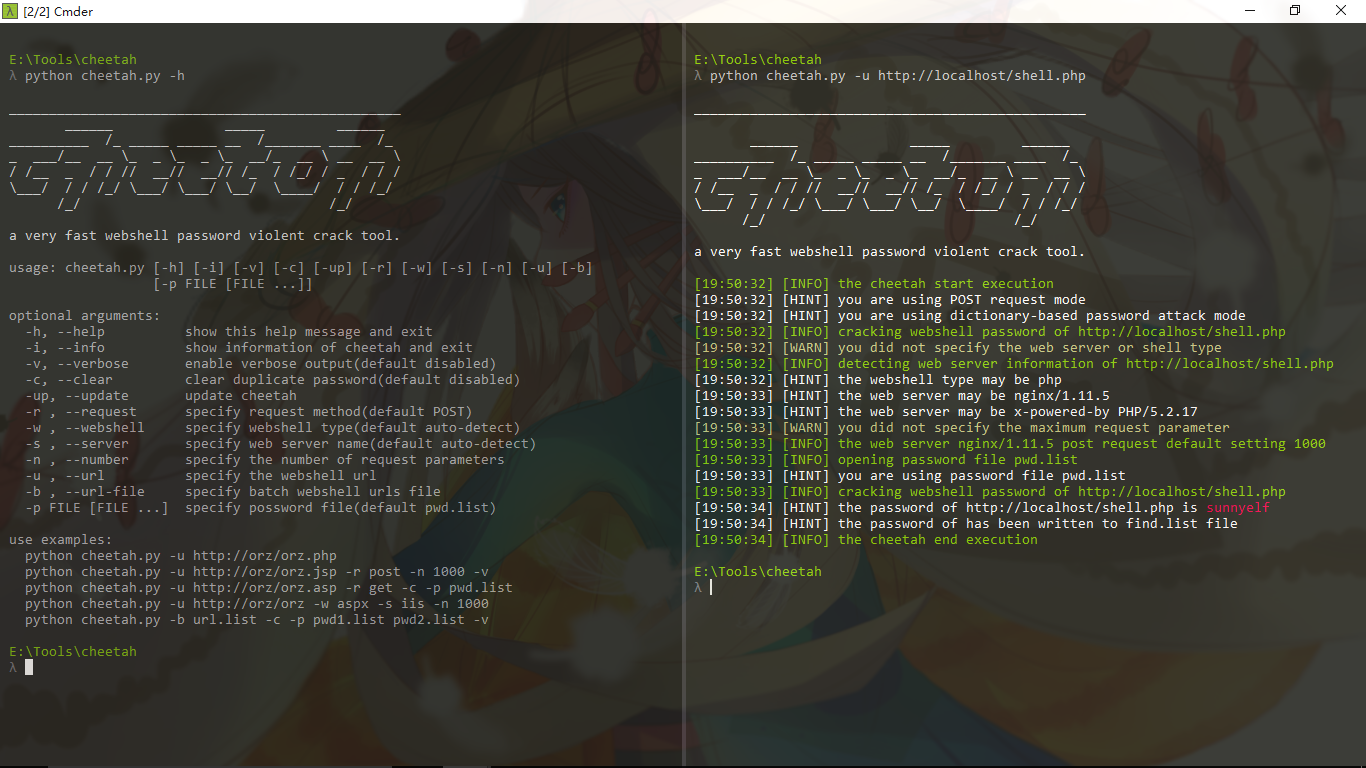 shmilylty/cheetah
a very fast brute force webshell password tool
 an0nlk/nosql-mongodb-injection-username-password-enumeration
Using this script, you can enumerate Usernames and passwords of Nosql(mongodb) injecion vulnerable web applications.