

mqattack
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
authenticationhardware-iot-securityinformation-gathering+7
1
affolter-engineering/mqattackRust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 affolter-engineering/ldapin
CLI tool to perform basic LDAP task for security assessments
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 hackerest/pwneye
Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥
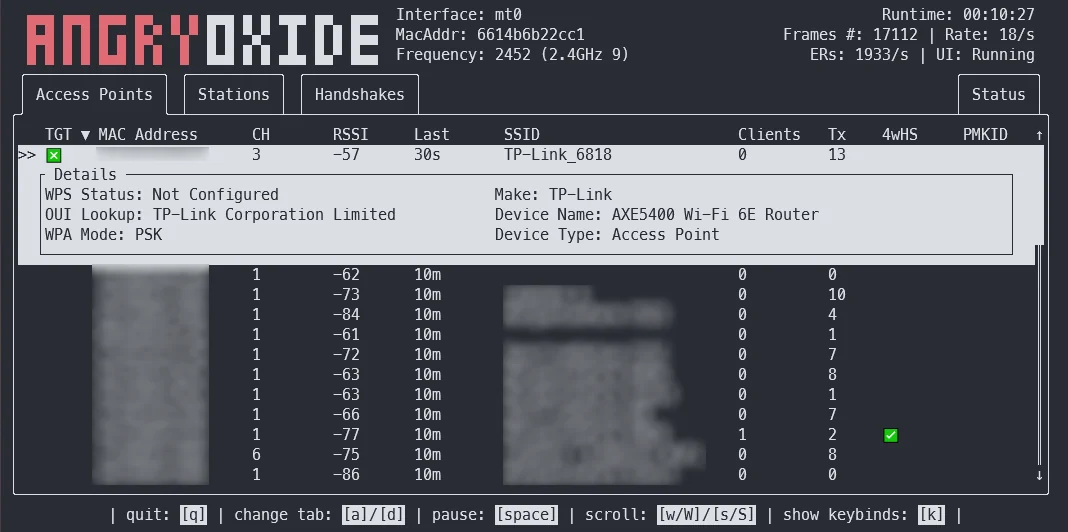 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 olivierlaflamme/cheatsheet-god
Penetration Testing Reference Bank - OSCP / PTP & PTX Cheatsheet
 mihat2/resetnightmare-impacket
CVE-2026-27912 (ResetNightmare) — Linux/impacket port of Semperis Community's Invoke-ResetNightmare PoC
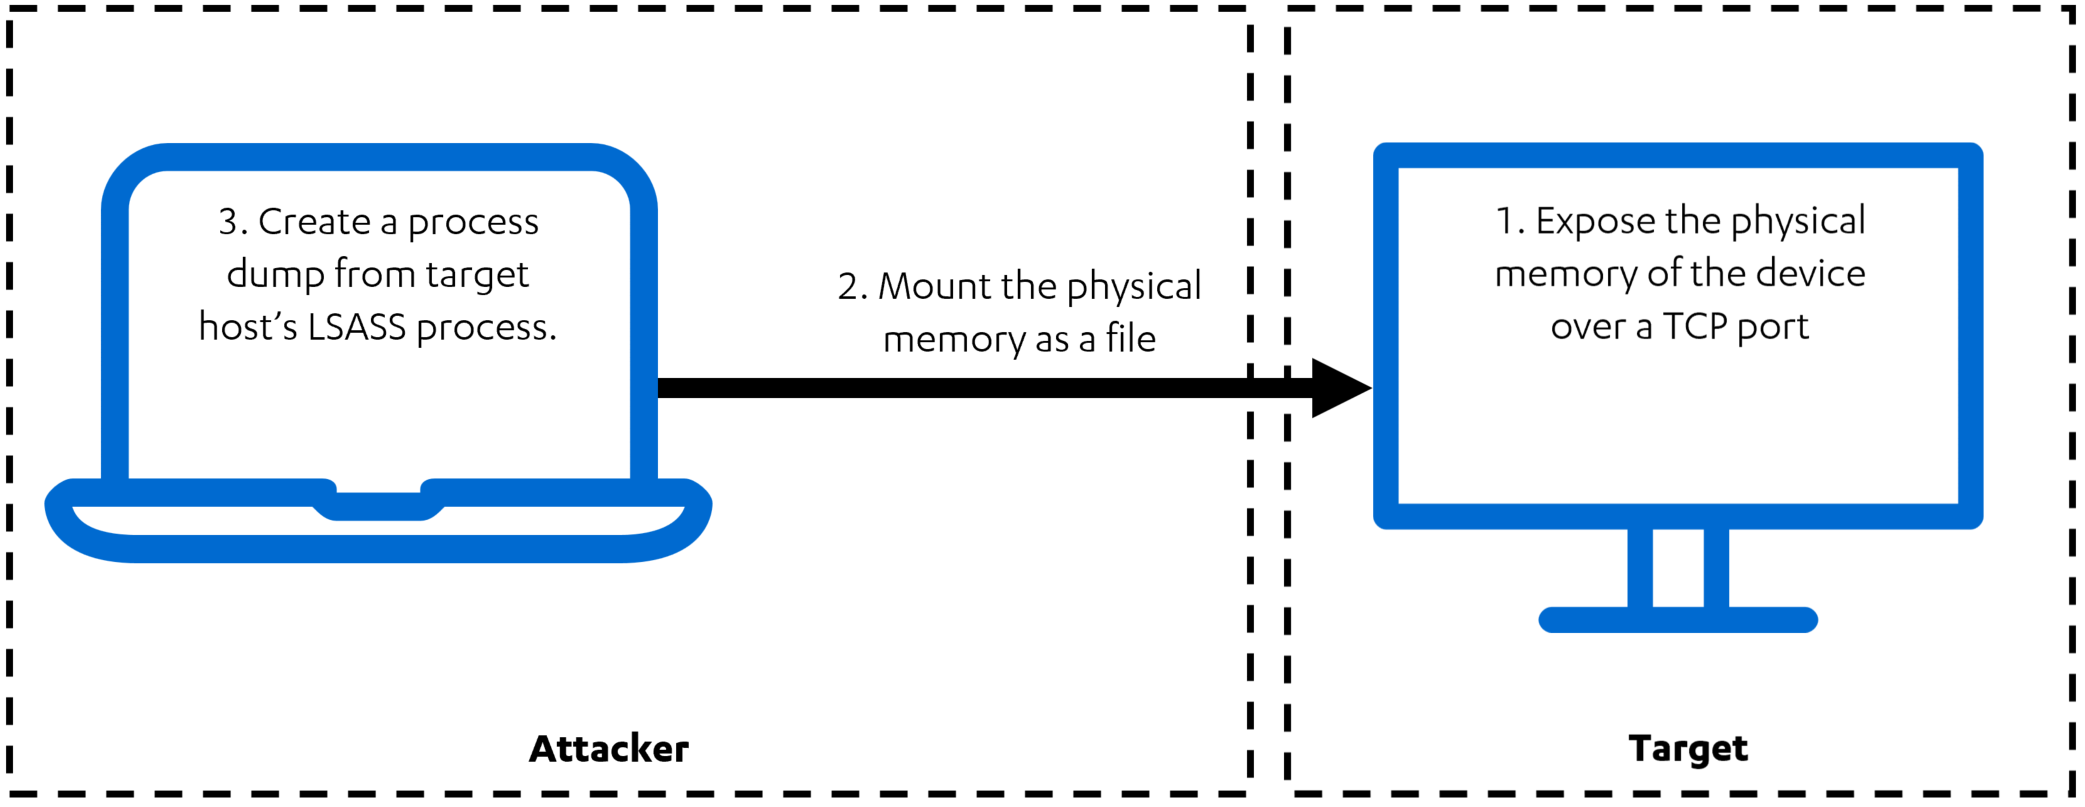 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
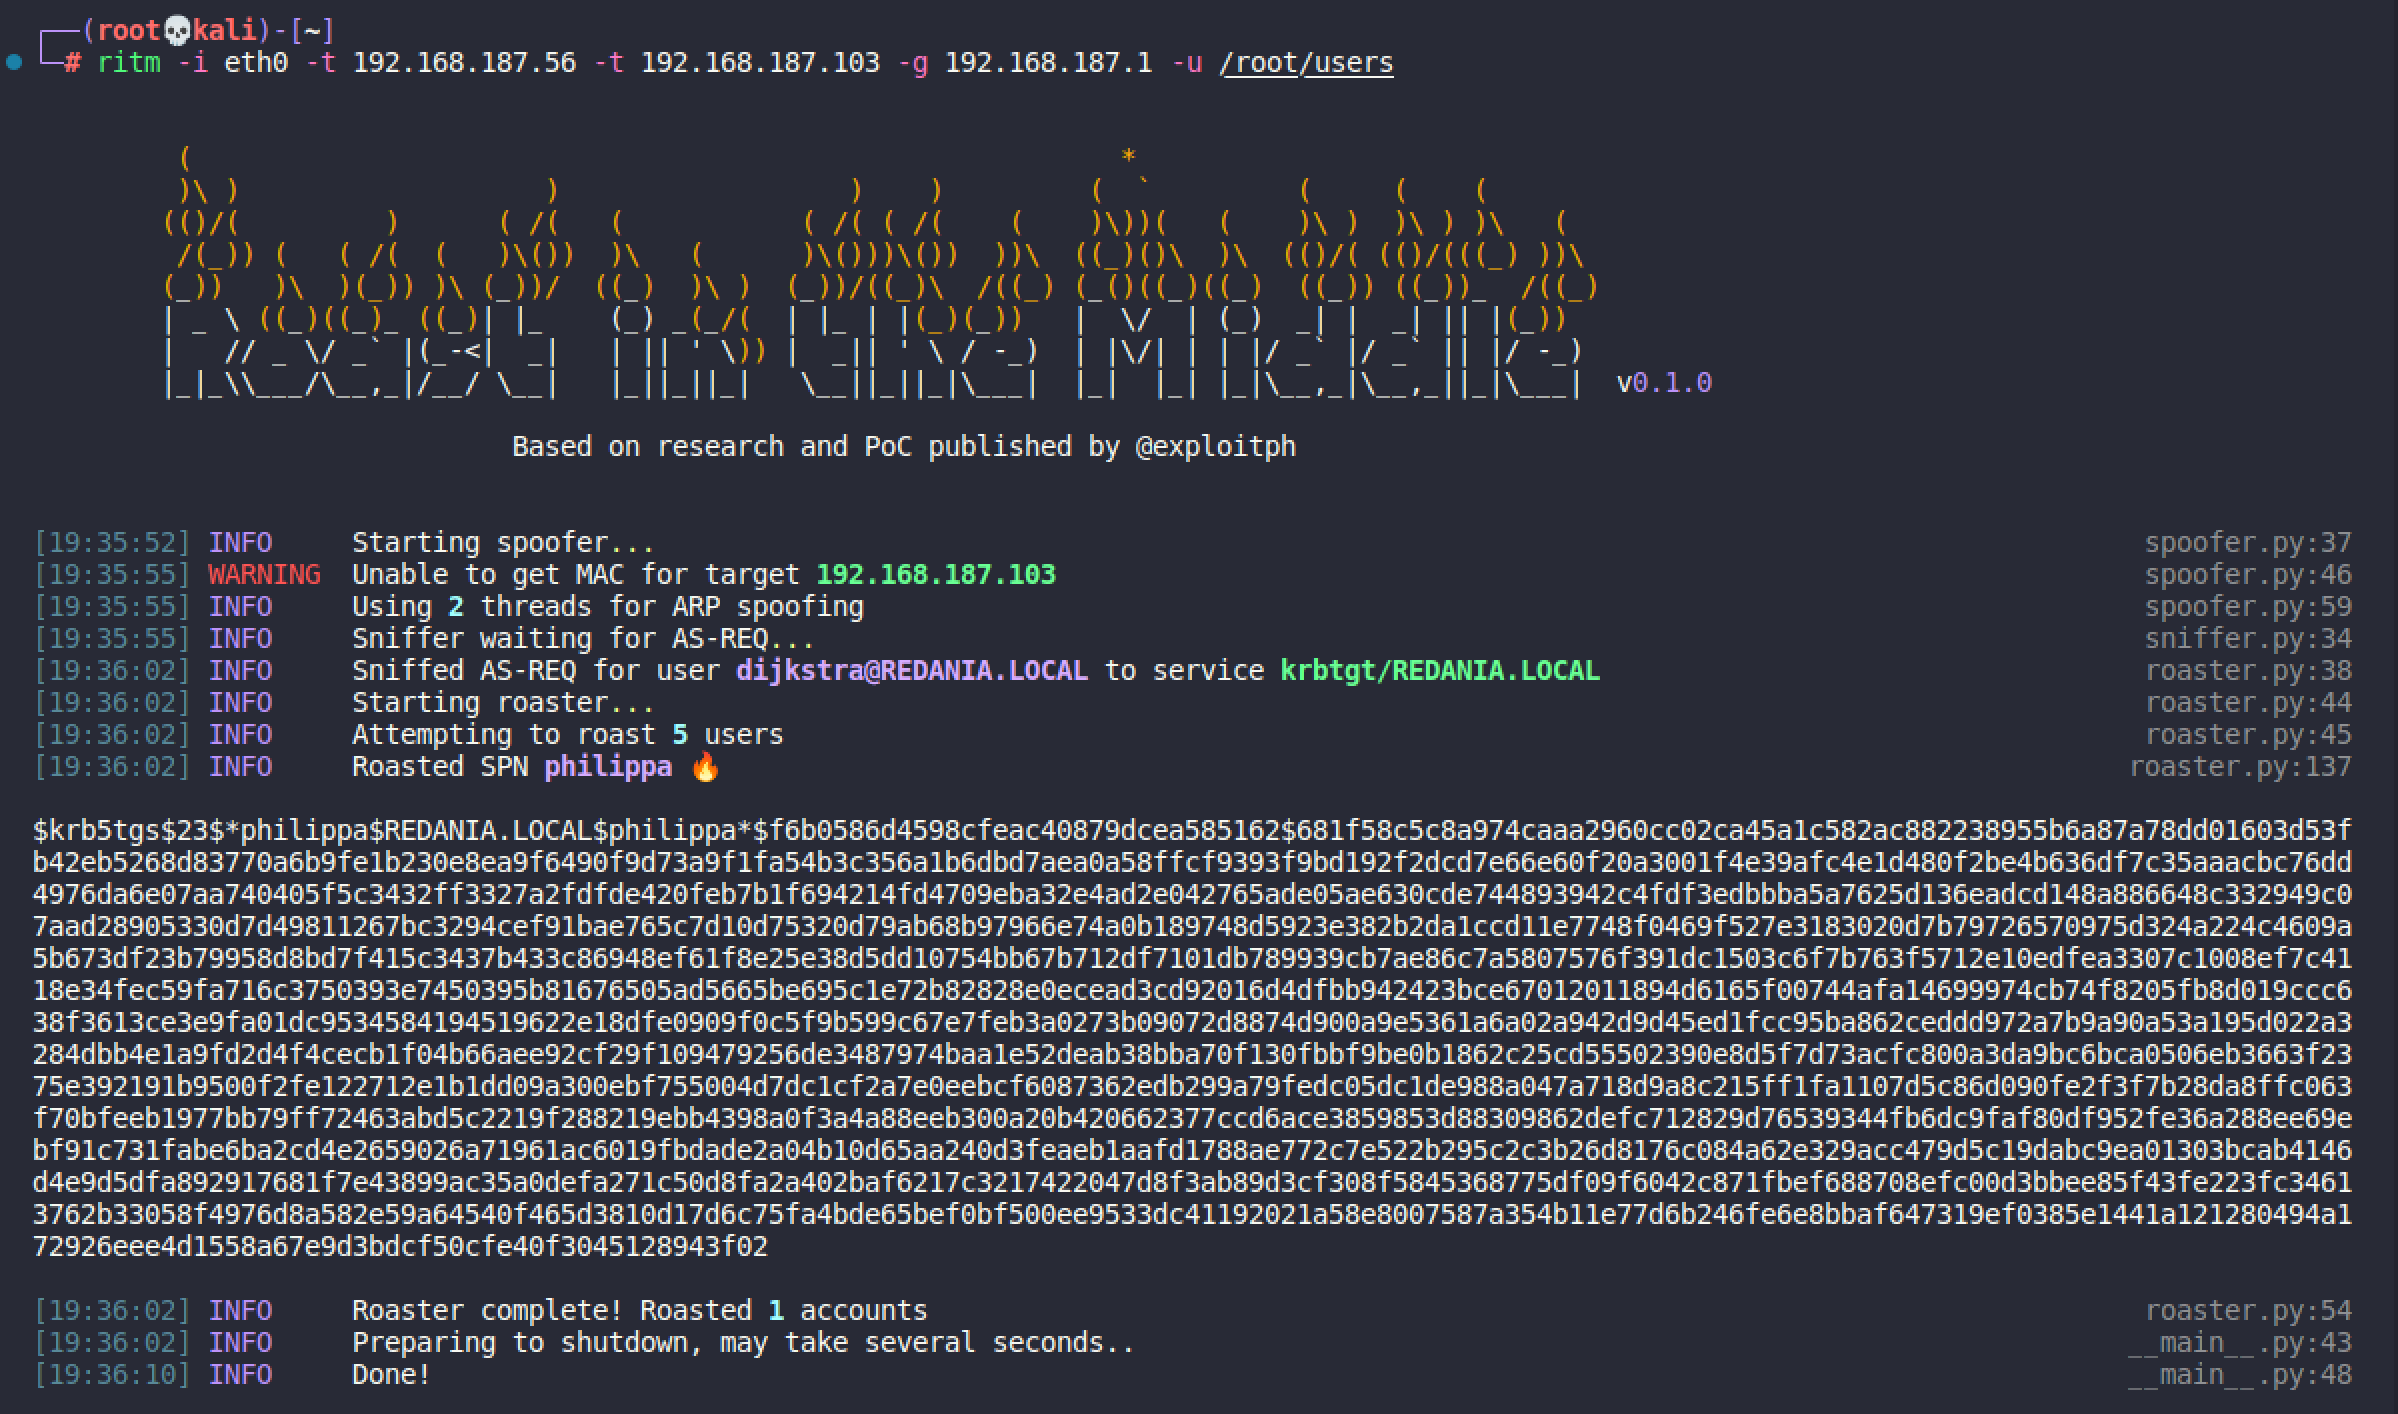
 darkspacesecurity/runas-stealer
RunAs Utility Credential Stealer implementing 3 techniques : Hooking CreateProcessWithLogonW, Smart Keylogging, Remote Debugging