

Overthrone
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
20
karmanya03/overthroneAll-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
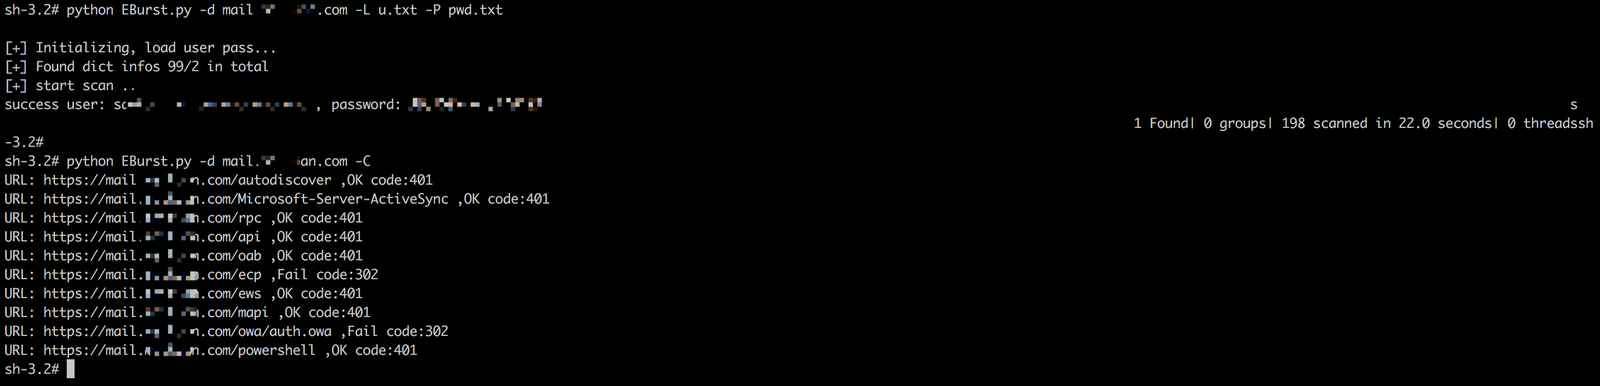 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 j-baines/even-you-brutus
Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 cyeezy08/kimai-cve-2026-52824-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
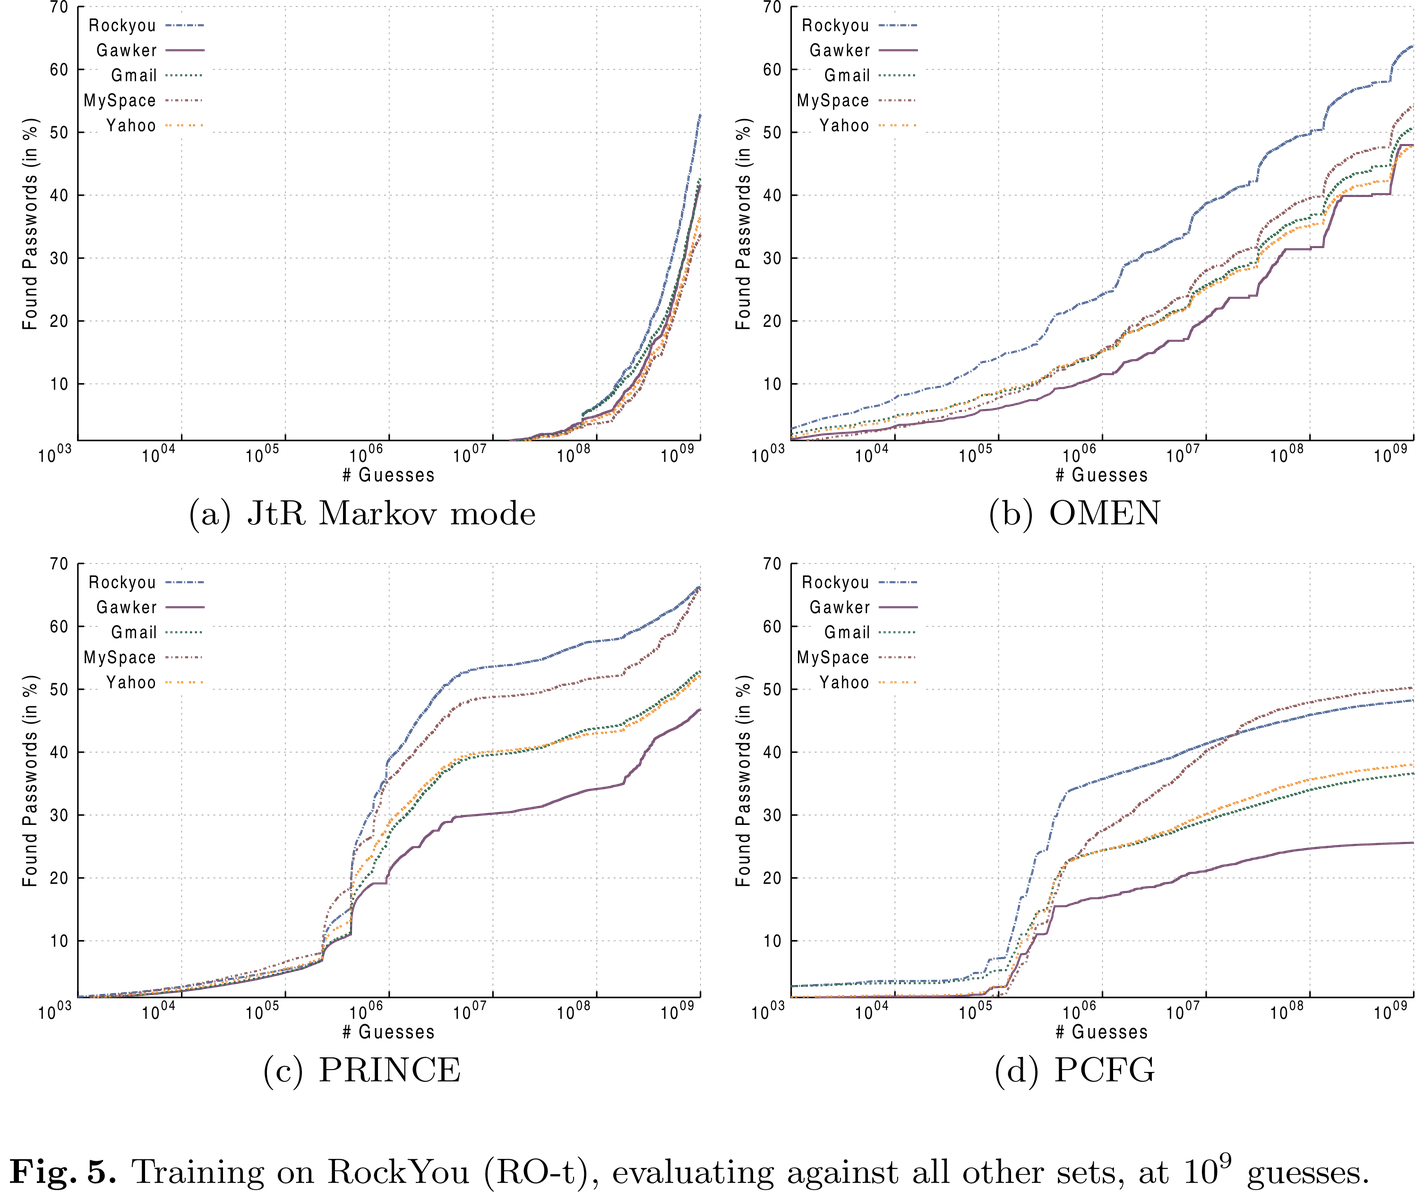 rub-syssec/omen
Markov model-based password guesser in C that enumerates candidates by probability, generating most likely passwords first for hash cracking via…
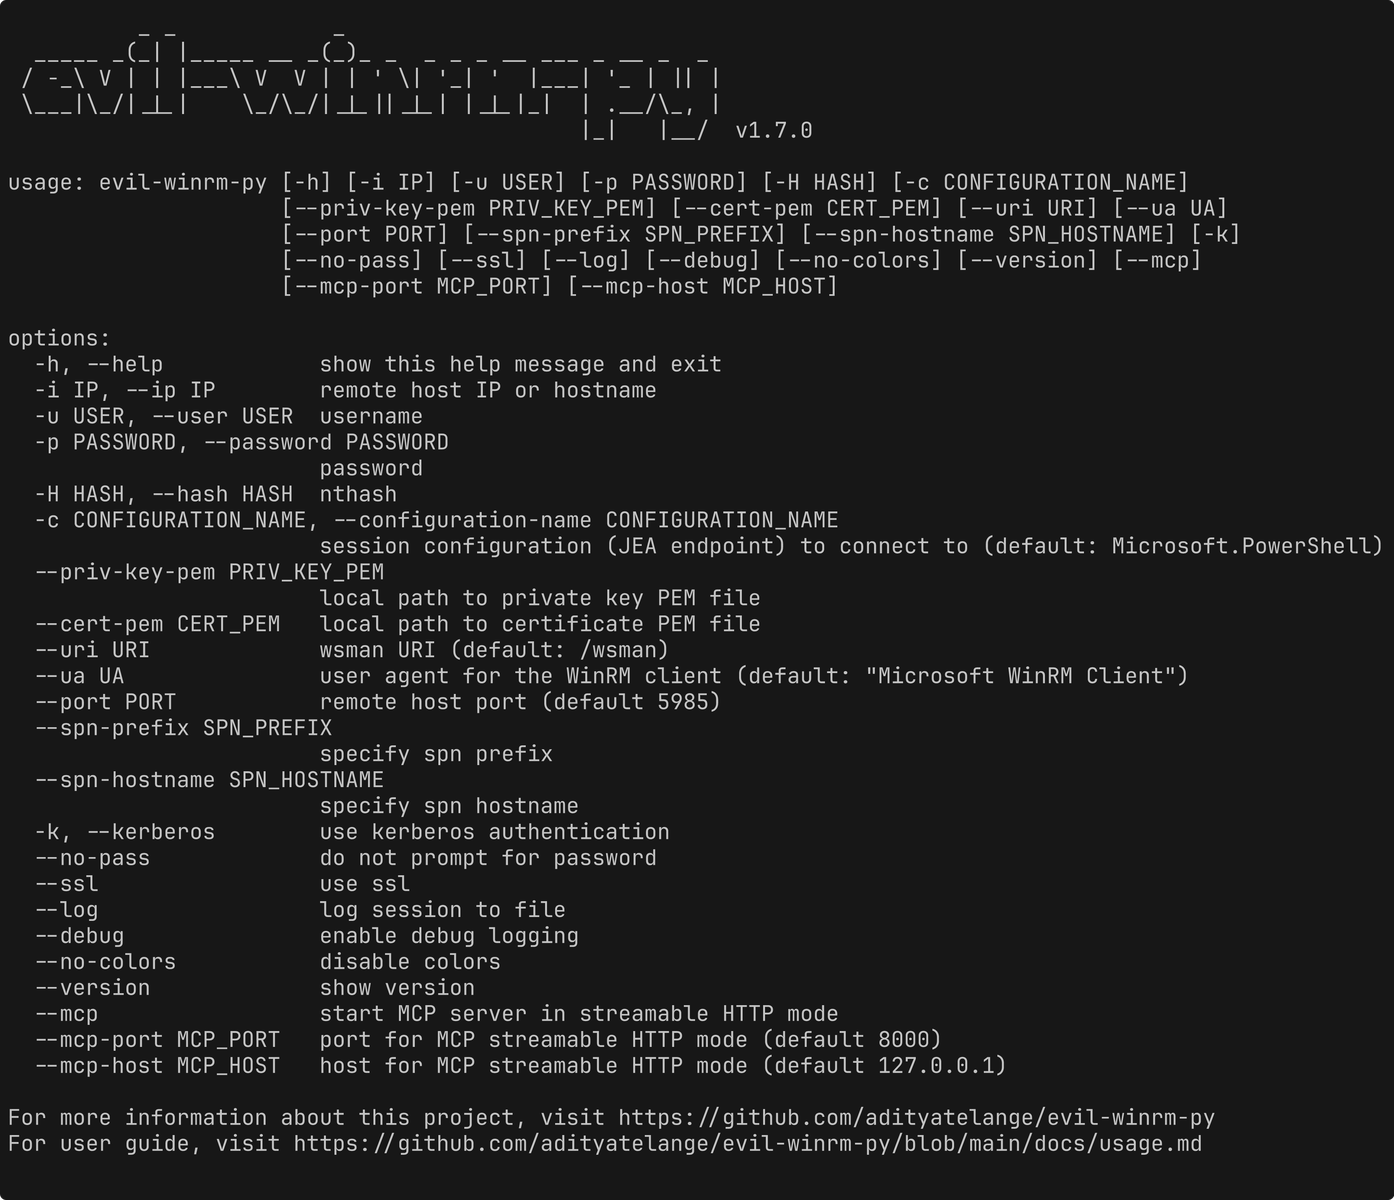 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
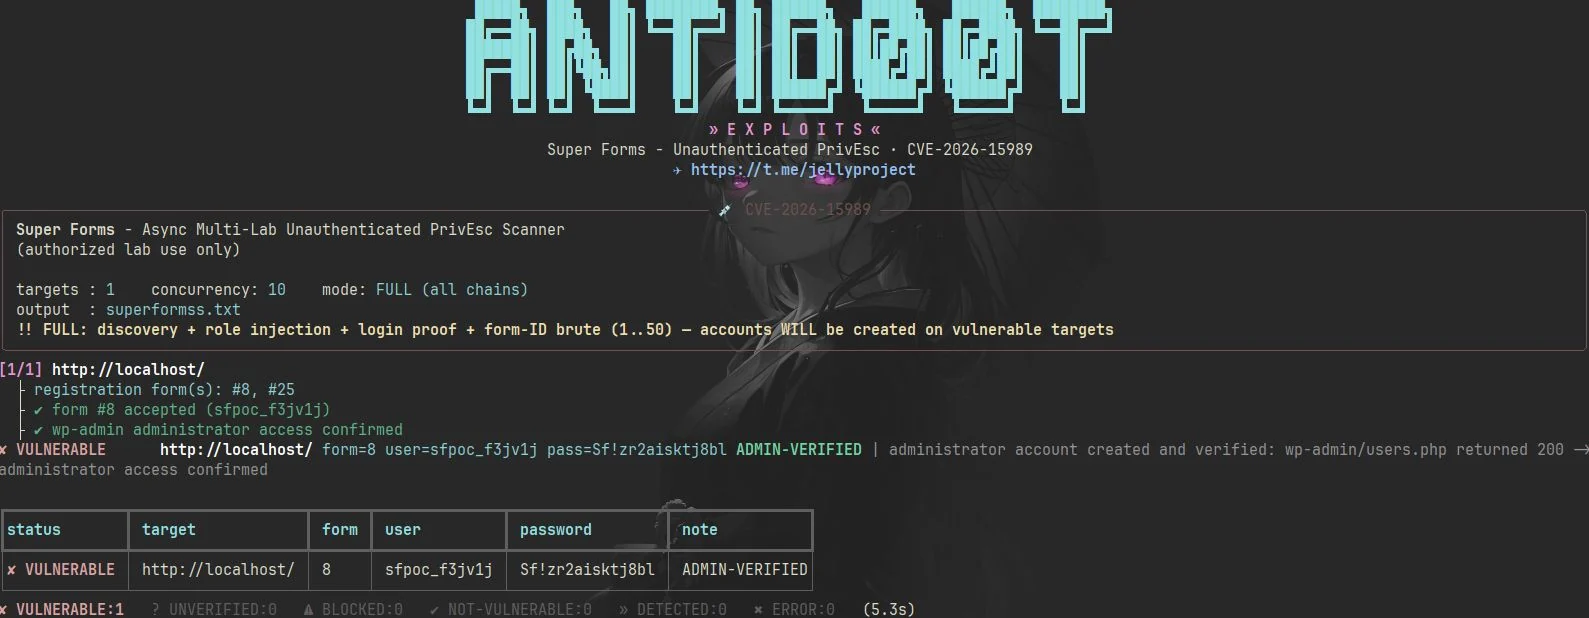 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 mythicagents/xenon
A Mythic agent for Windows written in C
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.