
ntlmscout
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
authenticationdns-analysisinformation-gathering+8
18
boydhacks/ntlmscoutUnauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
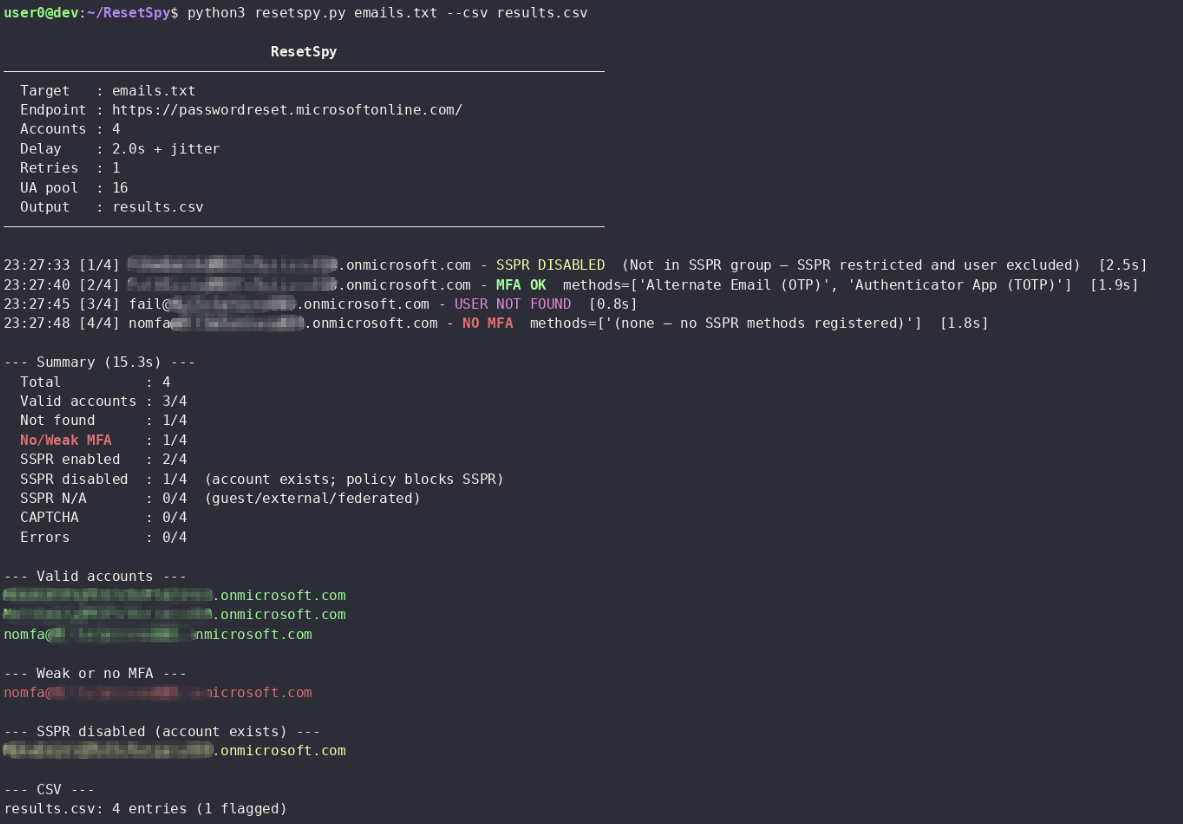 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.
 wayang1337/cve-2026-80099
Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated
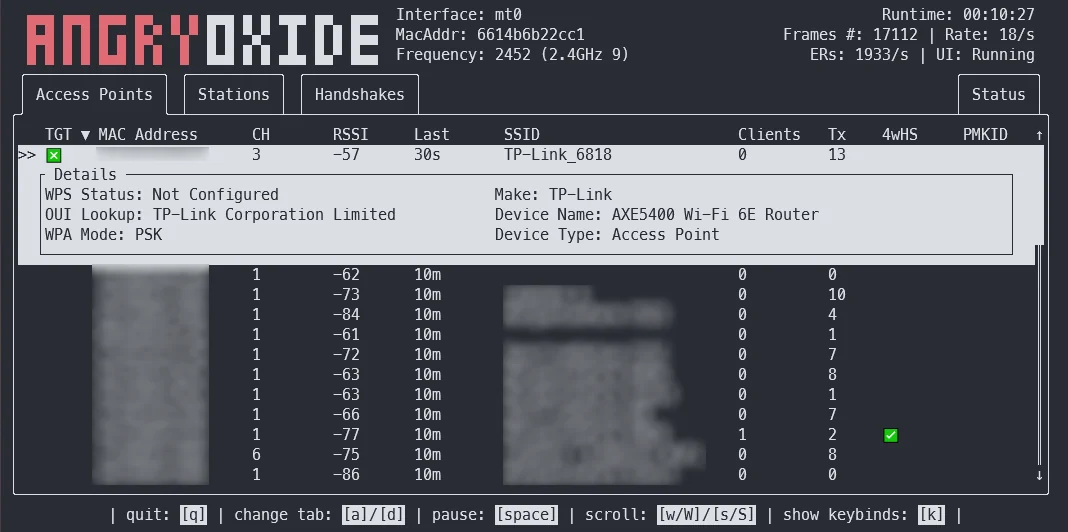 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 cloud-architekt/azuread-attack-defense
This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…
 garrettfoster13/pre2k
A tool to query for the existence of pre-windows 2000 computer objects.
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 m3f157o/combine_harvester
Rust in-memory dumper
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
 mzhmo/leakedwallpaper
Leak of any user's NetNTLM hash. Fixed in KB5040434