

hexstrike-ai
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
binary-analysiscloud-securityctf+9
12.2k
0x4m4/hexstrike-aiMCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 v1s1t0r1sh3r3/airgeddon
This is a multi-use bash script for Linux systems to audit wireless networks.
 alihzsec/cve-2024-28000
Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
 sofianehamlaoui/lockdoor-framework
🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources
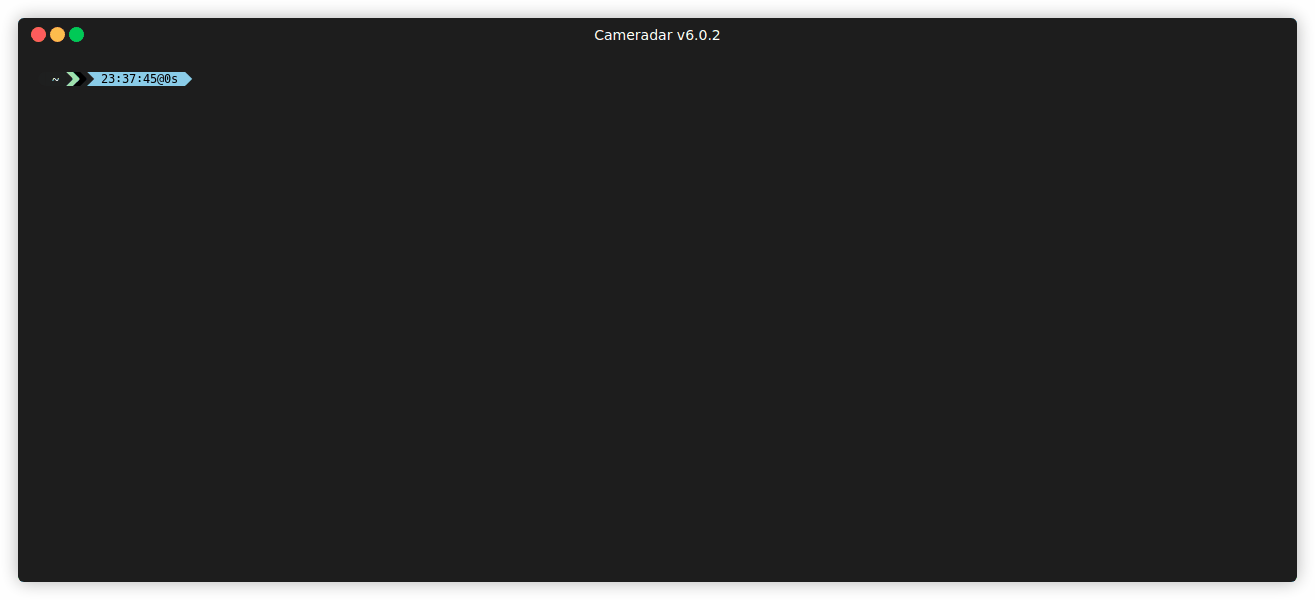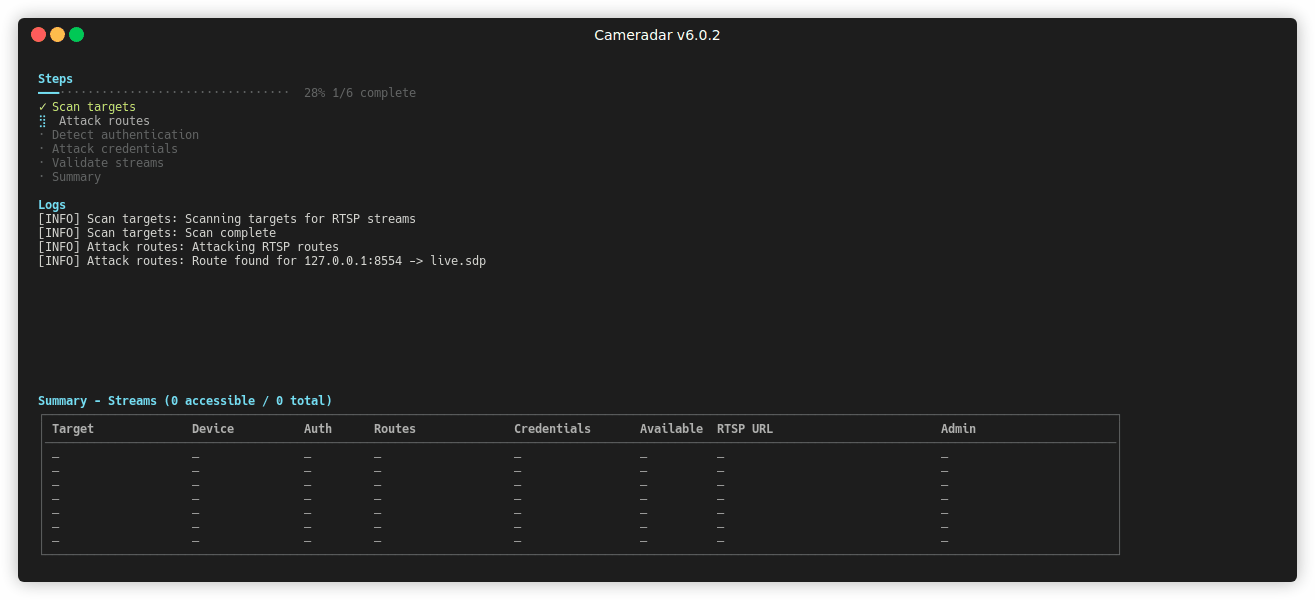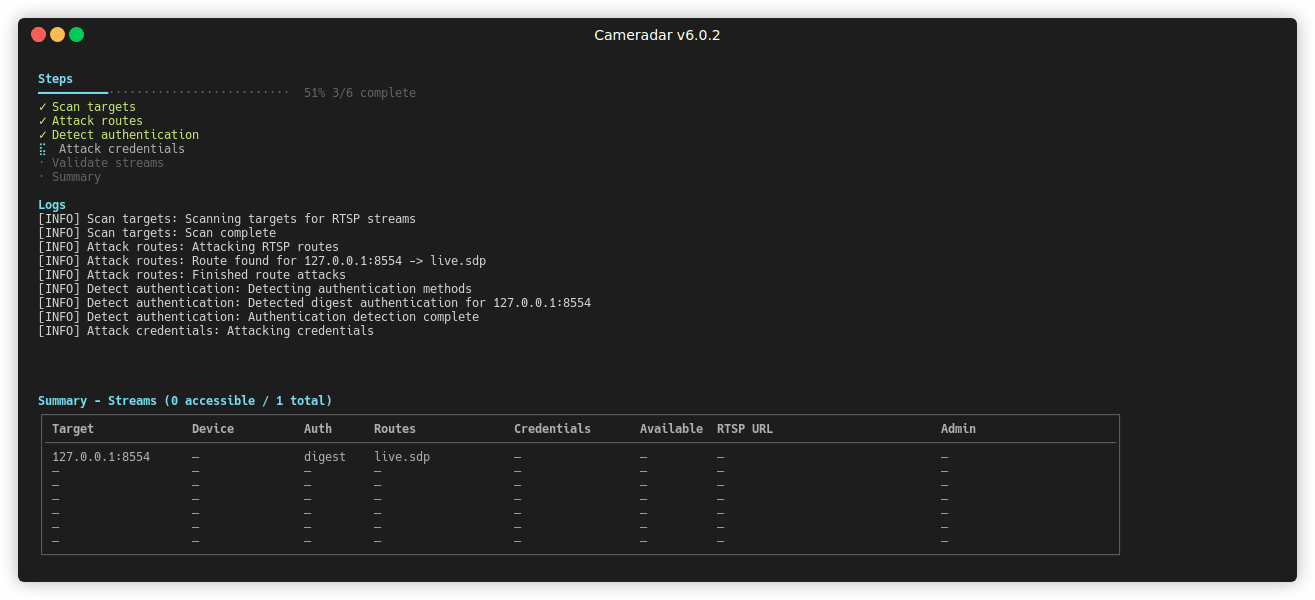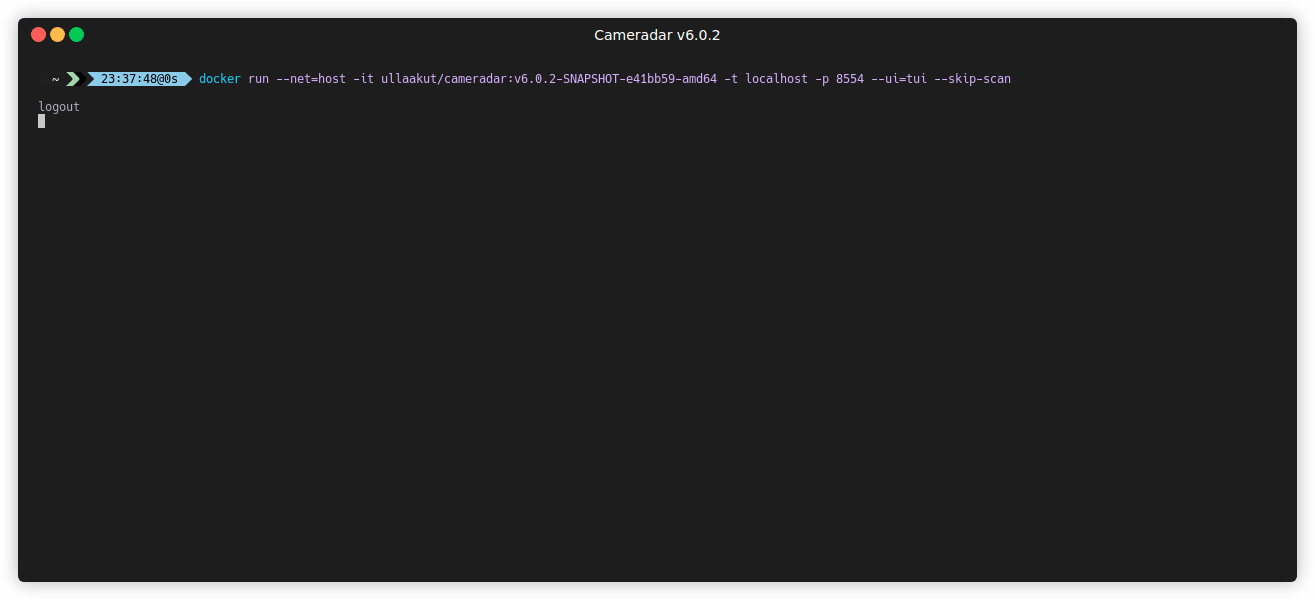 ullaakut/cameradar
Cameradar hacks its way into RTSP videosurveillance cameras
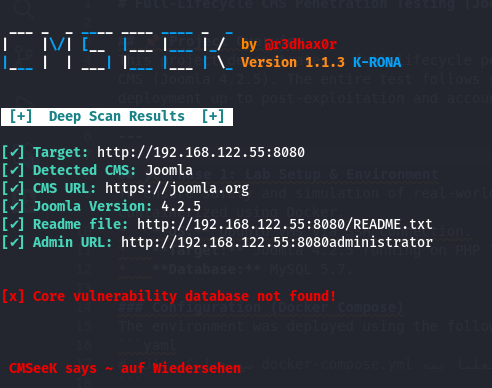 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 n0kovo/awesome-password-cracking
A curated list of awesome tools, research, papers and other projects related to password cracking and password security.

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 d4vinci/cr3dov3r
Know the dangers of credential reuse attacks.
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 david-botelho-mariano/exploit-cve-2024-25723
Educational Proof of Concept exploit for CVE-2024-25723, demonstrating unauthorized account takeover in ZenML via API password reset, with version…
 devisions/cve-2024-29868
Proof of concept of CVE-2024-29868 affecting Apache StreamPipes from 0.69.0 through 0.93.0
 ninajafli/dotcms-cve-2022-45782
Proof-of-concept for CVE-2022-45782: predictable dotCMS password-reset tokens, with a token cracker and full exploit chain.
 varandinawer/cve-2020-28874
CVE-2020-28874
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.