
PXEThief
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
exploitationinformation-gatheringpassword-attacks+5
438
mwr-cybersec/pxethiefPXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
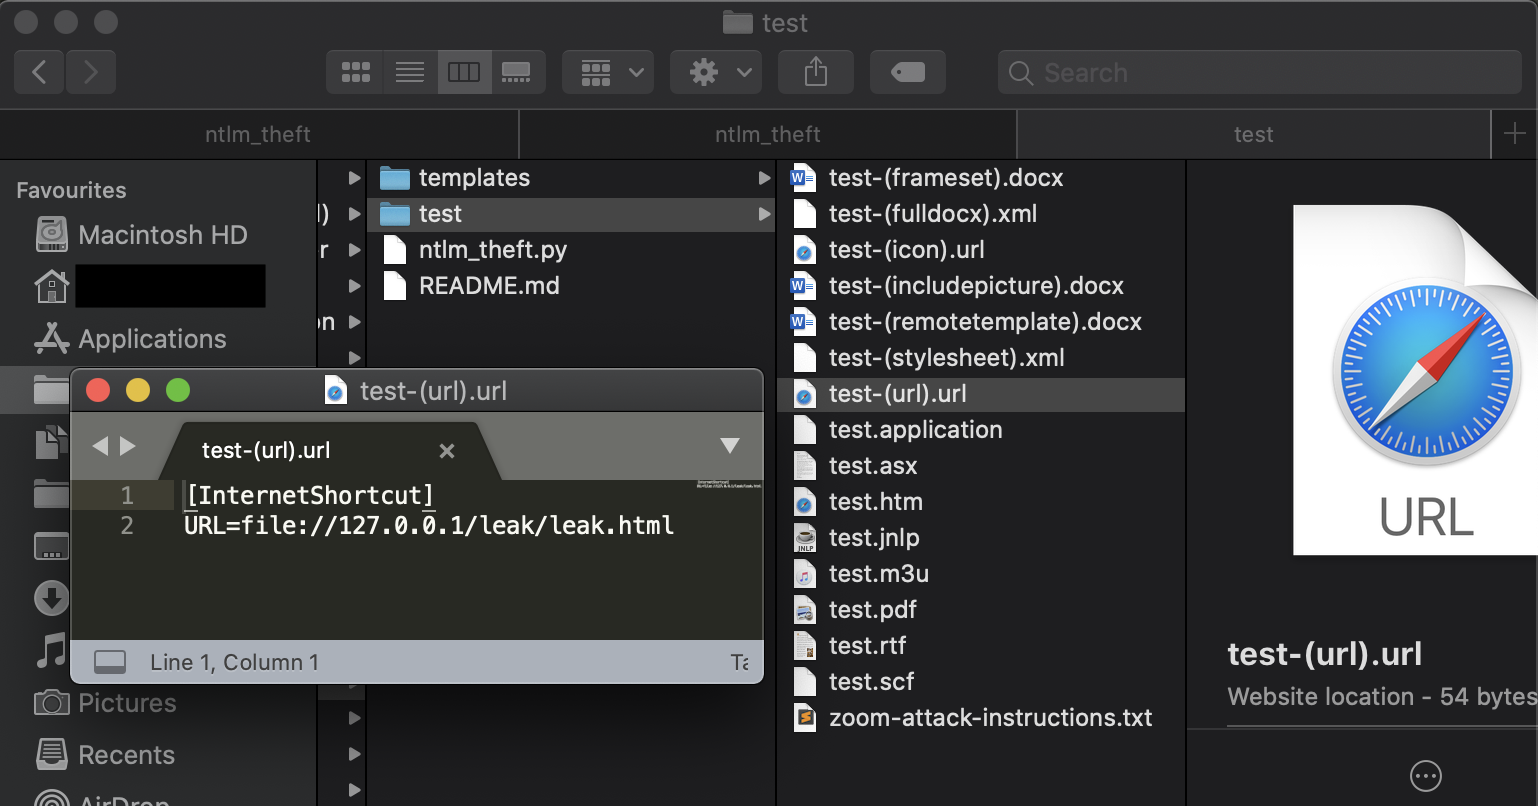 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
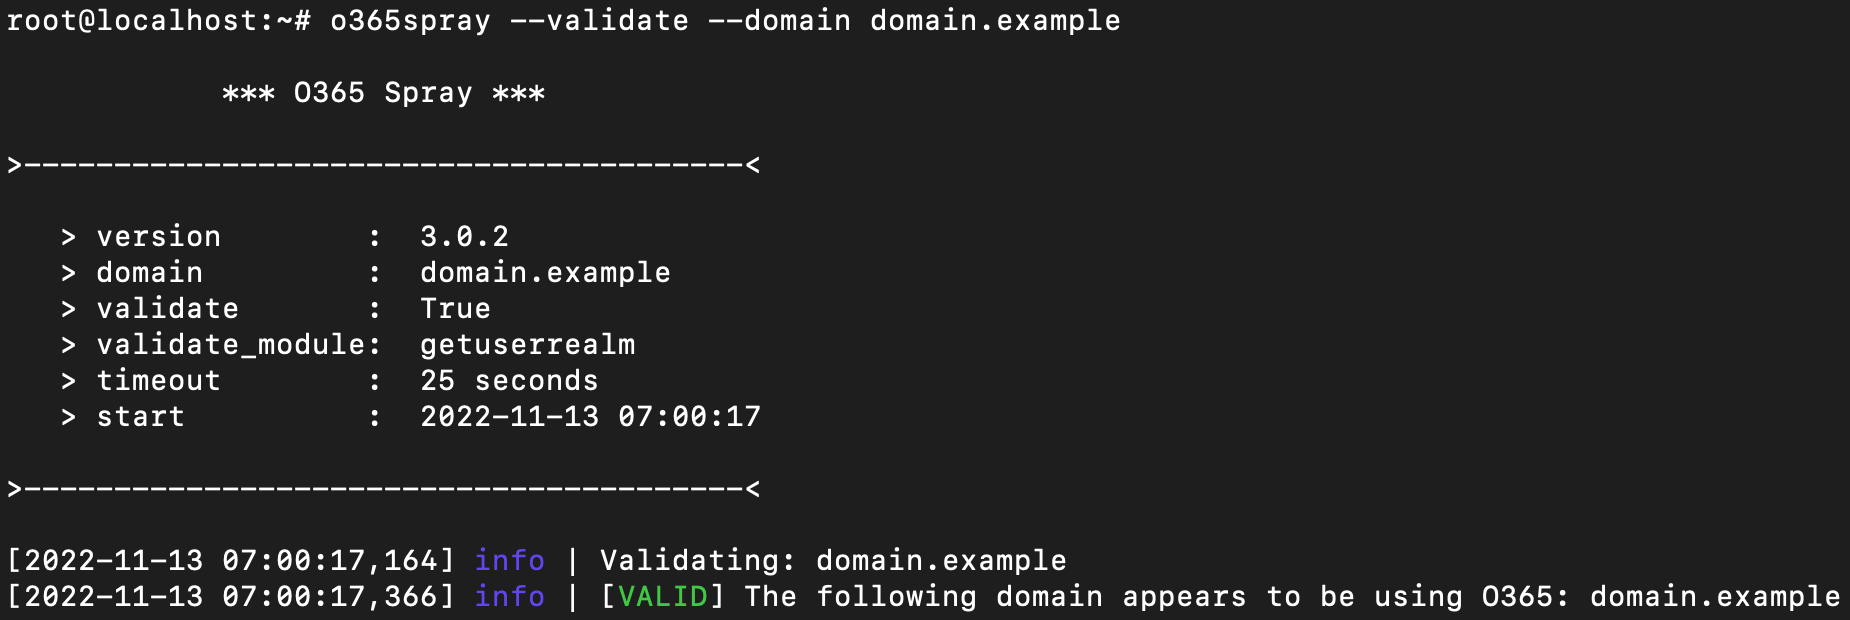 0xzdh/o365spray
Username enumeration and password spraying tool aimed at Microsoft O365.
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 nccgroup/hashcrack
Guesses hash types, picks some sensible dictionaries and rules for hashcat
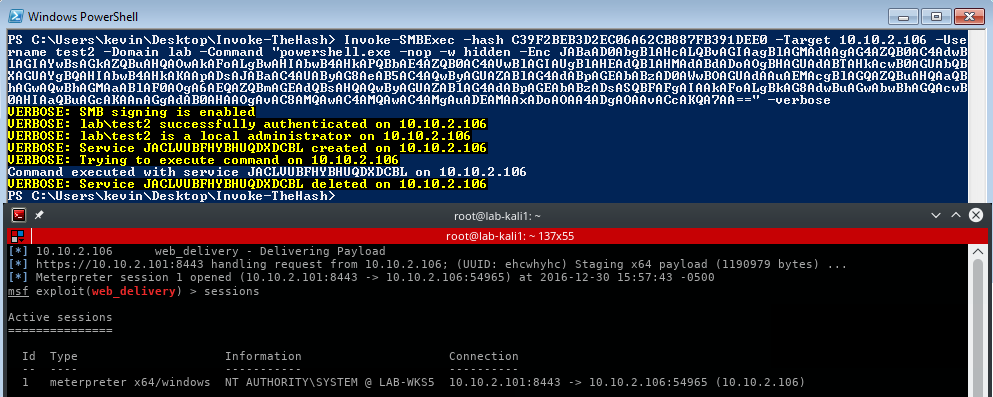 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 dozernz/bugstropics
Supporting material for the "Hunting Bugs In The Tropics" DEFCON 30 talk
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 nccgroup/scomdecrypt
SCOMDecrypt is a tool to decrypt stored RunAs credentials from SCOM servers
 nccgroup/jmxbf
A brute force program to test weak accounts configured to access a JMX Registry
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
 0xa1m/cve-2025-63353
This is a Proof-Of-Concept of CVE-2025-63353
 deetl/cve-2023-24055
POC and Scanner for CVE-2023-24055
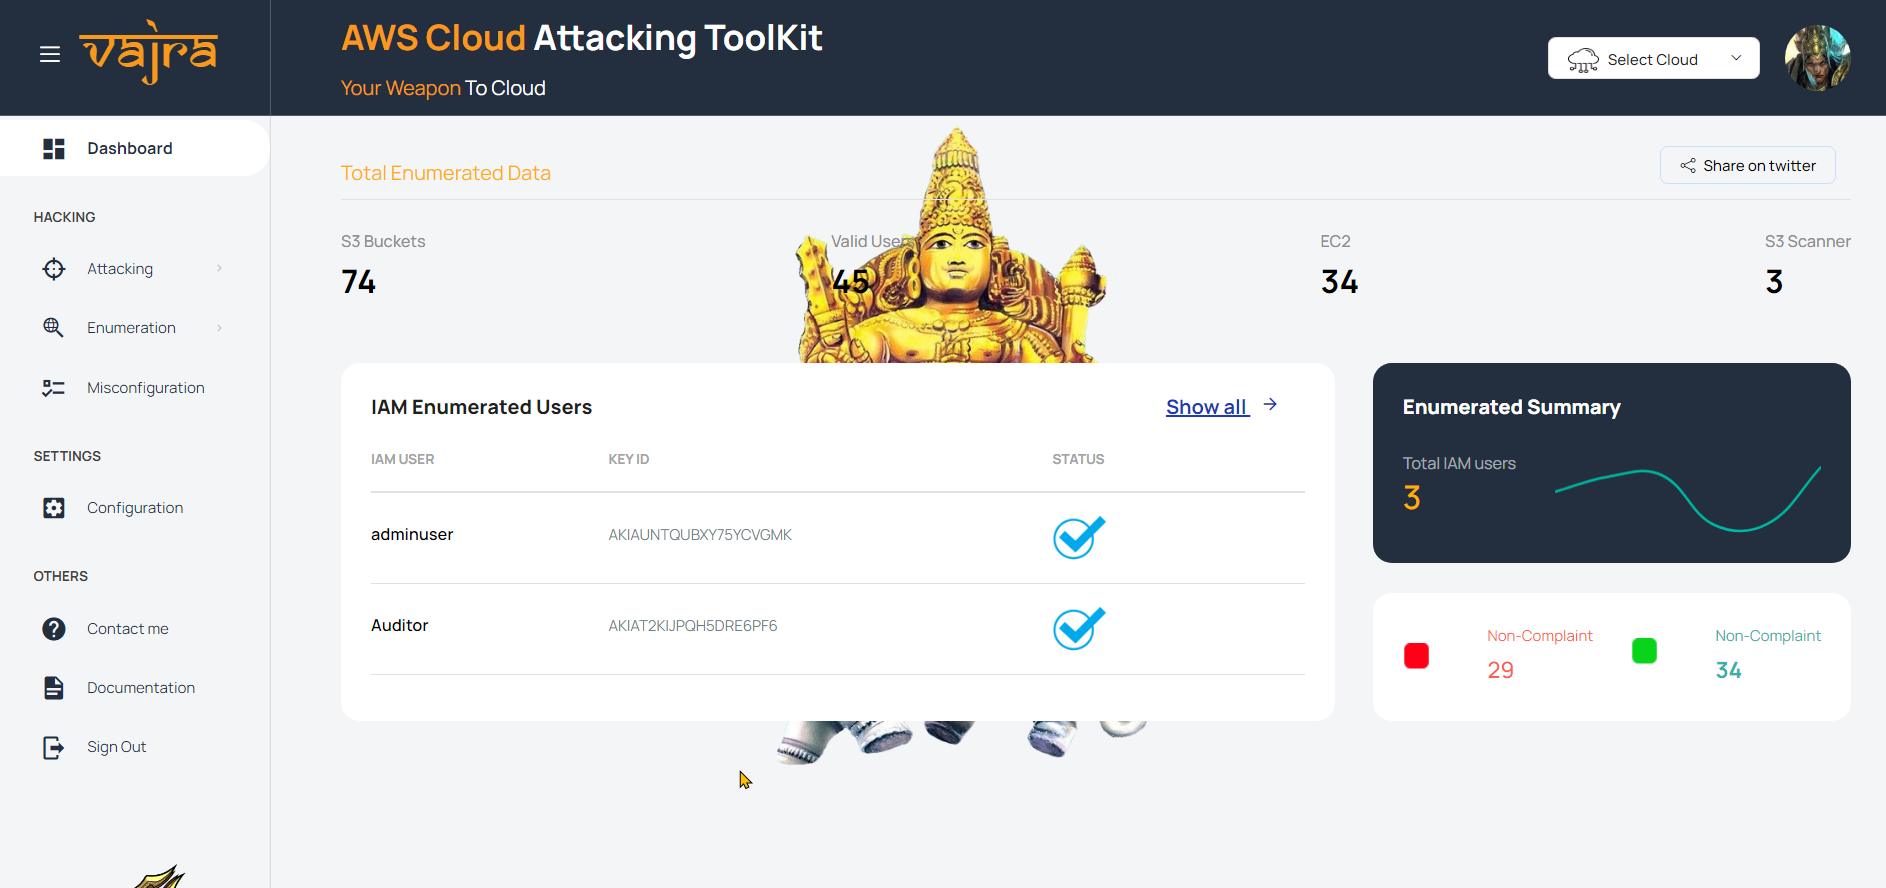 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…