Responder
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
authenticationdns-analysisdns-fuzzing+10
6.6k
lgandx/responderResponder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 ivancabrera02/hashsiphon
Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…
 atn1ght/fakeauth
Creates Fake Auth prompt to capture users plaintext passwords
 thesw0rd/cve-2026-27886-poc-account-takeover
Account takeover full PoC for CVE-2026-27886 in Strapi CMS
 brutemap-dev/brutemap
Let's find someone's account
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.
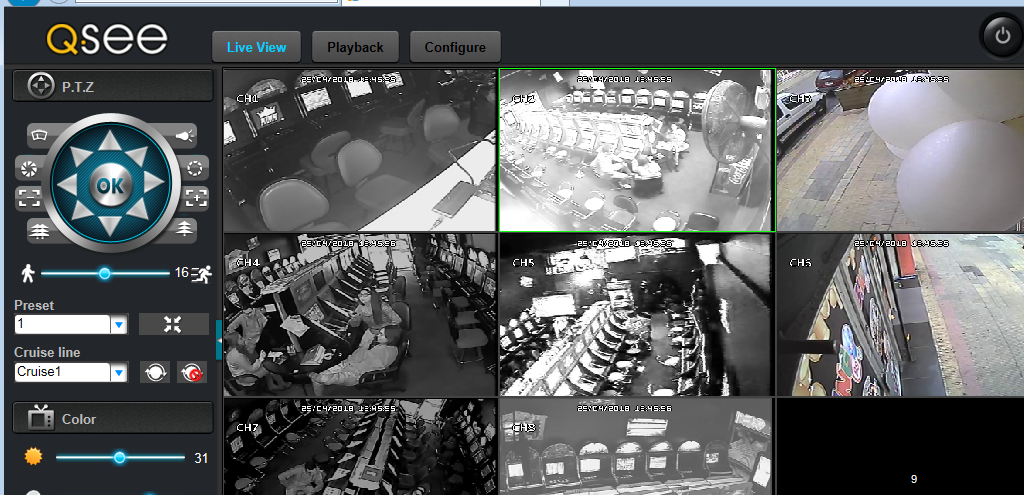 mrali-code/cve-2018-9995_dvr_credentials
Exploit tool for CVE-2018-9995 that extracts DVR credentials via unauthenticated HTTP request to vulnerable Nov, CeNova, QSee, and other DVR devices.
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
 likaifeng0/cve-2018-9995_dvr_credentials-dev_tool
Exploit tool for CVE-2018-9995 that extracts credentials from exposed DVR devices via HTTP request with cookie bypass, targeting multiple vendor…
 batmoshka55/cve-2018-9995_dvr_credentials
Exploit tool for CVE-2018-9995 that retrieves DVR credentials via crafted HTTP request, targeting multiple DVR vendors for security testing.
 pezwarinaan/cve-2014-0195
Exploit for CVE-2014-0195