
Abused-Legitimate-Services
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
curated-resourcespapers-researchphishing+2
61
bushidouk/abused-legitimate-servicesCloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 artur-augustyniak/class_struggle
Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
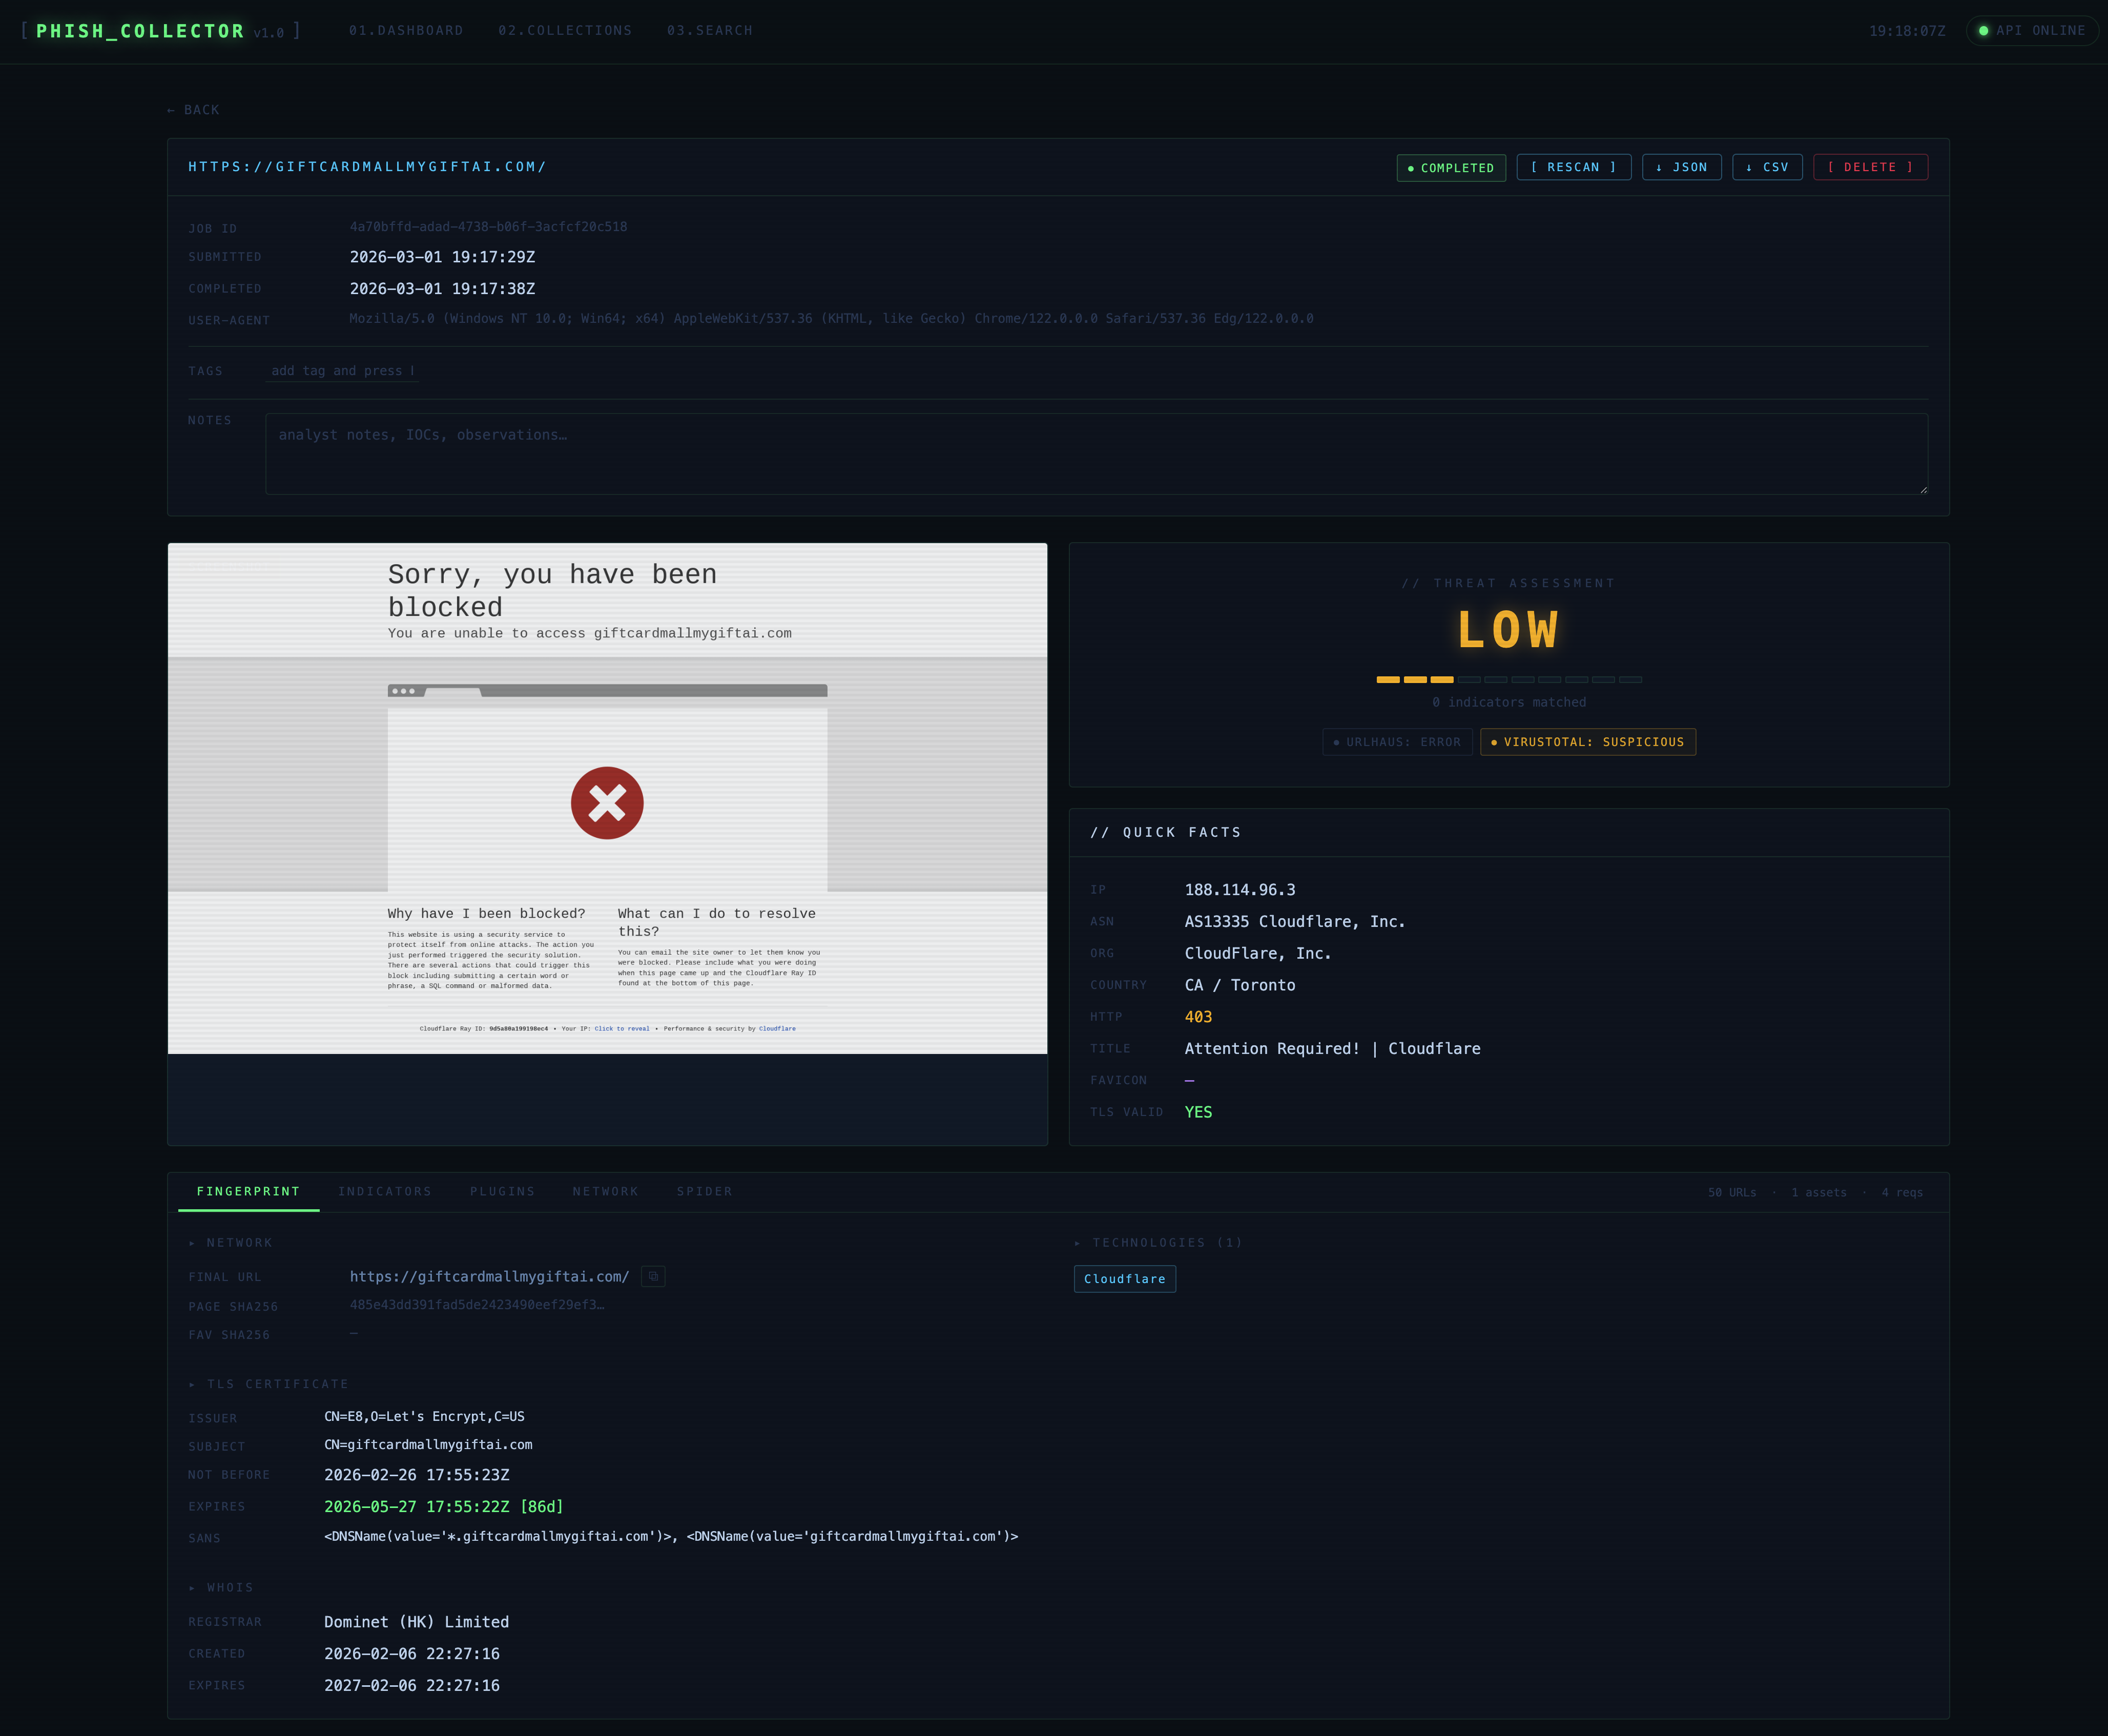 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 rub-nds/johnny-you-are-fired
Artifacts for the USENIX publication.
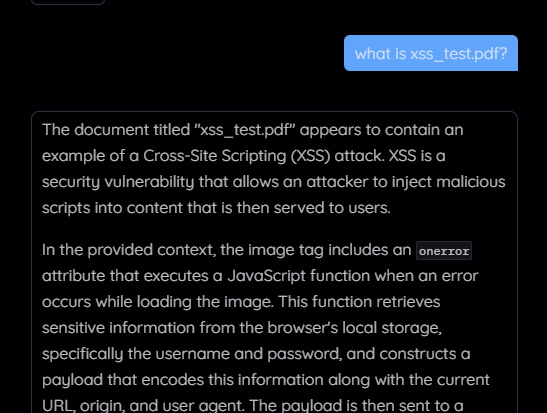 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
 strangerealintel/cyberthreatintel
Analysis of malware and Cyber Threat Intel of APT and cybercriminals groups
 pasquini-dario/project_mantis
Project Mantis: Hacking Back the AI-Hacker; Prompt Injection as a Defense Against LLM-driven Cyberattacks
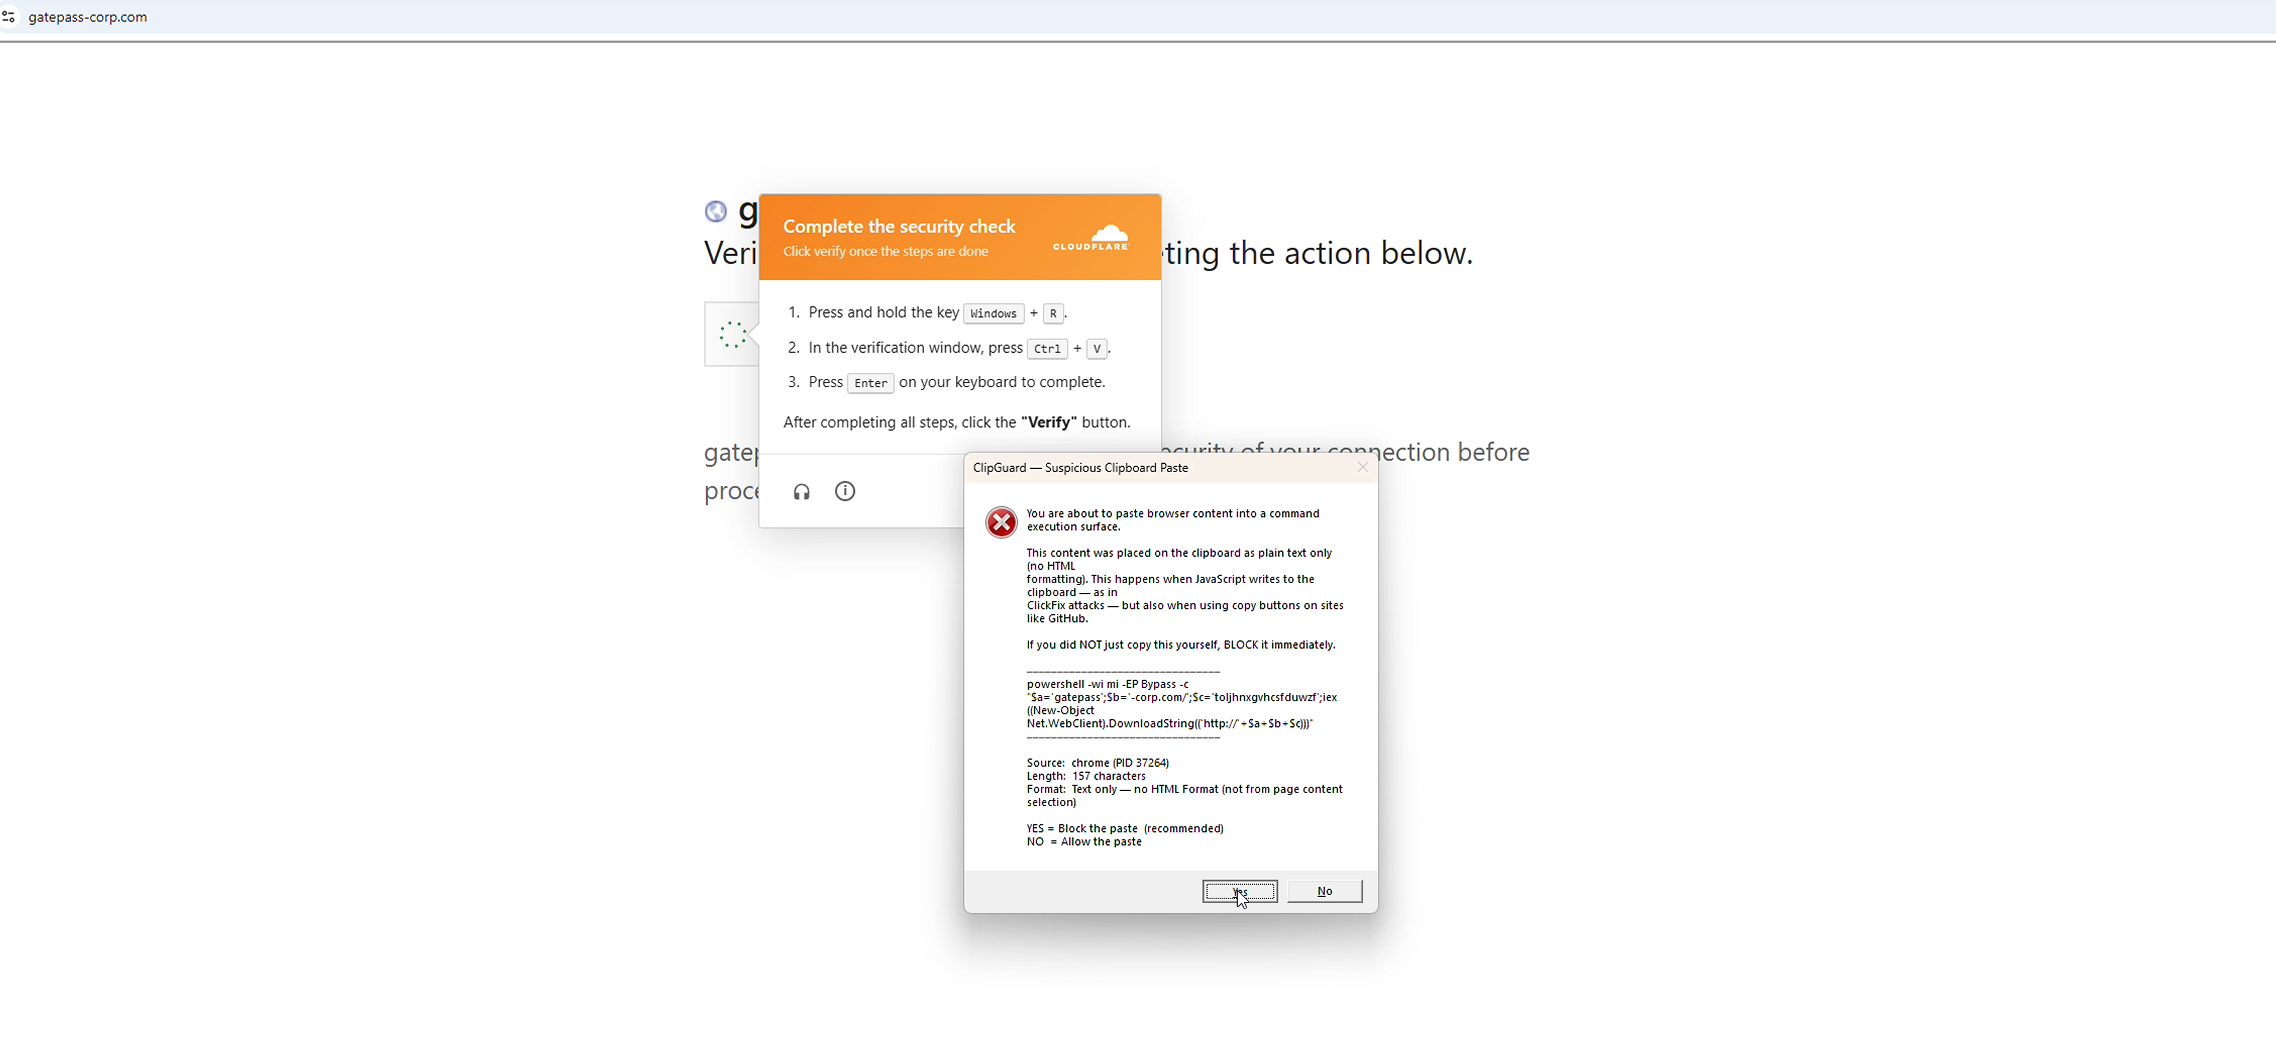 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
 romain-deperne/cve-2026-34975
CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5
 blueteamsteve/cve-2020-0601
Curated list of CVE-2020-0601 resources
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
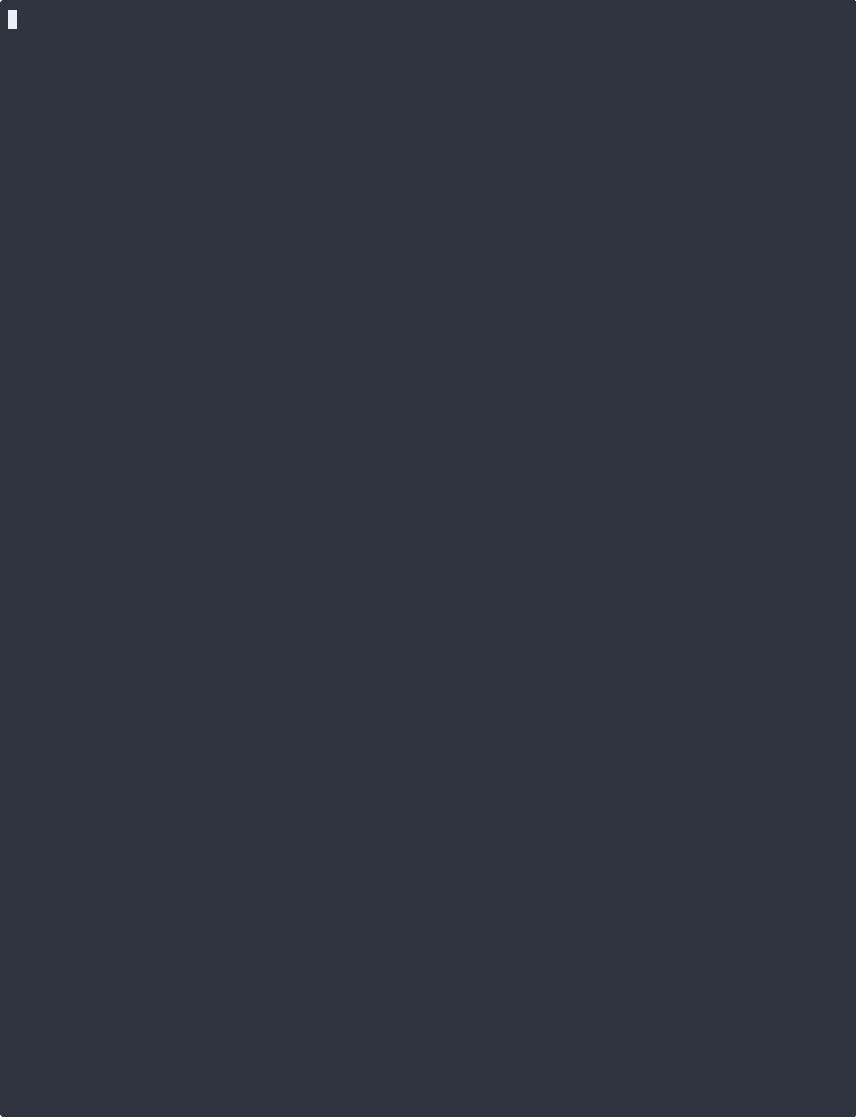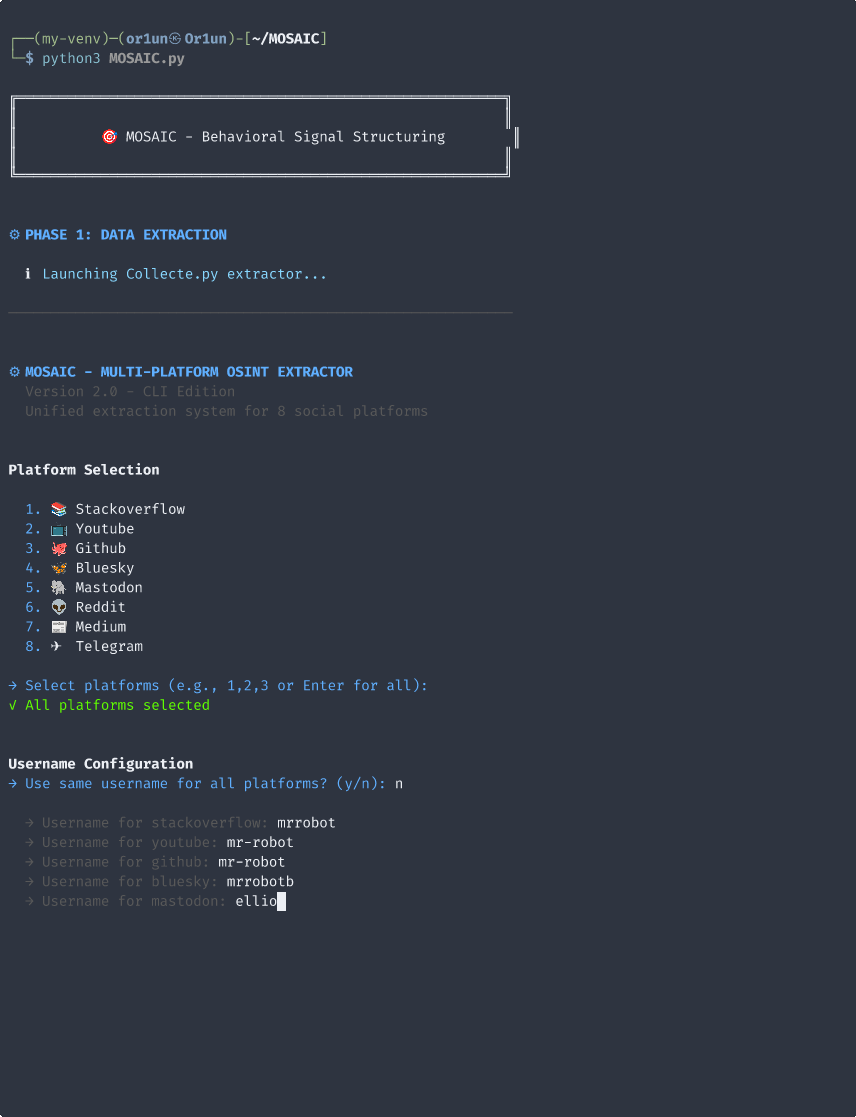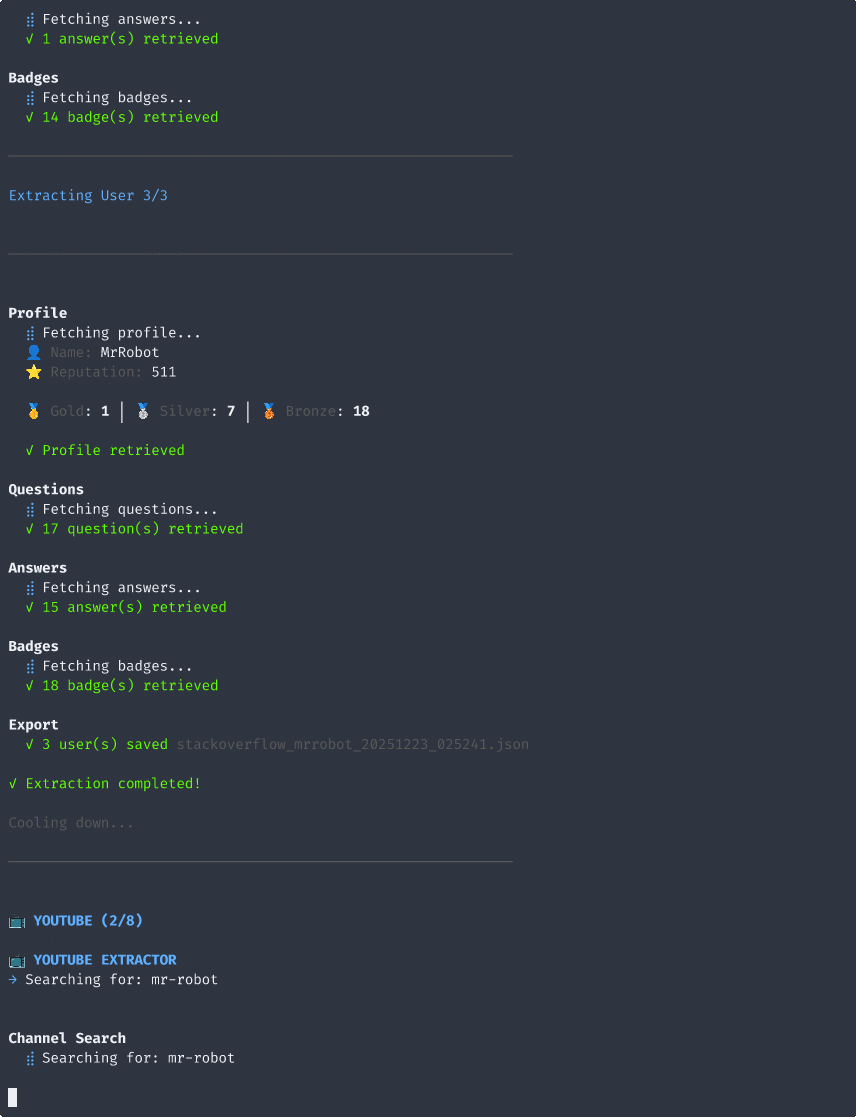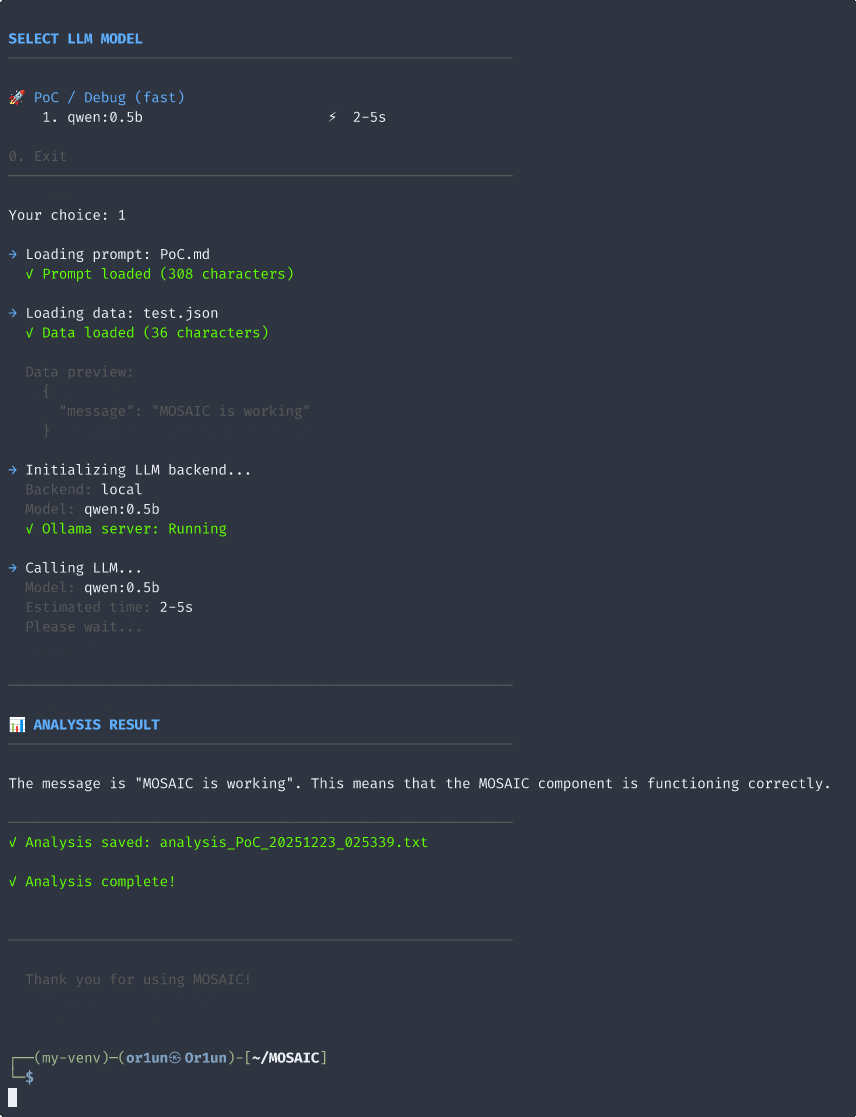 or1un/mosaic
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
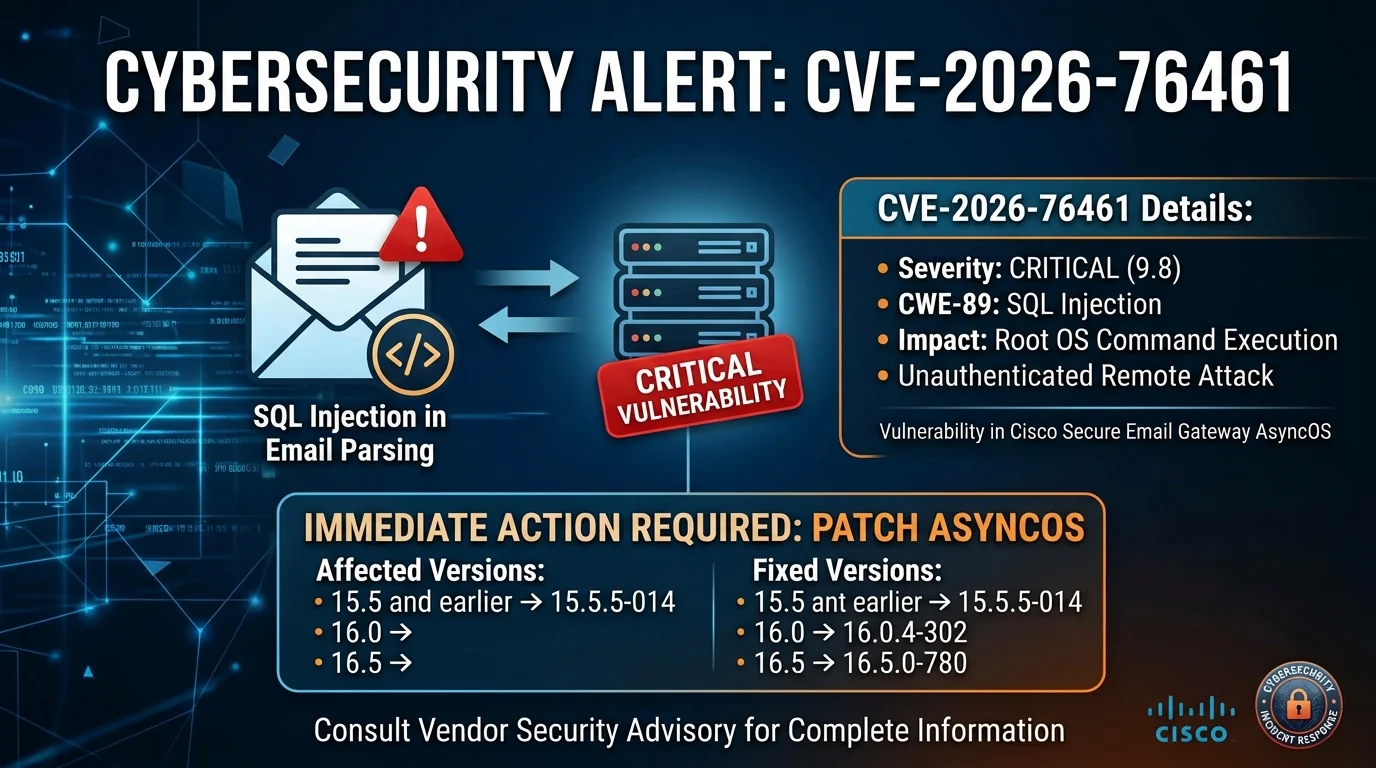 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
 dharmstm/cve-2026-30502-openkm-6.3.12-reflected-xss
Documentation and proof-of-concept for CVE-2026-30502, a reflected XSS vulnerability in OpenKM v6.3.12. Includes technical analysis, root cause,…