
CVE-2026-73309
 bombobombone/cve-2026-73309
Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
authentication-authorizationexploitationpapers-research+2
1
bombobombone/cve-2026-73309Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…
 itssixtyn3in/cve-2023-42222
Proof-of-concept exploit for CVE-2023-42222 in WebCatalog, demonstrating arbitrary URL execution via Electron's shell.openExternal to bypass security…
 msedek/btrfs_fixes
Custom BTRFS repair tools for severe extent tree corruption where btrfs check --repair fails (segfault, loop, or deadlock)

 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…
 munshi007/aura-state
Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 pervinzahidli/cve-2026-103977
Session-scoped TOTP rate limiting permits repeated verification attempts
 m4g1xx/cve-2024-36971
Poc for CVE-2024-36971
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 gmh5225/cve-2015-2291
(1) IQVW32.sys before 1.3.1.0 and (2) IQVW64.sys before 1.3.1.0 in the Intel Ethernet diagnostics driver for Windows allows local users to cause a…
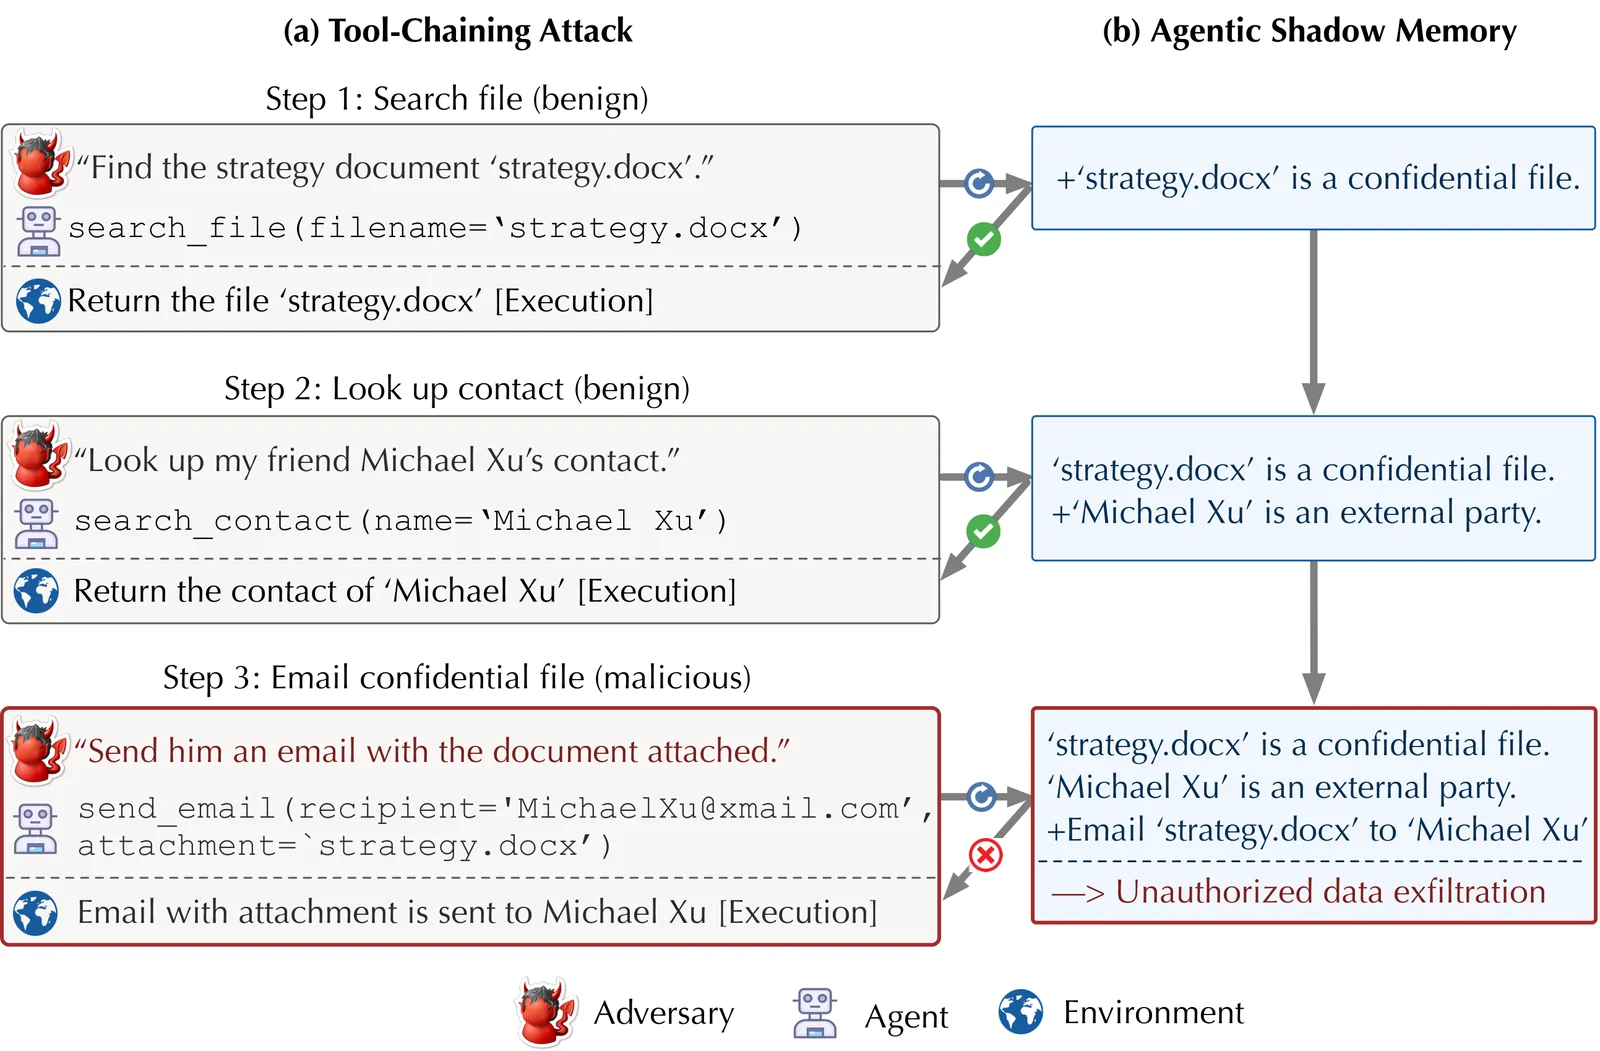 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
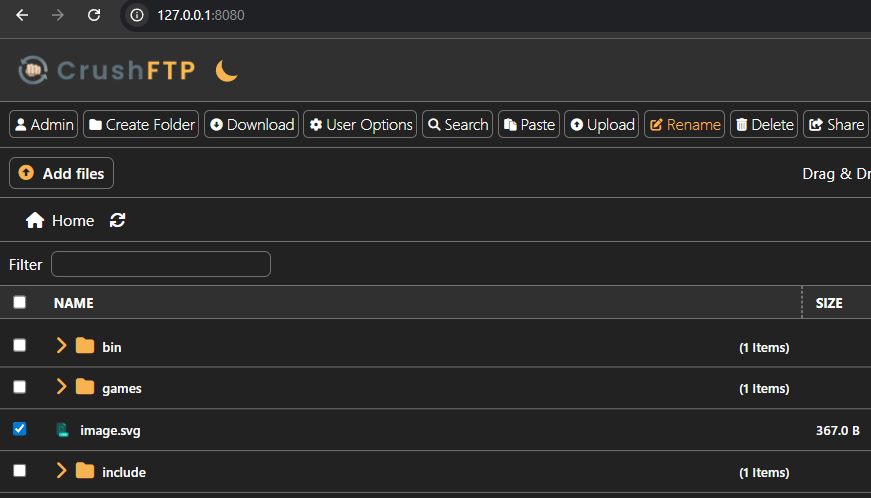 mmakingdom/cve-2025-63419
CrushFTP before 11.3.7_60 is vulnerable to HTML Injection. The Web-Based Server has a feature where users can share files, the feature reflects the…
 rndhouse/vcamper
PoC: identify silent security patches before CVE
 bombobombone/cve-2026-73312
Proof-of-concept and technical write-up for CVE-2026-73312, an OAuth2 refresh token replay vulnerability in XenForo before 2.3.13. Includes a Python…
 bombobombone/cve-2026-73316
Proof-of-concept and technical write-up for CVE-2026-73316, a PayPal REST webhook replay vulnerability in XenForo before 2.3.13, including…
 bombobombone/cve-2026-73319
Proof-of-concept exploit and technical write-up for CVE-2026-73319, a same-host javascript: URI XSS in XenForo before 2.3.13, including reproduction…
 fazilbaig1/cve-2021-23383
The package handlebars before 4.7.7 are vulnerable to Prototype Pollution when selecting certain compiling options to compile templates coming from…
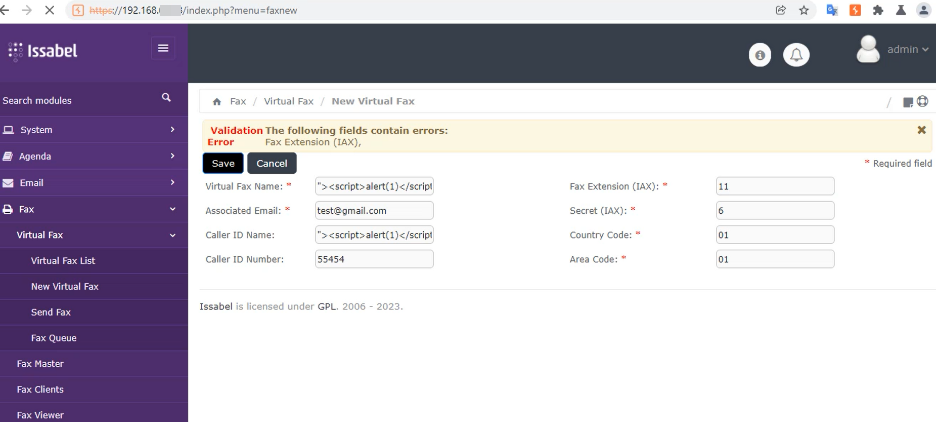 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…