
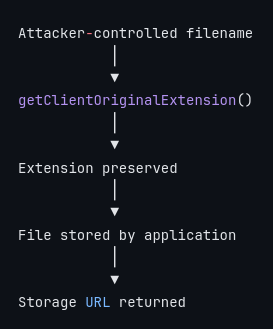
CVE-2026-38526-KrayinCRM
 ish3ng0m4/cve-2026-38526-krayincrm
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
educationexploitationpapers-research+5
ish3ng0m4/cve-2026-38526-krayincrmAuthenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
 ivanesk315/cve-2020-13671
Proof-of-concept exploit for CVE-2020-13671, a Drupal file upload vulnerability enabling remote code execution via crafted filenames.
 firstlax6t/cve-2026-36669-fengoffice
Detailed security advisory for CVE-2026-36669: unauthenticated arbitrary file upload in Feng Office, enabling stored XSS and session hijacking.…
 imxur/cve-2026-48908-joomla-sp-page-builder-rce
Technical analysis and advisory for CVE-2026-48908: Unauthenticated Arbitrary File Upload to RCE in JoomShaper SP Page Builder.
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
 lukasz-rybak/cve-2026-23499
CVE-2026-23499 - Saleor vulnerable to stored XSS via Unrestricted File Upload
 lukasz-rybak/cve-2026-27621
CVE-2026-27621 - TypiCMS Core has Stored Cross-Site Scripting (XSS) via SVG File Upload
 shubham03007/cve-2025-63830
Identified a Stored Cross-Site Scripting (XSS) vulnerability in CKFinder v1.4.3 via malicious SVG file upload leading to script execution upon file…
 gcatt-as/cve-2024-48591
Disclosure of a Cross-Site Scripting (XSS) vulnerability in Inflectra SpiraTeam 7.2.00 via malicious SVG file upload, with impact analysis and…
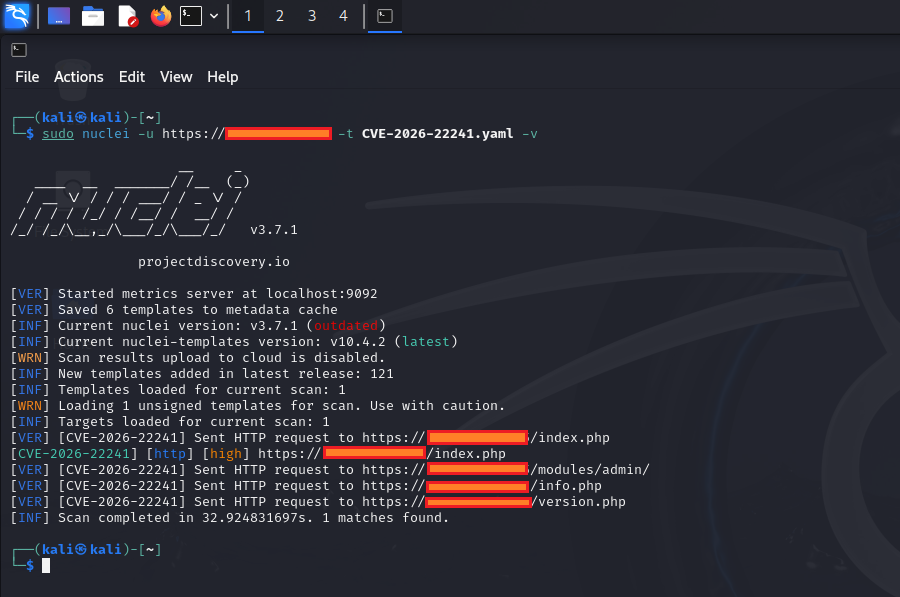
 sangrok-jeon/cve-2024-53677-analysis
CVE-2024-53677 취약점 분석 보고서
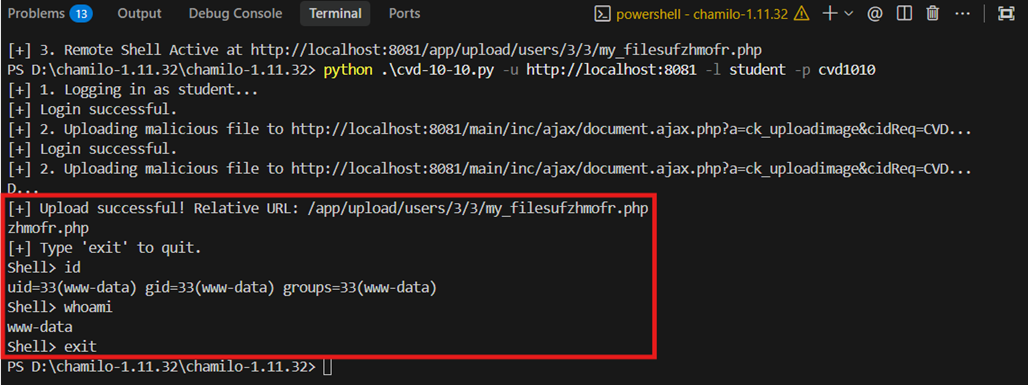 kx00007/cve-2026-29041
Hi, I’m K, This is my first CVE, which is a Remote Code Execution (RCE) vulnerability. It is the beginning of my journey as a security researcher.
 jonastrikex/cve-2026-14856-tastyigniter
Technical analysis and PoC for CVE-2026-14856, a stored XSS in TastyIgniter v4.3.0 Media Manager that chains with CSRF to achieve admin account…
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing