CVE-2026-43284-DIRTY-FRAG-

Technical analysis of CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm ESP local privilege escalation enabling page-cache writes to read-only files…

Technical analysis of CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm ESP local privilege escalation enabling page-cache writes to read-only files…

CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…

Universal local privilege escalation Proof-of-Concept exploit for CVE-2024-1086, working on most Linux kernels between v5.14 and v6.6, including…

Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…

Public exploit and research material for CVE-2026-42980, a Windows kernel WMI integer-underflow vulnerability enabling local privilege escalation to…

Exploits for CVE-2017-6008, a kernel pool buffer overflow leading to privilege escalation.

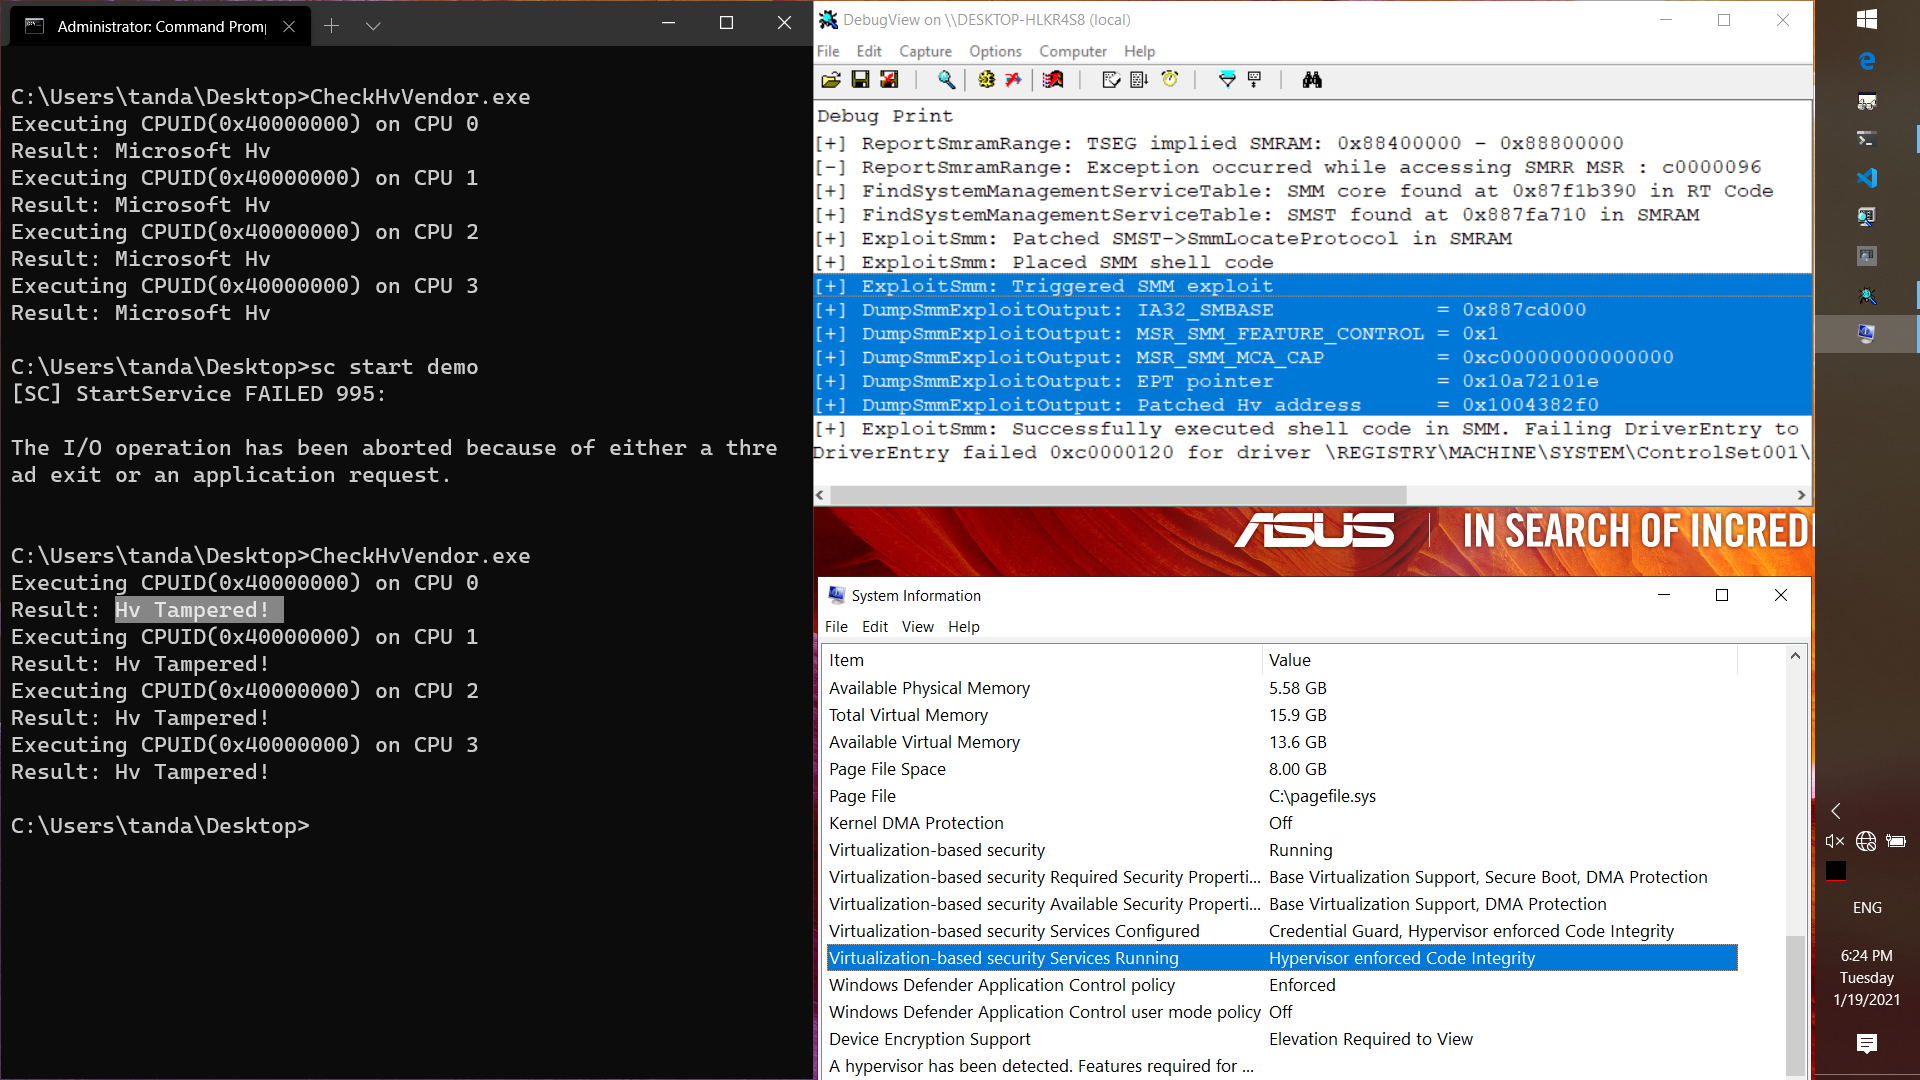
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.

Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…

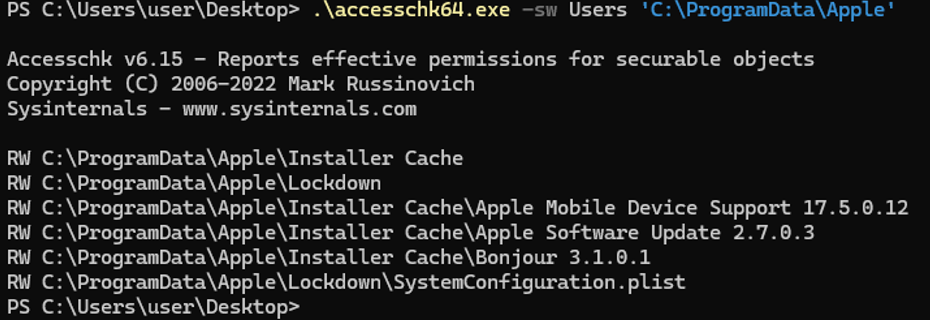
Hacking Windows through iTunes - Local Privilege Escalation 0-day

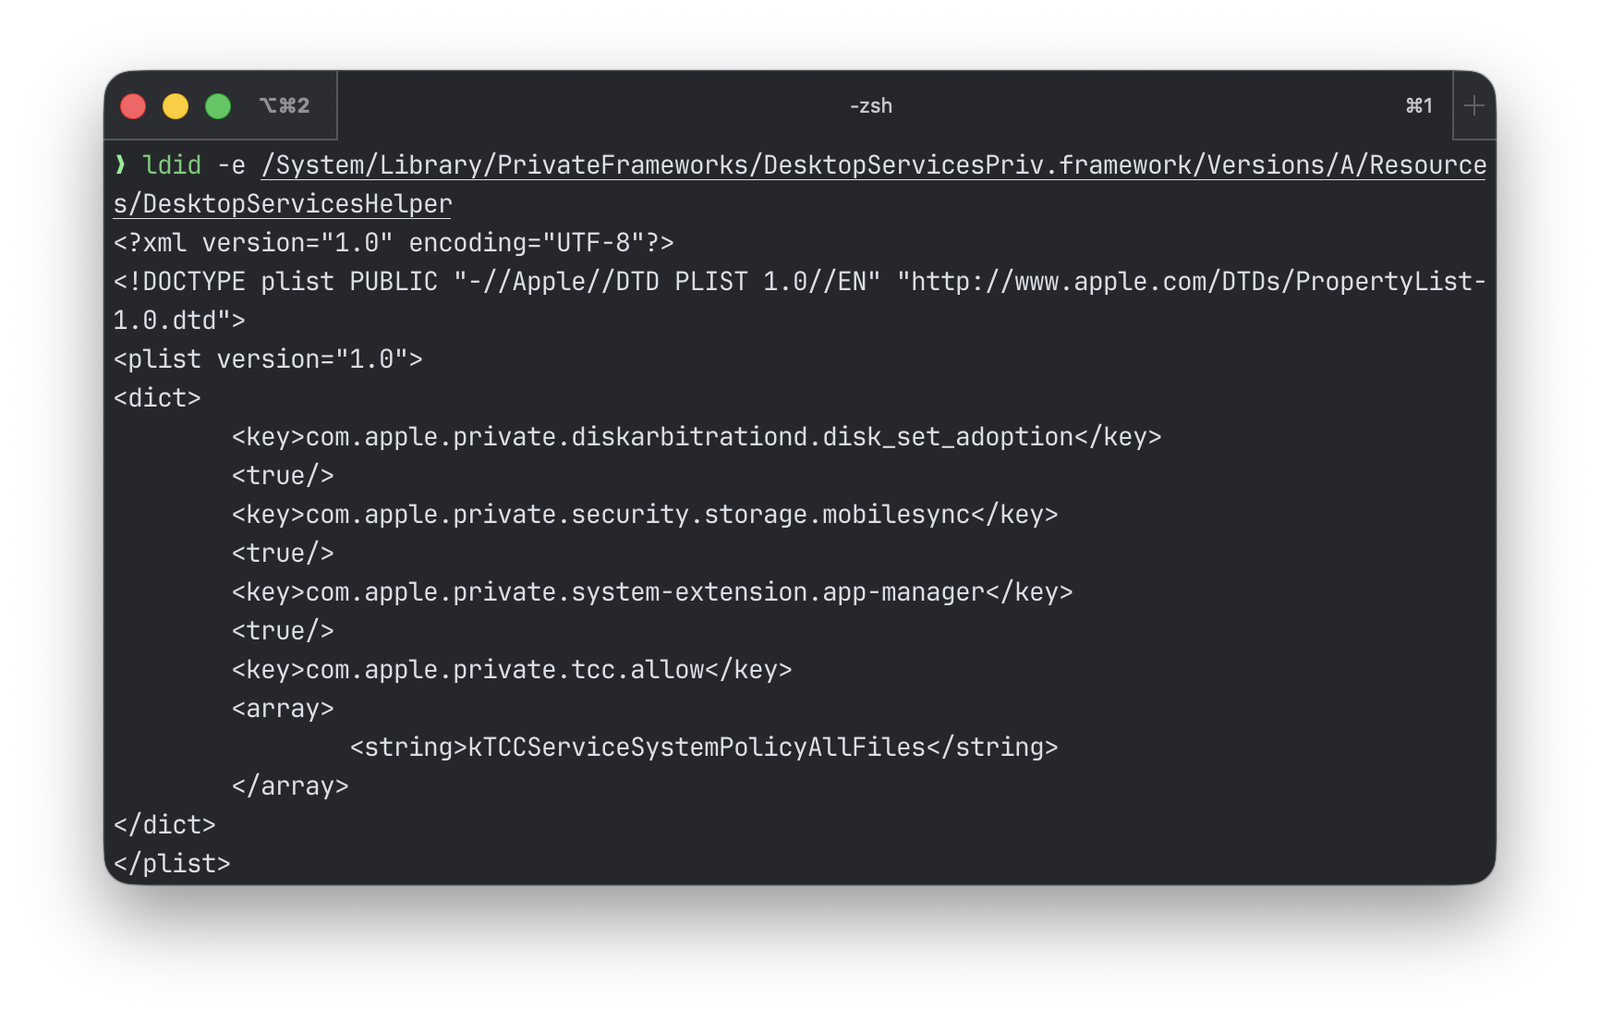
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…

CVE-2017-8890 exploit implementation with detailed analysis documents for privilege escalation on Ubuntu 16.04 and Nexus 6P kernels.

Log4j 2.15.0 Privilege Escalation -- CVE-2021-45046

Technical analysis and proof-of-concept exploit for CVE-2022-24934, a privilege escalation vulnerability in WPS Office's update mechanism allowing…

Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.

Linux kernel local privilege escalation PoC for CVE-2026-43503 (DirtyClone). Exploits a cloned sk_buff flag loss to write into page-cache memory,…

Local privilege escalation PoC for CVE-2026-74469, exploiting an SCTP diagnostic-reply kernel memory corruption to gain root on Linux x86-64 systems.

Proof-of-concept exploit for CVE-2024-21338, a Windows AppLocker driver (appid.sys) privilege escalation vulnerability used by Lazarus group as a…

Proof-of-concept exploit code for Linux kernel use-after-free vulnerabilities (CVE-2022-2585, CVE-2022-2586, CVE-2022-2588) enabling local privilege…