
CVE-2026-32202
 f0xox/cve-2026-32202
Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
exploitationinformation-gatheringpapers-research+4
f0xox/cve-2026-32202Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
 sbamit/exponentiated-gradient-descent-llm-attack
A novel adversarial attack on LLM based on the Exponentiated Gradient Descent technique.
 tubaaiftikhar-ui/moveit-transfer-data-breach-analysis.
Detailed analysis of the 2023 MOVEit Transfer data breach (CVE-2023-34362) for CS50 Cybersecurity. This project explores the technical impact of…
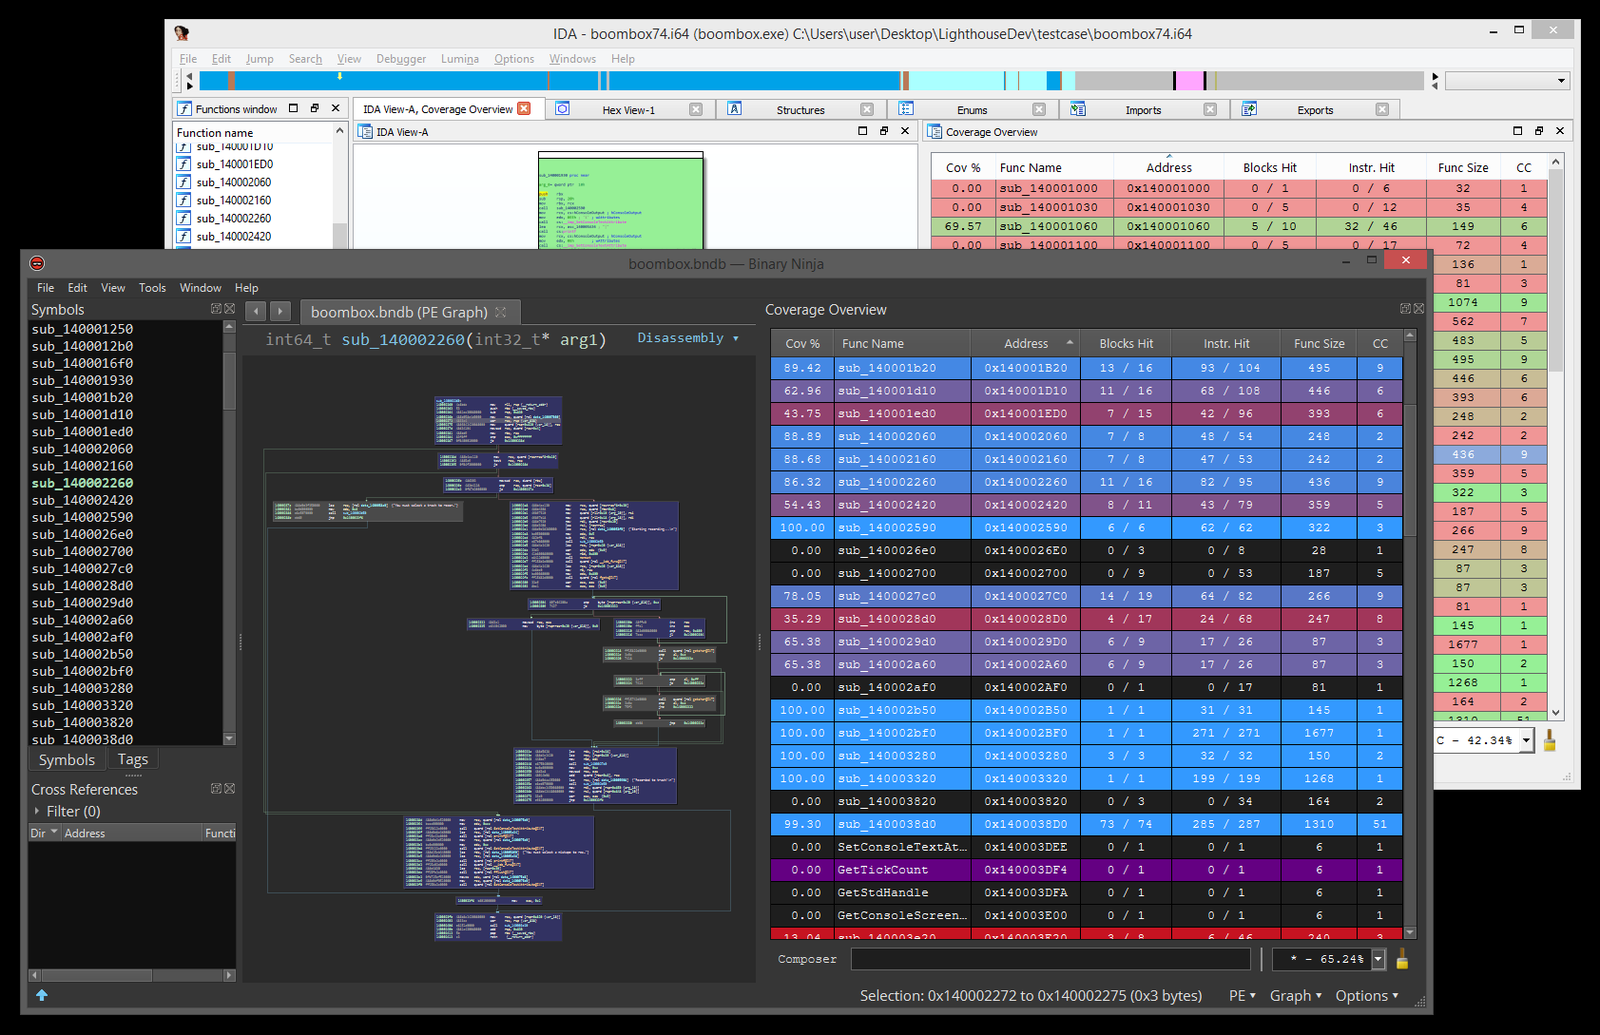 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers