
class_struggle
 artur-augustyniak/class_struggle
Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
anomaly-detectiondns-analysiseducation+4
2
artur-augustyniak/class_struggleAutoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
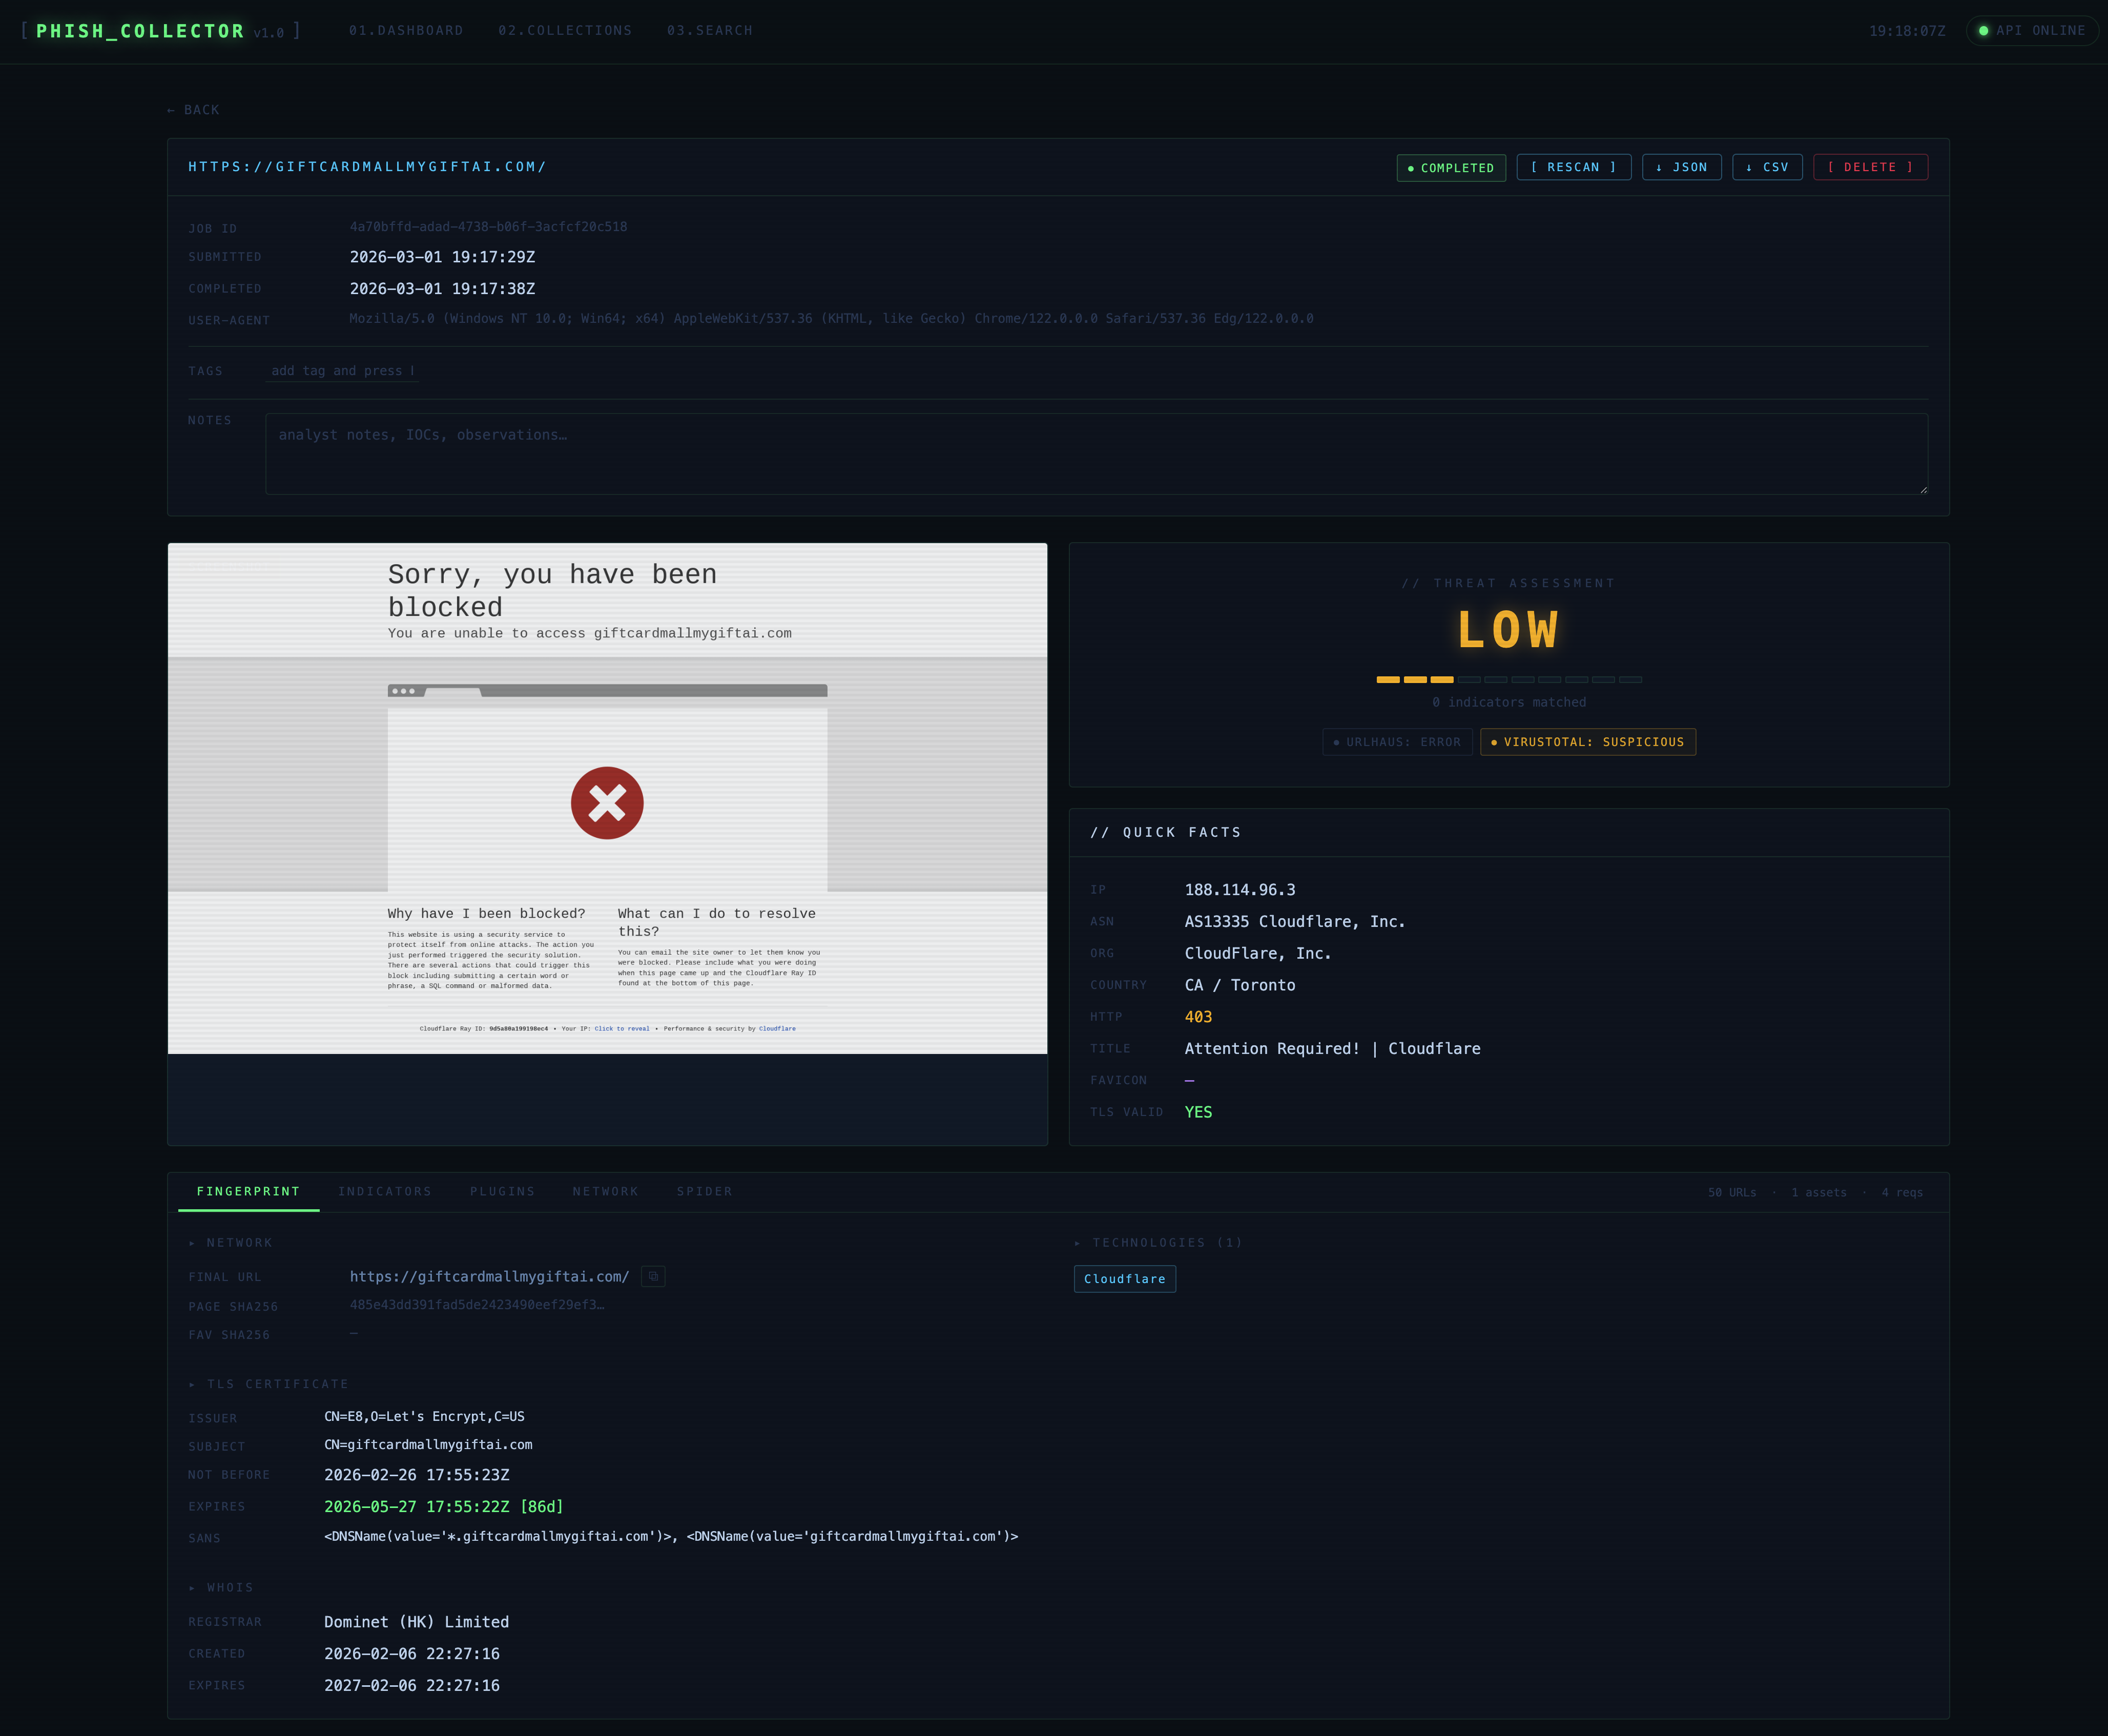 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 imthecopilotnow/cve-2025-4102025
Security advisory detailing a critical CVE in Copilot AI where RAG-based citation links are forged to a third-party domain, enabling source…
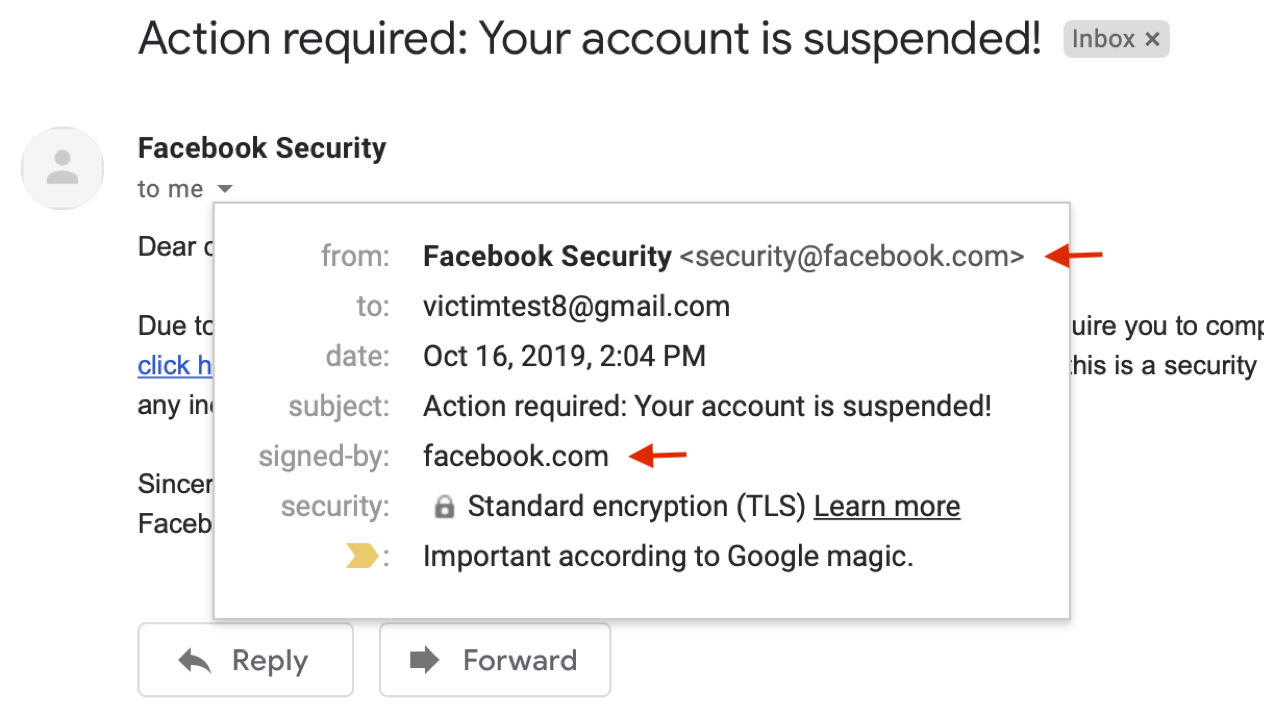 chenjj/espoofer
An email spoofing testing tool that aims to bypass SPF/DKIM/DMARC and forge DKIM signatures.🍻
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT
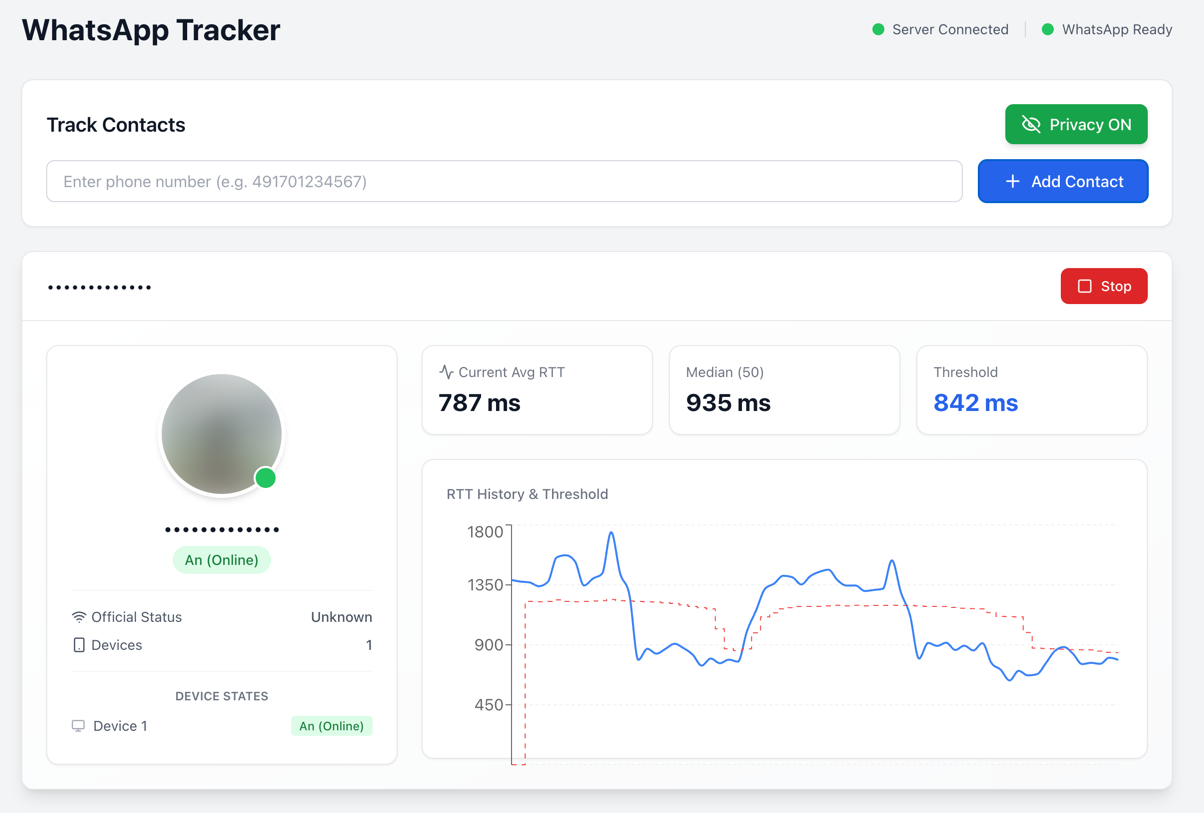 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 jakabakos/cve-2023-36884-ms-office-html-rce
MS Office and Windows HTML RCE (CVE-2023-36884) - PoC and exploit
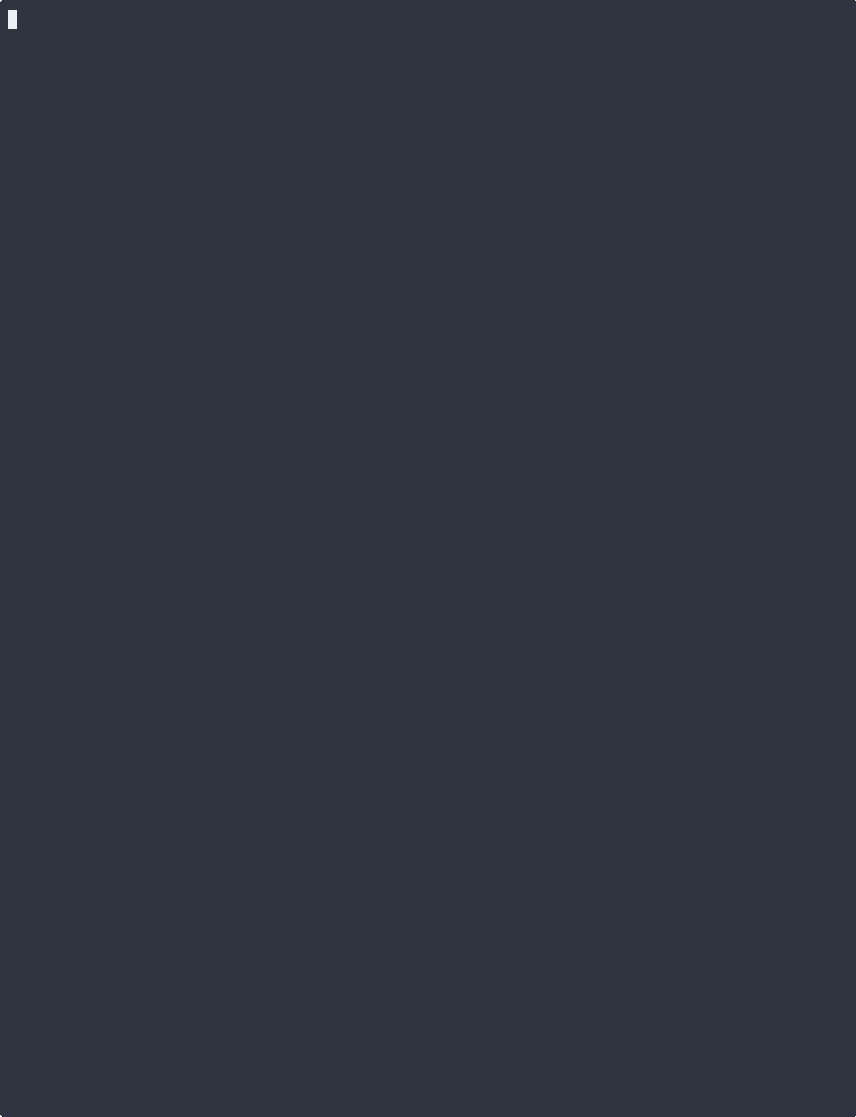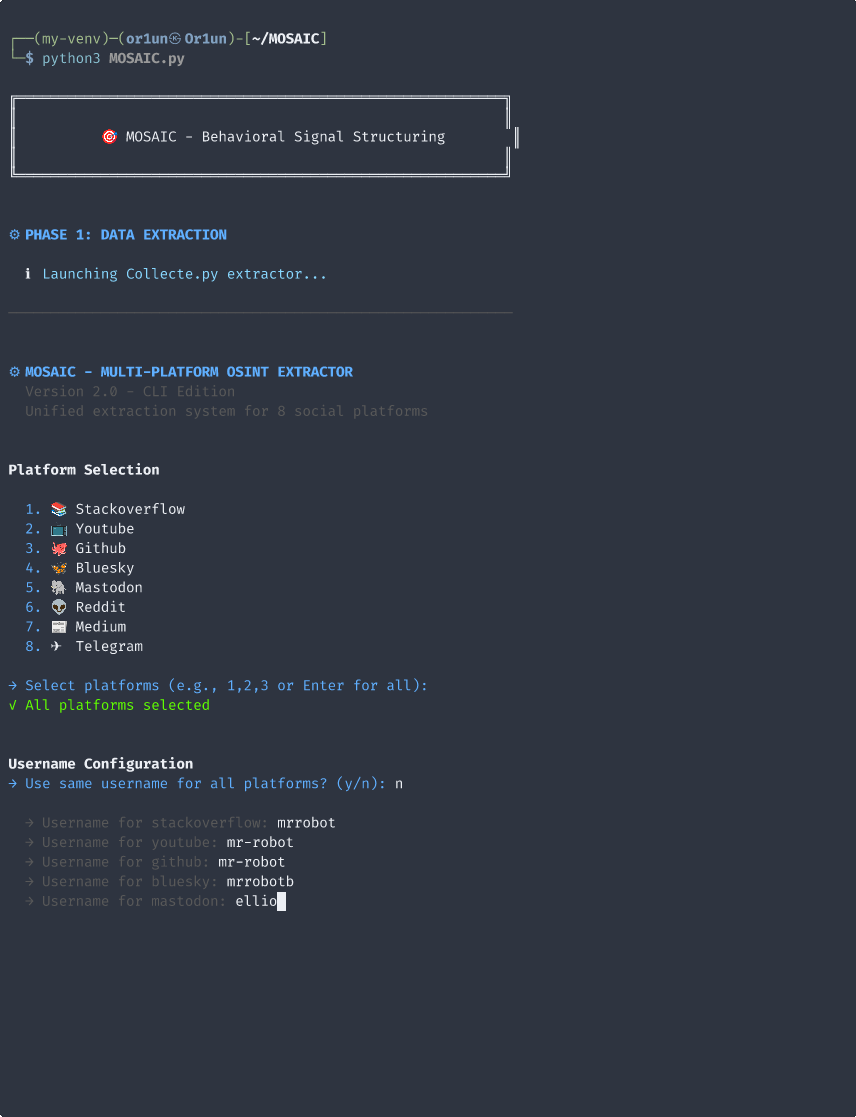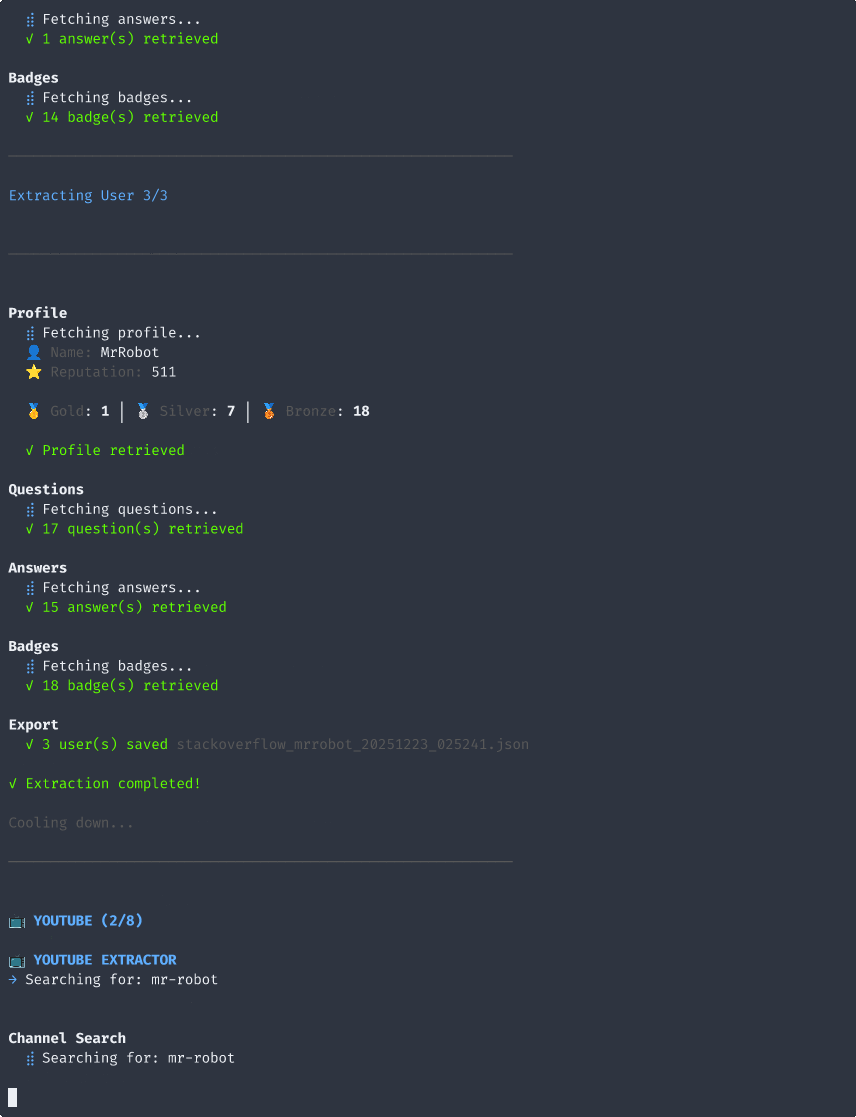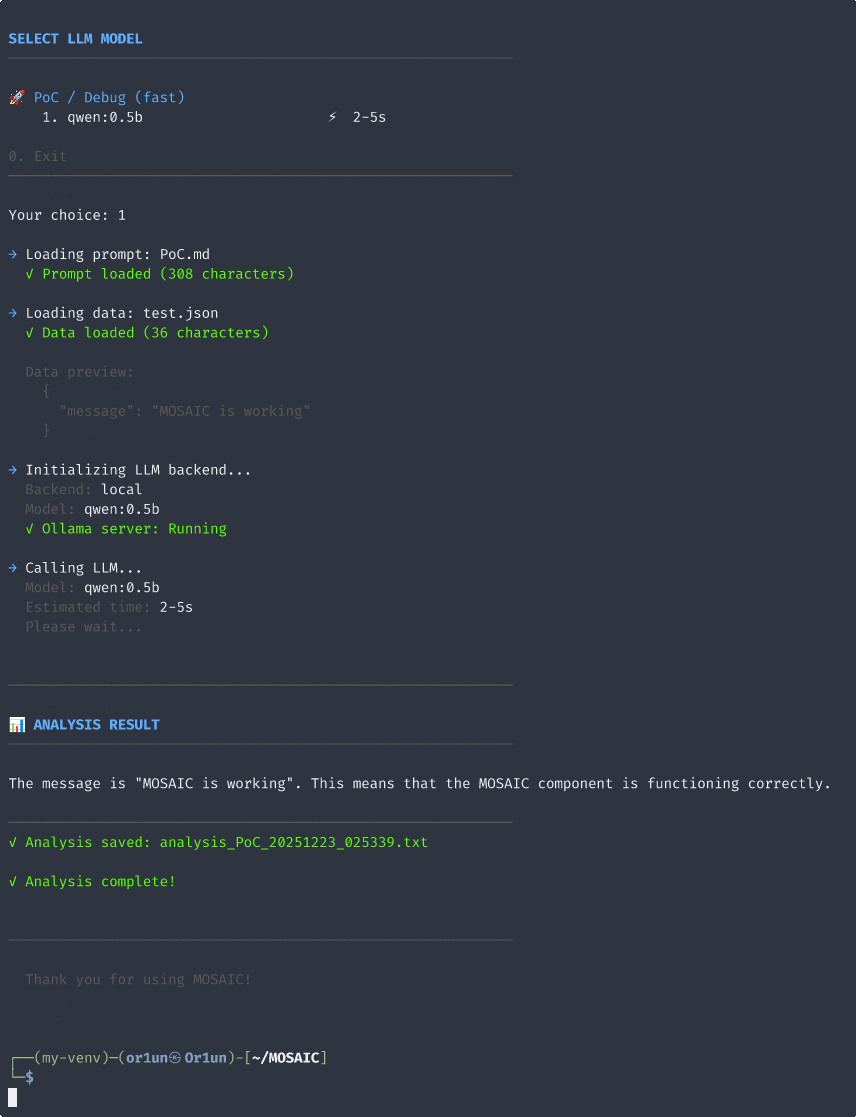 or1un/mosaic
Privacy-first, experimental implementation of a sociological framework for multi-platform positional analysis.
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
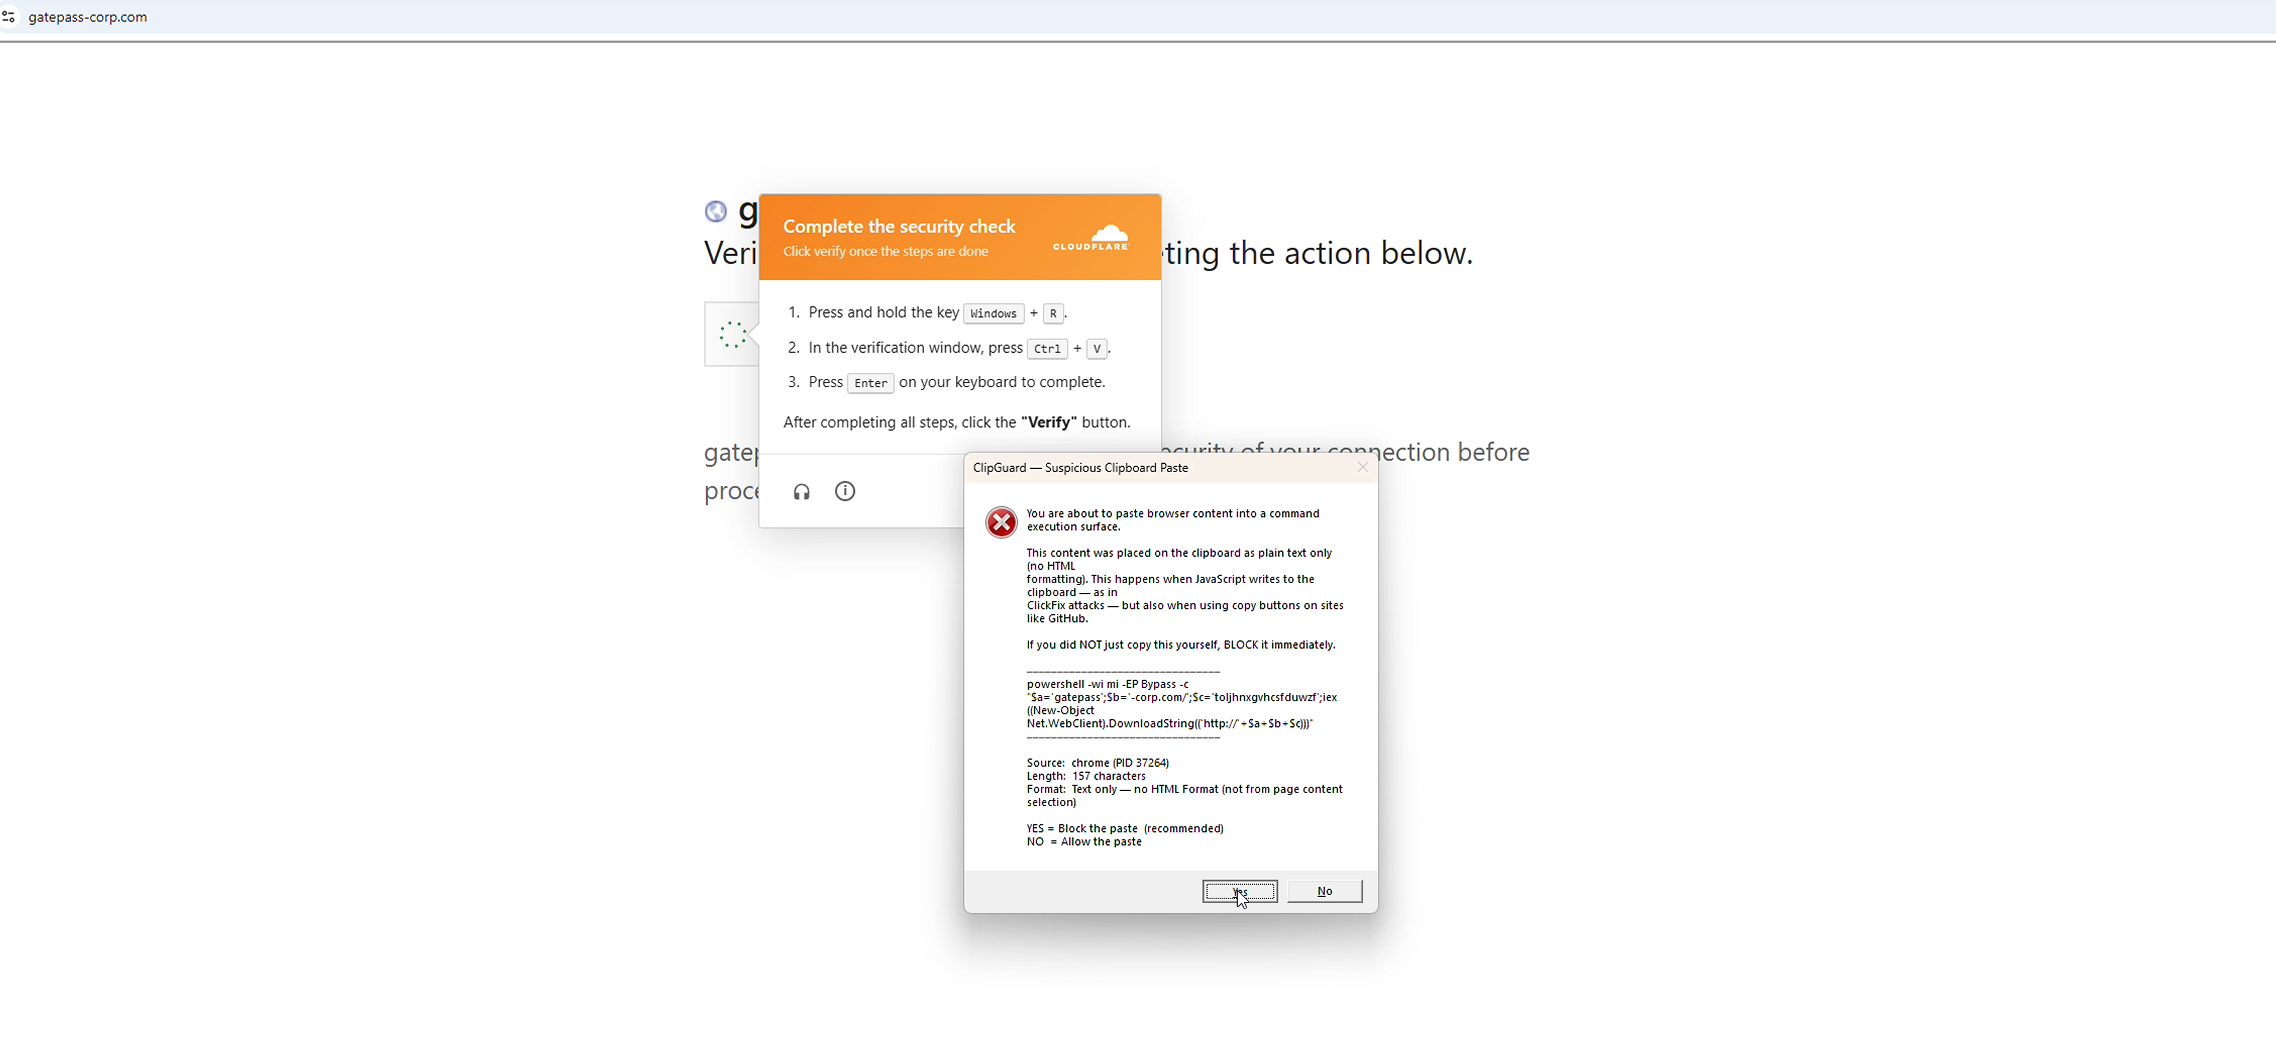 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
 unhackerencapital/pdfernetremotelo
PoC - Prueba de Concepto de CVE-2024-4367 en conjunto al CVE-2023-38831 en un solo Script
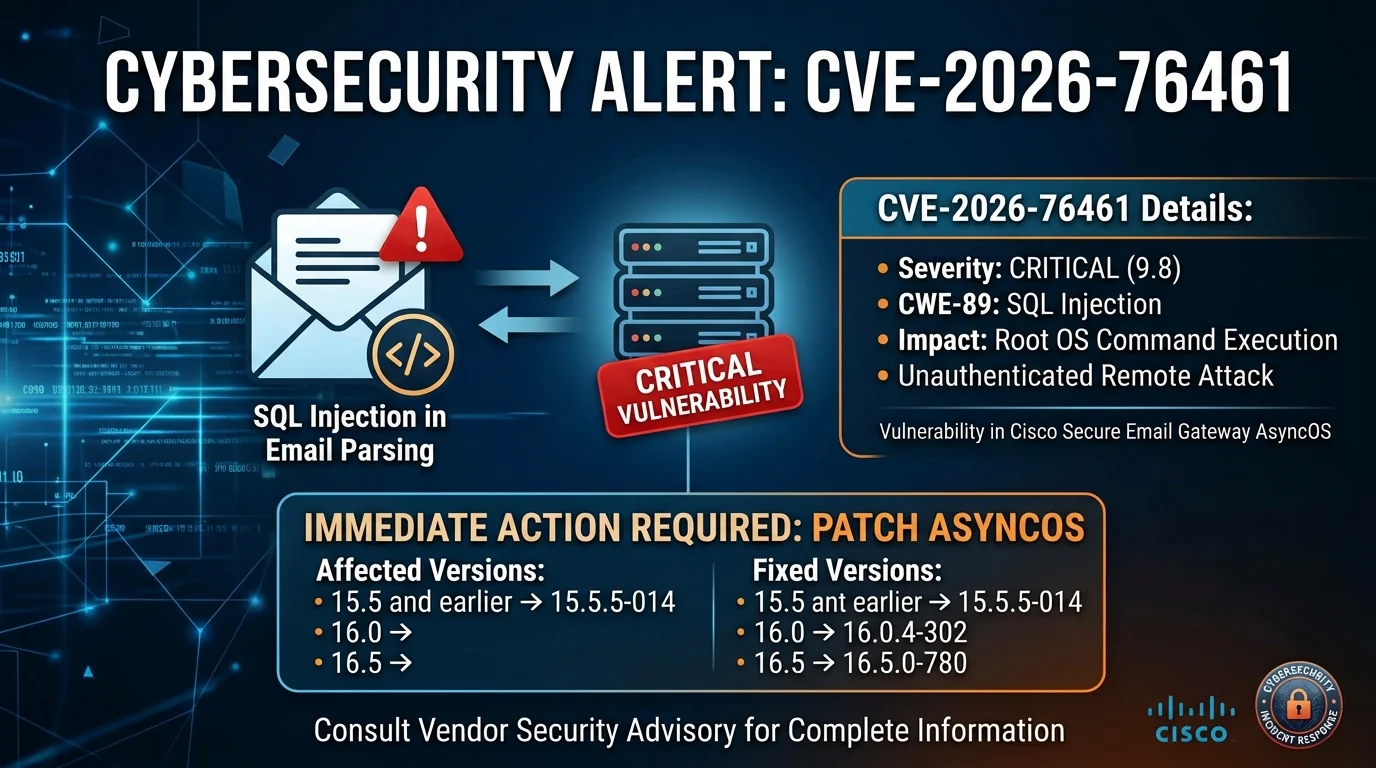 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
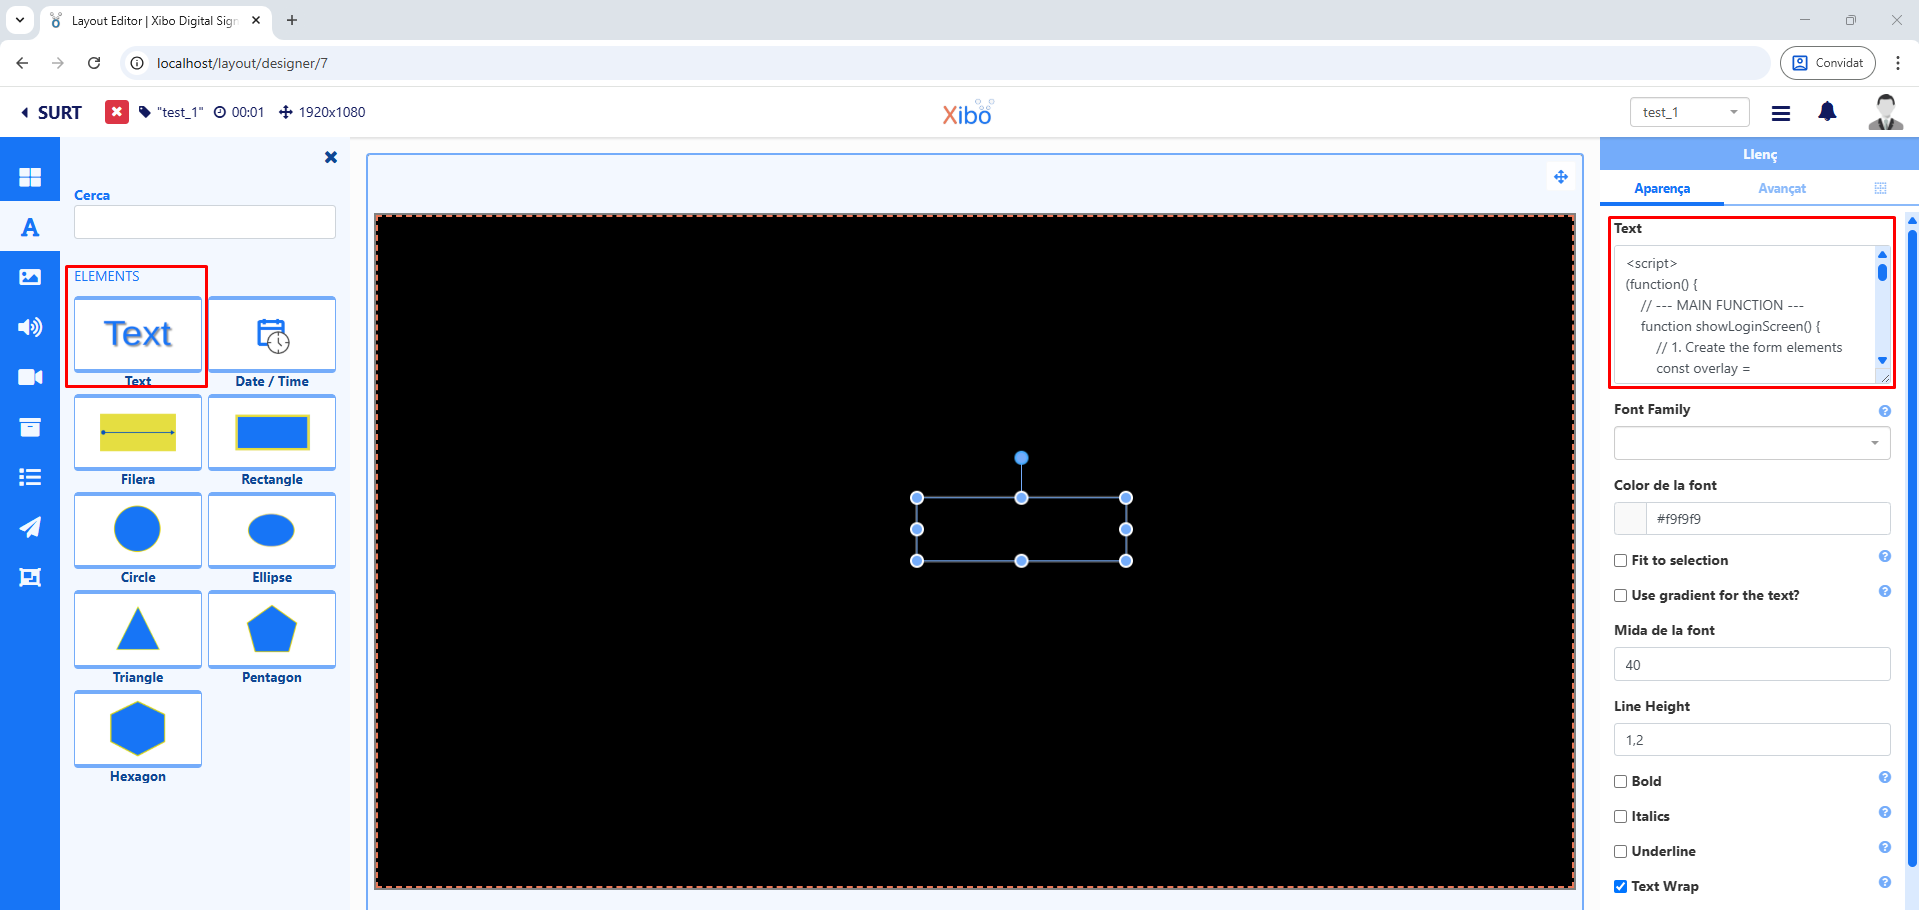 marinafabregat/cve-2025-41088
Stored Cross-Site Scripting (XSS) in Xibo Signage's Xibo CMS v4.1.2, due to a lack of proper validation of user input.
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).