CVE-2023-38831-WinRAR-Vulnerability-Analysis

This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…

This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…

Awesome-Cellular-Hacking

CVE-2024-4367

Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…

An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…

This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…

Project focused on governance and risk in application security, providing resources and frameworks for security maturity and risk management.

OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.

CVSS v3.1 assessment of CVE-2009-0658 (Adobe Acrobat Buffer Overflow), including Base, Temporal, and Environmental scoring and remediation…

Research and hands-on PoC of Spectre Variant 2 (CVE-2017-5715), a hardware side-channel vulnerability exploiting CPU speculative execution and branch…

Simulation code and report for CVE-2015-2315, demonstrating the vulnerability exploitation scenario for educational analysis.

Reproduces and analyzes CVE-2026-3494, an audit logging bypass in MariaDB server_audit plugin, using Docker-based multi-version testing to compare…

Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.

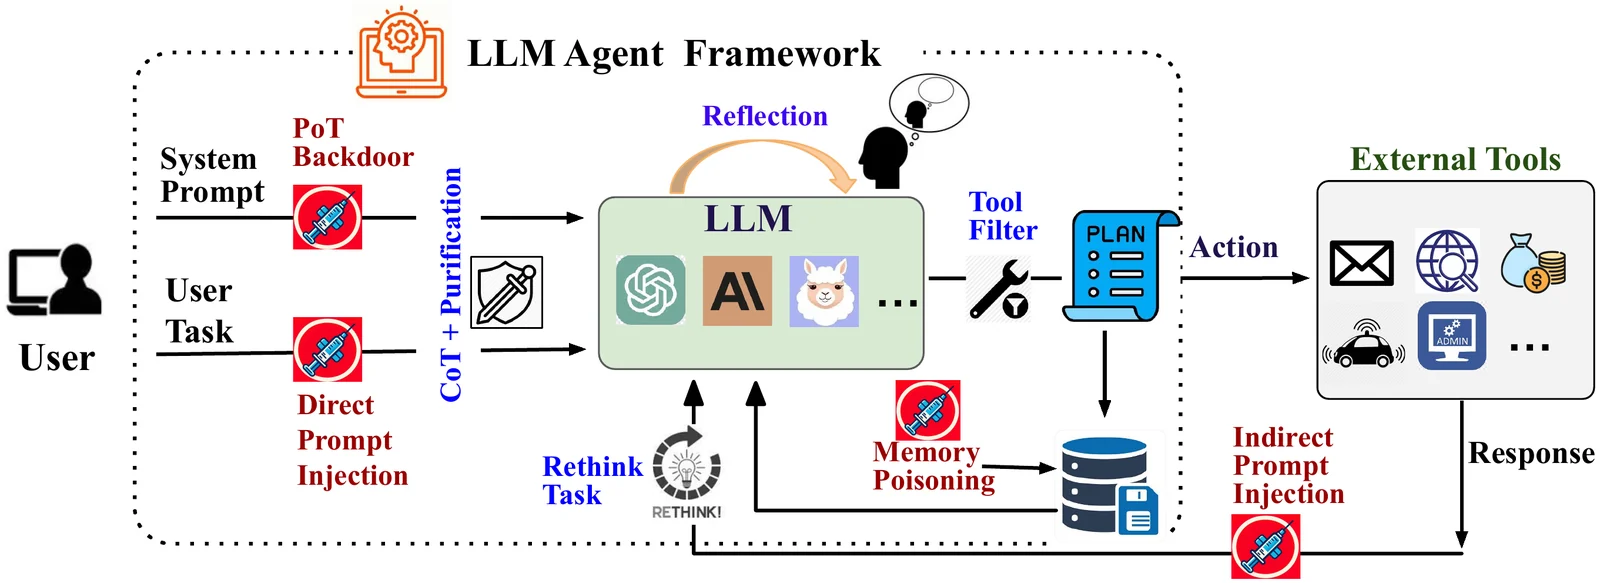
Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…

Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…

This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…

A local package installation helper trusted caller-supplied package names too much. In yeoman-environment, missing generators could be installed…