Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
88 results
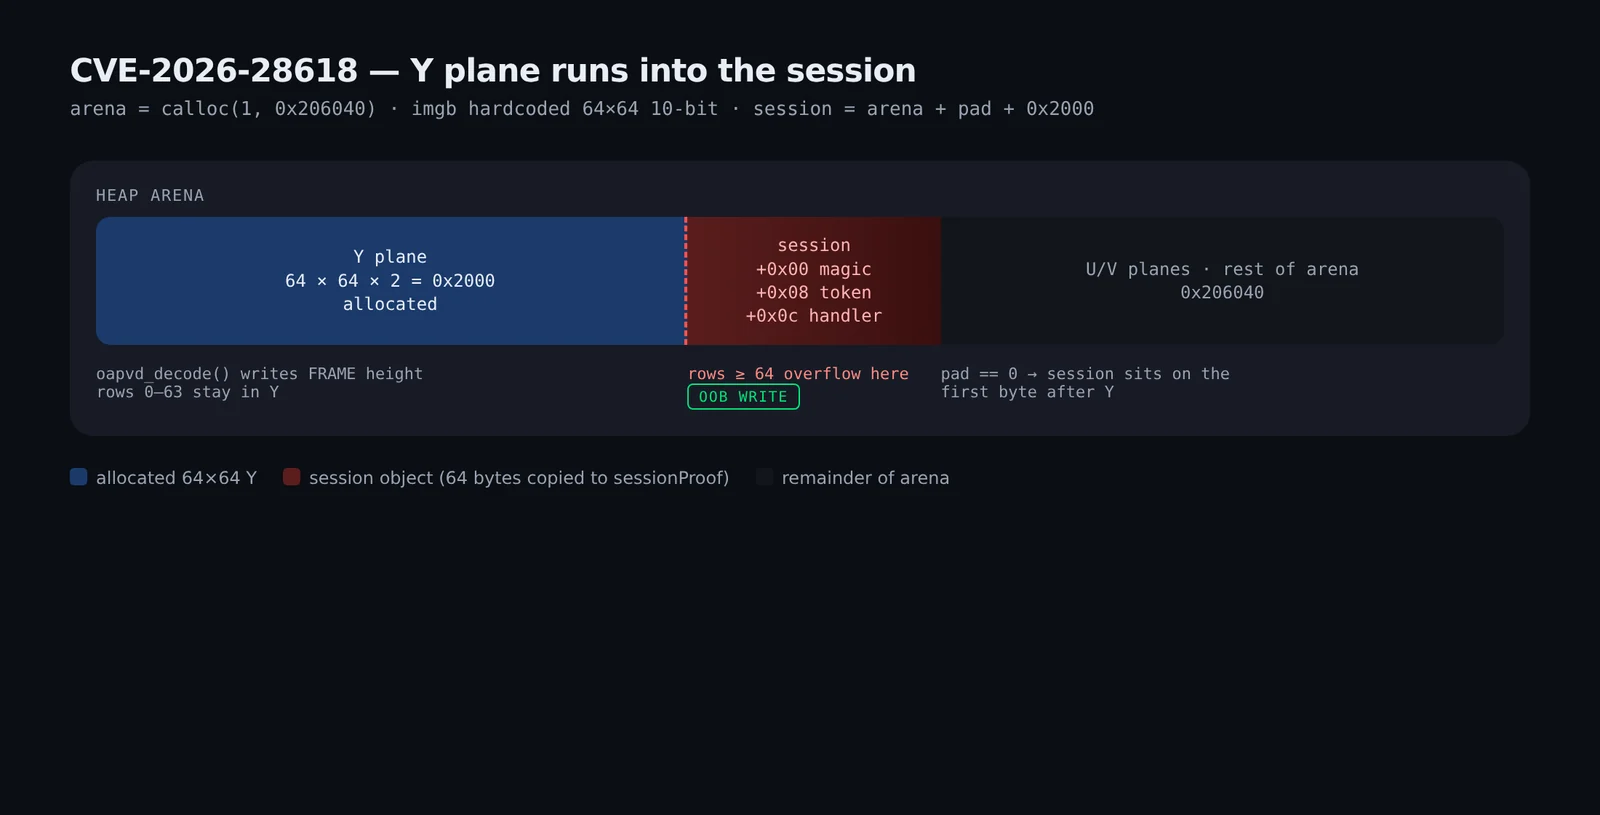
streambox-cve-2026-28618 preview

streambox-cve-2026-28618

GitHubraafatabualazm/streambox-cve-2026-28618

Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch

android-securitybinary-exploitationeducation+6
1 month ago
CVE-2020-0022 preview

CVE-2020-0022

GitHubidkwim/cve-2020-0022

Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
android-securitybinary-exploitationbluetooth-security+4
6 years ago
-Help-vivo-Y200i-5.10.218-GKI-CVE-2026-43499-stack-reclaim-reaches-0x300-need-0x318 preview

-Help-vivo-Y200i-5.10.218-GKI-CVE-2026-43499-stack-reclaim-reaches-0x300-need-0x318

GitHubanksgls-sj/-help-vivo-y200i-5.10.218-gki-cve-2026-43499-stack-reclaim-reaches-0x300-need-0x318

Research notes and PoC development for CVE-2026-43499 (GhostLock) kernel UAF on vivo Y200i Android 14, covering futex PI-chain stack-reclaim…
android-securitybinary-exploitationexploitation+5
1 month ago
CVE-2025-50944 preview

CVE-2025-50944

GitHubshinycolumn/cve-2025-50944

Improper Certificate Chain Validation in EagleEyes Lite Android Application
android-securitycryptographyeducation+3
1 year ago
CVE-2019-6447 preview

CVE-2019-6447

GitHubvino-theva/cve-2019-6447

This paper is about manual exploitation of android open port vulnerability found in ES file manager. This open TCP 59777 port allows the attacker to…
android-securityeducationexploitation+3
4 years ago
Obfuscapk preview
Archived

Obfuscapk

GitHubclaudiugeorgiu/obfuscapk

An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
android-securitydynamic-analysis-sandboxingeducation+4
1.3k2 years ago
tcl-androidtv-root-attempts preview

tcl-androidtv-root-attempts

GitHub4onurdemir/tcl-androidtv-root-attempts

Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…
android-securitybinary-analysiseducation+8
1 day ago
cve-2026-98260-vivo-gki-research preview

cve-2026-98260-vivo-gki-research

GitHubjanewas/cve-2026-98260-vivo-gki-research

Research notes: porting CVE-2026-98260 to vivo/iQOO GKI 6.6.127 (no exploit code; coordinated disclosure planned)
android-securitybinary-exploitationexploitation+5
48 days ago
CVE-2026-98937 preview

CVE-2026-98937

GitHubwoshigenm/cve-2026-98937

Verified PoC and analysis for a Linux perf/core permission-check bypass that leaks kernel callchain addresses to unprivileged Android tasks, enabling…
android-securityexploitationinformation-gathering+3
44 days ago
lpe-study-notes preview

lpe-study-notes

GitHubjadedfella/lpe-study-notes

A slow, from-zero walk through a Linux kernel privilege-escalation bug (CVE-2026-98260)
android-securitybinary-exploitationcurated-resources+6
112 days ago
o3root preview

o3root

GitHubzsw125/o3root

Shizuku-driven CVE-2026-98260 root + KernelSU runtime LKM loader for Xiaomi yingtian / lhasa (kernel 6.18.21)
android-securityeducationexploitation+5
333 days ago
CVE-2026-89633 preview

CVE-2026-89633

GitHubwoshigenm/cve-2026-89633

PoC and exploit chain for CVE-2026-89633, a heap out-of-bounds write in the Linux cifs.ko SMB1 TRANS2 coalescing path, escalating to uid 0 via cred…
android-securitybinary-exploitationexploitation+4
14 days ago
AuthenticatorFlaw-CVE-2026-80097 preview

AuthenticatorFlaw-CVE-2026-80097

GitHubghost-bx1/authenticatorflaw-cve-2026-80097

CVE-2026-80097 - Microsoft Authenticator Android Token Theft PoC & Exploit
android-securityauthenticationdata-exfiltration+6
4 days ago
CVE-2026-86950 preview

CVE-2026-86950

GitHub34zy/cve-2026-86950

Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…
binary-exploitationexploitationios-security+7
119 days ago
cve-2026-98260-uaf preview

cve-2026-98260-uaf

GitHubnanoturtle1145/cve-2026-98260-uaf

CVE-2026-98260 (posix-cpu-timers exec UAF) exploit research: S9280 Android 14 GKI 6.1 — UAF trigger + zero-write primitive + SELinux Permissive.…
android-securitybinary-exploitationexploitation+4
31 day ago
CVE-2026-97555 preview

CVE-2026-97555

GitHubwoshigenm/cve-2026-97555

Analysis, POC, and arm64 exploit chain for a Linux cifs.ko DACL heap overflow (CVE-2026-97555), escalating to a uid-0 credential overwrite on the…

android-securitybinary-exploitationexploitation+5
37 days ago
Previous12345Next